Compliance Modules: Implementation Guide for FSPs
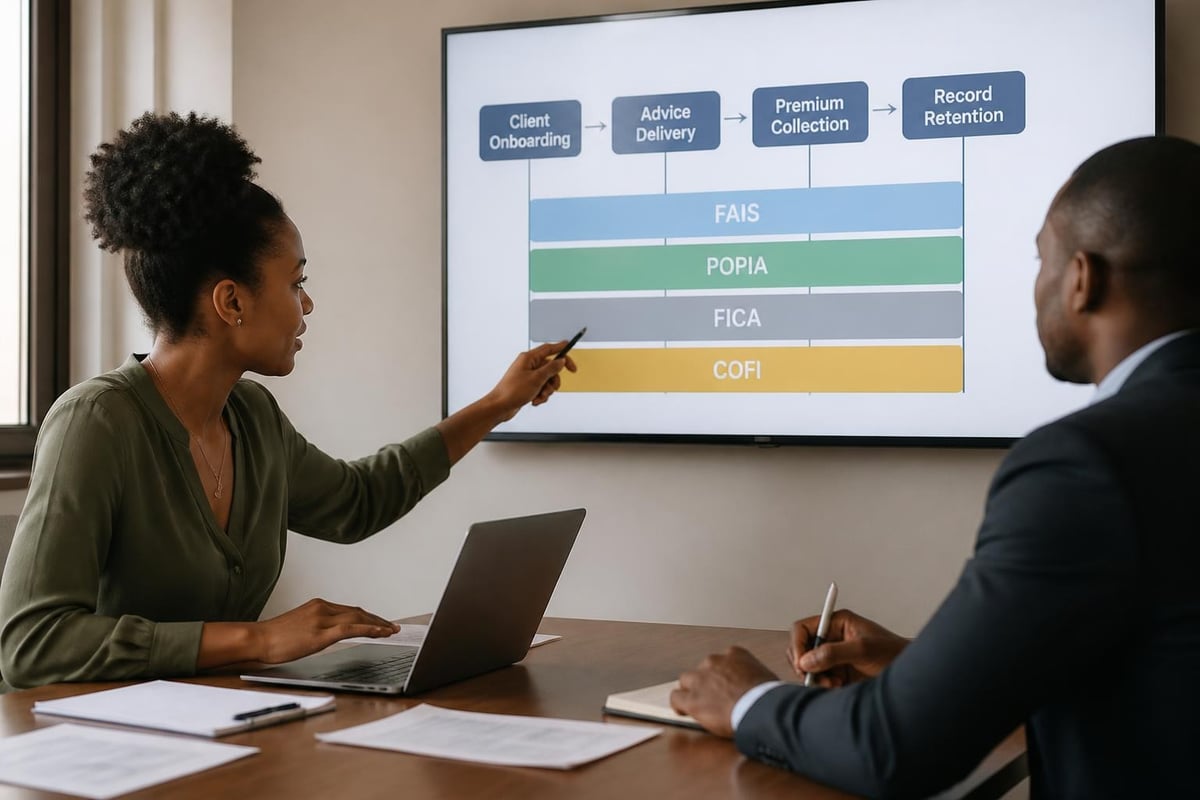
Financial service providers (FSPs) in South Africa face mounting regulatory obligations across multiple pieces of legislation. The Financial Advisory and Intermediary Services Act (FAIS), Protection of Personal Information Act (POPIA), Financial Intelligence Centre Act (FICA), and Conduct of Financial Institutions Act (COFI) each impose distinct compliance requirements on independent brokers and financial advisors. Compliance modules offer a structured approach to organising these obligations into manageable, auditable systems. Rather than treating compliance as an overwhelming checklist, well-designed compliance modules segment requirements by regulation, business function, and control type, enabling FSPs to demonstrate adherence systematically whilst maintaining efficient operations. This guide explores how independent broker practices can implement, maintain, and leverage compliance modules to meet South African regulatory standards.
Understanding Compliance Modules in the Financial Services Context
Compliance modules are discrete units within a broader governance framework that address specific regulatory domains or operational risks. Each module typically encompasses policy documentation, control procedures, monitoring mechanisms, training requirements, and evidence collection protocols related to a particular compliance obligation.
For South African FSPs, compliance modules commonly align with regulatory pillars: a FAIS module addressing fit and proper requirements, product suitability, and client advice standards; a POPIA module governing personal information processing; a FICA module managing client verification and anti-money laundering controls; and a COFI module preparing for market conduct obligations. This modular approach prevents regulatory overlap whilst ensuring comprehensive coverage.
Why Modular Architecture Matters
Independent broker practices benefit from modular design because it allows incremental implementation and focused updates. When the Financial Sector Conduct Authority (FSCA) issues a conduct standard or interpretation notice, you can update the relevant module without overhauling your entire compliance programme. Similarly, when onboarding new staff, training can be sequenced module by module rather than attempting to cover all obligations simultaneously.
The Center for Internet Security (CIS) Controls Navigator demonstrates how technical controls can be organised into implementation groups and mapped to multiple frameworks. This same principle applies to FSP compliance: individual modules contain controls that satisfy multiple regulatory requirements, creating efficiency through thoughtful structure.
FAIS Compliance Module: Core Components for Independent Brokers
Your FAIS compliance module must address the licensing regime, representative oversight, and advice standards that govern financial intermediaries. This module sits at the heart of your practice because it defines who may conduct business, under what conditions, and to what standard.
Essential FAIS Module Elements:
- Fit and proper file maintenance (including qualifications, experience records, criminal and credit checks)
- Representative register with up-to-date status, categories, and competency evidence
- Conflicts of interest policy, register, and disclosure protocols
- Client advice process (needs analysis templates, product comparison frameworks, suitability matrices)
- Complaints management procedure with timelines, escalation paths, and FAIS Ombud liaison process
- Outsourcing register (where you rely on third-party administrators, technology providers, or support services)
The compliance module should incorporate monthly checks to verify representative qualifications remain current and that Continuous Professional Development (CPD) hours are tracked against FSCA requirements. Quarterly reviews should assess whether advice files contain complete needs analyses, product comparisons, and suitability justifications.
Implementing Representative Oversight Controls
Your FAIS module requires a multi-layered oversight structure. At the first line, representatives complete advice files according to standardised templates. At the second line, compliance officers conduct file reviews using a sampling methodology (typically 5-10 per cent of new business monthly, plus all complaints and cancellations). At the third line, internal audit or an independent compliance practice reviews the effectiveness of first and second-line controls.
| Oversight Layer | Frequency | Focus Areas | Documentation Output |
|---|---|---|---|
| Representative self-review | Per transaction | Completeness, product suitability | Advice file checklist |
| Compliance file review | Monthly (sample) | Policy adherence, disclosure quality | File review register |
| Independent audit | Quarterly | Control effectiveness, trend analysis | Audit report and action plan |
Holistic Compliance Management Solutions offers compliance monitoring services that fulfill this second-line function for independent brokers who lack internal capacity, ensuring consistent file quality and early identification of control gaps.
POPIA Compliance Module: Information Officer Accountability
The Protection of Personal Information Act introduced the Information Officer role and eight processing conditions that FSPs must satisfy when handling client data. Your POPIA compliance module translates these statutory obligations into practical controls embedded in your daily operations.
Structuring the POPIA Module
Begin with a comprehensive information processing inventory. Document every instance where your practice collects, stores, uses, or shares personal information. For most independent brokers, this includes:
- Client onboarding forms (identity documents, contact details, financial information)
- Needs analysis records (health disclosures, dependant information, income and asset details)
- Policy administration data (premium payment records, beneficiary nominations)
- Marketing databases (prospect lists, communication preferences)
- Employee records (payroll information, performance reviews, disciplinary matters)
- Third-party data sharing (insurer submissions, reinsurer notifications, claims referrals)
Each processing activity requires documented purpose, lawful basis (typically consent or legitimate interest for FSPs), retention period, security measures, and cross-border transfer controls where applicable.
POPIA Module Checklist:
- Information processing register (activity, purpose, lawful basis, retention)
- Privacy notice templates (client-facing, website, marketing materials)
- Consent management framework (opt-in procedures, withdrawal mechanisms, record-keeping)
- Security controls assessment (access management, encryption standards, physical security)
- Breach response protocol (detection, containment, notification timelines, Information Regulator liaison)
- Data subject request procedure (access, correction, deletion workflows)
- Third-party processor agreements (insurer contracts, technology vendors, cloud service providers)
The NIST SP 800-53 controls catalog provides a comprehensive framework for mapping technical security controls to privacy requirements, offering FSPs a reference point for assessing whether their information security measures meet the POPIA standard of reasonable technical and organisational measures.
FICA Compliance Module: Client Verification and Risk Management
The Financial Intelligence Centre Act imposes customer due diligence, record-keeping, and suspicious transaction reporting obligations on FSPs as accountable institutions. Your FICA compliance module operationalises these requirements through standardised client onboarding procedures and ongoing monitoring protocols.
Client Onboarding and Verification Standards
FICA distinguishes between individuals, companies, trusts, and foreign entities, prescribing different verification standards for each. Your compliance module should include decision trees or flowcharts that guide representatives through the correct verification pathway based on client type.
Individual Client Verification:
- Identity document (certified copy not older than three months)
- Proof of residential address (utility bill, bank statement, or lease agreement dated within three months)
- Tax reference number
- Source of funds declaration (for high-value transactions exceeding risk threshold)
Legal Entity Verification:
- Registration certificate (company, trust deed, or foreign registration)
- Resolution authorising specific individuals to act on behalf of the entity
- Identification and verification of beneficial owners (natural persons holding 25 per cent or more)
- Proof of business address
Your FICA module must specify acceptable documents, certification requirements, verification procedures, and record retention obligations. Many independent brokers fail FSCA inspections because they accept uncertified copies or documents that exceed the three-month currency requirement.
Risk Management and Control Programme (RMCP)
Every FSP must maintain a documented RMCP that identifies money laundering and terrorist financing risks specific to their practice, assesses likelihood and impact, and implements controls proportionate to the risk assessment. Your FICA compliance module should incorporate:
| Risk Category | Assessment Factors | Controls | Monitoring Frequency |
|---|---|---|---|
| Client risk | Geographic location, occupation, politically exposed person status | Enhanced due diligence for high-risk categories | Quarterly review of client base |
| Product risk | Cash equivalence, investment flexibility, beneficiary nomination | Limits on cash payments, enhanced verification for flexible products | Annual product risk review |
| Channel risk | Face-to-face vs remote onboarding, intermediated transactions | Video verification for remote clients, intermediary due diligence | Per transaction |
| Transaction risk | Premium size, lump-sum contributions, early surrenders | Manual approval for amounts exceeding threshold | Real-time screening |
The compliance module should automate risk scoring where possible, flagging high-risk scenarios for manual review. Independent brokers processing fewer than 100 new clients annually may rely on spreadsheet-based systems, whilst larger practices benefit from compliance technology that integrates risk assessment into workflow tools.
COFI Compliance Module: Preparing for Market Conduct Standards
The Conduct of Financial Institutions Act introduces a principles-based conduct framework that will eventually replace FAIS. Whilst full implementation awaits, forward-thinking FSPs are building COFI compliance modules that align with the fair treatment of customers outcomes and conduct standards.
Designing the COFI Module
COFI emphasises six customer outcomes: fair treatment at all stages of the product lifecycle, suitable products and services, clear and appropriate information, advice that is in the customer's best interests, timely and efficient service, and protection of customer information. Your compliance module should map existing FAIS controls to these outcomes and identify gaps.
COFI Outcome Mapping:
- Outcome 1 (Fair treatment culture): Governance frameworks, incentive structures, complaint root-cause analysis
- Outcome 2 (Product suitability): Needs analysis procedures, product comparison matrices, replacement business justification
- Outcome 3 (Clear information): Disclosure templates, readability testing, client comprehension verification
- Outcome 4 (Customer-centric advice): Conflict of interest management, remuneration transparency, best-execution standards
- Outcome 5 (Timely service): Service level agreements, turnaround time monitoring, escalation procedures
- Outcome 6 (Information protection): POPIA controls, data breach response, third-party oversight
Because COFI adopt a principles-based approach rather than prescriptive rules, your compliance module requires more robust evidence collection. Where FAIS specifies that you must maintain a complaints register, COFI asks whether you are achieving fair customer outcomes. This demands management information dashboards that track outcome metrics: advice file quality scores, complaint resolution times, product performance against initial projections, and customer satisfaction indicators.
Practical Implementation: Building Your Compliance Module Framework
Implementing compliance modules requires a phased approach that balances regulatory completeness with operational practicality. Independent broker practices often lack dedicated compliance resources, making efficient design critical.
Phase 1: Foundation and Prioritisation (Months 1-2)
Begin with a compliance gap assessment against FAIS, POPIA, FICA, and COFI requirements. Document current practices, identify missing controls, and prioritise based on regulatory risk and FSCA enforcement trends. Recent supervisory communications highlighting representative oversight gaps, FICA verification deficiencies, and POPIA breach notifications indicate areas demanding immediate attention.
Create a modular documentation structure:
- Policy tier: High-level board-approved statements of intent (FAIS compliance policy, POPIA protection policy, FICA RMCP framework)
- Procedure tier: Step-by-step operational instructions (client onboarding procedure, file review procedure, data breach response procedure)
- Template tier: Standardised forms, checklists, and registers (needs analysis template, file review checklist, FICA verification register)
- Evidence tier: Completed forms, review outputs, and monitoring reports (individual advice files, monthly file review summaries, quarterly compliance reports to key individuals)
Phase 2: Control Deployment (Months 3-6)
Roll out compliance modules sequentially rather than simultaneously. Most practices prioritise FAIS and FICA modules first because these address core licensing and onboarding requirements that directly affect revenue generation.
For each module, establish control ownership. Your compliance officer coordinates and monitors, but operational staff execute controls. Representatives complete advice files, administrators verify FICA documents, and IT personnel implement POPIA security measures. Clear accountability prevents the "compliance officer does everything" trap that leads to superficial implementation.
Control Deployment Checklist:
- Control owner identified and trained on procedure
- Template or system support available to execute control
- Monitoring mechanism defined (sample size, frequency, acceptance criteria)
- Evidence collection and storage process established
- Escalation path for control failures documented
- Initial baseline measurement completed
Phase 3: Monitoring and Continuous Improvement (Ongoing)
Compliance modules deteriorate without active maintenance. Quarterly reviews should assess control effectiveness using leading indicators (control execution rates, quality scores, time to complete activities) and lagging indicators (complaints, FSCA queries, audit findings, near-miss incidents).
The ENISA NIS2 Technical Implementation Guidance provides practical examples of evidence collection and control maturity assessment that translate well to FSP compliance modules, particularly for technology-related controls like access management and incident response.
Update modules when regulations change, supervisory guidance clarifies expectations, or internal incidents reveal control gaps. FSCA conduct standards under COFI will necessitate module updates as detailed requirements emerge. Treat your compliance framework as living documentation subject to version control and change management.
Technology Enablement: Systems Supporting Compliance Modules
Manual compliance processes suffice for very small practices (1-2 representatives), but independent brokers with three or more staff benefit from technology that automates routine controls and consolidates evidence.
Evaluating Compliance Technology Solutions
The Forrester Buyer’s Guide on Governance, Risk, and Compliance platforms outlines evaluation criteria applicable to FSP compliance systems: regulatory content management, workflow automation, audit trails, reporting dashboards, and integration capabilities.
For South African independent brokers, key functionality includes:
- FICA workflow: Client type identification, document checklist generation, certification tracking, verification sign-off, expiry alerts
- Advice file workflow: Needs analysis templates, product comparison tools, suitability justification logic, supervisory review queues
- CPD tracking: Representative qualifications register, CPD hour accumulation, renewal date alerts, evidence repository
- Complaints management: Intake forms, classification taxonomy, resolution workflow, Ombud referral triggers, root-cause analytics
- POPIA consent management: Consent capture, purpose specification, withdrawal processing, consent audit trail
Avoid over-engineering. Many brokers implement sophisticated GRC platforms designed for large financial institutions, then fail to utilise advanced features whilst struggling with complexity. Purpose-built FSP compliance solutions or well-configured practice management systems often deliver better outcomes than enterprise platforms.
Training Requirements Within Compliance Modules
Each compliance module requires associated training to ensure staff understand obligations and execute controls correctly. Training effectiveness directly correlates with control quality: representatives who comprehend why FICA verification matters produce better documentation than those who view it as bureaucratic box-ticking.
Structuring Compliance Training Programmes
Design training around regulatory competencies rather than generic content. Your FAIS module training should cover specific advice process steps, disclosure requirements, and suitability assessment methodologies that representatives apply daily. POPIA training should address information handling scenarios staff encounter: emailing client details, storing documents in cloud systems, discussing client matters in public spaces.
Recommended Training Schedule:
| Module | Audience | Frequency | Format | Assessment Method |
|---|---|---|---|---|
| FAIS fundamentals | All representatives | Annually | Classroom or webinar | Case study evaluation |
| FICA procedures | Client-facing staff | Annually | Practical workshop | Document review exercise |
| POPIA awareness | All staff | Annually | E-learning | Multiple-choice test |
| COFI principles | Management and compliance | Bi-annually | Facilitated discussion | Scenario analysis |
| Product-specific compliance | Relevant representatives | Per new product | Product training integration | Competency interview |
Document training completion as part of fit and proper evidence. The FSCA expects FSPs to demonstrate that representatives possess not only initial qualifications but ongoing competency through structured training programmes addressing regulatory and product developments.
Common Implementation Pitfalls and Solutions
Independent brokers encounter predictable challenges when implementing compliance modules. Recognising these patterns enables preventive measures.
Pitfall 1: Documentation Without Implementation
Many practices develop impressive policy manuals that remain unread and unused. Staff continue prior workflows whilst compliance documentation gathers digital dust. Solution: Build procedures collaboratively with operational staff, embed compliance controls into existing workflows rather than creating parallel processes, and measure control execution rates as a key performance indicator.
Pitfall 2: Compliance Officer Overload
Smaller practices often designate one individual (frequently the principal) as the compliance officer responsible for executing all compliance activities. This model fails under volume and creates key-person risk. Solution: Distribute control ownership across relevant functions whilst the compliance officer coordinates, monitors, and reports to key individuals and the board.
Pitfall 3: Static Frameworks That Don't Evolve
Initial implementation receives focus and resources, but subsequent maintenance languishes. Compliance modules become outdated as regulations change or business models evolve. Solution: Schedule quarterly compliance module reviews as recurring calendar events, assign responsibility for tracking regulatory developments, and budget time for updates.
Pitfall 4: Evidence Gaps During Inspections
FSPs implement controls but fail to generate retrievable evidence demonstrating consistent execution. File reviews occur but lack documentation; training happens without attendance records; FICA verifications proceed without retention of certified copies. Solution: Treat evidence creation and storage as integral control components, implement naming conventions and folder structures for digital evidence, and conduct mock inspections quarterly.
Integrating Compliance Modules With Business Strategy
Mature FSP practices view compliance modules not as regulatory impositions but as business enablers that facilitate sustainable growth. Well-designed modules support strategic objectives whilst managing risk.
Compliance as Competitive Advantage
Demonstrating robust compliance capabilities attracts higher-quality insurers and product providers. Underwriters preferentially appoint brokers with strong governance frameworks because it reduces their own conduct risk exposure. Your compliance modules become marketing collateral when pitching for commercial schemes or institutional client mandates.
Similarly, professional liability insurers (offering errors and omissions cover) assess governance quality when underwriting and pricing. Brokers with documented compliance modules, regular file reviews, and active training programmes secure better terms than practices relying on informal processes.
Enabling Operational Efficiency
Standardised processes within compliance modules eliminate inconsistency that creates rework. When every representative follows the same needs analysis template, file review becomes faster and advice quality improves. When FICA verification follows a checklist, client onboarding accelerates and abandonment rates decrease.
Compliance modules also facilitate delegation and scaling. New representatives integrate faster when clear procedures define expected workflows. Adding administrative support becomes viable because tasks are sufficiently documented for handover. Growth ambitions require operational scalability that informal compliance approaches cannot support.
Measuring Compliance Module Effectiveness
Implementing compliance modules represents the starting point, not the destination. Ongoing measurement determines whether modules achieve regulatory compliance and operational objectives.
Key Performance Indicators by Module
FAIS Module KPIs:
- Percentage of advice files meeting quality standards (target: 95 per cent on first review)
- Average time to complete file review (target: within 5 business days of submission)
- Representative CPD compliance rate (target: 100 per cent by year-end)
- Client complaints per 1,000 policies (benchmark against industry averages)
POPIA Module KPIs:
- Data subject requests resolved within statutory timelines (target: 100 per cent)
- Security incidents detected and contained (target: detection within 24 hours, containment within 72 hours)
- Staff POPIA awareness training completion (target: 100 per cent annually)
- Third-party processor agreements reviewed and current (target: 100 per cent)
FICA Module KPIs:
- Client verification completed before first transaction (target: 100 per cent)
- Percentage of verifications meeting documentary standards (target: 98 per cent on compliance review)
- High-risk clients identified and subject to enhanced due diligence (target: 100 per cent)
- RMCP annual review completed and approved by board (target: within 3 months of financial year-end)
Track KPIs monthly and report to key individuals quarterly. Trends matter more than point-in-time measurements: improving file quality scores indicate effective training and feedback, whilst deteriorating verification standards suggest control breakdown requiring intervention.
Regulatory Examination Preparedness
FSCA on-site inspections test whether your compliance modules translate into consistent practice. Examiners verify that documented policies reflect operational reality and that evidence substantiates claimed controls.
Typical FSCA Inspection Focus Areas
Supervisory visits commonly examine representative oversight (file reviews, CPD records, fit and proper files), FICA compliance (verification documentation, RMCP implementation, suspicious transaction awareness), complaints handling (register completeness, resolution timelines, Ombud referrals), and conflicts of interest management (register maintenance, disclosure practices, remuneration transparency).
Prepare by conducting internal inspections using FSCA examination guides as reference materials. Sample representative files quarterly using the same methodology examiners employ: random selection across representatives, product types, and time periods. Assess against regulatory standards and internal policies, document findings, remediate deficiencies, and track remediation completion.
Maintain an inspection-ready evidence repository. When examiners request your FAIS compliance policy, you should produce the current board-approved version within minutes. When they ask to see file review summaries for the past year, you should access organised monthly reports instantly. Evidence retrieval speed and organisation signal governance maturity.
Advanced Compliance Module Capabilities
As your compliance framework matures, consider advanced capabilities that enhance efficiency and provide deeper insights.
Risk-Based Control Intensity
Differentiate control intensity based on risk assessment. Low-risk transactions (straightforward product replacements for existing clients with stable circumstances) may justify streamlined procedures, whilst high-risk scenarios (complex investment strategies, financially vulnerable clients, unclear source of funds) trigger enhanced controls.
This risk-based approach allocates compliance resources where they deliver most value. Representatives spend more time on files that present genuine risk whilst processing routine matters efficiently. The OWASP application security resources demonstrate risk-based testing methodologies applicable to compliance workflows: focus intensive review where risk concentrates.
Predictive Analytics and Early Warning Indicators
Mature compliance modules incorporate forward-looking indicators that predict control failures before they manifest. Declining file quality scores presage complaint increases; extended file review backlogs indicate capacity constraints; representative CPD shortfalls signal qualification lapses approaching.
Monitor leading indicators and intervene proactively. When file quality dips below threshold, schedule refresher training. When FICA verification errors cluster around particular administrators, provide targeted coaching. When complaint volumes spike in specific product categories, investigate root causes and adjust advice procedures.
Third-Party Assurance Integration
Independent brokers increasingly rely on third-party service providers for technology, administration, and compliance support. Your compliance modules should incorporate oversight controls for these relationships: due diligence at onboarding, service level monitoring during the relationship, and periodic assurance reviews.
Obtain SOC 2 reports or equivalent assurance from significant technology vendors. For compliance practices providing file review or FICA verification support, request sample quality assessments and qualifications verification. The PCI Security Standards Council guidance on system component applicability illustrates how to scope third-party environments and determine control responsibilities, a framework transferable to FSP outsourcing arrangements.
Building a Culture of Compliance
Compliance modules provide structure, but culture determines execution quality. Technical compliance (following procedures) differs from cultural compliance (understanding why compliance matters and embedding it in decision-making).
Foster compliance culture through visible leadership commitment: key individuals should reference compliance in strategic discussions, allocate sufficient resources, and celebrate compliance achievements alongside sales successes. When management treats compliance as equal to revenue generation, staff mirror that prioritisation.
Communicate the "why" behind requirements. Representatives who understand that FICA verification prevents your practice from inadvertently facilitating financial crime demonstrate greater diligence than those who view it as bureaucracy. Staff who comprehend that POPIA protects client trust and prevents reputational damage handle information more carefully than those who see it as an IT issue.
Recognise and reward compliance excellence. Include compliance metrics in performance evaluations and variable compensation structures. Acknowledge representatives who consistently produce high-quality advice files. Feature compliance achievements in team meetings and internal communications. What gets measured and celebrated gets repeated.
Compliance modules transform overwhelming regulatory obligations into manageable, auditable systems that enable independent brokers and FSPs to operate confidently within South Africa's financial services framework. By structuring FAIS, POPIA, FICA, and COFI requirements into discrete modules with clear controls, evidence protocols, and monitoring mechanisms, you create sustainable compliance capabilities that support business growth whilst managing regulatory risk. At Holistic Compliance Management Solutions (Pty) Ltd, we partner with independent brokers across South Africa to design, implement, and maintain compliance frameworks tailored to your practice size and complexity. Whether you need FICA training to strengthen client verification procedures, compliance monitoring to provide independent file reviews, or comprehensive support building your compliance module framework from foundation, our team brings practical experience serving FSPs since 2018. Schedule FICA training with us to equip your team with verification best practices, RMCP implementation guidance, and practical workflows that integrate compliance into daily operations. This training is ideal for independent brokers establishing new practices, regulated brokers strengthening existing controls, and compliance officers seeking structured implementation methodologies. Contact us to discuss how our training programmes can elevate your compliance capabilities and prepare your practice for regulatory scrutiny.