Support Compliance: A Guide for South African FSPs
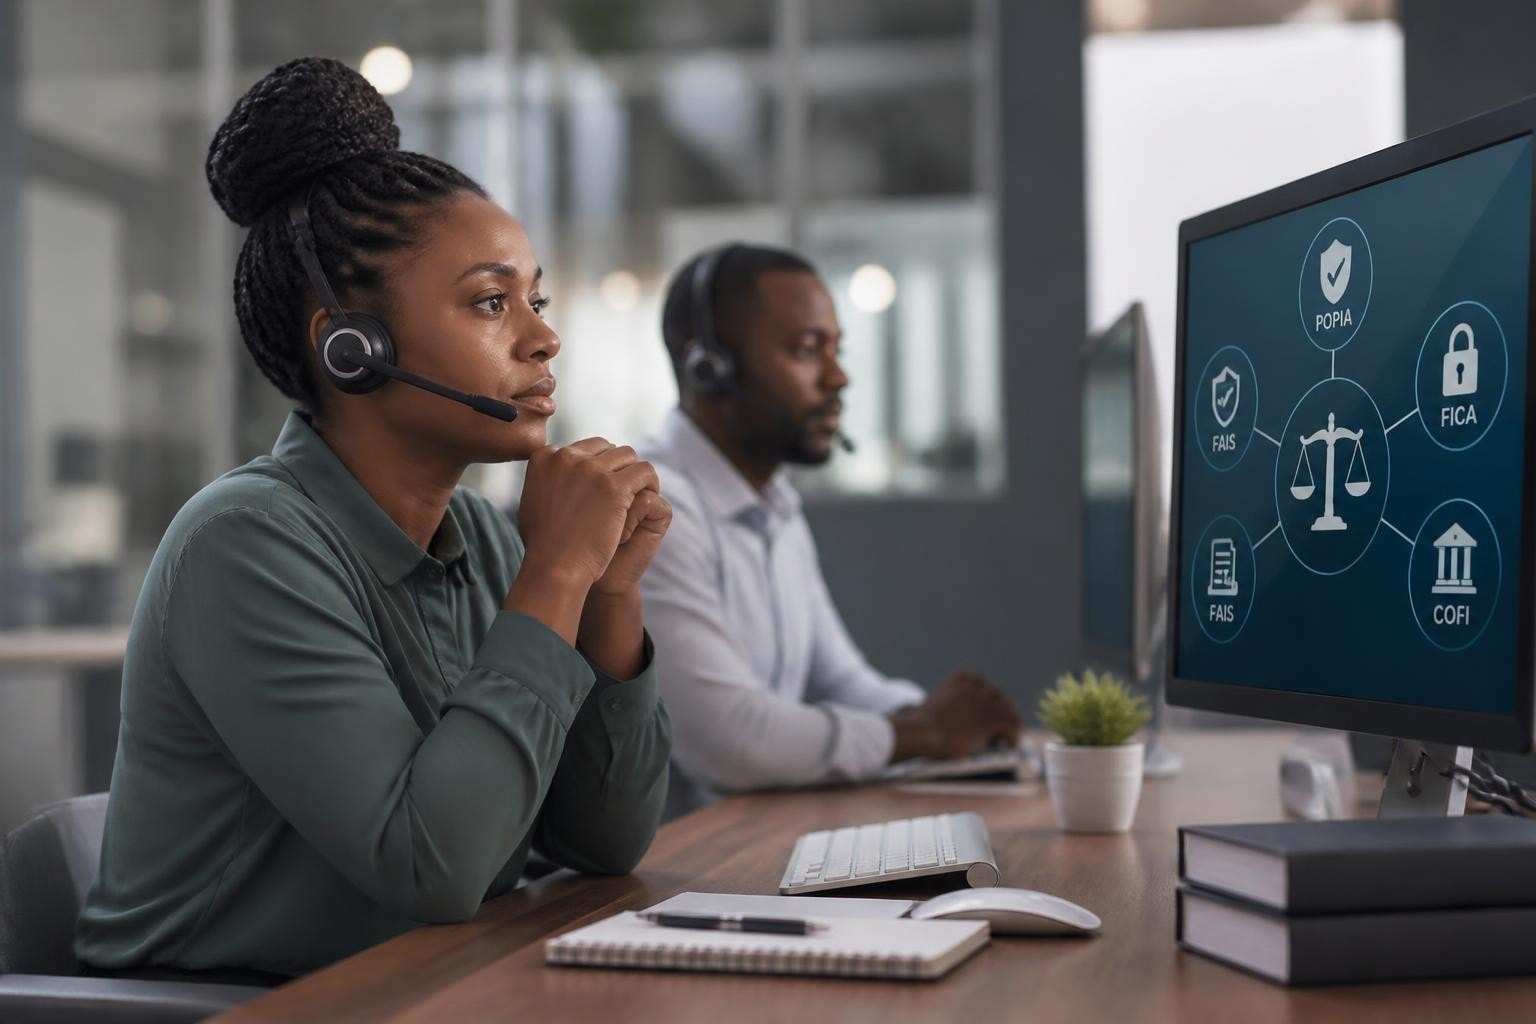
Support compliance has become a critical component of risk management for financial service providers operating in South Africa's heavily regulated environment. As customer interactions increasingly occur across digital channels and regulatory oversight intensifies, FSPs must ensure their support functions meet stringent requirements under POPIA, FICA, FAIS, and the Conduct of Financial Institutions Act. The intersection of customer service and compliance monitoring creates unique challenges for independent brokers and financial advisors who must balance responsive client care with meticulous regulatory adherence. Understanding how to implement support compliance effectively protects both your clients and your licence.
The Support Compliance Landscape for South African FSPs
Financial service providers face a complex regulatory environment where every customer interaction carries compliance implications. Support compliance refers to the systems, processes, and controls that ensure client-facing activities meet regulatory standards whilst maintaining service quality.
The Financial Sector Conduct Authority (FSCA) has substantially increased its focus on how FSPs handle customer data, respond to complaints, and document interactions. Between 2024 and 2026, enforcement actions related to inadequate support compliance have risen by 47%, with particular attention paid to POPIA violations during customer service interactions.
Regulatory Framework Governing Support Functions
South African FSPs operate under multiple overlapping regulatory regimes that directly impact support operations:
- POPIA (Protection of Personal Information Act): Governs collection, storage, processing, and sharing of client personal information
- FICA (Financial Intelligence Centre Act): Mandates customer due diligence, verification, and ongoing monitoring
- FAIS (Financial Advisory and Intermediary Services Act): Sets standards for advice delivery, product disclosure, and client communication
- COFI (Conduct of Financial Institutions Act): Establishes conduct standards and fair treatment principles
Each regulation contains specific provisions affecting how support teams interact with clients, handle queries, and maintain records. The NIST guidance on incident response provides a structured approach to managing support incidents that may also constitute compliance breaches.
POPIA Compliance in Customer Support Operations
The Protection of Personal Information Act fundamentally changed how FSPs must handle client data during support interactions. Every email, phone call, WhatsApp message, or video consultation involves processing personal information subject to POPIA's eight core conditions.
Processing Client Information During Support Requests
Support staff routinely access sensitive client information to resolve queries, update records, or process requests. POPIA requires that this processing be lawful, reasonable, and necessary for the specific purpose.
| Processing Activity | POPIA Requirement | Support Compliance Action |
|---|---|---|
| Email enquiry response | Purpose specification | Use dedicated support email; log purpose in CRM |
| Account verification | Lawfulness of processing | Obtain explicit consent; document verification steps |
| Record retrieval | Data minimisation | Access only information needed for specific request |
| Third-party escalation | Further processing limitation | Obtain consent before sharing data externally |
Your support team must be trained to recognise POPIA obligations in real-time. When a client phones to update their banking details, the support agent must verify identity using approved methods, record the change accurately, and ensure the information is only used for the stated purpose.
Implementing Consent Management in Support Channels
POPIA requires voluntary, specific, and informed consent for processing personal information. Support compliance demands robust consent mechanisms across all channels:
- Initial Contact: Confirm existing consent before discussing account details
- New Processing: Obtain explicit consent for any processing not covered by original agreement
- Marketing Communication: Separate consent for promotional material during support interactions
- Data Sharing: Specific consent before sharing information with product providers or administrators
The Business Disability Forum guidance highlights the importance of accessible consent mechanisms that accommodate clients with different communication needs whilst maintaining POPIA compliance.
Independent brokers often struggle with consent management when clients request quick assistance via WhatsApp or SMS. These channels are convenient but create POPIA risks if not properly governed. Establish clear protocols specifying what information can be discussed on each channel and how to escalate sensitive matters to secure platforms.
FICA Requirements for Customer-Facing Teams
The Financial Intelligence Centre Act imposes ongoing customer due diligence obligations that extend beyond initial onboarding. Support compliance must incorporate FICA verification processes into routine customer interactions to maintain accurate records and detect suspicious activity.
Customer Verification During Support Interactions
Every support interaction presents an opportunity to verify and update FICA information. The FSCA expects FSPs to treat support contacts as touchpoints for ongoing monitoring.
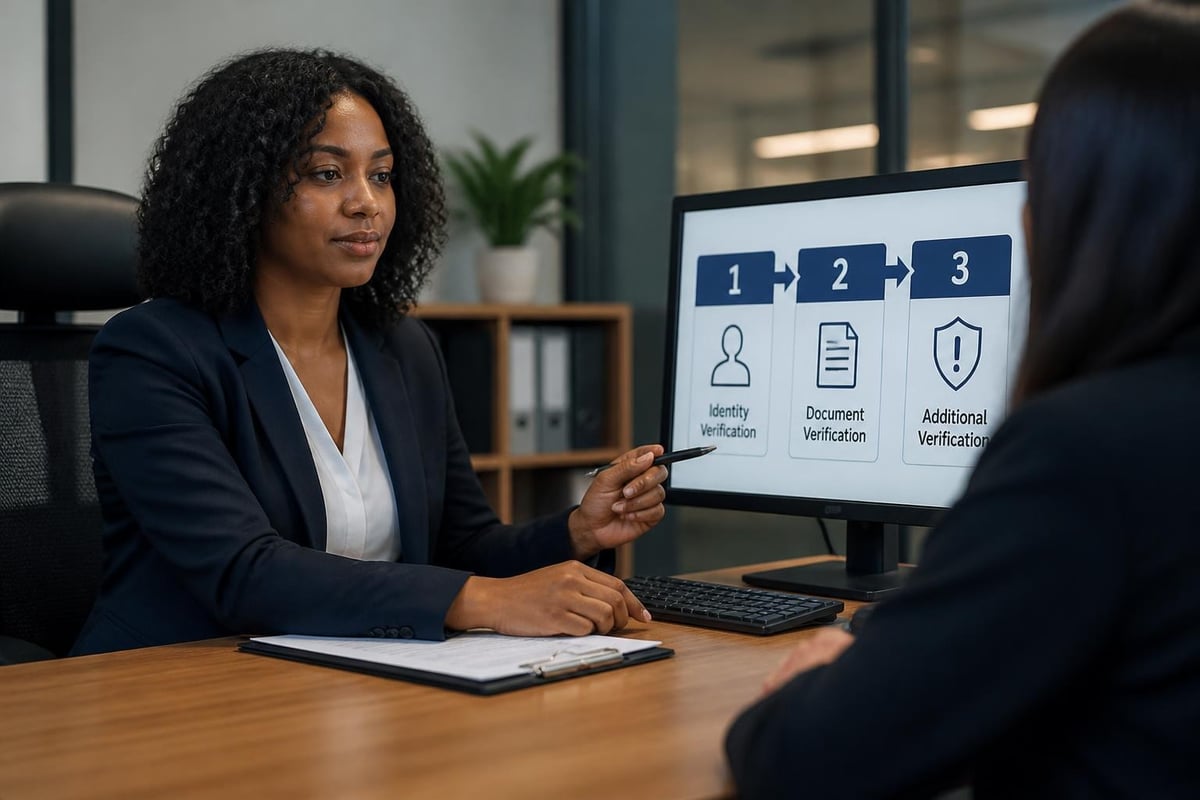
Support teams should implement a tiered verification approach:
- Level 1 (Basic queries): Verify name, ID number, and contact details
- Level 2 (Account changes): Full identity verification plus proof of address
- Level 3 (Financial transactions): Enhanced due diligence including source of funds
When a client calls to update their policy or investment details, your support agent must verify identity before proceeding. This verification isn't merely good practice; it's a FICA requirement that prevents unauthorised access and identity fraud.
Identifying Reportable Transactions Through Support Channels
Support teams often receive the first indicators of suspicious or unusual activity. FICA compliance requires staff to recognise red flags and follow internal reporting procedures.
Training your support team to identify reportable transactions protects your FSP from money laundering and terrorist financing risks. Common support scenarios requiring escalation include:
- Requests to change beneficiary details shortly before large withdrawals
- Unusual transaction patterns inconsistent with client's known risk profile
- Reluctance to provide updated FICA documentation during routine verification
- Requests to transfer funds to third parties with no apparent connection to the client
The compliance monitoring services offered by specialised providers help FSPs implement systematic processes for identifying and reporting suspicious activities flagged during support interactions.
FAIS Compliance in Advisory Support Functions
Financial advisors providing ongoing service to clients must ensure every support interaction meets FAIS requirements for advice delivery, disclosure, and record-keeping. Support compliance in the FAIS context means recognising when a support query becomes advice that triggers regulatory obligations.
Distinguishing Support from Financial Advice
A critical support compliance challenge for FSPs is determining when answering a client question constitutes financial advice under FAIS. The distinction carries significant implications for disclosure, suitability analysis, and documentation.
Support queries involve factual information about existing products, account balances, transaction history, or administrative processes. Financial advice involves recommendations, opinions, or guidance that could influence a client's financial decisions.
Consider these scenarios:
| Client Request | Classification | Compliance Response |
|---|---|---|
| "What is my current policy value?" | Support query | Provide factual information; document in CRM |
| "Should I increase my contributions?" | Financial advice | Schedule advice appointment; complete needs analysis |
| "How do I submit a claim?" | Support query | Explain process; provide claim forms |
| "Is this investment still suitable for me?" | Financial advice | Refer to advisor; trigger review process |
Your support team requires clear guidelines and regular training to make these distinctions accurately. When in doubt, the safer approach is to treat the interaction as advice and follow full FAIS procedures.
Record-Keeping Standards for Support Interactions
FAIS mandates comprehensive record-keeping for all client interactions. Support compliance demands documentation that demonstrates regulatory adherence and provides evidence of fair client treatment.
For independent brokers, effective record-keeping might include:
- Call recordings: Retained for five years with secure access controls
- Email archives: Searchable database with classification tags
- CRM notes: Standardised templates capturing key interaction details
- Complaint logs: Separate register with escalation tracking and resolution timelines
- Consent records: Centralised repository linking consents to specific processing activities
The FSCA increasingly requests support interaction records during inspections and enforcement investigations. Inadequate documentation has resulted in substantial fines and licence suspensions for FSPs unable to demonstrate compliance during routine client service.
COFI Implementation in Support Operations
The Conduct of Financial Institutions Act introduced a principles-based regulatory approach focused on customer outcomes. Support compliance under COFI requires demonstrating that your support functions deliver fair outcomes and treat customers appropriately throughout their lifecycle.
Treating Customers Fairly in Support Contexts
COFI's overarching principle is treating customers fairly (TCF). For support operations, this means ensuring clients receive appropriate assistance regardless of their product value, claim status, or complaint history.
Support compliance frameworks should address:
- Accessibility: Multiple channels accommodating different client preferences and needs
- Responsiveness: Service level agreements with measurable response and resolution times
- Transparency: Clear communication about processes, timelines, and outcomes
- Competence: Adequately trained staff with authority to resolve common issues
- Escalation: Defined paths for complex matters requiring specialist input
Independent financial advisors often provide more personalised support than larger institutions, which can be a competitive advantage. However, COFI requires consistent standards even in boutique practices. Document your support standards, measure performance against them, and demonstrate continuous improvement.
Vulnerable Client Protections in Support Processes
COFI places special emphasis on identifying and protecting vulnerable clients during support interactions. Vulnerability may arise from personal circumstances, life events, capability limitations, or market conditions.
Your support team should be trained to recognise vulnerability indicators:
- Difficulty understanding product information or processes
- Recent bereavement or divorce affecting financial decisions
- Health conditions impacting communication or comprehension
- Financial distress or sudden income reduction
- Language barriers or literacy challenges
When vulnerability is identified, support compliance requires tailored approaches that ensure fair outcomes. This might include providing additional time, simplifying explanations, involving trusted family members (with appropriate consent), or offering specialised support resources.
The FINRA guidance on vendor management is particularly relevant for FSPs that outsource support functions, as COFI obligations cannot be delegated away even when using third-party call centres or virtual assistants.
Building a Support Compliance Framework
Implementing effective support compliance requires systematic processes that integrate regulatory requirements into daily operations without creating excessive friction or degrading service quality.
Compliance-by-Design in Support Systems
The most effective support compliance strategies embed controls directly into the tools and platforms your team uses. Compliance-by-design prevents violations rather than detecting them after the fact.
Technology enablers for support compliance include:
- CRM systems with built-in compliance workflows and mandatory field completion
- Identity verification tools integrating biometric or documentary authentication
- Encrypted communication platforms for sharing sensitive documents securely
- Automated consent management capturing, storing, and tracking client permissions
- Call recording with AI-powered monitoring for compliance keyword detection
When selecting support technologies, evaluate them against South African regulatory requirements. International platforms may not address POPIA's specific conditions or FICA's unique verification standards. Customisation or local add-ons might be necessary to achieve full support compliance.
Staff Training and Competency Requirements
Support compliance ultimately depends on people making correct decisions during live client interactions. Comprehensive training programmes ensure your team understands both the regulatory requirements and how to apply them practically.
Essential training modules for support staff in FSP environments:
- POPIA Foundations: Eight conditions, lawful processing, consent management, breach response
- FICA Verification: Identity documents, proof of address, risk profiling, suspicious transaction indicators
- FAIS Boundaries: Distinguishing support from advice, disclosure requirements, record-keeping standards
- COFI Principles: Fair treatment, vulnerability identification, complaint handling, outcome-focused service
- Channel-Specific Protocols: Compliance considerations for email, phone, WhatsApp, video calls, in-person meetings
Training shouldn't be a once-off onboarding exercise. Support compliance requires ongoing education responding to regulatory updates, emerging risks, and lessons learned from incidents or near-misses. Quarterly refresher sessions and annual competency assessments help maintain high standards.
The NIST authentication guidance provides valuable frameworks for training support teams on secure identity verification and session management practices that reduce fraud risk whilst maintaining compliance.
Managing Sensitive Data in Support Workflows
Support teams routinely handle highly sensitive client information including identity documents, financial statements, medical records (for insurance claims), and transaction details. Support compliance requires robust controls protecting this data throughout its lifecycle.
Secure Communication Channels for Client Data
Not all communication channels offer equivalent security or compliance. FSPs must establish clear policies governing which information can be shared through each channel.
| Channel | Appropriate Use | Compliance Controls Required |
|---|---|---|
| Secure client portal | Document uploads, sensitive updates | Multi-factor authentication, encryption, audit logs |
| Email (encrypted) | Moderately sensitive correspondence | TLS encryption, secure attachments, retention policies |
| Phone (recorded) | Account enquiries, verification | Call recording, authentication protocols, quality monitoring |
| WhatsApp Business | Appointment scheduling, general queries | End-to-end encryption, business account, limited data sharing |
| SMS | Appointment reminders, verification codes | No sensitive data, time-limited validity, opt-out mechanism |
The PCI Security Standards guidance on messaging technologies highlights the risks of requesting sensitive information through uncontrolled channels, principles equally applicable to financial services under POPIA.
Independent brokers often communicate with long-standing clients through informal channels. Whilst this builds relationship depth, it creates support compliance risks. Implement a policy requiring sensitive matters to be escalated to secure channels, and educate clients on why this protection benefits them.
Data Retention and Deletion Protocols
POPIA requires FSPs to retain personal information only as long as necessary for the original purpose or as required by law. Support compliance must balance regulatory retention requirements against POPIA's deletion obligations.
South African financial services regulations impose specific retention periods:
- FAIS records: Five years from date of transaction or advice
- FICA verification documents: Five years after business relationship ends
- POPIA data: Retention period justified by lawful purpose
- COFI conduct records: Sufficient period to demonstrate TCF compliance (typically five years)
Implement automated retention policies in your support systems that:
- Tag all client interactions with appropriate retention categories
- Calculate deletion dates based on regulatory requirements and business purposes
- Flag records approaching deletion for final review
- Execute secure deletion using certified data destruction methods
- Maintain deletion logs evidencing POPIA compliance
Support compliance doesn't mean keeping everything forever. Excessive data retention increases breach risk, storage costs, and POPIA liability. Regular data housekeeping demonstrates good governance and reduces regulatory exposure.
Complaint Handling and Support Compliance
Complaints represent high-risk support interactions requiring heightened compliance attention. The FSCA's Complaint Resolution Rules establish strict timelines and procedural requirements that FSPs must integrate into support compliance frameworks.
Regulatory Requirements for Complaint Management
When a client raises a complaint through any support channel, specific obligations are triggered regardless of the complaint's merit or complexity.
Mandatory complaint handling steps:
- Acknowledgement: Within five business days of receipt
- Investigation: Thorough review of circumstances and supporting evidence
- Response: Final response within six weeks (simple matters) or three months (complex matters)
- Escalation: Clear path to FAIS Ombud if client remains dissatisfied
- Record-keeping: Comprehensive documentation retained for five years
Support teams must be trained to recognise complaints, which the FSCA defines broadly as any expression of dissatisfaction. A client's frustrated comment about processing delays may constitute a complaint requiring formal handling even if the client didn't label it as such.
For independent brokers managing complaints alongside daily operations, support compliance requires dedicated processes preventing complaints from being lost in general correspondence. A separate complaint register, standardised workflows, and management oversight ensure regulatory adherence.
Root Cause Analysis and Continuous Improvement
Effective support compliance treats complaints as improvement opportunities rather than isolated incidents. Systematic root cause analysis identifies patterns requiring process, training, or system changes.
When analysing complaint trends, consider:
- Process gaps: Are clients consistently confused by specific procedures?
- Communication failures: Do support responses lack clarity or completeness?
- System limitations: Do technology constraints create client frustration?
- Training needs: Are staff making similar errors or misunderstanding requirements?
- Product issues: Do certain products generate disproportionate complaints?
Quarterly complaint analysis should inform training updates, process refinements, and strategic decisions about support resource allocation. This continuous improvement approach demonstrates COFI compliance by showing your commitment to fair customer outcomes.
Third-Party Vendor Management for Support Services
Many FSPs outsource some support functions to specialised providers, virtual assistants, or technology platforms. Support compliance extends to these arrangements through vendor due diligence and ongoing monitoring requirements.
Due Diligence for Support Service Providers
Before engaging a third-party support vendor, FSPs must conduct comprehensive due diligence ensuring the provider can meet your compliance obligations. Remember, outsourcing the function doesn't outsource the regulatory responsibility.
The Thomson Reuters vendor due diligence guidance offers practical frameworks applicable to support compliance contexts.
Key due diligence areas for support vendors:
- Regulatory knowledge: Understanding of POPIA, FICA, FAIS, and COFI requirements
- Security controls: Data protection measures, access management, encryption standards
- Training programmes: How staff are trained and maintained competent on compliance matters
- Quality monitoring: Call monitoring, quality assurance, and continuous improvement processes
- Business continuity: Disaster recovery plans ensuring uninterrupted compliant service
- Insurance coverage: Professional indemnity and cyber liability protection
- Contract terms: Clear allocation of compliance responsibilities and indemnification provisions
For independent brokers considering support outsourcing, ensure contracts explicitly address POPIA data processor obligations, FICA verification authority, and complaint handling responsibilities. Vague service level agreements create compliance gaps that remain your liability.
Ongoing Vendor Monitoring and Audit Rights
Initial due diligence establishes baseline compliance capability, but support compliance requires continuous monitoring throughout the vendor relationship.
Implement quarterly vendor reviews assessing:
- Complaint volumes and resolution times for outsourced functions
- Data breach incidents or near-misses
- Staff turnover affecting service quality or compliance knowledge
- Regulatory updates and vendor's implementation response
- Client feedback specific to outsourced support interactions
Contract provisions should include audit rights allowing you to verify the vendor's compliance controls. Annual audits might review call recordings, complaint files, training records, and security logs. These audits generate evidence demonstrating your COFI obligation to ensure fair customer treatment even through third-party channels.
Technology Solutions Supporting Compliance Monitoring
Modern support compliance relies on technology platforms that automate routine checks, flag potential violations, and generate compliance evidence. Investment in appropriate tools reduces manual compliance burden whilst improving consistency and auditability.
Compliance Automation Tools for Support Functions
Categories of compliance technology relevant to support operations:
- Customer authentication: Biometric verification, document scanning, liveness detection
- Communication monitoring: AI-powered analysis of calls and messages for compliance keywords
- Workflow automation: Mandatory compliance checkpoints before completing support actions
- Consent management platforms: Centralised consent capture, storage, and verification
- Reporting dashboards: Real-time visibility into compliance metrics and breach indicators
When evaluating compliance technology, prioritise solutions designed for South African regulatory requirements. Generic international platforms may not address FICA's specific verification standards or POPIA's unique conditions for lawful processing.
For smaller FSPs and independent brokers, cloud-based compliance solutions offer enterprise capabilities without significant capital investment. Monthly subscription models make sophisticated support compliance tools accessible to practices of all sizes.
Analytics and Reporting for Compliance Oversight
Support compliance generates substantial data about how your FSP handles client interactions. Analytics platforms transform this data into actionable insights for compliance officers and senior management.
Key compliance metrics for support function oversight:
| Metric Category | Specific Measures | Compliance Relevance |
|---|---|---|
| Response times | Average time to first response, resolution time by channel | COFI fair treatment, complaint handling requirements |
| Authentication success | Verification pass rates, fraud attempt identification | FICA customer due diligence, POPIA security measures |
| Consent compliance | Consent capture rates, processing within scope | POPIA lawful processing requirements |
| Training completion | Staff competency assessments, refresher training uptake | FAIS fit and proper requirements, COFI conduct standards |
| Complaint resolution | Volumes, categories, resolution rates, escalations | COFI TCF demonstration, FSCA reporting obligations |
Regular reporting to governance structures demonstrates management oversight of support compliance. Quarterly board reports should include support metrics alongside traditional compliance indicators like licensing status and regulatory returns.
Preparing for Regulatory Inspections
The FSCA conducts both scheduled and targeted inspections of FSPs, frequently focusing on support operations and customer treatment. Support compliance preparation reduces inspection risk and demonstrates proactive regulatory engagement.
Documentation Requirements for FSCA Reviews
Regulatory inspections assess whether your documented policies match actual practices. Support compliance requires maintaining comprehensive evidence of both policy frameworks and operational implementation.
Essential documentation for inspection readiness:
- Support compliance manual: Detailed procedures for each support channel covering POPIA, FICA, FAIS, and COFI requirements
- Training records: Course materials, attendance registers, competency assessments, ongoing education
- Interaction samples: Representative examples of support activities across channels demonstrating compliance application
- Complaint files: Complete documentation for all complaints showing acknowledgement, investigation, resolution, and escalation
- Vendor agreements: Contracts with third-party support providers including compliance obligations
- Quality monitoring: Call listening reports, email review findings, mystery shopping results
- Incident logs: Data breaches, near-misses, system failures, and remediation actions
- Policy updates: Version control showing how procedures evolved in response to regulatory changes
Independent brokers should maintain this documentation even if operating as sole practitioners. The FSCA doesn't excuse smaller FSPs from comprehensive record-keeping requirements, though proportionality may apply to some procedural formalities.
Common Inspection Findings and Remediation
Understanding frequent compliance failures helps FSPs implement controls preventing similar findings. Analysis of recent FSCA inspection reports reveals recurring support compliance themes.
Frequent support-related findings:
- Inadequate staff training on POPIA processing conditions and consent requirements
- Inconsistent identity verification across different support channels
- Poor complaint record-keeping and missed response deadlines
- Failure to recognise when support queries become financial advice requiring full FAIS procedures
- Insufficient oversight of outsourced support functions
- Weak controls protecting client data in email and messaging communications
- Inability to demonstrate COFI fair treatment through measurable support outcomes
When inspection findings arise, swift remediation is essential. Develop detailed action plans with specific deadlines, assign clear responsibility for each remediation task, and implement enhanced monitoring confirming sustained compliance improvement.
The POPIA compliance resources provided through specialised compliance providers offer sector-specific guidance on addressing common deficiencies identified during regulatory inspections.
Creating a Support Compliance Culture
Technical systems and documented procedures provide the compliance framework, but sustainable support compliance requires a culture where every team member understands their role in protecting clients and maintaining regulatory standing.
Leadership Commitment and Tone from the Top
Compliance culture begins with visible leadership commitment. When principals and senior management demonstrate that support compliance is a strategic priority rather than an administrative burden, staff respond accordingly.
Practical demonstrations of leadership commitment include:
- Resource allocation: Investing in compliance training, technology, and specialist support
- Performance metrics: Including compliance measures in staff evaluations and reward structures
- Personal involvement: Senior management participating in support training and quality monitoring
- Open communication: Regular updates on regulatory developments and their support implications
- Accountability: Consistent consequences for compliance failures regardless of seniority
For independent brokers, your personal approach to support compliance sets the standard. If you shortcut procedures when busy or dismiss complaints as client unreasonableness, any support staff or virtual assistants will follow that example.
Continuous Learning and Improvement
The regulatory environment continues evolving, with POPIA, FICA, and COFI amendments regularly changing compliance requirements. Support compliance demands ongoing learning that keeps pace with regulatory developments.
Establish mechanisms for continuous improvement:
- Subscribe to FSCA communications and regulatory update services
- Participate in industry forums sharing compliance practices and lessons learned
- Conduct post-incident reviews analysing what happened and how to prevent recurrence
- Benchmark your support compliance against peer FSPs and industry standards
- Solicit client feedback on support experiences and compliance pain points
The compliance monitoring guidance available through industry resources helps FSPs maintain current knowledge of regulatory expectations and emerging compliance risks.
Annual support compliance reviews should assess policy effectiveness, identify improvement opportunities, and plan investments in enhanced capabilities. This forward-looking approach prevents compliance from becoming a reactive scramble responding to regulatory pressure.
Practical Implementation Checklist
Translating support compliance requirements into operational reality requires systematic implementation across people, processes, and technology. Use this checklist to assess your current state and identify priority actions.
Assessment and Gap Analysis
Regulatory alignment review:
- POPIA: Documented processing purposes for each support channel
- POPIA: Consent management system capturing, storing, and verifying permissions
- POPIA: Data security controls appropriate to sensitivity of information accessed
- FICA: Identity verification procedures for each support interaction level
- FICA: Suspicious transaction identification training and escalation protocols
- FICA: Ongoing client information update processes during routine support
- FAIS: Clear distinction between support queries and financial advice requiring full procedures
- FAIS: Record-keeping systems capturing all client interactions with appropriate retention
- COFI: Defined support standards demonstrating fair customer treatment
- COFI: Vulnerable client identification and tailored support protocols
Operational capability review:
- Support staff trained on all relevant regulations with documented competency
- Quality monitoring programme reviewing representative sample of interactions
- Complaint handling procedures meeting FSCA timeline and documentation requirements
- Vendor management framework if any support functions are outsourced
- Technology platforms enabling compliance-by-design in daily operations
- Management information providing visibility into compliance performance
- Regular compliance reporting to governance structures
- Incident response procedures for data breaches or significant violations
Priority Implementation Actions
Based on gap analysis, prioritise improvements addressing the highest risks first. For most FSPs, critical actions include:
-
Immediate (within 30 days)
- Implement multi-factor authentication for systems accessing client information
- Establish complaint register capturing all expressions of dissatisfaction
- Conduct emergency training on POPIA consent requirements
- Review and restrict use of uncontrolled communication channels (personal WhatsApp, unencrypted email)
-
Short-term (within 90 days)
- Deploy comprehensive support compliance training programme
- Implement quality monitoring with monthly review of sample interactions
- Update client communication templates incorporating required POPIA disclosures
- Establish vendor management framework if using third-party support
-
Medium-term (within 180 days)
- Upgrade CRM or support systems with integrated compliance workflows
- Conduct comprehensive FICA verification refresh for existing client base
- Implement automated consent management platform
- Develop analytics dashboard tracking key support compliance metrics
-
Ongoing
- Quarterly training refreshers responding to regulatory updates
- Annual vendor audits and due diligence reviews
- Monthly compliance reporting to management
- Continuous process refinement based on lessons learned
Support compliance is not a project with a completion date; it's an ongoing operational discipline requiring sustained attention and investment. The regulatory environment will continue evolving, client expectations will shift, and new technologies will create both opportunities and risks. Building adaptive support compliance capabilities positions your FSP for long-term success in South Africa's dynamic regulatory landscape.
Effective support compliance protects your clients, safeguards your FSP licence, and demonstrates the professionalism that distinguishes quality financial service providers. By systematically addressing POPIA, FICA, FAIS, and COFI requirements across your support operations, you build sustainable compliance capability that evolves with the regulatory environment.
For independent brokers, regulated financial advisors, and compliance officers: Holistic Compliance Management Solutions (Pty) Ltd provides specialist compliance monitoring services designed specifically for South African financial service providers.
Book a compliance consultation to assess your current support compliance framework and identify priority improvements:
- Comprehensive gap analysis across POPIA, FICA, FAIS, and COFI requirements
- Tailored recommendations addressing your specific practice structure and client base
- Implementation roadmap with practical, actionable steps
Schedule your consultation today to ensure your support operations meet regulatory expectations and deliver the fair customer outcomes the FSCA demands.