ServiceNow GRC for Financial Services Compliance in SA
For independent financial advisors and FSPs operating under South Africa's increasingly complex regulatory landscape, managing compliance across POPIA, FICA, FAIS, and COFI requirements demands more than spreadsheets and good intentions. The modern compliance environment requires systematic governance, integrated risk assessment, and real-time monitoring capabilities. ServiceNow GRC (now branded as Integrated Risk Management or IRM) offers financial services providers a unified platform to orchestrate these critical compliance activities, bringing together policy management, risk registers, control testing, and audit workflows into a single source of truth. As South African regulators intensify their focus on conduct, data protection, and anti-money laundering controls, understanding how enterprise GRC platforms can support broker compliance operations becomes essential for sustainable practice management.
Understanding ServiceNow GRC for Financial Services Compliance
ServiceNow GRC represents a comprehensive approach to managing governance, risk, and compliance activities through a unified technology platform. According to the official ServiceNow product documentation, the platform provides an integrated framework for identifying risks, mapping controls, conducting assessments, and maintaining evidence across the entire organisation.
For South African financial services providers, this integration proves particularly valuable because regulatory requirements don't exist in isolation. POPIA data protection obligations intersect with FICA client verification processes, whilst FAIS fit and proper requirements connect directly to training records and competency management. Traditional siloed compliance approaches create gaps where these intersections occur.
Core Capabilities Relevant to FSP Operations
The servicenow grc platform delivers several foundational capabilities that align with financial services compliance needs:
- Policy and compliance management for maintaining current regulatory libraries and mapping requirements to controls
- Risk register and assessment tools for documenting and quantifying operational, conduct, and financial crime risks
- Control testing and attestation workflows for evidence collection and supervisor sign-offs
- Audit management for coordinating FSCA inspections, internal reviews, and remediation tracking
- Vendor risk assessment for evaluating third-party service providers and product suppliers
- Regulatory change management for tracking amendments to FAIS, FICA, POPIA, and COFI requirements
These modules work together on a common data model, ensuring that when you update a control in response to a POPIA amendment, all linked risks, policies, and audit findings automatically reflect that change.
Mapping South African Financial Services Regulations to GRC Workflows
Implementing servicenow grc effectively requires translating regulatory obligations into structured workflows and control frameworks. Financial advisors and FSPs must map four primary regulatory domains within the platform.
POPIA Data Protection Framework
The Protection of Personal Information Act establishes eight conditions for lawful processing of client information. Within ServiceNow GRC, these translate to:
| POPIA Condition | GRC Implementation Approach | Key Controls |
|---|---|---|
| Accountability | Policy library with designated Information Officer role | Governance structure, training records, incident response plan |
| Processing limitation | Purpose mapping for client data categories | Consent workflows, retention schedules, processing registers |
| Purpose specification | Data inventory with declared purposes | Client notification templates, privacy notices |
| Further processing limitation | Change control for new processing activities | Impact assessments, consent updates |
| Information quality | Data accuracy validation rules | Client verification processes, update workflows |
| Openness | Transparency documentation | PAIA manual, privacy policy publication |
| Security safeguards | Technical and organisational controls | Access controls, encryption, audit logs |
| Data subject participation | Request management workflows | Access requests, correction processes, objection handling |
The platform allows you to build control libraries aligned to each condition, assign ownership to specific roles (compliance officer, Information Officer, practice principal), and schedule recurring attestations to confirm controls remain effective.
FICA Client Verification and Ongoing Monitoring
Financial Intelligence Centre Act compliance centres on client due diligence and ongoing monitoring. ServiceNow GRC supports this through automated workflows that track verification status across your client base.
Client onboarding workflow components:
- Risk categorisation based on client profile (individual, legal entity, foreign national, PEP screening)
- Document collection checklist (ID verification, proof of residence, source of funds for high-risk clients)
- Verification sign-off by authorised representative
- Record retention with automated expiry alerts for time-limited documents
- Escalation protocols when verification cannot be completed within regulatory timeframes
For independent brokers managing FICA RMCP programmes, the platform provides a centralised repository for risk management and compliance programme documentation, linking client-level CDD records to your enterprise-wide FICA policies and control environment.
Ongoing monitoring automation:
- Scheduled re-verification triggers based on risk category (annual for high-risk, three-yearly for lower-risk)
- Transaction monitoring threshold alerts integrated with policy administration systems
- PEP and sanctions list screening workflows with quarterly refresh cycles
- Suspicious transaction report (STR) case management with FIC submission tracking
FAIS Compliance and Conduct Management
The Financial Advisory and Intermediary Services Act establishes fit and proper requirements, conduct standards, and client disclosure obligations. ServiceNow GRC maps these requirements to operational controls within broker practices.
Key representative and competency tracking:
The platform maintains a skills matrix linking each representative to:
- Current regulatory examination status (RE 5, RE 1, specific product categories)
- CPD credit accumulation with automatic alerts 60 days before compliance deadlines
- Fit and proper declarations with annual attestation workflows
- Supervision arrangements and oversight evidence
- Complaints and conduct incidents for pattern analysis
Product supplier due diligence:
FAIS requires FSPs to satisfy themselves that product suppliers are financially sound and meet operational standards. Within servicenow grc, vendor risk assessment modules support:
- Initial supplier approval workflows with financial analysis and compliance verification
- Ongoing monitoring schedules based on supplier risk ratings
- Contract management with renewal tracking and performance reviews
- Issues register for supplier-related client complaints or service failures
COFI Conduct Standards Implementation
The Conduct of Financial Institutions Act introduces explicit conduct obligations and fair treatment principles. GRC platforms help FSPs demonstrate systematic adherence through:
- Culture and governance monitoring via employee surveys, whistleblower case management, and board reporting dashboards
- Product governance frameworks tracking product approval, review cycles, and target market assessments
- Complaints management with root cause analysis and remediation tracking against TCF outcomes
- Disclosure and communication controls ensuring client communications meet plain language and fair treatment standards
The Forrester Wave on GRC platforms highlights how leading solutions now incorporate AI-driven insights to identify conduct risk patterns across customer interactions, particularly valuable as COFI enforcement intensifies in 2026.
Implementing ServiceNow GRC in Financial Services Practices
Successful GRC implementation requires structured planning and phased deployment. For independent brokers and smaller FSPs, the full enterprise platform may exceed immediate needs, but understanding the implementation framework helps evaluate scaled alternatives or managed service options.
Phase 1: Foundation and Regulatory Mapping
The initial phase establishes your compliance baseline and translates regulatory requirements into structured data.
Regulatory library build:
- Import current versions of POPIA, FICA, FAIS General Code of Conduct, COFI conduct standards, and relevant Board Notices
- Map specific regulatory citations to compliance obligations (e.g., FAIS GCC Section 8 maps to conflicts of interest disclosure)
- Create obligation owners within your practice structure (compliance officer, principal, key individual)
- Establish update protocols for regulatory amendments
Risk assessment framework:
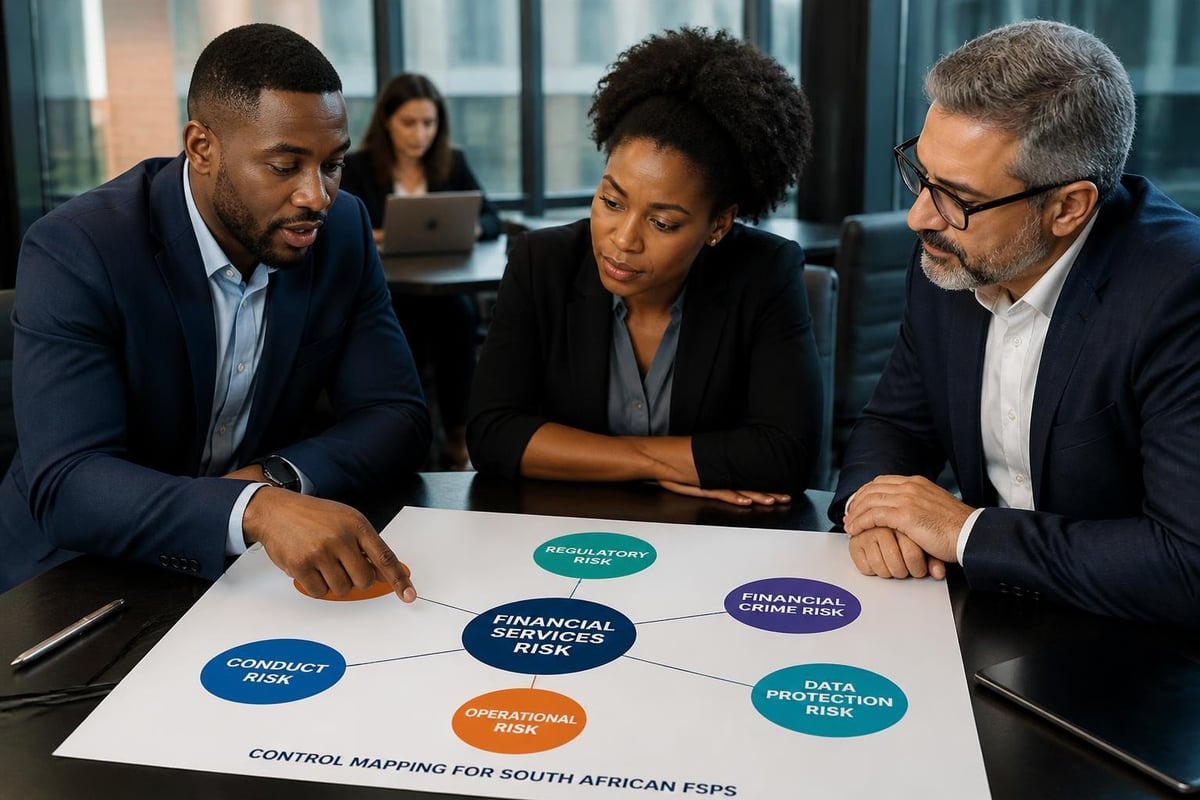
Start with a tailored risk taxonomy covering financial services operational realities:
- Regulatory risk: FSCA enforcement, licence conditions breaches, conduct failures
- Financial crime risk: Money laundering, sanctions breaches, fraud
- Data protection risk: POPIA breaches, client information security incidents
- Operational risk: System failures, errors in advice processes, outsourcing failures
- Conduct risk: Mis-selling, unsuitable advice, complaints escalation
Document inherent risk ratings, existing controls, and residual risk to establish your baseline risk profile. The NIST Risk Management Framework provides a structured approach to categorising information systems and controls that many GRC platforms reference.
Phase 2: Control Library and Evidence Collection
With regulatory obligations and risks mapped, build your control environment within the servicenow grc platform.
Control design principles:
- Preventive controls that stop issues before they occur (system access restrictions, automated verification checks, mandatory training completion before licence approval)
- Detective controls that identify issues when they happen (transaction monitoring alerts, complaint trend analysis, audit sampling)
- Corrective controls that remediate identified issues (incident response procedures, remediation workflows, enhanced monitoring for high-risk areas)
| Control Category | Example Controls for FSPs | Testing Frequency | Evidence Types |
|---|---|---|---|
| Access management | Role-based system access for client data | Quarterly review | Access logs, approval records |
| Client verification | FICA CDD checklist completion | Transaction-based | Verification documents, sign-offs |
| Competency | RE exam and CPD compliance checks | Annual attestation | Training records, exam certificates |
| Disclosure | COI register maintenance and disclosure | Per transaction | Disclosure forms, client acknowledgements |
| Data protection | Encryption of personal information | Continuous monitoring | Security scan reports, configuration settings |
| Complaints management | Client complaint response within 6 weeks | Case-by-case | Case files, resolution documentation |
Evidence collection automation:
Rather than manual evidence gathering before audits, configure the platform to collect evidence continuously:
- Integrate with policy administration systems to pull transaction records
- Connect to learning management systems for automatic CPD credit updates
- Link to email archives for client communication evidence
- Automate screenshot capture of system configurations demonstrating controls
This approach, detailed in KPMG’s guidance on modern risk and compliance systems, reduces compliance burden whilst improving audit readiness.
Phase 3: Workflow Automation and Continuous Monitoring
The true value of servicenow grc emerges when manual compliance processes transform into automated workflows with exception management.
Attestation campaigns:
Schedule recurring attestations for control owners to confirm controls operate effectively:
- Annual fit and proper declarations from all representatives
- Quarterly vendor risk reviews for product suppliers
- Monthly confirmation of FICA client verification status for high-risk clients
- Bi-annual review of POPIA processing purposes and legal bases
The platform tracks completion rates, sends automatic reminders, and escalates to supervisors when deadlines pass.
Integrated monitoring dashboards:
Configure role-specific dashboards providing real-time compliance visibility:
For compliance officers:
- Open FICA verifications approaching regulatory deadlines
- Representatives with CPD deficiencies within 90 days of year-end
- Unresolved high-risk audit findings
- Month-on-month complaint trends by category
For practice principals:
- Overall regulatory risk rating and movement trends
- Control effectiveness scores across risk domains
- Upcoming regulatory changes requiring implementation
- Resource allocation for compliance activities
For FSCA audit readiness:
- Complete evidence repositories organised by regulatory requirement
- Control testing results with failure analysis and remediation tracking
- Incident registers with root cause analysis and corrective actions
- Board and senior management oversight evidence
The OpsMatters overview of ServiceNow IRM demonstrates how operational teams use these dashboards to run compliance activities without constant manual reporting.
Integration with Financial Services Technology Stack
ServiceNow GRC doesn't operate in isolation. For FSPs, value comes from integration with existing practice management, CRM, and regulatory systems.
Critical Integration Points for South African Brokers
Policy administration system connections:
Extract transaction data, client details, and policy information to support:
- Automated FICA ongoing monitoring based on transaction patterns
- Product governance reviews using actual sales data
- Complaints analysis linking to specific products or representatives
CRM and client communication platforms:
Pull communication logs and client interaction records to evidence:
- Disclosure delivery and client acknowledgement
- Complaints received through all channels (email, phone, web forms)
- Client consent for marketing and data processing purposes
Learning management systems:
Synchronise training records to maintain:
- Current RE examination status for all representatives
- CPD credit allocation by category and provider
- FICA, POPIA, and product-specific training completion dates
Document management repositories:
Link to centralised storage for:
- Client verification documents and supporting evidence
- Policy libraries and procedure manuals
- Audit reports and remediation documentation
- Board minutes and governance records
According to Bloor Research’s analysis of ServiceNow Integrated Risk Management, integration capabilities represent a key differentiator, allowing organisations to leverage existing technology investments rather than recreating data in isolated compliance tools.
Practical Implementation Checklist for FSP Compliance
For independent brokers and smaller FSPs evaluating servicenow grc or similar platforms, this implementation checklist provides a structured approach.
Pre-Implementation Planning (Weeks 1-4)
Stakeholder alignment:
- Secure principal and board commitment with business case showing audit cost reduction and risk mitigation
- Identify compliance champion with platform administration responsibility
- Define roles for control owners across practice (admin, compliance officer, key individuals, representatives)
Regulatory scope definition:
- List all applicable regulations (POPIA, FICA, FAIS, COFI, specific Board Notices)
- Identify upcoming regulatory changes requiring implementation in 2026-2027
- Document current compliance gaps identified in previous audits or self-assessments
Data preparation:
- Audit existing client verification status and documentation completeness
- Compile current policy library and procedure manuals
- Gather representative licensing, competency, and training records
- Document existing risk register and control descriptions
Configuration and Customisation (Weeks 5-12)
Platform setup:
- Configure user roles matching your practice structure (principal, compliance officer, representatives, admin staff)
- Build regulatory library with POPIA, FICA, FAIS, and COFI requirements mapped to specific citations
- Create risk taxonomy aligned to financial services operational model
- Design control library with ownership assignments and testing schedules
- Develop workflow templates for common processes (FICA verification, CPD tracking, complaint management, incident response)
Integration development:
- Establish connections to policy administration, CRM, and learning management systems
- Configure automated data feeds for transaction monitoring and training records
- Set up document repository links for evidence storage
Testing and validation:
- Run pilot attestation campaign with small group of control owners
- Test workflow automation with sample FICA verifications and complaint cases
- Validate reporting dashboards against known compliance data
Rollout and Training (Weeks 13-16)
User training programmes:
- Platform overview for all staff explaining how GRC supports compliance activities
- Detailed workflow training for control owners and attestation participants
- Dashboard and reporting training for compliance officers and principals
- Evidence collection training for representatives
Phased deployment:
Rather than attempting to implement all compliance domains simultaneously, phase rollout:
- Phase 1: FICA client verification workflows and POPIA data protection controls
- Phase 2: FAIS competency tracking and CPD management
- Phase 3: COFI conduct monitoring and complaints management
- Phase 4: Vendor risk assessment and product governance
This approach, recommended in the INRY healthcare case study, reduces change management resistance and allows learning from early phases to improve later implementations.
Continuous Improvement (Ongoing)
Monthly activities:
- Review dashboard metrics for compliance trends and emerging risks
- Address overdue attestations and control testing failures
- Update regulatory library with amendments and new requirements
- Analyse incident and complaint data for systemic issues
Quarterly activities:
- Conduct control effectiveness reviews and adjust testing frequency
- Update risk ratings based on incident data and regulatory developments
- Review integration performance and data quality
- Provide board reporting on compliance status and risk profile
Annual activities:
- Comprehensive risk assessment refresh aligned to business planning cycle
- Full policy library review and update
- Platform optimisation based on user feedback and process efficiency analysis
- External audit coordination using platform-generated evidence
Addressing Common FSP Implementation Challenges
Financial services practices encounter specific challenges when implementing servicenow grc systems. Understanding these obstacles enables proactive mitigation.
Resource Constraints in Smaller Practices
Independent brokers and boutique FSPs rarely have dedicated compliance technology teams. This reality creates several pain points:
Challenge: Limited internal IT resources for platform administration and integration development.
Mitigation strategies:
- Engage ServiceNow partner firms specialising in financial services implementations
- Consider managed service options where compliance consultants operate the platform on your behalf
- Start with core modules (policy management, risk register, audit management) before complex workflow automation
- Leverage pre-built templates and industry frameworks rather than custom development
Challenge: Compliance officer capacity for data migration and evidence collection.
Mitigation strategies:
- Prioritise high-risk compliance areas (FICA for high-risk clients, representatives with CPD deficiencies) for initial data load
- Implement prospective data collection for new clients and leave historical remediation to natural verification cycles
- Train representatives to capture evidence during normal workflow rather than retrospective collection
Data Quality and System Integration Issues
Compliance platforms are only as valuable as the data they contain. Common data quality issues include:
- Incomplete client verification records from legacy systems
- Inconsistent representative training data across multiple providers
- Outdated policy documentation and control descriptions
- Fragmented evidence stored across email, file shares, and paper archives
The ISACA Journal article on managing cyber risk with GRC emphasises that continuous monitoring requires clean, integrated data foundations. For FSPs, this means:
- Establishing data quality standards before platform deployment
- Implementing validation rules to prevent incomplete record creation
- Scheduling periodic data cleansing campaigns to remediate historical issues
- Treating data quality as an ongoing programme rather than one-time project
Regulatory Change Management
South Africa's financial services regulatory environment continues evolving. Recent and upcoming changes include:
- POPIA enforcement intensification: Information Regulator enforcement actions increased significantly in 2025-2026
- COFI implementation: Conduct standards rollout continues across financial services sectors
- FICA amendments: Enhanced beneficial ownership and PEP screening requirements
- FAIS updates: Ongoing refinement of fit and proper requirements and CPD frameworks
Platform configuration for regulatory agility:
Configure servicenow grc to accommodate regulatory changes without requiring extensive redevelopment:
- Build flexible obligation libraries that support versioning when regulations are amended
- Map controls to regulatory principles rather than specific rule citations where possible
- Establish change management workflows to assess impact of regulatory amendments
- Maintain regulatory horizon scanning calendars with implementation deadline tracking
This approach, detailed in the practitioner analysis of ServiceNow IRM evolution, ensures your compliance programme adapts to regulatory change without platform obsolescence.
Measuring ROI and Compliance Programme Effectiveness
Financial services principals need to justify GRC platform investments through measurable returns and risk reduction.
Quantifiable Benefits for FSPs
Audit preparation time reduction:
- Before GRC platform: 40-60 hours of evidence gathering and documentation compilation before FSCA inspections or internal audits
- After implementation: 10-15 hours reviewing automated evidence packages and addressing specific auditor queries
- Annual savings: 25-45 hours of compliance officer time per audit cycle
Remediation tracking efficiency:
- Before GRC platform: Manual tracking of audit findings in spreadsheets with frequent status update requests
- After implementation: Automated remediation workflows with deadline alerts and supervisor escalation
- Improvement: 60-80% reduction in overdue remediation items and repeat audit findings
Regulatory breach reduction:
- Before GRC platform: Reactive identification of CPD deficiencies, expired FICA verifications, and lapsed representative licences
- After implementation: Proactive alerts enabling remediation before regulatory breach occurs
- Risk mitigation: Estimated 70-90% reduction in technical compliance breaches
Qualitative Risk Management Improvements
Beyond time savings, servicenow grc delivers risk management benefits that strengthen practice resilience:
Enhanced governance and oversight:
Principals and boards gain real-time visibility into compliance status, enabling informed risk decisions and resource allocation. This proves particularly valuable during periods of rapid regulatory change or practice growth.
Improved regulatory relationship management:
When FSCA inspectors request information, immediate evidence production demonstrates compliance maturity and reduces inspection duration and follow-up requirements.
Stronger culture of compliance:
Systematic workflows and automated attestations embed compliance into daily operations rather than treating it as periodic activity, improving representative engagement and reducing resistance.
Better client outcomes:
Consistent application of FICA verification, disclosure processes, and complaints management directly supports TCF outcomes and reduces conduct risk exposure.
Advanced Capabilities: AI and Continuous Monitoring
Modern servicenow grc implementations increasingly incorporate artificial intelligence and machine learning to enhance compliance effectiveness.
AI-Powered Risk Detection
Recent platform enhancements include:
- Natural language processing for analysing client complaints and identifying conduct risk patterns across seemingly unrelated cases
- Anomaly detection for transaction monitoring, flagging unusual patterns that may indicate money laundering or fraud
- Predictive analytics for forecasting compliance resource requirements based on business growth and regulatory change pipelines
- Automated control testing using AI to sample transactions and verify control operation without manual review
For South African FSPs, these capabilities particularly support:
FICA ongoing monitoring:
Machine learning algorithms analyse client transaction patterns and flag behaviour inconsistent with verified risk profiles, triggering enhanced due diligence workflows.
COFI conduct surveillance:
AI reviews client communications, complaint narratives, and product sales patterns to identify potential fair treatment concerns before they escalate to regulatory breaches.
POPIA breach detection:
Anomaly detection monitors access to personal information, identifying potential data breaches or unauthorised access requiring notification to the Information Regulator.
Continuous Controls Monitoring
Traditional compliance operates on periodic cycles (annual audits, quarterly attestations, monthly reviews). Continuous monitoring shifts to real-time surveillance:
- Always-on control testing: Automated sampling and verification run constantly rather than on schedules
- Dynamic risk scoring: Risk ratings update automatically based on incident frequency, audit findings, and external threat intelligence
- Instant remediation triggering: Control failures immediately generate remediation workflows rather than waiting for review meetings
This approach aligns with regulatory expectations for sophisticated risk management, particularly under COFI's conduct risk management requirements.
ServiceNow GRC Alternatives and Considerations for FSPs
Whilst servicenow grc offers comprehensive capabilities, independent brokers should evaluate whether the full enterprise platform matches their scale and needs.
Platform Sizing Considerations
Full ServiceNow IRM implementation:
- Best suited for larger FSPs (50+ representatives, multiple branch locations, diverse product portfolios)
- Requires dedicated platform administrator and integration development resources
- Licensing costs typically justify where compliance team size exceeds 3-4 FTEs
- Implementation timeline of 3-6 months with ongoing customisation programme
Scaled alternatives for smaller practices:
- Managed service GRC platforms: Compliance consultancies operate the platform on behalf of multiple broker clients, sharing costs
- Purpose-built FSP compliance tools: South African vendors offer solutions specifically designed for FAIS/FICA/POPIA compliance at SME scale
- Modular implementations: Deploy specific ServiceNow modules (policy management, audit management) without full IRM suite
- Enhanced spreadsheet frameworks: For micro-practices (1-5 representatives), well-designed templates with embedded workflows provide meaningful improvement over ad-hoc approaches
Selection criteria:
| Factor | Enterprise GRC Platform | Managed Service Option | Purpose-Built FSP Tool |
|---|---|---|---|
| Practice size | 50+ representatives | 10-50 representatives | 1-20 representatives |
| Compliance team | Dedicated team of 3+ | 1-2 compliance officers | Principal + outsourced support |
| IT resources | Internal IT team | No IT resources required | Minimal IT requirements |
| Customisation needs | Complex, unique workflows | Standard FSP processes | Standard FSP processes |
| Integration requirements | Multiple systems | Core systems only | Limited integrations |
| Budget | R500k+ annually | R100k-300k annually | R30k-100k annually |
The key is matching platform sophistication to compliance complexity and available resources, ensuring the solution enhances rather than burdens compliance activities.
ServiceNow GRC and integrated risk management platforms offer South African financial services providers powerful tools to systematically manage POPIA, FICA, FAIS, and COFI compliance requirements through unified workflows, automated evidence collection, and continuous monitoring. For independent brokers and FSPs navigating increasingly complex regulatory expectations, the structured approach these platforms enable transforms compliance from reactive crisis management to proactive risk mitigation. Whether you're preparing for FSCA inspections, responding to POPI Act enforcement, or building sustainable compliance programmes as your practice grows, Holistic Compliance Management Solutions (Pty) Ltd provides independent compliance services, regulatory training, and practice management support tailored to South African financial advisors. Schedule FICA training to strengthen your compliance foundation with practical guidance on risk management and compliance programme implementation, POPI and FICA regulatory requirements, and evidence collection for audit readiness. This service is designed for independent brokers seeking systematic compliance approaches, regulated FSPs preparing for regulatory inspections, and compliance officers implementing structured risk frameworks.