Regulatory Compliance Training for South African FSPs
Regulatory compliance training has become non-negotiable for South African financial services providers navigating an increasingly complex legislative landscape. Independent financial advisors, insurance brokers, and FSP licence holders face overlapping obligations under POPIA, FICA, FAIS, and the Conduct of Financial Institutions (COFI) Bill, each demanding specific knowledge, procedural competence, and cultural commitment. A structured training programme transforms regulatory burden into competitive advantage, reducing risk exposure whilst building client trust and operational resilience.
Understanding the South African Compliance Training Landscape
The financial services sector in South Africa operates within a multi-layered regulatory framework that has expanded significantly since 2018. The Protection of Personal Information Act (POPIA), Financial Intelligence Centre Act (FICA), Financial Advisory and Intermediary Services Act (FAIS), and the anticipated COFI legislation create intersecting obligations that independent brokers must navigate simultaneously.
Core Legislative Pillars for FSPs
POPIA governs how financial advisors collect, process, store, and share client personal information. Every broker handling client data must demonstrate lawful processing grounds, implement security safeguards, and respect client rights to access and deletion.
FICA establishes customer due diligence requirements to combat money laundering and terrorist financing. FSPs must verify client identity, understand beneficial ownership structures, conduct ongoing monitoring, and report suspicious transactions.
FAIS regulates the conduct of financial services providers, setting competency standards, disclosure requirements, and fiduciary duties. Representatives must maintain appropriate qualifications and adhere to the General Code of Conduct.
COFI (pending implementation) will introduce a market conduct regulatory framework focusing on treating customers fairly, product governance, and cultural accountability across the financial sector.
| Legislation | Primary Focus | Key Training Requirements |
|---|---|---|
| POPIA | Data protection | Lawful processing, consent, security measures, breach response |
| FICA | Anti-money laundering | Client verification, beneficial ownership, risk assessment, reporting |
| FAIS | Conduct standards | Product knowledge, needs analysis, disclosure, conflicts of interest |
| COFI | Market conduct | Fair treatment, product design, complaints handling, cultural embedding |
Building a Comprehensive Regulatory Compliance Training Programme
Effective regulatory compliance training extends beyond tick-box exercises. It requires systematic design, role-specific content, continuous reinforcement, and measurable outcomes. The NIST framework for cybersecurity and privacy learning provides valuable programme-level guidance applicable to compliance training architecture.
Programme Design Principles
Risk-based prioritization ensures training resources address the highest-impact compliance gaps first. Independent brokers should assess which regulations pose the greatest enforcement risk or operational disruption if breached.
Role-specific customization recognizes that compliance officers, client-facing representatives, and administrative staff require different depth and application focus. A receptionist needs basic POPIA awareness; a key individual needs comprehensive FICA implementation knowledge.
Continuous learning cycles replace annual compliance marathons with quarterly refreshers, monthly case studies, and real-time updates when regulations change. This approach improves retention and embeds compliance into daily workflows.
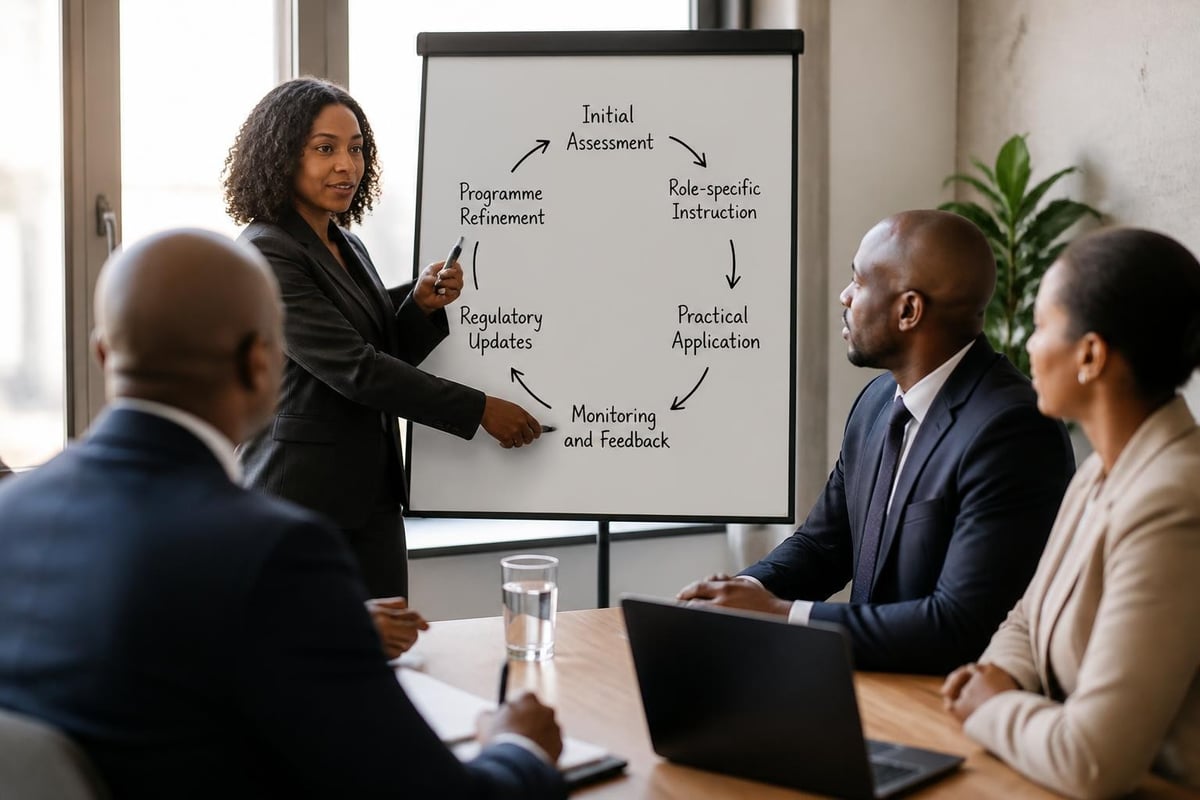
Research from the OCEG compliance and ethics training survey reveals that organizations measuring training impact (behavioural change, risk reduction) rather than activity (hours completed, attendance) achieve significantly better compliance outcomes. South African brokers should track metrics like reduction in FICA verification errors, decrease in POPIA breach incidents, and improvement in client file audit scores.
POPIA Compliance Training for Financial Advisors
POPIA compliance demands that every team member who touches client information understands their responsibilities as an operator within your practice. Training must cover eight conditions for lawful processing, accountability structures, and practical implementation.
Essential POPIA Training Modules
- Lawful processing foundations: Conditions for lawful processing, consent requirements, legitimate interests balancing, special personal information restrictions
- Information officer responsibilities: Accountability obligations, PAIA manual integration, notification to Information Regulator, breach response protocols
- Security safeguards: Physical security measures, electronic access controls, encryption requirements, secure disposal procedures
- Client rights management: Access requests, correction procedures, deletion obligations, objection handling, direct marketing opt-outs
- Third-party data sharing: Operator agreements, cross-border transfer restrictions, vendor due diligence, cloud service considerations
Practical application exercises should include analyzing real client scenarios, drafting consent notices, conducting privacy impact assessments, and simulating breach response. Independent brokers benefit from template libraries covering consent forms, privacy notices, operator agreements, and breach notification letters.
POPIA Implementation Checklist for Brokers
- Appoint an Information Officer and register with the Information Regulator
- Conduct a personal information audit across all client touchpoints
- Update client onboarding forms with POPIA-compliant consent notices
- Implement access controls limiting staff to necessary client information
- Establish secure document destruction procedures for paper and electronic records
- Draft and publish a privacy policy accessible to clients
- Create breach response protocols with notification templates
- Train all staff on their specific POPIA responsibilities quarterly
- Document training attendance and competency assessments
- Review and update data processing activities register annually
FICA and RMCP Training Requirements
The Financial Intelligence Centre Act places significant obligations on accountable institutions, including most FSPs. Regulatory compliance training must equip staff to conduct customer due diligence, identify suspicious activities, and maintain risk management and compliance programmes (RMCPs).
FICA Training Core Components
Client identification and verification forms the foundation of FICA compliance. Staff must understand acceptable identification documents, verification procedures for individuals versus legal entities, beneficial ownership identification thresholds, and enhanced due diligence triggers.
Risk assessment methodologies enable brokers to classify clients according to money laundering and terrorist financing risk. Training should cover risk factors (geographic location, product type, client profile, transaction patterns), risk categorization matrices, and escalation procedures for high-risk relationships.
Ongoing monitoring and reporting obligations require staff to recognize unusual transactions, understand reporting thresholds for cash transactions, identify suspicious activity indicators, and follow internal reporting channels to the Money Laundering Control Officer (MLCO).
| FICA Obligation | Staff Level | Training Frequency | Competency Assessment |
|---|---|---|---|
| Basic client verification | All client-facing | Quarterly | Scenario testing |
| Beneficial ownership | Senior advisors | Bi-annually | Case study analysis |
| Suspicious transaction reporting | All staff | Quarterly | Red flag identification |
| RMCP maintenance | Compliance officers | Annually | Regulatory updates |
For brokers requiring comprehensive support, FICA RMCP services provide training and affordable solutions for drafting risk management and compliance programmes tailored to independent practices.
Building Effective FICA Training Delivery
Case-based learning proves particularly effective for FICA compliance. Present anonymized scenarios involving complex ownership structures, cross-border transactions, politically exposed persons, or unusual investment patterns. Participants analyze risk factors, determine appropriate due diligence levels, and decide whether reporting is required.
Regular typology updates keep staff aware of emerging money laundering methods specific to the financial advisory sector. The Financial Intelligence Centre publishes guidance and typology reports that should inform training content quarterly.
Documentation standards must be emphasized throughout FICA training. Even perfect client verification provides no protection if inadequately documented. Training should include completing client acceptance forms, recording verification steps, documenting risk assessment decisions, and maintaining audit trails.
FAIS Conduct Standards and Competency Requirements
The General Code of Conduct for Authorised Financial Services Providers and Representatives establishes ethical and professional standards that require ongoing training reinforcement. Regulatory compliance training under FAIS addresses both technical competency and conduct obligations.
FAIS Training Programme Structure
- Product knowledge maintenance: Regular updates on investment products, insurance structures, retirement solutions, regulatory changes affecting product suitability
- Needs analysis procedures: Client profiling techniques, risk tolerance assessment, financial goal identification, appropriate advice formulation
- Disclosure obligations: Remuneration disclosure, conflict of interest identification, product information provision, record of advice requirements
- Treating customers fairly: Fair treatment principles, vulnerable client considerations, complaint handling, redress mechanisms
- Record-keeping standards: Advice documentation, client file management, retention periods, audit readiness
Regulatory exam preparation forms a critical component for new representatives entering the industry. Structured training programmes covering the regulatory framework, product knowledge, and ethical conduct prepare candidates for mandatory examinations.
Practical FAIS Compliance Scenarios
Training effectiveness increases when participants work through realistic situations encountered in independent broker practices:
- A client requests investment advice but refuses to complete a full financial needs analysis
- A product provider offers enhanced commission on a particular investment platform
- A client complains that disclosed fees differ from amounts actually deducted
- Regulatory changes affect the suitability of existing client investments
- A family member seeks financial advice creating potential conflicts of interest
Participants should identify compliance obligations, evaluate appropriate responses, and document decisions according to FAIS requirements. This scenario-based approach, recommended in the OECD guidance on internal controls and ethics, builds practical judgment alongside technical knowledge.
Preparing for COFI: Cultural Change Through Training
The Conduct of Financial Institutions Bill represents a paradigm shift from rules-based to principles-based regulation, emphasizing cultural accountability and treating customers fairly. Effective regulatory compliance training must begin preparing FSPs for this transition now.
COFI Readiness Training Components
Fair treatment principles extend beyond individual transactions to systemic practices affecting customer outcomes. Training should explore how product design, sales incentives, complaint resolution, and communication strategies demonstrate fair treatment commitments.
Product governance frameworks require FSPs to understand product value, target market definition, distribution appropriateness, and ongoing product monitoring. Advisors must assess whether products meet client needs before recommendation, not merely rely on provider representations.
Complaints as compliance data shifts perspective from viewing complaints as irritations to recognizing them as early warning indicators of systemic issues. Training should cover root cause analysis, complaint trending, and using complaint data to improve processes.
Cultural embedding techniques help translate compliance obligations into daily behaviors. Role-playing exercises, ethical decision frameworks, leadership modeling, and recognition systems reinforce desired compliance culture.
Designing Role-Specific Training Pathways
Generic compliance training achieves minimal impact. Effective programmes tailor content, depth, and application to specific roles within the FSP structure.
Training Pathways by Role
Key individuals and compliance officers require comprehensive regulatory knowledge across POPIA, FICA, FAIS, and COFI. They need advanced skills in risk assessment, regulatory interpretation, programme design, and regulatory liaison. Annual training should include at least 40 hours covering regulatory updates, emerging risks, and compliance management techniques.
Client-facing representatives need practical application knowledge. They must understand how to conduct compliant client onboarding, execute needs analysis, disclose fees and conflicts, verify client information, recognize suspicious transactions, and maintain client confidentiality. Quarterly training of 8-12 hours per year maintains competency.
Administrative and support staff require focused training on their specific compliance touchpoints. Receptionists handling client data need POPIA awareness. Administrative staff processing applications need FICA verification procedures. Support staff managing files need record-keeping standards. Bi-annual training of 4-6 hours addresses these focused needs.
| Role | Annual Training Hours | Primary Focus Areas | Assessment Method |
|---|---|---|---|
| Key Individual | 40+ hours | All regulations, oversight, programme management | Regulatory knowledge exam + case studies |
| Compliance Officer | 35+ hours | Risk assessment, monitoring, regulatory updates | Compliance audit simulation |
| Financial Advisor | 20+ hours | Conduct standards, product knowledge, client processes | Scenario testing + file review |
| Administrative Staff | 6+ hours | POPIA, FICA verification, record-keeping | Procedure competency checks |
Implementing Effective Training Delivery Methods
Training methodology significantly impacts knowledge retention, behavioral change, and compliance outcomes. A blended approach combining multiple delivery methods proves most effective for regulatory compliance training.
Training Delivery Options
In-person workshops enable interactive discussion, immediate question resolution, and relationship building. They work particularly well for complex topics like beneficial ownership determination, ethical dilemma resolution, or new regulatory interpretation. Schedule quarterly sessions of 2-4 hours for optimal engagement without workflow disruption.
Online learning modules provide flexibility for independent brokers managing client commitments. Well-designed e-learning covers foundational knowledge, regulatory updates, and procedure reviews. Include interactive elements (quizzes, branching scenarios, knowledge checks) rather than passive reading. Modules should run 15-30 minutes to maintain attention.
Microlearning refreshers deliver bite-sized compliance reminders integrated into daily workflows. Weekly emails with single compliance tips, monthly case studies, or brief video updates (3-5 minutes) maintain awareness between formal training sessions.
On-the-job coaching embeds compliance into actual work processes. Compliance officers review client files with advisors, provide real-time feedback on documentation, and guide through complex client situations. This apprenticeship model, highlighted in PCAOB quality control standards, builds competency through supervised practice.
Peer learning communities leverage collective experience within the broker community. Monthly roundtable discussions where advisors share compliance challenges, solutions, and regulatory insights create collaborative learning environments. These sessions work particularly well for independent brokers who may feel isolated in compliance responsibilities.
Measuring Training Effectiveness and Compliance Impact
Training hours completed tells you nothing about compliance improvement. Effective measurement tracks knowledge acquisition, behavioral change, and risk reduction.
Compliance Training Metrics Framework
Knowledge assessments measure whether participants understood training content. Use pre-training and post-training quizzes to demonstrate knowledge gain. For ongoing competency, conduct quarterly scenario-based assessments where staff identify compliance requirements in realistic situations.
Behavioral indicators reveal whether training changes actual work practices:
- Percentage of client files with complete FICA verification documentation
- Rate of POPIA consent forms properly executed
- Frequency of conflicts of interest appropriately disclosed
- Quality scores on compliance file audits
- Time elapsed between client engagement and needs analysis completion
Risk reduction metrics demonstrate training's ultimate value:
- Number of regulatory breaches or reportable incidents
- Client complaints related to compliance failures
- Audit findings and remediation requirements
- Regulatory examination results
- Insurance claims related to professional misconduct
Leading versus lagging indicators provide different insights. Lagging indicators (complaints, breaches, enforcement actions) confirm problems occurred. Leading indicators (file audit scores, process completion rates, near-miss identification) predict and prevent future issues.
Building a Sustainable Training Calendar
Compliance obligations don't pause for year-end holidays. A sustainable training calendar distributes learning throughout the year, aligns with regulatory cycles, and accommodates business rhythms.
Annual Training Calendar Template
January-March: POPIA refresher focusing on information security, access controls, and breach response procedures. Coincides with typical IT security reviews and system updates early in the year.
April-June: FICA and anti-money laundering update covering regulatory guidance issued in prior year, typology reports, and enhanced due diligence procedures. Aligns with mid-year compliance reviews.
July-September: FAIS conduct standards and product knowledge update. Schedule before year-end financial planning season when client engagement intensifies.
October-December: COFI readiness and cultural assessment. Year-end period allows reflection on compliance culture, customer treatment, and programme improvements for the coming year.
Monthly: Microlearning modules on specific topics (third-party data sharing, cross-border transfers, beneficial ownership, politically exposed persons, product suitability assessments).
Quarterly: Case-based scenario sessions, regulatory update briefings, and competency assessments.
This distributed approach, informed by research showing continuous learning outperforms annual marathons, maintains engagement and improves retention compared to concentrated training blocks.
Overcoming Common Training Challenges in Independent Practices
Independent brokers and small FSPs face distinct training challenges compared to larger institutions with dedicated learning departments. Practical solutions address these constraints.
Resource and Time Constraints
Challenge: Limited staff means training disrupts client service and revenue generation.
Solution: Implement microlearning and just-in-time training. Fifteen-minute modules completed during administrative time slots provide continuous learning without significant disruption. Create a library of focused resources (checklists, templates, quick-reference guides) accessible when needed rather than requiring comprehensive courses.
Challenge: Training budget limitations restrict access to professional programmes.
Solution: Leverage free regulatory resources (Financial Sector Conduct Authority publications, Financial Intelligence Centre guidance, Information Regulator materials), industry association webinars, and peer learning groups. Invest selectively in professional training for key individuals and compliance officers, then cascade knowledge internally.
Engagement and Retention Challenges
Challenge: Compliance training perceived as tedious obligation rather than valuable skill development.
Solution: Frame training around practical benefits (reduced professional indemnity insurance premiums, faster client onboarding, competitive differentiation, personal liability protection). Use real cases from the South African context demonstrating compliance failures and their consequences.
Challenge: Knowledge retention fades between annual training sessions.
Solution: Space repetition through monthly case studies, quarterly refreshers, and weekly compliance tips. Brief, regular reinforcement builds lasting competency better than intensive annual sessions.
Keeping Content Current
Challenge: Regulatory landscape evolves continuously with new guidance, enforcement priorities, and legislative amendments.
Solution: Subscribe to regulatory newsletters (FSCA, FIC, Information Regulator), join industry associations providing regulatory updates, and schedule quarterly content reviews. Maintain a compliance updates log tracking changes requiring training updates.
Challenge: Translating regulatory text into practical procedures for daily operations.
Solution: Work with compliance specialists who understand independent broker workflows to develop practical implementation guidance. Generic compliance training often fails to address specific operational questions brokers face.
Technology and Tools for Compliance Training Management
Learning management systems (LMS), documentation platforms, and assessment tools can enhance training effectiveness even for small FSPs, but selection must match organizational capacity.
Technology Considerations for Independent Brokers
Learning management systems range from enterprise platforms to simple cloud-based solutions. For small practices, focus on ease of administration, mobile accessibility, and clear reporting. Essential features include:
- Course delivery and tracking
- Quiz and assessment functionality
- Completion certificates
- Basic reporting (who completed what training, when)
- Reminders for upcoming required training
Avoid over-complicated systems requiring dedicated administrators. If setup and maintenance consume more time than manual tracking, the technology adds burden rather than efficiency.
Document management and compliance repositories centralize policies, procedures, templates, and training materials. Cloud-based solutions enable staff to access current resources from any location. Version control ensures everyone works from current procedures as regulations evolve.
Assessment and certification platforms provide professional credibility for training completion. Digital badges, certificates, and CPD (Continuing Professional Development) tracking demonstrate regulatory commitment to supervisors, auditors, and clients.
Integrating Compliance Training with Quality Management
Regulatory compliance training achieves maximum impact when integrated with broader quality management, risk management, and business improvement initiatives rather than operating as an isolated compliance exercise.
Quality Management Integration Points
Client onboarding processes should embed compliance requirements into workflow design. Training on FICA verification, POPIA consent, and needs analysis links directly to client onboarding procedures. Staff learn compliance not as abstract rules but as integral steps in serving clients professionally.
File review and audit processes provide practical feedback loops. Regular compliance file audits identify common errors, revealing training gaps requiring targeted intervention. Review findings inform training content, making it immediately relevant to actual performance issues.
Complaint analysis and root cause investigation often reveal compliance knowledge gaps. If multiple complaints stem from inadequate disclosure, training must address not just what to disclose but how to communicate it effectively. This connection between customer feedback and training content strengthens both.
Risk assessment and mitigation planning should identify compliance training as a key control. Annual risk assessments evaluate whether current training adequately addresses identified compliance risks. This systematic approach ensures training resources address highest-priority risks.
Regulatory Compliance Training for FSP License Applications
New FSPs seeking licensing must demonstrate adequate compliance infrastructure, including planned training programmes. The Financial Sector Conduct Authority evaluates whether applicants have robust systems for ensuring ongoing compliance.
FSP License Application Training Requirements
Competency frameworks submitted with license applications must specify required qualifications, continuous professional development, and role-specific training for all representatives. The framework should address:
- Minimum qualifications for each representative category
- Ongoing training hours required annually
- Training topics covering relevant regulatory obligations
- Assessment and competency verification procedures
- Training record maintenance and audit trails
Training programme documentation should include curricula, delivery methods, frequency, responsible parties, and measurement approaches for each regulatory obligation. Generic statements ("we will provide compliance training") are insufficient. Specific programmes addressing POPIA, FICA, FAIS, and COFI demonstrate preparedness.
Key individual competency receives particular scrutiny. License applications must demonstrate that key individuals possess comprehensive regulatory knowledge, compliance management expertise, and commitment to maintaining current competency through ongoing training.
Applicants benefit from developing comprehensive training programmes before license application, demonstrating operational readiness rather than aspirational intentions. This preparation accelerates approval and ensures smooth commencement once licensed.
Creating Compliance Training Documentation and Audit Trails
Regulatory supervisors and professional indemnity insurers increasingly require evidence that training occurred, covered required topics, and achieved competency. Systematic documentation protects the FSP and demonstrates compliance commitment.
Essential Training Documentation
Training attendance registers record who attended which sessions, when, and for how long. Digital sign-in systems, LMS completion tracking, or simple spreadsheets serve this purpose. Maintain registers for at least five years to cover typical audit and claim periods.
Training content records preserve what was covered in each session. Keep training presentations, course outlines, case studies, and materials. If training content is questioned years later during litigation or regulatory examination, contemporaneous records prove invaluable.
Competency assessments and results demonstrate that participants understood content and can apply it. Store quiz results, scenario assessment scores, practical evaluations, and any remedial training provided for staff who didn't initially demonstrate competency.
Training needs assessments justify training topic selection and resource allocation. Document how you identified training needs through file audits, incident reviews, regulatory changes, or staff competency gaps.
Training effectiveness evaluations show continuous improvement. Record post-training surveys, follow-up assessments, behavioral observations, and compliance metric changes attributable to training interventions.
Building a Compliance Training Culture
Technical training programmes fail without cultural foundation. Creating an environment where compliance is valued, questions are welcomed, and continuous improvement is expected transforms regulatory compliance training from obligation to competitive advantage.
Cultural Foundation Elements
Leadership commitment sets the tone. When key individuals and practice principals visibly prioritize compliance, participate in training, discuss compliance in team meetings, and allocate resources to compliance improvement, staff recognize its importance. Empty rhetoric about compliance importance contradicts actions undermines training effectiveness.
Psychological safety enables staff to raise compliance concerns, ask questions, and report potential issues without fear of blame or retaliation. Training environments should encourage questions, reward identification of compliance gaps, and treat mistakes as learning opportunities rather than punishable offenses.
Competency recognition values compliance expertise. Acknowledge staff who achieve strong compliance audit results, identify process improvements, or develop enhanced compliance skills. Public recognition, performance bonuses, or advancement opportunities linked to compliance competency reinforce its value.
Continuous improvement mindset positions compliance as an evolving discipline requiring ongoing development. Frame regulatory changes as opportunities for enhancement rather than burdens. Encourage staff to suggest compliance improvements and participate in refining procedures.
Client value connection helps staff understand compliance benefits beyond avoiding penalties. Training should emphasize how POPIA protection builds client trust, FICA processes protect clients from fraud, and FAIS conduct standards ensure appropriate advice. This purpose-driven approach motivates more effectively than fear-based compliance.
Regulatory compliance training in South Africa's financial services sector demands comprehensive, role-specific programmes addressing POPIA, FICA, FAIS, and emerging COFI obligations. Independent brokers must move beyond checkbox compliance toward strategic training investments that reduce risk, enhance client trust, and build sustainable competitive advantage through demonstrated professionalism.
Holistic Compliance Management Solutions (Pty) Ltd supports Financial Service Providers across South Africa with independent compliance services, regulatory exam preparation, FICA and POPI training, and comprehensive compliance monitoring. Whether you're an independent broker building your first structured training programme, an established practice preparing for COFI implementation, or an FSP applicant developing licensing documentation, our tailored services address the unique challenges of the South African regulatory environment.
Schedule FICA training with Holistic Compliance Management Solutions to strengthen your practice's anti-money laundering compliance:
- Comprehensive FICA verification procedures workshop
- RMCP drafting support and implementation guidance
- Ongoing regulatory updates and typology briefings
Ideal for: Independent insurance brokers, financial advisors, FSP compliance officers, and practices requiring FICA programme development or enhancement.