Regulatory and Compliance Training for FSPs in 2026
Regulatory and compliance training has become the cornerstone of sustainable financial services operations in South Africa. For independent financial brokers, advisors, and Financial Service Providers (FSPs), maintaining regulatory compliance isn't simply about avoiding penalties-it's about building client trust, protecting business continuity, and demonstrating professional competence. With evolving legislation including the Protection of Personal Information Act (POPIA), the Financial Intelligence Centre Act (FICA), the Financial Advisory and Intermediary Services Act (FAIS), and the Conduct of Financial Institutions (COFI) framework approaching implementation, structured training programmes have shifted from optional professional development to mandatory operational requirements. This comprehensive guide explores how South African FSPs can design, implement, and measure effective regulatory and compliance training that protects both clients and business interests.
Understanding South Africa's Regulatory Landscape for FSPs
The South African financial services sector operates under one of the continent's most sophisticated regulatory frameworks. Four primary legislative pillars govern FSP operations, each requiring specific knowledge, documented processes, and ongoing staff competency.
The Four Pillars of FSP Compliance
FAIS (Financial Advisory and Intermediary Services Act) establishes the foundational requirements for anyone providing financial advice or intermediary services. Representatives must demonstrate competence through passing the Regulatory Exam training, maintain fit-and-proper status, and operate within clearly defined mandates. The Act requires FSPs to ensure all representatives receive adequate training on products, regulations, and ethical conduct.
FICA (Financial Intelligence Centre Act) combats money laundering and terrorist financing by imposing strict client identification, verification, and reporting obligations. Financial institutions must establish Risk Management and Compliance Programmes (RMCPs) that document policies, procedures, training schedules, and monitoring systems. FICA compliance demands regular training updates as criminal methodologies evolve.
POPIA (Protection of Personal Information Act) regulates how FSPs collect, process, store, and share client information. Since full enforcement began in 2021, FSPs must train staff on eight core principles: accountability, processing limitation, purpose specification, further processing limitation, information quality, openness, security safeguards, and data subject participation. Non-compliance carries administrative penalties up to R10 million or criminal sanctions.
COFI (Conduct of Financial Institutions Bill) represents the most significant regulatory shift in decades, introducing a comprehensive conduct-of-business framework that will eventually replace FAIS. Although not yet enacted in 2026, FSPs must prepare for COFI's emphasis on customer fairness, product governance, and enhanced disclosure requirements. The UK Information Commissioner’s Office provides valuable guidance on similar conduct-focused regulatory frameworks that inform COFI's design.
Regulatory Examination Requirements
The Financial Sector Conduct Authority (FSCA) mandates that all representatives pass specific regulatory examinations demonstrating knowledge of legislation, products, and ethical conduct. These examinations test Class of Business knowledge and general regulatory understanding.
| Examination Component | Coverage Areas | Validity Period |
|---|---|---|
| Regulatory Examination (RE) | FAIS, FICA, POPIA, General Code of Conduct | 3 years (re-test required) |
| Class of Business Exams | Product-specific knowledge (Long-term, Short-term, Securities, etc.) | Ongoing (CPD requirements) |
| Immovable Property Examination | Property-specific regulations for property practitioners | 3 years |
| Key Individual Assessment | Enhanced compliance knowledge for compliance officers | Ongoing professional development |
Representatives joining the industry after 2026 must complete examinations within 12 months of appointment, whilst existing representatives require refresher testing every three years. This creates continuous demand for structured regulatory and compliance training programmes.
Designing Effective Regulatory and Compliance Training Programmes
Successful compliance training extends beyond exam preparation. According to research from OCEG on contemporary compliance training, organisations with mature programmes integrate regulatory education into daily workflows, measure behavioural change, and continuously adapt content to emerging risks.
Needs Assessment and Risk-Based Prioritisation
Before developing training content, FSPs must assess their specific risk profile, business model, and staff competency gaps.
Conduct a compliance gap analysis:
- Review previous audit findings and regulatory feedback
- Identify roles with elevated compliance exposure (client-facing, data processors, key individuals)
- Map existing knowledge against regulatory requirements
- Assess technology systems and their compliance support capabilities
- Document current training records and identify outdated certifications
Prioritise training based on risk exposure:
- High-risk, high-impact areas (client money handling, vulnerable client interactions, cross-border transactions)
- Recent regulatory changes (POPIA implementation updates, FICA amendment requirements)
- Historical non-compliance patterns within the organisation
- Industry-wide enforcement trends published by the FSCA
Independent brokers and smaller FSPs often face resource constraints. A risk-based approach ensures limited training budgets target areas with greatest compliance exposure and business impact.
Content Development for Different Audiences
One-size-fits-all training rarely achieves meaningful behavioural change. Effective regulatory and compliance training segments content by role, experience level, and operational context.
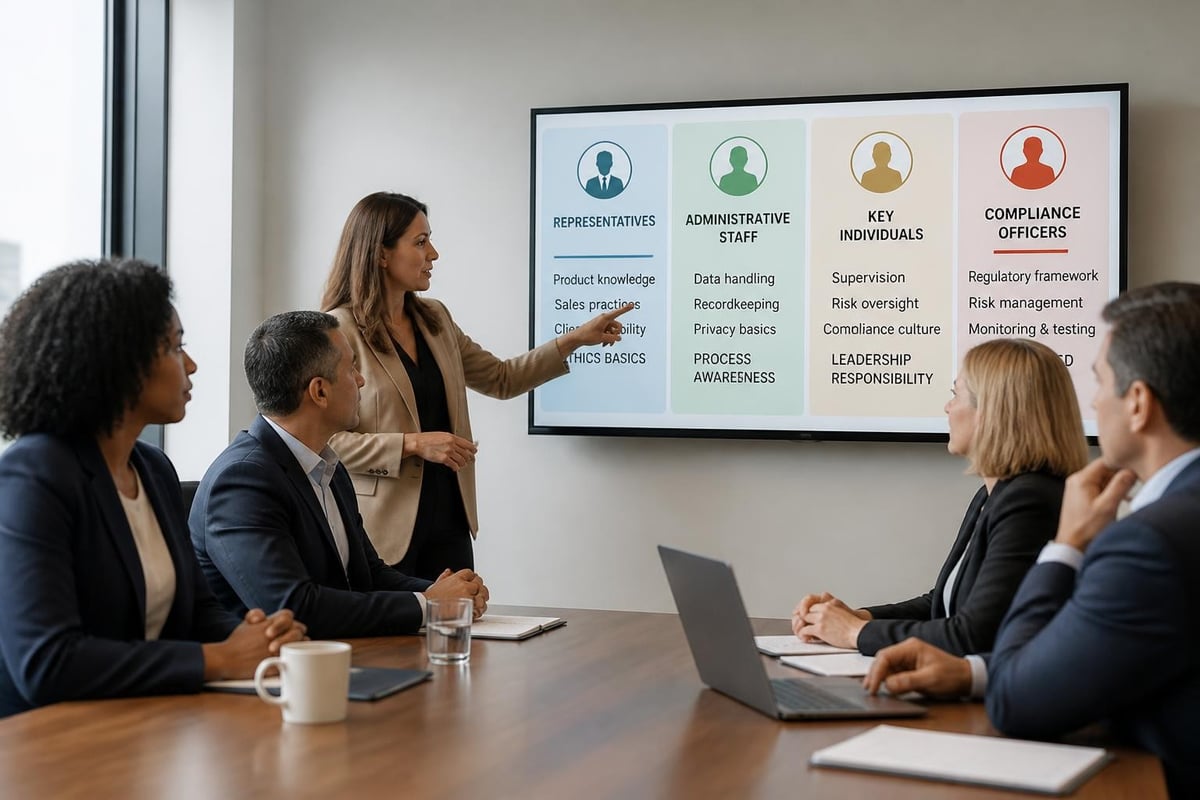
Role-based training modules:
| Role Category | Priority Training Areas | Delivery Format |
|---|---|---|
| Representatives | Product knowledge, needs analysis, disclosure requirements, conflict management | Interactive workshops, case studies, role-playing |
| Administrative Staff | Data protection, record-keeping, client communication protocols | Online modules, quick-reference guides |
| Key Individuals | Oversight responsibilities, RMCP implementation, regulatory reporting, internal controls | Facilitated seminars, regulatory updates |
| Compliance Officers | Monitoring techniques, risk assessment methodologies, regulatory interpretation, audit preparation | Professional development courses, regulator engagement |
Experience-level customisation ensures new representatives receive foundational regulatory knowledge whilst experienced advisors focus on complex scenarios, regulatory changes, and advanced ethical considerations. The U.S. Department of Justice framework for evaluating corporate compliance programmes emphasises that effective training demonstrates clear differentiation between audience segments.
Training Delivery Methods and Technology Integration
Modern regulatory and compliance training blends multiple delivery channels to accommodate different learning preferences, operational constraints, and content complexity.
Blended learning approaches:
- E-learning modules for foundational knowledge, regulatory updates, and standardised content (POPIA principles, FICA client verification steps)
- Instructor-led workshops for complex scenarios, ethical discussions, and interactive case studies
- Microlearning for just-in-time support (quick reminders before client meetings, disclosure requirement checklists)
- Simulation exercises for high-risk scenarios (suspected money laundering detection, data breach response)
- Peer learning forums where experienced representatives share practical compliance challenges and solutions
Technology platforms streamline training administration, tracking, and evidence collection. Learning Management Systems (LMS) automatically record completion certificates, schedule refresher training, and generate compliance reports for FSCA inspections.
However, technology should enhance-not replace-human interaction. Complex ethical dilemmas, nuanced regulatory interpretation, and cultural embedding of compliance values require facilitated discussion and leadership modelling.
Implementing POPIA Compliance Training
POPIA fundamentally changed how FSPs handle client information. Effective POPIA training transforms abstract principles into practical workflows that representatives apply daily.
The Eight POPIA Conditions Translated for Brokers
Accountability (Condition 1): FSPs must designate an Information Officer responsible for POPIA compliance. Training ensures all staff understand who holds this role, how to escalate data-protection queries, and their individual accountability for information handling.
Processing Limitation (Condition 2): Representatives must collect client information lawfully, with consent, and through fair methods. Practical training scenarios include:
- Obtaining explicit consent for collecting personal information during needs analysis
- Explaining information usage in clear, accessible language
- Avoiding deceptive collection methods or excessive data requests
Purpose Specification (Condition 3): Client data may only be used for the specific purpose disclosed during collection. Representatives require training on documenting collection purposes, restricting internal sharing, and obtaining fresh consent for new purposes.
Further Processing Limitation (Condition 4): Information collected for insurance applications cannot automatically be used for marketing unrelated products. Training must clarify permissible secondary uses and when re-consent is required.
Information Quality (Condition 5): Representatives must verify client information accuracy and update records regularly. Training includes practical steps for annual data reviews, correction procedures, and quality-control protocols.
Openness (Condition 6): Clients have the right to know what information is held, why it's processed, and who accesses it. Training covers responding to access requests within statutory timeframes and providing clear privacy notices.
Security Safeguards (Condition 7): Technical and organisational measures protect client data from loss, damage, unauthorised access, or disclosure. Representatives need training on:
- Password management and secure login procedures
- Email encryption for sensitive client communications
- Physical document security (locked filing, clean desk policies)
- Mobile device security when accessing client information remotely
- Incident reporting procedures when breaches occur
Data Subject Participation (Condition 8): Clients can request corrections, deletions, or objections to processing. Training equips staff to handle these requests appropriately and escalate complex cases to the Information Officer.
Practical POPIA Implementation Checklists
Checklists embedded within training materials help representatives apply POPIA principles consistently:
Client onboarding POPIA checklist:
- Provide clear privacy notice explaining information collection, usage, and storage
- Obtain documented consent (written or recorded) for personal information processing
- Verify identity documents are current and accurate
- Explain client rights to access, correct, and delete information
- Record consent basis and purpose in client management system
- Implement secure storage immediately upon collection
Marketing communications POPIA checklist:
- Verify marketing consent was obtained and documented
- Provide clear opt-out mechanism in every communication
- Process opt-out requests within 24 hours
- Distinguish existing client communications (legitimate interest) from prospect marketing (consent required)
- Document consent basis for compliance audits
FICA Training for Anti-Money Laundering Compliance
FICA imposes stringent obligations on FSPs to detect and prevent money laundering and terrorist financing. Effective regulatory and compliance training transforms these legal requirements into practical daily procedures.
Client Identification and Verification (CDD)
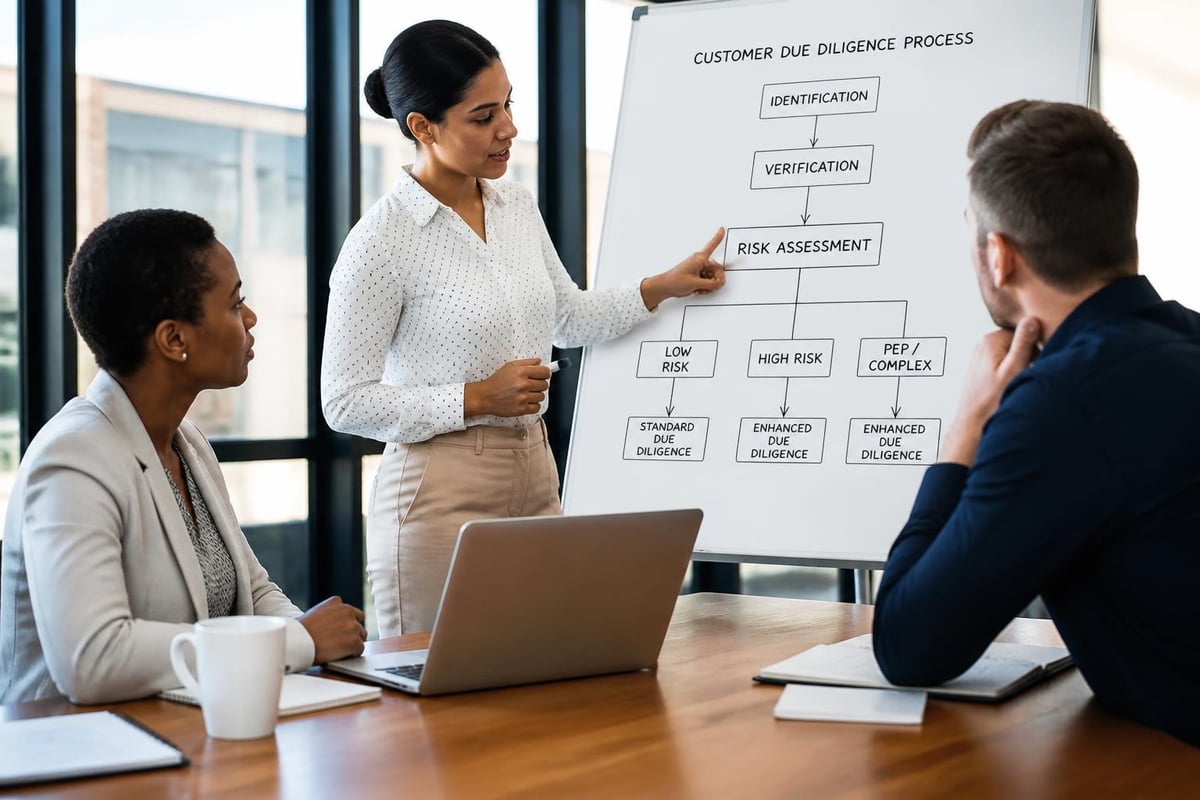
Customer Due Diligence forms the foundation of FICA compliance. Representatives must understand the difference between identification (establishing who the client claims to be) and verification (confirming that identity through reliable, independent sources).
Standard CDD training components:
- Acceptable identification documents (SA ID, passport, driver's licence)
- Verification methods (physical document inspection, certified copies, electronic verification systems)
- Timing requirements (verification before establishing business relationship)
- Record-keeping obligations (retention for five years after relationship ends)
- Corporate client complexities (beneficial ownership, authorised signatories, company registration verification)
Enhanced Due Diligence (EDD) triggers require additional scrutiny and training:
- High-value transactions exceeding prescribed thresholds
- Foreign nationals from high-risk jurisdictions
- Politically Exposed Persons (PEPs) and their relatives or close associates
- Complex corporate structures or trust arrangements
- Cash-intensive businesses or unusual transaction patterns
Representatives need scenario-based training to recognise EDD triggers and apply appropriate additional measures: source of wealth verification, ongoing monitoring frequency, senior management approval, and enhanced record-keeping.
Suspicious Transaction Reporting
FICA requires FSPs to report suspicious or unusual transactions to the Financial Intelligence Centre (FIC). This obligation creates tension-representatives must balance client relationships with regulatory duties, often without clear definitional guidance on "suspicion."
Training must develop representatives' professional scepticism and provide practical indicators:
Red flags for potential money laundering:
- Reluctance to provide identification or verification documents
- Provision of false, incomplete, or suspicious documentation
- Unusual transaction patterns inconsistent with stated occupation or income
- Requests for complex structuring below reporting thresholds
- Involvement of unrelated third parties in transactions
- Last-minute product changes or beneficiary substitutions
- Cash payments in substantial amounts when electronic transfers are available
- Nervousness or evasiveness when discussing transaction purposes
Training scenarios help representatives practise the internal reporting process without alerting clients (tipping-off prohibition). Role-playing exercises build confidence in escalating concerns to the Money Laundering Control Officer whilst maintaining professional client interactions.
Risk Management and Compliance Programme (RMCP) Requirements
FICA mandates that all accountable institutions establish, maintain, and implement an RMCP. For many independent brokers, the RMCP document represents their central compliance framework.
Regulatory and compliance training must ensure all staff understand:
- The RMCP's location and accessibility
- Their specific responsibilities documented within it
- Procedures for client onboarding, verification, and ongoing monitoring
- Record-keeping requirements and retention schedules
- Internal reporting lines for suspicious transactions
- Training schedules and refresher requirements
- Monitoring and testing procedures
Key individuals and compliance officers require advanced training on RMCP drafting, risk assessment methodologies, and regulatory expectations. Practical guidance on affordable, proportionate RMCP implementation helps smaller FSPs avoid over-engineered systems whilst maintaining regulatory adequacy.
FAIS Compliance and Ethical Conduct Training
The Financial Advisory and Intermediary Services Act establishes conduct standards that extend beyond technical product knowledge to ethical behaviour, conflicts management, and client-centric advice.
General Code of Conduct Requirements
The FAIS General Code of Conduct outlines specific obligations for FSPs and representatives. Effective training translates these legal requirements into daily decision-making frameworks.
Honesty and integrity (Code section 2): Representatives must act with honesty, fairness, and due care in client dealings. Training scenarios explore:
- Balancing commission structures with client best interests
- Disclosing product limitations alongside benefits
- Avoiding misleading claims or unrealistic performance projections
- Handling client complaints with transparency
Conflicts of interest (Code section 3): Representatives must identify, disclose, and manage conflicts that might influence advice. Training covers:
- Recognition of direct and indirect conflicts (ownership interests, financial incentives, personal relationships)
- Disclosure requirements and appropriate disclosure formats
- Management strategies when conflicts cannot be eliminated (independent review, client consent, referral alternatives)
- Documentation obligations for compliance evidence
Information about the FSP (Code section 4): Clients must receive clear information about the FSP's authorisation, complaints procedures, and professional indemnity cover. Training ensures representatives can explain:
- The difference between Category I (advice) and Category II (intermediary) licences
- Limitations on the FSP's mandate and authorised product categories
- The Ombudsman for Financial Services Providers' role and contact information
- Professional indemnity insurance coverage and limitations
Product supplier relationships (Code section 3A): Representatives must disclose relationships with product suppliers that might create conflicts. Training addresses:
- Ownership interests in insurers or investment firms
- Volume-based commission arrangements
- Incentive schemes, competitions, and non-financial benefits
- Preferential distribution agreements
Needs Analysis and Product Suitability
FAIS requires that advice must be appropriate to the client's risk profile, needs, and objectives. Representatives need training on structured needs-analysis methodologies.
Comprehensive needs analysis training includes:
- Fact-finding techniques (open questioning, active listening, documentation)
- Risk tolerance assessment (quantitative tools, behavioural indicators, scenario testing)
- Goal prioritisation (short-term versus long-term, essential versus aspirational)
- Affordability analysis (income verification, expenditure patterns, debt obligations)
- Existing cover review (policy audits, gap analysis, duplication identification)
- Matching product features to identified needs (suitability matrix development)
The OECD’s guidance on internal controls and compliance emphasises that effective training includes documented, standardised processes that demonstrate consistent application across all client interactions.
Training must also address unsuitable advice scenarios-when representatives should decline to recommend products, refer clients to specialists, or advise against transactions despite commission implications.
Disclosure Requirements and Documentation
FAIS imposes extensive disclosure obligations before, during, and after advice provision. Representatives frequently struggle with the volume and timing of required disclosures.
Training should provide practical disclosure checklists:
Pre-advice disclosures:
- FSP licence details and authorised categories
- Conflict of interest disclosures
- Commission and fee structures
- Product supplier relationships
- Professional indemnity cover details
Advice documentation:
- Client needs, objectives, and priorities
- Recommended product features and benefits
- Product limitations, exclusions, and risks
- Premium calculations and policy charges
- Alternative products considered and reasons for recommendations
- Projected performance (with appropriate disclaimers)
Post-advice requirements:
- Written records of advice within 30 days
- Policy documentation and waiting period notices
- Ongoing servicing commitments
- Review schedules and triggers
Technology solutions automate disclosure generation and evidence collection, but representatives require training on system operation, quality checking, and handling client questions about disclosed information.
Training Delivery, Measurement, and Continuous Improvement
Implementing regulatory and compliance training programmes requires structured project management, clear accountability, and ongoing evaluation.
Creating Training Schedules and Completion Tracking
FSPs must document training schedules, monitor completion, and maintain evidence for regulatory inspections.
Annual training calendar template:
| Training Module | Target Audience | Frequency | Delivery Method | Responsible Person | Completion Deadline |
|---|---|---|---|---|---|
| POPIA Foundations | All staff | Annual | E-learning | Compliance Officer | 31 March 2026 |
| FICA Client Verification | Representatives | Annual | Workshop | Key Individual | 30 April 2026 |
| Product Knowledge (Long-term) | Long-term representatives | Quarterly | Webinar | Product Supplier | Quarterly end |
| Conflicts of Interest | Representatives | Annual | Case studies | Compliance Officer | 31 May 2026 |
| Data Breach Response | All staff | Annual | Simulation | IT & Compliance | 30 June 2026 |
Compliance officers should maintain individual training records documenting:
- Training attended (topic, date, duration, facilitator)
- Assessment results (examination scores, competency demonstrations)
- Certificates issued and expiry dates
- Refresher training due dates
- CPD points allocated (where applicable)
Measuring Training Effectiveness Beyond Completion Rates
Completion statistics indicate participation but not learning outcomes or behavioural change. SAI360’s research on compliance training measurement identifies five levels of training evaluation:
Level 1: Reaction – Did participants find training relevant, engaging, and professionally delivered? (Post-training surveys)
Level 2: Learning – Did participants acquire intended knowledge and skills? (Assessments, examinations, scenario-based testing)
Level 3: Behaviour – Do participants apply training in daily work? (File reviews, observation, mystery shopping, compliance monitoring)
Level 4: Results – Has training reduced compliance incidents, improved audit outcomes, or enhanced client satisfaction? (Incident tracking, complaints analysis, regulatory feedback)
Level 5: Return on Investment – Do compliance improvements justify training costs? (Cost-benefit analysis, penalty avoidance, efficiency gains)
Most FSPs measure levels 1 and 2 effectively but struggle with behavioural observation and results measurement. Practical approaches include:
- File reviews: Compliance officers sample client files quarterly, checking for proper needs analysis, disclosure documentation, and FICA verification
- Spot-checks: Unannounced reviews of client communications, marketing materials, or data-handling practices
- Incident tracking: Monitoring complaints, near-misses, and control failures to identify training gaps
- Representative self-assessment: Structured reflection on confidence levels, practical challenges, and support needs
Continuous Improvement and Regulatory Responsiveness
South Africa's regulatory environment evolves continuously. FSCA guidance notices, industry conduct standards, and enforcement trends require rapid training updates.
Establish regulatory monitoring processes:
- Subscribe to FSCA communications and regulatory update services
- Monitor industry associations (Financial Intermediaries Association, Insurance Institute of South Africa)
- Review enforcement actions and published sanctions for emerging compliance risks
- Attend regulatory roadshows, industry conferences, and professional development events
Implement agile training updates:
- Develop rapid-response training modules for urgent regulatory changes (48-hour turnaround)
- Use microlearning formats for quick updates (email bulletins, short videos, infographics)
- Schedule quarterly regulatory update sessions for representatives
- Maintain version-controlled training materials with clear effective dates
The SCCE conference materials on compliance training best practices highlight that leading organisations integrate continuous improvement cycles: plan training based on risk assessment, deliver through appropriate channels, measure effectiveness through multiple metrics, and refine content based on results.
Technology Solutions for Compliance Training Management
Technology platforms streamline training administration, reduce manual tracking, and provide defensible compliance evidence.
Learning Management Systems for FSPs
Specialised LMS platforms designed for financial services compliance offer:
Core functionality:
- Centralised training library with version control
- Automated training assignment based on role, licence category, or hire date
- Completion tracking and certificate generation
- Automated reminders for upcoming or overdue training
- Reporting dashboards for compliance oversight
- Integration with FSCA representative databases
- Mobile accessibility for remote or field-based representatives
Advanced features:
- Scenario-based learning with branching logic
- Gamification elements (leaderboards, badges, completion milestones)
- Social learning forums for peer discussion
- Content authoring tools for custom module development
- External training integration (professional body courses, product supplier sessions)
- CPD point allocation and tracking
When selecting technology solutions, independent brokers should prioritise:
- Affordability: Subscription models scaled to practice size
- Ease of use: Minimal technical skills required for administration
- Regulatory alignment: Content specifically addressing South African legislation
- Evidence quality: Comprehensive audit trails for FSCA inspections
- Scalability: Capacity to grow with practice expansion
Digital Tools for Practical Compliance Support
Beyond formal training platforms, digital tools support daily compliance application:
Compliance checklists and workflows:
- Client onboarding checklists integrated into CRM systems
- FICA verification workflows with automated prompts
- Disclosure document generators with current regulatory templates
- Conflicts-of-interest registers with real-time updating
- Complaint handling workflows with statutory deadline tracking
Knowledge repositories:
- Searchable regulatory libraries (Acts, regulations, guidance notices)
- Internal policy and procedure manuals
- Product knowledge databases with technical specifications
- Template libraries (client communications, disclosure documents, reporting forms)
- FAQ databases addressing common compliance queries
Monitoring and testing tools:
- Automated file review tools checking for compliance indicators
- Email monitoring for marketing compliance (POPIA consent verification)
- Transaction monitoring for FICA suspicious pattern detection
- Data-protection impact assessment templates
- Internal audit checklists aligned to regulatory requirements
Technology should complement-not replace-professional judgment. Representatives require training not only on system operation but on critically evaluating automated outputs and escalating complex scenarios appropriately.
Building a Compliance Culture Beyond Tick-Box Training
The ultimate goal of regulatory and compliance training extends beyond certification evidence. Mature organisations embed compliance into organisational culture, leadership behaviour, and daily decision-making.
Leadership's Role in Compliance Culture
Key individuals and principal officers model compliance commitment through:
Visible participation: Leaders attend training sessions alongside representatives, demonstrating that compliance applies universally
Resource allocation: Adequate budgets for quality training, technology, and specialist expertise
Accountability enforcement: Consistent consequences for non-compliance, regardless of seniority or production levels
Communication priorities: Regular messaging emphasising compliance as business enablement, not administrative burden
Recognition systems: Celebrating compliance excellence alongside sales achievements
When leadership treats compliance as peripheral or burdensome, training becomes performative box-ticking. When leadership integrates compliance into strategic discussions, resource decisions, and performance management, training becomes valued professional development.
Embedding Compliance in Daily Operations
Regulatory and compliance training achieves lasting impact when connected to daily workflows:
Integration strategies:
- Process design: Build compliance controls into standard operating procedures (templates, system prompts, approval workflows)
- Performance metrics: Include compliance indicators in representative scorecards (file quality scores, disclosure completeness, training currency)
- Team meetings: Allocate standing agenda time for compliance discussions, regulatory updates, and case studies
- Mentoring programmes: Pair experienced representatives with new hires for practical compliance coaching
- Open communication: Encourage questions, near-miss reporting, and improvement suggestions without fear of punishment
Creating psychological safety for compliance discussions:
Representatives must feel comfortable raising compliance uncertainties, reporting potential breaches, and challenging questionable practices. Training should explicitly emphasise:
- Questions indicate professionalism, not incompetence
- Early escalation prevents serious violations
- The organisation values honesty over concealment
- Support mechanisms exist for compliance dilemmas (compliance officer access, ethics hotlines, confidential reporting)
Measuring Cultural Indicators
Compliance culture measurement extends beyond training completion rates:
Behavioural indicators:
- Frequency of proactive compliance questions to the compliance officer
- Representative participation rates in optional compliance development
- Time elapsed between potential breach identification and reporting
- Quality of self-identified compliance improvements
- Feedback quality in training evaluations (specific, constructive, engaged versus perfunctory)
Outcome indicators:
- Complaints per representative trending downward
- Regulatory inspection findings decreasing in severity and frequency
- Internal audit results improving across review cycles
- Client satisfaction scores for transparency and communication
- Representative retention rates (stable compliance culture reduces turnover)
Organisations with strong compliance cultures view regulatory and compliance training as continuous professional development that enhances client service, protects business sustainability, and demonstrates market leadership.
Practical Implementation Guidance for Independent Brokers
Independent brokers and smaller FSPs face unique challenges implementing comprehensive regulatory and compliance training: limited budgets, administrative capacity constraints, and competing operational priorities.
Cost-Effective Training Solutions
Free and low-cost resources:
- FSCA guidance notices and circulars (foundational regulatory knowledge)
- Industry association webinars and member resources
- Product supplier training (product knowledge, market updates)
- Professional body CPD sessions (South African Insurance Institute, Financial Planning Institute)
- Peer learning groups within non-competing brokers
Affordable professional training:
- Online regulatory examination preparation courses
- Annual compliance workshops from specialist providers
- Shared training costs through buying groups or networks
- Recorded webinars for flexible, repeated access
- Microlearning subscriptions targeting specific topics
Internal content development:
- Document internal procedures as training materials
- Create case studies from actual compliance scenarios (anonymised)
- Develop template checklists and quick-reference guides
- Record informal training sessions for new hire onboarding
- Leverage experienced representatives as subject-matter experts
Creating Manageable Training Schedules
Small practices cannot afford to remove representatives from client-facing activities for extended training periods. Practical scheduling approaches include:
Distributed learning model:
- Monthly 90-minute training sessions (alternating topics)
- Weekly 15-minute microlearning (regulatory updates, case discussions)
- Quarterly half-day workshops (intensive skill development)
- Annual compliance day (comprehensive review, planning, team building)
Flexible delivery options:
- Early-morning sessions before client appointments
- Lunch-and-learn formats
- Evening sessions with catering
- Online modules for self-paced completion
- Weekend intensive options for major updates
Integration with operational meetings:
- Allocate first 15 minutes of weekly team meetings to compliance topics
- Rotate responsibility for presenting regulatory updates
- Discuss real client scenarios as compliance learning opportunities
- Review recent complaints or near-misses for lessons learned
Documentation for Regulatory Inspections
FSCA inspections require comprehensive training evidence. Independent brokers should maintain:
Training file contents:
- Annual training plan with scheduled dates and topics
- Training attendance registers with signatures
- Training materials (presentations, handouts, case studies)
- Assessment results (examination scores, competency demonstrations)
- Individual representative training records
- Certificates and CPD documentation
- Evidence of regulatory examination currency
- Training evaluation feedback and improvement actions
Proportionate documentation:
Small practices need not maintain elaborate systems. A simple spreadsheet tracking training dates, topics, attendees, and assessment results, combined with a folder containing training materials and certificates, satisfies basic regulatory expectations.
The key principle: demonstrate systematic approach, not bureaucratic complexity. Inspectors seek evidence that training occurs regularly, covers mandatory topics, reaches all relevant staff, and includes some form of knowledge verification.
Regulatory and compliance training represents a fundamental investment in FSP sustainability, client protection, and professional development. South African financial services providers navigating POPIA, FICA, FAIS, and approaching COFI requirements need structured, practical training that translates complex legislation into daily workflows.
Book a FICA training consultation with Holistic Compliance Management Solutions (Pty) Ltd:
For: Independent brokers, regulated financial advisors, FSP compliance officers, and practices seeking practical compliance implementation
Your FICA training consultation includes:
- Comprehensive assessment of current FICA compliance gaps and RMCP adequacy
- Customised training plan addressing client verification, suspicious transaction detection, and record-keeping obligations
- Practical tools including verification checklists, red-flag indicators, and documentation templates
Holistic Compliance Management Solutions (Pty) Ltd delivers independent compliance and training services specifically designed for South African FSPs. Since 2018, we've helped Cape Town financial services providers build sustainable compliance frameworks that protect both clients and business interests. Schedule your FICA training today.