GRC ServiceNow for Financial Services Compliance in SA
Financial services providers in South Africa face an increasingly complex regulatory environment. Between POPIA data protection requirements, FICA anti-money laundering obligations, FAIS conduct standards, and COFI customer treatment principles, independent brokers and advisors must maintain continuous compliance across multiple frameworks. Manual spreadsheets and disconnected systems create gaps, delays, and audit risks. This is where grc service now becomes valuable. ServiceNow's Integrated Risk Management (IRM) platform offers South African FSPs a unified approach to governance, risk, and compliance, automating workflows, centralizing evidence, and providing real-time visibility into regulatory obligations. For compliance officers managing broker practices, understanding how grc service now can transform compliance operations is essential to building sustainable, auditable frameworks that protect both clients and the business.
Understanding GRC ServiceNow for Financial Services
ServiceNow's Governance, Risk, and Compliance (GRC) module sits within the broader Integrated Risk Management suite. The platform transforms how organizations manage regulatory requirements, enterprise risks, and internal controls.
GRC service now provides financial services providers with a central system of record for compliance activities. Rather than managing POPIA consent registers in one spreadsheet, FICA customer due diligence in another, and FAIS training records separately, the platform consolidates these workflows into connected modules.
The architecture includes several key components:
- Policy and compliance management for publishing, acknowledging, and tracking regulatory policies
- Risk management to identify, assess, and monitor compliance risks across the practice
- Audit management for planning, executing, and remediating internal and external audits
- Vendor risk management for third-party due diligence and ongoing monitoring
- Entity and business unit management for multi-office or branch compliance oversight
Core GRC ServiceNow Capabilities
| Capability | Description | Financial Services Application |
|---|---|---|
| Control framework mapping | Map regulations to internal controls and evidence | Link POPIA principles to data processing controls, FICA obligations to KYC procedures |
| Risk register | Centralized risk identification and assessment | Track non-compliance risks, data breach scenarios, AML red flags |
| Compliance obligations library | Database of regulatory requirements | Maintain current FAIS, FICA, POPIA, COFI obligations with change tracking |
| Automated workflows | Task assignment and escalation | Route client onboarding approvals, trigger FICA reviews, schedule training |
| Reporting and dashboards | Real-time compliance status visibility | Show POPIA consent rates, outstanding FICA verifications, training completion |
The platform integrates with ServiceNow's broader IT Service Management (ITSM) capabilities, connecting compliance to IT security, change management, and incident response. This integration proves particularly valuable for POPIA compliance, where data breach response must coordinate between compliance, IT security, and legal teams.
According to the ServiceNow GRC reference documentation, the platform supports multiple compliance frameworks simultaneously, making it well-suited for South African FSPs juggling overlapping regulations.
Implementing GRC ServiceNow for POPIA Compliance
The Protection of Personal Information Act (POPIA) requires financial services providers to implement comprehensive data protection controls. GRC service now offers specific capabilities that align with POPIA's eight conditions for lawful processing.
Mapping POPIA Requirements to ServiceNow Controls
Start by building a POPIA compliance framework within the platform. Create a policy library containing your privacy policy, processing notices, data subject rights procedures, and breach notification protocols. Each policy should link to specific controls that demonstrate compliance.
Key POPIA controls to configure:
- Consent management workflows – Automate collection, recording, and withdrawal of client consent for data processing
- Data subject rights fulfillment – Create request forms and tracking for access, correction, deletion, and objection requests
- Processing activity register – Maintain POPIA-required records of processing activities with data categories, purposes, retention periods
- Third-party processor assessments – Implement vendor risk workflows for outsourced data processing
- Data breach incident response – Configure incident workflows that trigger Information Regulator notification timelines
The platform's risk management module allows you to assess POPIA compliance risks across different data processing activities. For example, you might identify high-risk scenarios such as:
- Cross-border data transfers to offshore insurance underwriters
- Historical client data lacking documented consent
- Inadequate security controls on mobile devices accessing client information
Each risk can be assigned to an owner, given a treatment plan, and tracked through remediation. The system generates audit trails showing when risks were identified, assessed, and mitigated.
POPIA Automation Opportunities
| Manual Process | GRC ServiceNow Automation | Compliance Benefit |
|---|---|---|
| Spreadsheet of consents | Consent workflow with client portal integration | Auditable timestamps, version control, withdrawal tracking |
| Email-based DSR requests | Data subject request ticketing and SLA monitoring | Meet 30-day POPIA response requirements consistently |
| Annual policy review reminders | Policy review workflows with approval chains | Ensure annual POPIA policy updates with evidence |
| Manual breach assessment | Incident severity scoring and automatic escalation | Trigger Information Regulator notification within 72 hours |
The platform's reporting capabilities prove invaluable during FSCA inspections. Compliance officers can generate real-time reports showing consent coverage rates, outstanding data subject requests, completed privacy training, and remediated data security findings.
Leveraging GRC ServiceNow for FICA and AML Compliance
The Financial Intelligence Centre Act (FICA) imposes customer due diligence, record-keeping, and suspicious transaction reporting obligations on financial services providers. GRC service now can orchestrate the complex workflows required for FICA compliance.
Building a FICA Compliance Framework
Configure the platform to manage your Risk Management and Compliance Programme (RMCP) as a living document. The RMCP should exist as a controlled policy within ServiceNow, with sections mapped to specific controls and evidence.
For customer onboarding, create workflows that enforce FICA's verification requirements:
- Identity verification – Task assignments for collecting and verifying ID documents
- Residential address verification – Approval gates requiring proof of address within specified timeframes
- Source of funds verification – Enhanced due diligence triggers for high-risk clients
- Beneficial ownership identification – Workflows for corporate clients requiring ownership structure documentation
Each verification step creates audit evidence automatically. When a broker completes identity verification, the platform timestamps the action, records the documents reviewed, and links the evidence to the client record.
For ongoing monitoring, configure risk-based review cycles. Higher-risk clients (foreign nationals, politically exposed persons, cash-intensive businesses) can trigger more frequent reviews, while lower-risk retail clients follow standard intervals.
Suspicious Transaction Monitoring Integration
While grc service now doesn't replace dedicated transaction monitoring systems, it can orchestrate the compliance response when suspicious activity is detected. Create incident workflows for suspicious transactions that:
- Assign investigation tasks to compliance officers
- Provide standardized templates for documenting investigation findings
- Track decision-making (file STR, escalate for review, document legitimate explanation)
- Maintain audit trails of all investigative steps
- Generate FIC Centre reporting submissions with supporting evidence
The ServiceNow risk management documentation outlines how to configure risk indicators and monitoring protocols that align with these AML workflows.
For businesses offering compliance monitoring services to other FSPs, the multi-entity capabilities allow you to manage FICA compliance across multiple client practices from a single platform, with segregated data and reporting per FSP.
FAIS and COFI Compliance Management
The Financial Advisory and Intermediary Services Act (FAIS) and Conduct of Financial Institutions (COFI) Bill establish conduct standards, competency requirements, and customer treatment principles for brokers and advisors.
Competency and Training Management
GRC service now includes learning management capabilities that can track regulatory training requirements. Configure the platform to monitor:
- Initial Regulatory Examination (RE) status for all representatives
- Continuous Professional Development (CPD) hour accumulation
- Product-specific training requirements
- FAIS fit and proper criteria maintenance
Create workflows that automatically assign training based on role, product category, or regulatory changes. For example, when COFI becomes law, the system can automatically enroll all client-facing staff in COFI principles training and track completion.
Training compliance tracking:
| Requirement | ServiceNow Configuration | Compliance Output |
|---|---|---|
| RE exam status | Link representatives to qualification records | Real-time view of unqualified representatives |
| Annual CPD hours | Track training completion against 30-hour target | Exception reports for non-compliant reps |
| Product training | Map products to required certifications | Prevent product sales without proper training |
| Fit and proper criteria | Annual declaration workflows | Auditable compliance with FAIS General Code |
Complaints Management and Customer Treatment
COFI emphasizes customer treatment outcomes. The platform's case management capabilities can centralize complaint handling, ensuring consistent processes and regulatory reporting.
Configure complaint workflows that:
- Capture all client complaints through multiple channels (email, phone, web form)
- Categorize complaints by type, severity, and root cause
- Assign investigation and resolution tasks with SLA monitoring
- Track remediation actions and customer communications
- Generate regulatory reports for FSCA submission
The system can identify complaint trends that indicate broader compliance issues. For example, if multiple complaints relate to unclear policy wording, the platform can trigger a policy review workflow and link the issue to your FAIS compliance risk register.
According to ISACA’s guidance on managing cyber risk with GRC tools, connecting operational incidents like complaints to risk management processes provides valuable insight for continuous improvement.
Building a Unified Compliance Framework
South African financial services providers must comply with multiple overlapping regulations. GRC service now enables a unified approach that reduces duplication and identifies synergies.
Cross-Framework Control Mapping
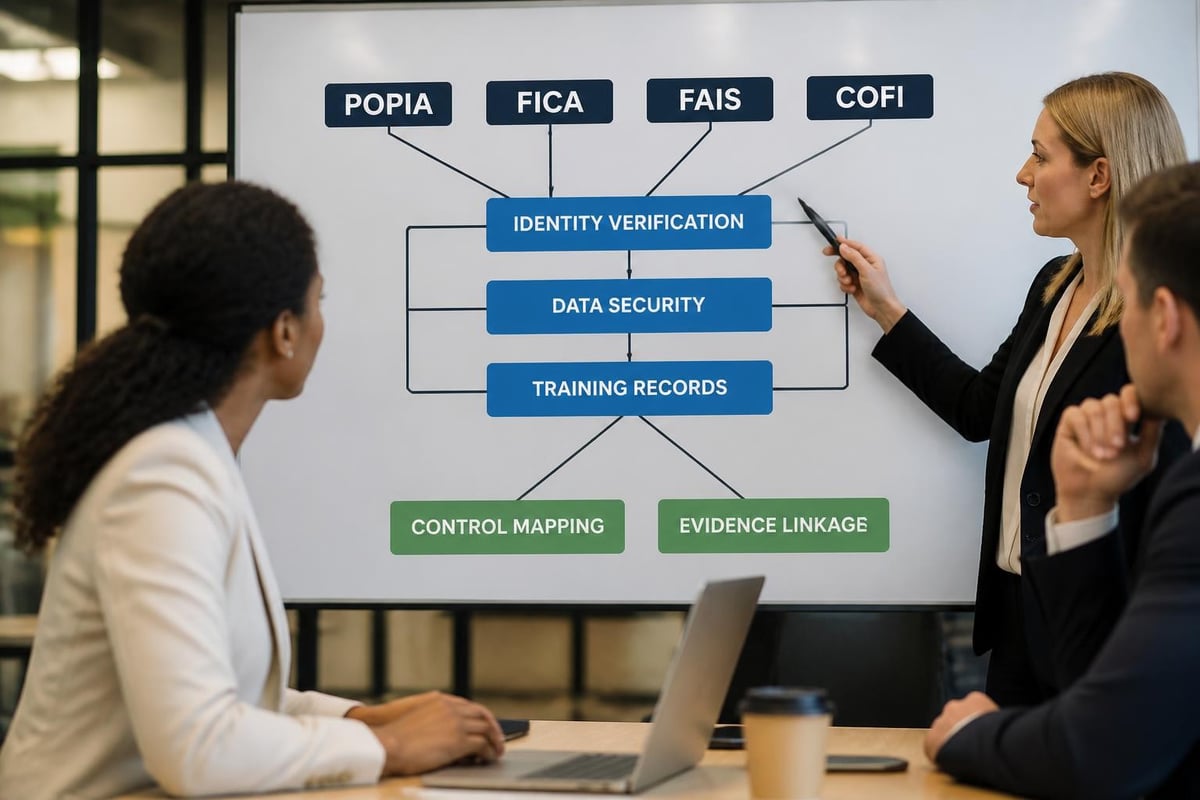
Many compliance requirements appear across multiple regulations. For example, client identity verification serves both FICA (customer due diligence) and POPIA (data accuracy) purposes. Training records demonstrate both FAIS competency and POPIA awareness.
The platform allows you to map a single control to multiple regulatory obligations. This approach:
- Reduces compliance costs – One control implementation satisfies multiple requirements
- Improves efficiency – Compliance evidence collected once serves multiple frameworks
- Provides better risk insight – Control failures impact multiple compliance areas simultaneously
Create a control library that includes:
- Client identity verification procedures
- Data security and access controls
- Training and competency management
- Third-party due diligence processes
- Incident response and breach notification
- Record retention and destruction
- Customer communication and disclosure
Each control should map to the specific POPIA, FICA, FAIS, and COFI requirements it satisfies. The platform can then generate compliance attestation reports showing coverage across all frameworks.
Implementing Common Compliance Frameworks
The Unified Compliance Framework provides pre-built control mappings for common regulations. While UCF's library focuses primarily on international standards, the methodology applies to South African regulations.
Consider mapping your POPIA, FICA, FAIS, and COFI obligations to control families based on the NIST Cybersecurity Framework. This approach creates a standardized control structure that can accommodate future regulations without rebuilding your entire compliance program.
Sample control family mapping:
- Identify – Data inventories (POPIA), customer risk assessments (FICA), product knowledge requirements (FAIS)
- Protect – Access controls (POPIA), verification procedures (FICA), competency requirements (FAIS)
- Detect – Transaction monitoring (FICA), data breach detection (POPIA), complaints monitoring (COFI)
- Respond – Data subject rights (POPIA), suspicious transaction reporting (FICA), complaint resolution (COFI)
- Recover – Breach remediation (POPIA), control restoration (FICA), customer remediation (COFI)
Risk-Based Compliance Monitoring
Effective compliance programs prioritize resources based on risk. GRC service now enables risk-based monitoring that focuses attention on high-risk areas while maintaining baseline controls across the practice.
Configuring Risk-Based Monitoring Workflows
Implement a risk assessment methodology that scores compliance risks based on:
- Likelihood – How probable is the non-compliance or control failure?
- Impact – What are the consequences (regulatory penalties, reputational damage, client harm)?
- Control effectiveness – How well are current controls mitigating the risk?
For example, a small broker practice might assess:
High risk – Inadequate FICA verification for high-net-worth foreign nationals (high likelihood of scrutiny, severe penalties, weak historical controls)
Medium risk – Incomplete POPIA consent for historical clients (moderate likelihood of complaint, moderate penalties, partial controls in place)
Low risk – Minor CPD hour shortfalls for administrative staff (low likelihood of detection, minimal penalties, generally strong compliance)
The platform can automate monitoring frequency based on risk scores. High-risk areas trigger monthly reviews, medium-risk quarterly, and low-risk annually.
Continuous Monitoring and Automation
Configure automated compliance checks that run continuously without manual intervention:
- POPIA consent coverage – Daily calculation of clients with valid consent vs. those requiring re-consent
- FICA verification expiry – Weekly reports of clients with outdated verification documents
- Training compliance – Monthly CPD hour tracking against annual targets
- Complaint resolution SLAs – Real-time monitoring of open complaints approaching deadlines
When monitoring identifies issues, the platform can trigger remediation workflows automatically. For example, if a representative's CPD hours fall below target, the system assigns training and notifies the compliance officer.
The NIST Risk Management Framework guidance provides a structured approach to continuous monitoring that translates effectively to financial services compliance.
Audit Management and Regulatory Inspections
FSCA inspections and internal audits test the robustness of compliance frameworks. GRC service now provides audit management capabilities that streamline preparation, execution, and remediation.
Preparing for FSCA Inspections
When the FSCA announces an inspection, the platform becomes your central repository for evidence gathering. Create an audit project that links to all relevant controls, policies, and evidence.
Pre-inspection preparation workflow:
- Scope definition – Identify which compliance areas the inspection will cover
- Evidence collection – Gather all supporting documentation from linked controls
- Gap analysis – Run compliance reports to identify any outstanding items
- Remediation – Prioritize and complete any gaps before the inspection
- Response coordination – Assign roles for who will respond to specific queries
During the inspection, use the platform to track requests and responses. Each FSCA query becomes a task with assigned owners, due dates, and response documentation. This ensures nothing falls through gaps and creates a complete record of the inspection process.
Internal Audit Programs
Implement regular internal audit cycles that test compliance controls before external scrutiny. Configure audit programs for:
- Annual POPIA compliance audit – Test all eight conditions, review processing registers, verify consent management
- Quarterly FICA sampling – Select random client files to verify verification completeness
- Bi-annual FAIS audit – Review representative qualifications, product training, complaint handling
- Monthly transaction monitoring review – Assess suspicious transaction identification and investigation
Each audit generates findings that feed into the risk register. High-severity findings trigger immediate remediation workflows with executive visibility, while lower-priority items follow standard remediation timelines.
The platform tracks remediation progress, ensuring findings don't languish unresolved. Compliance officers can generate executive reports showing open findings by age, severity, and owner.
Integration with Financial Services Systems
GRC service now delivers maximum value when integrated with existing practice management and financial systems. API connections enable automated data flows that reduce manual entry and improve accuracy.
Common Integration Points
| Source System | Data Exchange | Compliance Benefit |
|---|---|---|
| Practice management | Client demographics, policy information | Auto-populate FICA verification workflows, identify consent gaps |
| Document management | Policy documents, client files | Link evidence to compliance controls, centralize audit retrieval |
| Email and communication | Client correspondence | Capture consent communications, complaint documentation |
| Learning management | Training completion, CPD hours | Automate FAIS competency tracking, trigger training assignments |
| Financial systems | Transaction data | Support FICA monitoring, identify unusual patterns |
For businesses without sophisticated integration capabilities, the platform supports manual data uploads and basic connectors. Even without full automation, centralizing compliance evidence in one system provides significant benefits over dispersed spreadsheets and file shares.
Data Privacy Considerations
When integrating systems that contain personal client information, ensure data flows comply with POPIA's purpose limitation and data minimization principles. Only transfer the minimum data necessary for compliance purposes, and configure appropriate access controls within ServiceNow.
Document all data flows in your POPIA processing activity register, including:
- What personal information flows into the GRC platform
- The legal basis for processing (regulatory compliance)
- Who has access to the data
- Retention periods and deletion procedures
- Security measures protecting the data
Vendor Selection and Implementation Considerations
Implementing grc service now requires significant investment in licensing, configuration, and ongoing maintenance. South African FSPs should carefully evaluate whether the platform suits their specific needs.
When GRC ServiceNow Makes Sense
The platform typically delivers the best return on investment for:
- Medium to large FSPs with multiple branches, product lines, or complex structures
- FSPs with dedicated compliance teams who can manage ongoing configuration and workflows
- Organizations already using ServiceNow ITSM where GRC integration provides additional value
- Businesses subject to multiple regulations beyond POPIA, FICA, FAIS (e.g., international operations)
Smaller independent brokers or single-advisor practices may find the platform's capabilities exceed their needs. Simpler compliance management tools or manual processes with good documentation may suffice.
Implementation Best Practices
If you proceed with implementation, follow these guidelines:
Start with a pilot framework – Configure one compliance area (e.g., POPIA or FICA) fully before expanding to others. This builds expertise and demonstrates value.
Involve end users early – Representatives, client service staff, and compliance officers who will use the system daily should participate in configuration decisions.
Prioritize automation wins – Identify manual processes that consume the most time (consent management, training tracking, audit evidence gathering) and automate those first.
Maintain simplicity – The platform's extensive capabilities can lead to over-configuration. Build workflows that solve real problems, not theoretical ones.
Plan for ongoing maintenance – Regulations change. Assign responsibility for keeping policy libraries, control frameworks, and workflows current.
The SANS Institute’s guidance on GRC implementation emphasizes that technology alone doesn't create compliance. The platform enables processes, but organizations must still establish clear policies, assign responsibilities, and maintain compliance culture.
Measuring Compliance Program Effectiveness
GRC service now provides extensive reporting capabilities that help compliance officers demonstrate program value to executives and regulators.
Key Performance Indicators
Configure dashboards that track:
Compliance coverage metrics:
- Percentage of clients with current POPIA consent
- Percentage of clients with valid FICA verification
- Representative training compliance rates
- Control implementation status across frameworks
Operational efficiency metrics:
- Average time to resolve data subject requests
- Customer verification workflow completion times
- Training assignment to completion cycles
- Audit finding remediation timelines
Risk metrics:
- Number of high-risk compliance issues open
- Risk score trends over time
- Control effectiveness ratings
- Incident and breach frequency
These metrics provide early warning when compliance is deteriorating and evidence of improvement when initiatives succeed.
Regulatory Reporting
Configure scheduled reports that support regulatory submissions:
- FSCA annual compliance reports with supporting evidence
- POPIA Information Regulator notifications and breach reports
- FICA suspicious transaction report supporting documentation
- COFI customer treatment outcome reporting (once implemented)
The platform's audit trail capabilities ensure all reports can be substantiated with underlying evidence, strengthening regulatory credibility.
Change Management and Regulatory Updates
South African financial services regulations evolve constantly. COFI implementation, POPIA guidance updates, FICA amendments, and FAIS conduct standard changes all require compliance framework adjustments.
Managing Regulatory Change
When regulations change, grc service now provides a structured approach to impact assessment and implementation:
- Change notification – Create a regulatory change project when new requirements are announced
- Gap analysis – Compare new obligations against existing controls to identify gaps
- Impact assessment – Determine which policies, procedures, and controls require updates
- Implementation planning – Assign remediation tasks with dependencies and timelines
- Validation – Test new controls and verify compliance with updated requirements
- Communication – Notify affected staff and update training materials
The platform maintains version control for policies and controls, creating an audit trail that shows when changes were implemented and what triggered them.
Staying Current with ServiceNow Updates
ServiceNow releases platform updates regularly, adding features and improving functionality. Assign responsibility for reviewing release notes, identifying relevant enhancements, and planning upgrades.
For example, recent ServiceNow updates have added AI-powered risk assessment suggestions and natural language processing for policy analysis. These capabilities can enhance your compliance program as they mature.
According to Forrester’s analysis of ServiceNow’s platform strategy, the vendor's investment in workflow automation and AI capabilities positions the platform well for future compliance needs.
Building Internal Expertise
Successful grc service now implementation requires internal champions who understand both compliance requirements and platform capabilities.
Invest in training for:
Compliance officers – How to configure policies, controls, risk assessments, and audit programs specific to POPIA, FICA, FAIS, and COFI requirements.
System administrators – Technical configuration, workflow automation, integration setup, and report development.
End users – How to complete compliance tasks, submit evidence, acknowledge policies, and participate in audits.
Consider partnering with compliance professionals who understand the South African regulatory environment and can translate requirements into platform configuration. For businesses needing support with FICA compliance frameworks, services that assist with FICA RMCP drafting and compliance practice guidance can help structure your ServiceNow implementation around proven compliance methodologies.
ServiceNow offers certification programs for platform administrators and implementation specialists. While not specific to financial services compliance, these certifications build technical expertise that compliance teams can apply to regulatory workflows.
Balancing Technology and Human Judgement
While grc service now automates many compliance processes, it cannot replace professional judgement. The platform executes workflows, tracks evidence, and monitors deadlines, but compliance officers must still make risk-based decisions.
Technology handles:
- Task routing and deadline tracking
- Evidence collection and storage
- Report generation and dashboard updates
- Workflow automation and approval chains
- Audit trail creation
Humans handle:
- Risk assessment and prioritization
- Regulatory interpretation
- Customer treatment decisions
- Investigation conclusions
- Remediation strategy
The most effective compliance programs combine platform automation with skilled professionals who understand regulatory intent, client needs, and business context.
For example, the platform can flag a client file with expired FICA verification, but a compliance officer must decide whether the expiry creates genuine risk or represents a technical gap that poses minimal concern given the client's profile and activity.
Cost-Benefit Analysis for South African FSPs
Implementing grc service now requires substantial investment. South African FSPs should conduct thorough cost-benefit analysis before committing.
Costs to consider:
- Platform licensing (typically priced per user or per module)
- Implementation consulting and configuration
- Integration development with existing systems
- Ongoing maintenance and support
- Training and change management
- Staff time for configuration and administration
Benefits to quantify:
- Reduced compliance staff time through automation
- Avoided regulatory penalties from improved compliance
- Faster audit preparation and response
- Better risk identification and mitigation
- Improved operational efficiency
- Enhanced client trust and market differentiation
For a mid-sized FSP with 50 representatives and a dedicated compliance team, the platform might reduce compliance administration time by 30-40%, consolidate multiple software subscriptions into one platform, and reduce audit preparation costs significantly. These savings can justify the investment over a 3-5 year period.
Smaller practices should honestly assess whether their compliance complexity warrants the investment or whether simpler solutions meet their needs.
Implementing effective governance, risk, and compliance frameworks is essential for South African financial services providers navigating POPIA, FICA, FAIS, and COFI requirements. GRC service now offers powerful capabilities to automate workflows, centralize evidence, and provide real-time compliance visibility, but success requires careful planning, ongoing maintenance, and skilled compliance professionals who understand both regulatory requirements and platform capabilities. For independent brokers and FSPs seeking expert guidance on building comprehensive compliance frameworks, Holistic Compliance Management Solutions (Pty) Ltd provides specialized services including FICA training, RMCP drafting, and compliance monitoring tailored to South African financial services regulations.
Schedule FICA Training
Who this is for: Compliance officers, FSP principals, client service teams, and independent brokers requiring practical FICA implementation guidance.
Your comprehensive FICA training includes:
- Customer due diligence procedures aligned with FIC Act requirements and Money Laundering Regulations
- RMCP documentation and risk assessment methodologies
- Suspicious transaction identification and reporting protocols
- Ongoing monitoring and record-keeping best practices
Contact Holistic Compliance Management Solutions (Pty) Ltd to schedule customized FICA training that builds the expertise your team needs to implement robust anti-money laundering compliance, whether you're managing workflows manually or through platforms like GRC ServiceNow.