OSHA Training Compliance for Financial Services in SA
Workplace safety and regulatory compliance share fundamental principles that extend far beyond traditional manufacturing environments. For South African financial services providers, understanding osha training compliance frameworks offers valuable insights into building robust compliance cultures that satisfy both occupational health requirements and financial sector mandates. Although OSHA (Occupational Safety and Health Administration) originates from United States labour law, its training compliance methodologies provide proven templates for developing systematic compliance programmes that align with South Africa's Occupational Health and Safety Act, POPIA, FICA, and FAIS requirements. Independent brokers, financial advisors, and FSPs can adapt these structured approaches to create comprehensive training systems that demonstrate regulatory competence across multiple compliance domains.
Understanding OSHA Training Compliance Fundamentals
OSHA training compliance represents a systematic approach to ensuring employees receive adequate instruction on workplace hazards, safety protocols, and regulatory requirements. The framework demands documented training programmes, verified competency assessments, and regular refresher courses to maintain standards.
Financial services providers in South Africa face parallel challenges when implementing POPIA data protection training, FICA anti-money laundering protocols, and FAIS fit and proper requirements. The structured methodology behind osha training compliance offers a blueprint for addressing these regulatory obligations systematically.
Core Components of Compliant Training Systems
Effective compliance training programmes share essential characteristics regardless of industry sector:
- Documented curriculum aligned to specific regulatory standards
- Competency verification through assessments and practical demonstrations
- Training records maintained for audit and inspection purposes
- Periodic refreshers to address regulatory updates and reinforce critical concepts
- Qualified instructors with subject matter expertise and training delivery skills
The National Safety Council provides comprehensive training resources that illustrate how structured programmes create measurable compliance outcomes. South African FSPs can apply these same principles when developing FAIS product training, FICA customer due diligence instruction, and POPIA data subject rights education.
Regulatory Training Requirements for FSPs
Financial Service Providers operating under FAIS must ensure representatives complete mandatory regulatory examinations and ongoing continuous professional development. This regulatory training ecosystem mirrors osha training compliance requirements in several key aspects:
| OSHA Training Element | FSP Compliance Equivalent | Documentation Required |
|---|---|---|
| Initial qualification | RE 1 & RE 5 regulatory exams | FSCA exam certificates |
| Hazard-specific training | Product-specific knowledge (RE 2-4) | CPD certificates |
| Annual refreshers | CPD requirements (minimum hours) | CPD provider records |
| Competency verification | Fit and proper assessments | Quarterly supervision records |
| Record retention | Training files (duration of employment + period) | Seven years per FAIS |
Independent brokers managing their own compliance often struggle with the administrative burden of maintaining these records. The systematic approach borrowed from osha training compliance frameworks simplifies this challenge by creating standardised templates and workflows.
Building a Compliance Training Programme for Financial Services
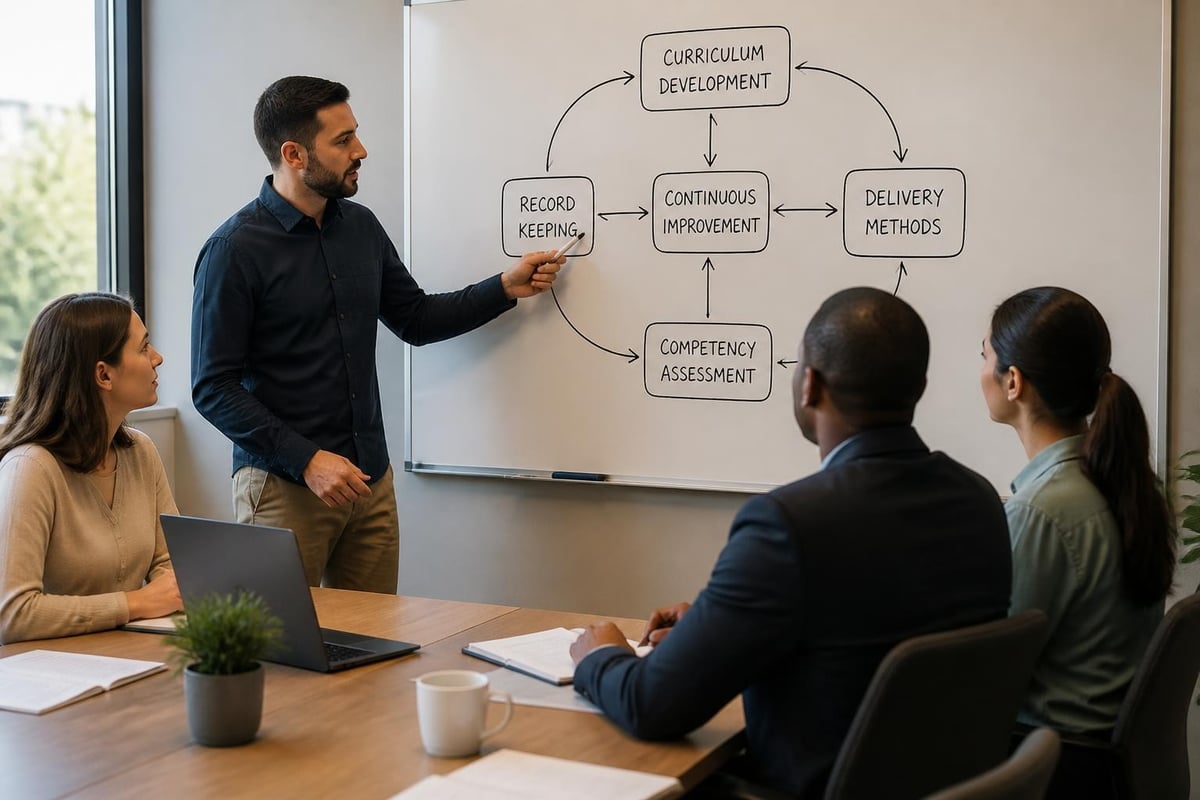
Developing a comprehensive training programme requires mapping regulatory obligations to specific learning outcomes and delivery methods. South African financial advisors must address multiple compliance frameworks simultaneously, making integration essential.
Mapping Regulatory Requirements to Training Needs
Begin by conducting a thorough compliance obligation inventory:
- FAIS requirements: Identify all applicable product categories (RE 2, RE 3, RE 4) and representative functions
- FICA obligations: Document customer due diligence procedures, risk assessment protocols, and reporting requirements
- POPIA mandates: Outline data processing activities, lawful bases, and data subject rights procedures
- COFI requirements: Establish customer fairness standards, disclosure obligations, and complaint handling processes
- Internal policies: Capture firm-specific procedures, quality standards, and practice management requirements
This inventory becomes the foundation for your training curriculum. Each obligation should connect to specific learning objectives, assessment criteria, and refresher schedules.
Selecting Appropriate Training Delivery Methods
OSHA’s guidance on computer-based training limitations emphasises that purely online instruction cannot adequately prepare employees for hands-on compliance tasks. Financial services training faces identical constraints.
Effective delivery methods for FSP compliance training:
- Classroom sessions for complex regulatory concepts (FICA risk assessment frameworks, POPIA lawful processing bases)
- Practical workshops for customer interaction scenarios (treating customers fairly, product suitability assessments)
- E-learning modules for knowledge acquisition (regulatory definitions, prohibited conduct examples)
- Case study analysis for application skills (identifying conflicts of interest, recognising suspicious transactions)
- Mentored practice for new representatives (supervised client meetings, file review processes)
The blended approach ensures representatives develop both theoretical knowledge and practical competency. For instance, Regulatory Exam training combines structured content delivery with practice assessments to verify mastery before candidates attempt official examinations.
Developing Training Content and Materials
Quality training materials form the backbone of any compliance programme. Content development should follow structured principles adapted from osha training compliance best practices.
Content development checklist:
- Start with learning objectives derived directly from regulatory text
- Use plain language explanations supplemented by regulatory references
- Include real-world examples from South African financial services contexts
- Provide job aids and quick reference guides for daily application
- Incorporate assessment questions that test comprehension and application
- Update materials within 30 days of regulatory amendments
Financial services regulations evolve continuously. FICA amendments, POPIA enforcement notices, and FAIS conduct standards require ongoing content maintenance. Establishing quarterly content review cycles ensures training materials remain current and accurate.
Implementing Effective Training Documentation Systems
Documentation transforms compliance training from an activity into verifiable evidence of regulatory adherence. OSHA training compliance standards emphasise meticulous record-keeping practices that South African FSPs should emulate.
Essential Training Records and Files
Every training intervention requires supporting documentation that proves completion, comprehension, and competency:
| Record Type | Contents | Retention Period | Audit Purpose |
|---|---|---|---|
| Training register | Attendee names, dates, topics, duration | Seven years | Demonstrates systematic training |
| Course materials | Presentation slides, handouts, assessments | Current + two cycles | Shows curriculum coverage |
| Assessment results | Test scores, practical evaluations, feedback | Seven years | Proves competency verification |
| Attendance records | Sign-in sheets, digital confirmations | Seven years | Confirms individual participation |
| Training certificates | Completion statements, CPD credits | Permanent in representative file | Supports fit and proper status |
These records must remain accessible for FSCA inspections, internal audits, and compliance reviews. Digital record management systems simplify organisation but require adequate POPIA-compliant data protection measures.
Creating Audit-Ready Training Files
FSCA inspectors regularly request evidence of representative competence and ongoing training. Preparing audit-ready files prevents compliance findings and demonstrates professional practice management.
Components of a comprehensive representative training file:
- Qualification history (matric certificate, relevant degrees or diplomas)
- Regulatory examination certificates (RE 1, RE 5, applicable product-specific exams)
- Initial FSP onboarding training records (FICA, POPIA, internal policies)
- Annual CPD plans and completion certificates
- Product knowledge assessments (minimum annually per product category)
- Supervision and coaching records (quarterly file reviews, meeting notes)
- Fit and proper declarations (annual attestations)
Maintaining these files demonstrates the systematic approach to competency management that regulators expect. The discipline mirrors osha training compliance requirements for safety-critical positions where inadequate training creates regulatory liability.
Integrating FICA and POPIA Training Requirements
Money laundering prevention and data protection represent critical compliance obligations for all FSPs. Effective training programmes integrate these requirements seamlessly rather than treating them as separate initiatives.
FICA Training Essentials for Financial Representatives
The Financial Intelligence Centre Act imposes specific obligations on accountable institutions and their representatives. Training must address both technical requirements and practical application.
Core FICA training topics:
- Customer identification and verification: Acceptable documents, verification procedures, record-keeping requirements
- Risk assessment and management: Client risk categorisation, enhanced due diligence triggers, ongoing monitoring
- Suspicious transaction detection: Red flag indicators, reporting obligations, internal escalation procedures
- Record retention: Required documents, retention periods, secure storage requirements
- Sanctions screening: UNSCR lists, domestic sanction requirements, politically exposed persons
Representatives handling client onboarding require practical training that goes beyond regulatory text. Role-playing exercises, sample document reviews, and decision-tree tools help embed knowledge into daily workflows. Holistic Compliance Management Solutions assists FSPs with developing practical FICA training programmes tailored to broker workflows and client interaction patterns.
POPIA Compliance Training Frameworks
The Protection of Personal Information Act fundamentally changed how financial services firms handle client data. Every employee who processes personal information requires appropriate training on their obligations.
POPIA training curriculum structure:
- Foundation concepts: Personal information definitions, responsible party obligations, operator duties
- Lawful processing conditions: Eight conditions explained with financial services examples
- Data subject rights: Access requests, correction procedures, objection protocols, deletion requirements
- Security safeguards: Physical security, digital protection, third-party agreements, breach response
- Cross-border transfers: Adequacy assessments, data subject consent, contractual safeguards
New representatives should receive comprehensive POPIA training during onboarding, with annual refreshers addressing regulatory updates and common compliance gaps. Assessment questions should test practical application rather than mere memorisation of regulatory definitions.
Developing Integrated Compliance Workflows
The most effective compliance training connects individual requirements into cohesive workflows that representatives follow naturally. Integration reduces duplication and demonstrates how regulations work together in practice.
Example integrated workflow: New client onboarding
- Collect FICA identification documents (FICA compliance)
- Obtain POPIA processing consent and provide privacy notice (POPIA compliance)
- Complete client risk assessment (FICA risk management)
- Conduct needs analysis and document advice basis (FAIS compliance)
- Provide product disclosure and key features (COFI compliance)
- Obtain signed mandate and instructions (FAIS record-keeping)
- Create secure client file with retention schedule (FICA and POPIA)
Training representatives on this integrated process rather than isolated compliance requirements improves both efficiency and compliance outcomes. Assessment scenarios should test the complete workflow to verify competency.
Technology-Enhanced Training Approaches
Modern training delivery increasingly incorporates digital tools and immersive technologies. While maintaining the hands-on elements essential for compliance competency, technology enhances accessibility, consistency, and measurement.
Learning Management Systems for Compliance Training
Digital learning platforms streamline training administration whilst creating comprehensive audit trails. Features particularly valuable for FSP compliance programmes include:
- Automated enrolment based on representative roles and product categories
- Progress tracking showing completion rates and outstanding requirements
- Assessment engines with randomised question banks and automated scoring
- Certificate generation integrated with CPD tracking systems
- Regulatory update alerts triggering mandatory refresher assignments
- Reporting dashboards for compliance officers and key individuals
When evaluating learning management systems, prioritise POPIA-compliant data handling, reliable record retention, and South African time zone support. The system should integrate with existing practice management platforms to avoid duplicate data entry.
Immersive Training Technologies
Recent research on immersive technologies for industrial safety training demonstrates how virtual reality and augmented reality enhance retention and skill transfer. Financial services can apply similar approaches to compliance scenarios.
Applications for FSP compliance training:
- Virtual customer interactions: Practice difficult conversations (declining unsuitable products, explaining fees, handling complaints) in risk-free environments
- Augmented reality job aids: Overlay compliance checklists and decision trees during real customer meetings
- Scenario simulations: Navigate complex situations (suspicious transaction identification, conflict of interest management) with branching outcomes
- Interactive case studies: Explore compliance failures and regulatory enforcement actions through immersive narratives
These technologies remain emerging tools rather than primary delivery methods. They supplement rather than replace practical mentorship and hands-on experience. Cost considerations currently limit adoption amongst smaller independent practices.
Mobile Learning and Microlearning Approaches
Representatives working in field-based roles benefit from accessible, bite-sized training content deliverable via mobile devices. Microlearning modules addressing specific compliance topics support just-in-time learning and rapid refreshers.
Effective microlearning topics:
- FICA document verification procedures (five-minute module with document examples)
- POPIA breach response steps (decision tree format, printable job aid)
- Product-specific disclosure requirements (comparison tables, mandatory statements)
- Common compliance pitfalls (short case studies with correct responses)
- Regulatory update summaries (three-minute briefings on new requirements)
Mobile delivery requires careful POPIA consideration regarding data security, device management, and personal information access controls. Policies should address acceptable use, security requirements, and data retention for training accessed via personal devices.
Measuring Training Effectiveness and Competency
OSHA training compliance extends beyond attendance records to verified competency and demonstrated skill application. Financial services compliance programmes require identical rigour in measuring training outcomes.
Assessment Methods and Competency Verification
Multiple assessment approaches provide comprehensive evidence of representative competency across different skill dimensions:
| Assessment Type | Purpose | Frequency | Documentation |
|---|---|---|---|
| Knowledge tests | Verify understanding of regulations | Post-training and annually | Scored assessments with pass thresholds |
| Practical demonstrations | Confirm procedure execution | Initial certification and when processes change | Observation checklists, supervisor sign-off |
| File reviews | Assess real-world application | Quarterly minimum | Quality scores, corrective action plans |
| Mystery shops | Evaluate customer interaction compliance | Semi-annually | Assessment forms, coaching notes |
| Compliance audits | Identify systemic gaps | Annually | Audit reports, remediation tracking |
Competency verification should use consistent standards across all representatives. Assessment criteria derived directly from regulatory requirements ensure objectivity and relevance. Pass thresholds must reflect true mastery rather than minimal performance.
Continuous Improvement Through Training Metrics
Data-driven compliance management requires systematic measurement of training programme effectiveness. Key performance indicators should track both outputs (training completion) and outcomes (compliance performance).
Essential training metrics:
- Completion rates: Percentage of required training finished within scheduled timeframes
- Assessment scores: Average results, pass/fail rates, common knowledge gaps
- Time to competency: Duration from hire to independent practice authorisation
- Compliance findings: Correlation between training participation and audit results
- Customer complaints: Frequency of issues related to inadequate representative knowledge
- Regulatory breaches: Incidents attributable to training deficiencies
Quarterly metric reviews should inform curriculum adjustments, delivery method changes, and resource allocation decisions. Declining assessment scores signal content issues or inadequate instructor preparation. Rising complaint rates linked to specific topics indicate training effectiveness gaps requiring immediate attention.
Supervision and Coaching as Training Extension
Formal training programmes establish foundational knowledge, but daily supervision embeds compliance competency into routine practice. Regular coaching reinforces learning and identifies individual development needs.
Effective supervision practices:
- Weekly file reviews during initial representative development (first 90 days)
- Monthly case discussions addressing complex compliance scenarios
- Quarterly performance conversations linking compliance metrics to development plans
- Annual competency assessments determining continued authorisation and product allocation
Supervision records form part of the representative's training file and demonstrate ongoing competency management. These records prove particularly valuable during FSCA inspections when inspectors question representative fitness and propriety.
Addressing Common Compliance Training Challenges
Implementation of comprehensive training programmes encounters predictable obstacles. Anticipating these challenges and developing mitigation strategies improves programme sustainability and effectiveness.
Time Constraints and Business Pressures
Independent brokers frequently cite time pressures as barriers to comprehensive compliance training. Revenue-generating activities compete with training requirements, creating tension between immediate business needs and long-term regulatory compliance.
Strategies for overcoming time barriers:
- Schedule training during naturally slower business periods (January for retail-focused practices)
- Implement modular programmes allowing progressive completion over extended timeframes
- Leverage technology for flexible, self-paced learning where appropriate
- Integrate training with regular team meetings rather than scheduling separate sessions
- Outsource training delivery to specialists, freeing internal resources for client service
The compliance monitoring services offered by specialised providers can supplement internal training capacity whilst ensuring regulatory standards are maintained. External trainers bring fresh perspectives and often achieve higher engagement than repeated internal presentations.
Maintaining Engagement and Retention
Compliance training suffers from reputation as dry, technical content disconnected from daily practice. Low engagement reduces knowledge retention and application, undermining programme effectiveness.
Engagement enhancement techniques:
- Use real case studies from South African enforcement actions and ombudsman determinations
- Incorporate interactive elements (polls, quizzes, small group discussions) every 15 minutes
- Connect compliance requirements to representative self-interest (avoiding personal liability, protecting professional reputation)
- Gamify learning with leader boards, achievement badges, and completion challenges
- Invite guest speakers (FSCA representatives, compliance specialists, experienced practitioners)
Representatives engage more deeply when they understand the "why" behind requirements. Explaining the customer protection objectives underlying regulations creates buy-in that rote rule recitation cannot achieve.
Budget Limitations for Smaller Practices
Comprehensive training programmes require investment in content development, delivery resources, technology platforms, and ongoing maintenance. Smaller independent practices often lack budgets for sophisticated training infrastructure.
Cost-effective training approaches:
- Join industry associations offering shared training resources and group sessions
- Utilise free regulatory guidance from FSCA, FIC, and Information Regulator
- Develop peer learning groups sharing training responsibilities across non-competing practices
- Focus initial investment on high-risk areas (FICA, product suitability) before expanding curriculum
- Negotiate group rates with training providers for consortium delivery
Quality training represents investment rather than expense. The cost of non-compliance (regulatory fines, reputational damage, business disruption) vastly exceeds training programme costs. Budget allocation should reflect risk prioritisation rather than treating all training equally.
Keeping Content Current with Regulatory Changes
South African financial services regulation evolves continuously. FICA amendments, POPIA enforcement guidance, FAIS conduct standards, and COFI implementation create ongoing content maintenance requirements.
Regulatory update management process:
- Monitor official sources (Government Gazette, FSCA communications, FIC notices)
- Assess training impact within five business days of regulatory publication
- Update affected content and mark version/effective date clearly
- Deploy refresher training within 30 days for material changes
- Document training delivery in compliance registers
- Verify representative comprehension through brief assessments
Establishing formal regulatory monitoring processes ensures training programmes remain current. Assigning specific responsibility for monitoring (compliance officer or designated representative) prevents updates falling through administrative cracks.
Regulatory Examination Training Requirements
The Regulatory Examinations administered by FSCA verify minimum competency for financial services representatives. Adequate preparation represents both a FAIS compliance obligation and a business necessity.
Understanding RE Exam Structure and Content
Different representative functions require specific regulatory examination passes:
- RE 1: General regulatory framework applicable to all representatives
- RE 5: Retail representative competency (mandatory for most brokers)
- RE 2: Long-term insurance product knowledge (life, disability, funeral)
- RE 3: Short-term personal lines insurance
- RE 4: Short-term commercial lines insurance
Each examination tests both theoretical knowledge and practical application. Pass rates vary significantly between candidates who receive structured preparation and those attempting examinations without adequate training.
Developing Effective Exam Preparation Programmes
Successful examination preparation requires more than content delivery. Candidates need test-taking strategies, time management skills, and stress management techniques alongside subject matter knowledge.
Comprehensive RE exam preparation components:
- Content instruction: Systematic coverage of syllabus topics with regulatory references
- Practice assessments: Multiple mock examinations under timed conditions
- Question analysis: Techniques for identifying correct answers and eliminating distractors
- Regulatory updates: Recent amendments and enforcement priorities
- Study planning: Personalised schedules balancing preparation with work commitments
- Remediation support: Targeted assistance for candidates with previous attempts
First-time pass rates directly impact business operations. Failed attempts delay representative authorisation, limit product allocations, and create reputational concerns. Investment in quality preparation reduces business disruption and representative frustration.
Post-Examination Competency Development
Passing regulatory examinations demonstrates minimum competency rather than complete mastery. Newly qualified representatives require ongoing development before achieving independent practice capability.
Progressive competency development pathway:
- Weeks 1-4: Shadowing experienced representatives, observing client interactions, reviewing completed files
- Weeks 5-8: Supervised client meetings with mentor present, joint file preparation
- Weeks 9-12: Independent meetings with file review before finalisation, weekly feedback sessions
- Month 4+: Quarterly file sampling, monthly team case discussions, annual competency verification
This structured approach mirrors osha training compliance principles requiring both initial qualification and ongoing competency verification. Documentation at each development stage proves systematic representative management during regulatory inspections.
Building a Compliance Culture Through Training
Effective compliance extends beyond rule following to creating organisational cultures where ethical conduct and customer protection drive decision-making. Training programmes shape culture when designed intentionally for that purpose.
Leadership Commitment and Tone from the Top
Key individuals and senior management must visibly prioritise compliance for training programmes to achieve cultural impact. Representatives model behaviours they observe from leadership.
Leadership actions demonstrating compliance commitment:
- Personal participation in compliance training (not exempting themselves as "too experienced")
- Regular communication linking business success to compliance excellence
- Resource allocation treating training as investment rather than cost centre
- Recognition systems celebrating compliance achievements alongside sales performance
- Swift corrective action when compliance failures occur, regardless of performer status
Key individuals completing the same training as representatives signals that compliance applies equally across all organisational levels. This consistency builds credibility and reinforces expectations.
Connecting Compliance to Customer Outcomes
Training that presents compliance as bureaucratic burden generates resistance and minimal engagement. Reframing compliance as customer protection creates purpose and meaning.
Customer-centric compliance messaging:
- FICA protocols protect customers from fraud and identity theft
- POPIA requirements respect customer privacy and build trust
- FAIS suitability assessments ensure customers receive appropriate advice
- COFI disclosure standards enable informed customer decisions
- Complaints handling procedures demonstrate respect for customer concerns
Case studies illustrating how compliance requirements prevented customer harm prove more compelling than regulatory citations. Representatives who understand the customer protection rationale demonstrate higher compliance adherence.
Embedding Compliance in Daily Workflows
Compliance becomes cultural when integrated seamlessly into routine business processes rather than treated as separate activity. Training should emphasise workflow integration.
Integration strategies:
- Compliance checklists built into client management systems
- Template documents incorporating regulatory requirements
- File review processes verifying compliance before finalisation
- Team meetings including compliance topic discussions
- Performance metrics balancing growth and compliance objectives
When compliance becomes "how we do things" rather than "extra tasks", sustainable behaviour change occurs. Training that demonstrates integrated workflows accelerates this cultural shift.
Who this is for: Independent financial brokers, compliance officers at FSPs, key individuals, and financial advisors seeking systematic approaches to regulatory training and competency management.
Robust osha training compliance methodologies provide proven frameworks for South African financial services providers navigating complex regulatory obligations across FAIS, FICA, POPIA, and COFI requirements. Systematic training programmes demonstrate regulatory commitment whilst building representative competency and protecting customer interests. Whether you're implementing comprehensive compliance training for the first time or enhancing existing programmes, Holistic Compliance Management Solutions offers specialised expertise helping FSPs develop practical, audit-ready training systems. Schedule your FICA training consultation today to discuss your specific training needs, including structured programmes covering FICA risk assessment frameworks, POPIA data protection protocols, and regulatory examination preparation tailored to independent broker workflows.