AML Audit: Comprehensive Guide for South African FSPs
Anti-money laundering compliance remains one of the most critical obligations facing South African financial services providers in 2026. As regulatory scrutiny intensifies and enforcement actions increase, the aml audit has evolved from a regulatory tick-box exercise into a strategic risk management function. For independent financial advisors, brokers, and FSPs operating under FAIS, FICA, and POPIA frameworks, a comprehensive aml audit provides the foundation for sustainable compliance whilst protecting your business from regulatory penalties, reputational damage, and criminal liability. This guide explores the essential components of an effective aml audit tailored specifically to the South African compliance landscape, offering practical implementation steps that align with your operational reality.
Understanding the AML Audit Framework in South Africa
An aml audit is fundamentally an independent, systematic evaluation of your organisation's anti-money laundering and counter-terrorist financing controls. Under the Financial Intelligence Centre Act (FICA), all accountable institutions-including FSPs, brokers, and financial advisors-must establish and maintain compliance programmes that prevent their services from being exploited for money laundering or terrorist financing purposes.
The audit function serves multiple purposes within the South African regulatory ecosystem. First, it validates that your risk management and compliance programme (RMCP) operates as designed. Second, it identifies gaps, weaknesses, and areas requiring remediation before regulators discover them. Third, it demonstrates to the Financial Intelligence Centre (FIC) and the Financial Sector Conduct Authority (FSCA) that your organisation takes its obligations seriously.
Regulatory Foundations and Expectations
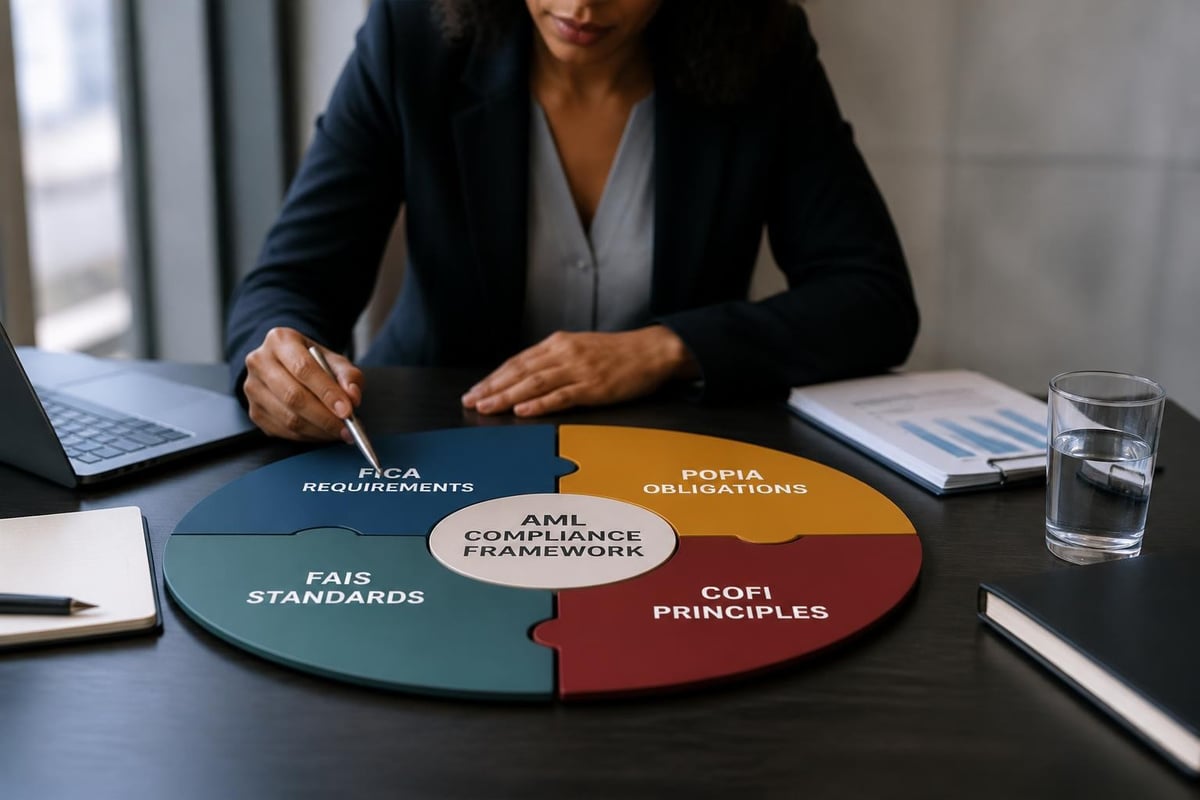
South African FSPs must navigate a complex web of interconnected compliance obligations. FICA establishes the core anti-money laundering framework, requiring customer due diligence, record-keeping, reporting of suspicious transactions, and the appointment of a compliance officer. POPIA governs how you collect, process, and protect personal information during these compliance activities. FAIS and COFI set conduct standards that intersect with AML obligations, particularly regarding client onboarding and suitability assessments.
The Financial Sector Regulation Act (2017) introduced enhanced supervisory powers and coordination between regulators. In 2026, the FSCA has demonstrated increased willingness to impose administrative sanctions for AML failures, with penalties reaching millions of rands for systematic compliance breakdowns. This enforcement environment makes the aml audit an essential defensive tool.
International standards also influence South African expectations. The Basel Committee’s Core Principles for Effective Banking Supervision emphasise the importance of independent testing and internal audit arrangements, principles that South African regulators increasingly expect FSPs to adopt regardless of size.
Designing Your AML Audit Scope and Methodology
A properly scoped aml audit begins with understanding your specific risk profile. South African brokers and advisors operate across diverse market segments-from retail investment advice to commercial insurance brokerage-each presenting distinct money laundering risks. Your audit scope must reflect these specific exposures rather than applying a generic template.
Risk-Based Audit Planning
The EBA Guidelines on ML/TF Risk Factors provide a comprehensive framework for identifying and assessing money laundering risks, principles that align closely with South African regulatory expectations. Your audit planning should consider:
- Customer risk factors: high net-worth individuals, politically exposed persons (PEPs), clients from high-risk jurisdictions, complex ownership structures, cash-intensive businesses
- Product and service risk factors: offshore investments, trust arrangements, life insurance policies with investment components, high-value single premium products
- Geographic risk factors: clients or beneficial owners from countries with weak AML controls, sanctions exposure, correspondent banking relationships
- Distribution channel risk factors: non-face-to-face onboarding, introducer arrangements, online platforms without robust verification
For most independent brokers and small FSPs, a risk-based approach means concentrating audit resources on higher-risk client segments whilst applying lighter-touch testing to lower-risk, well-understood relationships. Document your risk assessment methodology clearly-regulators expect you to justify your audit scope decisions.
Determining Audit Frequency and Independence
FICA does not prescribe specific audit frequency, but the FIC expects "regular" independent reviews proportionate to your risk profile and business scale. Industry practice in South Africa typically follows these patterns:
| FSP Category | Typical Audit Frequency | Independence Requirement |
|---|---|---|
| Large FSPs (50+ advisors) | Annual comprehensive audit | External auditor or dedicated internal audit function |
| Medium FSPs (10-49 advisors) | Annual or biennial audit | External auditor or senior compliance officer (not day-to-day compliance) |
| Small FSPs (2-9 advisors) | Biennial audit or file reviews | External compliance consultant or compliance officer peer review |
| Sole practitioners | Biennial focused review | External compliance consultant |
The independence requirement presents practical challenges for smaller practices. The FinCEN guidance on independent testing clarifies that independence means the auditor has no direct responsibility for the compliance function being tested. For small brokerages, engaging an external compliance consultant often provides the most cost-effective solution whilst satisfying independence expectations.
Core Components of an Effective AML Audit
A comprehensive aml audit for South African FSPs should systematically evaluate each pillar of your FICA compliance programme. The testing approach combines documentation review, transaction sampling, control testing, and interview procedures to assess both design effectiveness and operational performance.
Customer Due Diligence and Onboarding Controls
Customer identification and verification (CDD) forms the foundation of AML compliance. Your audit should test whether client onboarding procedures capture all required information under FICA and verify its accuracy through appropriate documentation.
Key testing procedures include:
- Sample selection: Draw a representative sample of new clients onboarded during the audit period, stratified by risk category and advisor
- Documentation completeness: Verify that client files contain certified identification documents, proof of address, source of wealth/funds declarations, and beneficial ownership information for entities
- Verification quality: Assess whether verification procedures (FICA certification, electronic verification, video identification) meet regulatory standards
- Risk assessment: Confirm that client risk ratings align with documented risk factors and that enhanced due diligence was applied to higher-risk relationships
- POPIA compliance: Verify that privacy notices were provided, consent obtained where required, and personal information processing aligns with stated purposes
For South African brokers, particular attention should focus on beneficial ownership identification for trusts and companies. The FICA regulations require identification of all beneficial owners holding 25% or more interest, a threshold many advisors struggle to apply consistently.
Ongoing Monitoring and Transaction Surveillance
Static onboarding compliance is insufficient-FICA requires ongoing monitoring of client relationships to detect unusual patterns or changes in risk profile. The aml audit should evaluate whether your monitoring mechanisms function effectively.
Testing procedures typically include:
- Periodic review execution: Verify that client files undergo periodic reviews at intervals commensurate with risk ratings (typically annually for high-risk, triennially for low-risk)
- Transaction monitoring: For FSPs handling client funds or investments, assess whether transaction patterns receive appropriate scrutiny
- Client activity alignment: Test whether client transactions align with stated occupation, income sources, and investment objectives
- Trigger event responses: Verify that risk rating changes, address updates, or unusual activity prompted appropriate due diligence updates
Many independent advisors lack sophisticated transaction monitoring systems. For smaller practices, the audit should focus on whether advisors exercise professional scepticism and escalate concerns appropriately rather than expecting automated surveillance capabilities.
Suspicious Activity Identification and Reporting
The obligation to report suspicious and unusual transactions (STRs and UTRs) to the FIC represents one of the highest-risk compliance areas. Regulatory enforcement actions frequently cite failures in this domain. Your aml audit must rigorously assess the suspicious activity reporting framework.
Critical audit procedures include:
- Red flag awareness: Interview advisors to assess their understanding of money laundering typologies and suspicious activity indicators relevant to your business
- Escalation mechanics: Test whether advisors know how to escalate concerns and whether the compliance officer receives all potential suspicious activity reports
- Investigation quality: Review internal investigations of escalated concerns to assess thoroughness, documentation, and decision-making
- FIC reporting: For filed STRs/UTRs, verify timeliness (within prescribed periods), completeness of information, and supporting documentation
- Declining to act: Where investigations concluded that reporting was not required, assess the reasonableness of conclusions and documentation quality
The UK FCA’s guidance on money laundering and terrorist financing provides practical examples of suspicious activity indicators that translate well to the South African context, including unexplained wealth, unusual transaction patterns, and evasive client behaviour.
Record-Keeping and Document Retention
FICA mandates retention of client identification records for five years after the business relationship ends, and transaction records for five years after the transaction. POPIA imposes additional requirements around data minimisation and retention limitation. Your aml audit should verify compliance with both frameworks.
Audit testing should cover:
- Retention policy documentation: Verify that written policies address both FICA and POPIA requirements and resolve any conflicts
- Physical and electronic storage: Assess whether records are maintained securely, remain accessible for regulators, and include appropriate backup arrangements
- Destruction procedures: For records reaching retention limits, verify secure destruction procedures that prevent unauthorised access
- Cross-border storage: If using cloud providers or offshore storage, confirm compliance with POPIA cross-border transfer requirements
For advisors drafting or updating their FICA RMCP, integrating clear record-keeping procedures significantly streamlines future audit processes whilst demonstrating regulatory commitment.
Implementing Audit Findings and Remediation
Identifying compliance gaps represents only half the audit value-systematic remediation determines whether the exercise strengthens your control environment. South African FSPs should establish structured remediation processes that prioritise findings, assign accountability, and track implementation.
Finding Classification and Prioritisation
Not all audit findings carry equal risk or urgency. Effective remediation requires classification that reflects both regulatory impact and operational feasibility. A typical framework includes:
| Severity Level | Definition | Remediation Timeline | Escalation |
|---|---|---|---|
| Critical | Systemic control failure; significant regulatory exposure; potential FIC reporting failure | Immediate (within 14 days) | Key individual, board notification |
| High | Material control weakness; regulatory breach likely without remediation | 30 days | Compliance officer, management |
| Medium | Control gap requiring attention; moderate regulatory risk if unaddressed | 90 days | Compliance officer |
| Low | Best practice opportunity; minimal regulatory impact | 180 days | Compliance officer |
Critical findings might include failures to report suspicious transactions, systematic CDD deficiencies across client portfolios, or absence of required FICA training. High findings could involve inadequate beneficial ownership verification or incomplete risk assessments. Medium and low findings typically address documentation quality, process efficiency, or enhanced controls for specific scenarios.
Developing Remediation Action Plans
Each audit finding should generate a documented action plan specifying the remediation approach, responsible person, target completion date, and success criteria. Effective action plans address root causes rather than symptoms.
For example, if the aml audit identifies inconsistent risk rating applications across advisors, a superficial response might simply re-rate affected clients. A root-cause approach would implement standardised risk assessment tools, deliver targeted training on risk factors, and establish compliance officer review of all high-risk ratings.
The OCC’s Community Bank BSA/AML Examination Procedures offer detailed procedural guidance on evaluating remediation effectiveness, principles South African FSPs can adapt to their context.
Management and Board Oversight
For larger FSPs with governance structures, audit findings and remediation progress should receive regular board or key individual oversight. Quarterly compliance reports should summarise:
- Open findings by severity and age
- Remediation progress against planned timelines
- Root cause analysis of recurring issues
- Resource requirements for complete remediation
- Regulatory engagement regarding significant findings
Even sole practitioners benefit from formalising oversight-reviewing your own remediation progress monthly ensures momentum and demonstrates personal accountability to regulators.
Training and Competency Requirements
An often-overlooked aspect of the aml audit involves evaluating whether your staff and advisors possess adequate AML knowledge and skills. FICA explicitly requires accountable institutions to provide ongoing training on money laundering risks and compliance obligations.
Assessing Training Programme Effectiveness
Your audit should examine both training inputs (what training is provided) and outputs (whether training achieves competency objectives). Effective testing procedures include:
- Training content review: Assess whether training materials cover FICA obligations, suspicious activity indicators, internal procedures, and relevant case studies
- Delivery and attendance: Verify that all advisors and relevant staff receive initial and annual refresher training, with attendance documented
- Knowledge testing: Interview advisors or administer written assessments to evaluate whether training translated into practical understanding
- Scenario response: Present hypothetical situations (e.g., client provides inconsistent source of funds information) and assess whether advisors identify red flags and follow proper escalation
Many South African brokers struggle with training quality rather than quantity-advisors sit through generic presentations without gaining practical competency. Scenario-based training that reflects your specific business model and client types delivers superior results.
Compliance Officer Competency
The FICA compliance officer bears ultimate responsibility for the compliance programme's effectiveness. The aml audit should evaluate whether the compliance officer possesses appropriate qualifications, experience, authority, and resources. Assessment criteria include:
- Formal qualifications (FICA training, compliance certifications, regulatory exam success)
- Practical experience in financial services compliance
- Authority to escalate concerns to senior management and halt potentially problematic transactions
- Sufficient time allocation to compliance duties (particularly for part-time or dual-role officers)
- Access to resources including legal advice, external consultants, and training materials
For FSPs where the compliance officer also serves as an advisor or performs other operational roles, the audit should critically assess whether conflicting responsibilities compromise compliance effectiveness.
Technology and Data Management in AML Audits
South African FSPs increasingly leverage technology for compliance management, from basic spreadsheet tracking to sophisticated compliance platforms. The aml audit should evaluate whether technology solutions enhance rather than obscure compliance effectiveness.
System and Data Integrity
If you maintain client information, risk assessments, or compliance records electronically, audit procedures should verify:
- Data accuracy: Test whether system data matches source documents and whether data migration or integration preserved information integrity
- Access controls: Under POPIA, verify that personal information access is restricted to authorised persons and that audit logs track access
- Business continuity: Assess backup procedures, disaster recovery arrangements, and the ability to provide regulators with required information during outages
- Vendor management: For third-party compliance platforms or cloud services, verify contractual protections, data processing agreements, and vendor AML controls
Many independent brokers use basic tools effectively-Excel spreadsheets can deliver robust compliance tracking if properly designed and maintained. The audit should focus on whether your chosen approach suits your scale and complexity rather than expecting enterprise-grade systems.
Regulatory Technology Considerations
The FinCEN fact sheet on proposed AML/CFT programme reforms discusses evolving expectations around technology-enabled compliance, including automated transaction monitoring and electronic verification. Whilst these U.S. proposals don't directly apply in South Africa, they signal global regulatory trends.
South African FSPs should consider technology investments that deliver efficiency without introducing new risks. Electronic FICA verification services, for instance, can streamline onboarding whilst maintaining compliance quality, provided you understand the verification methods and limitations.
Integrating POPIA and COFI with AML Compliance
The intersection between AML obligations, data protection, and customer fairness creates complex compliance challenges. A comprehensive aml audit must evaluate how these frameworks interact within your practice.
POPIA Compliance in AML Processes
POPIA requires that personal information collection serve specified, lawful purposes and that you collect only information necessary for those purposes. AML compliance provides a lawful basis for extensive information collection, but you must navigate this relationship carefully.
Audit procedures should verify:
- Privacy notices: Clients receive clear information about AML compliance purposes for personal information processing
- Consent versus legal obligation: Your POPIA documentation correctly identifies AML compliance as a legal obligation rather than requiring consent
- Data minimisation: You collect beneficial ownership and source of funds information proportionate to assessed risk
- Third-party sharing: FIC reporting and regulator access are documented as lawful sharing purposes
- Retention alignment: Client information retained for FICA purposes (5 years) aligns with POPIA retention limitation principles
The tension between AML and data protection is particularly acute when clients exercise POPIA rights. For example, a client's deletion request cannot override your FICA obligation to retain records for prescribed periods-your audit should verify that procedures address these scenarios correctly.
COFI and Customer Fairness
The Conduct of Financial Institutions (COFI) Bill, expected to commence in phases from 2026, introduces heightened customer fairness obligations across financial services. Whilst AML compliance necessarily creates customer friction (additional documentation, onboarding delays), COFI requires that you apply requirements proportionately and communicate clearly.
Your aml audit should assess whether compliance procedures meet COFI fairness standards:
- Proportionality: Enhanced due diligence requirements for higher-risk clients are justified by risk factors and applied consistently
- Communication quality: You explain AML requirements to clients in plain language, avoiding unnecessary jargon
-
- Timely processing: Client onboarding and transaction processing delays attributable to AML checks are minimised and communicated
- Complaint handling: Client concerns about AML procedures receive appropriate investigation and response
Independent brokers balancing compliance rigour with client service should document risk-based decision-making clearly-this protects you if clients complain about "excessive" requirements whilst demonstrating regulatory compliance.
Common AML Audit Findings in South African FSP Context
Understanding typical compliance weaknesses helps you proactively strengthen controls before conducting a formal aml audit. Based on FIC enforcement actions and industry experience, South African brokers most frequently encounter these findings:
Documentation and Record-Keeping Deficiencies
- Incomplete client files: Missing certified identification documents, outdated addresses, absent beneficial ownership information for entities
- Poor FICA certification: Certificates not properly completed, certifiers lacking appropriate status, electronic copies without certification
- Inadequate source of funds: Generic declarations without supporting documentation for large or unusual transactions
- Missing risk assessments: Client files lack documented risk ratings or ratings not updated when circumstances change
Suspicious Activity Reporting Failures
- Insufficient red flag training: Advisors fail to recognise common suspicious activity indicators in their business context
- Escalation gaps: No clear procedure for advisors to escalate concerns confidentially to the compliance officer
- Investigation documentation: Minimal records of how potential suspicious activity was assessed and why reporting was/wasn't required
- Reporting delays: STRs filed beyond prescribed timeframes or not at all despite concerning activity
Governance and Oversight Weaknesses
- Compliance officer authority: Officer lacks practical ability to challenge business decisions or halt problematic transactions
- Training inadequacy: Generic, infrequent training that doesn't address business-specific risks and scenarios
- Management reporting: Compliance officer doesn't provide regular AML risk reporting to key individuals or board
- Resource constraints: Compliance function severely under-resourced relative to business scale and risk profile
Risk Assessment and RMCP Deficiencies
For advisors developing or refining their risk management and compliance programme, addressing these common weaknesses significantly improves audit outcomes. If you need support with FICA RMCP drafting, specialised compliance practices can provide templates and guidance tailored to your business model whilst ensuring regulatory alignment.
Building a Sustainable AML Compliance Culture
The most effective aml audit identifies not just technical compliance gaps but also cultural weaknesses that allow non-compliance to persist. South African FSPs with strong compliance cultures share common characteristics that audits should evaluate.
Leadership Tone and Commitment
Compliance culture begins at the top. Key individuals and senior management must demonstrate genuine commitment to AML compliance through words and actions. Observable indicators include:
- Regular compliance discussion in management meetings and business planning
- Appropriate resource allocation to compliance functions
- Willingness to forego business opportunities that present unacceptable AML risks
- Public support for compliance officer decisions, even when commercially inconvenient
- Personal participation in compliance training and programme development
Your aml audit should assess whether leadership commitment exists beyond policy statements-do business incentives reward compliant behaviour or create pressure to cut corners?
Advisor Accountability and Empowerment
Individual advisors bear front-line responsibility for client onboarding, monitoring, and red flag identification. Effective compliance cultures balance accountability with empowerment. Audit procedures should evaluate:
- Clear expectations: Job descriptions, performance objectives, and compliance policies clearly define AML responsibilities
- Consequences: Non-compliance receives appropriate response, from coaching for minor issues to disciplinary action for serious breaches
- Support mechanisms: Advisors can easily access compliance guidance, escalate concerns without fear, and obtain timely answers to questions
- Recognition: Compliant behaviour receives positive acknowledgement alongside business performance
Independent brokers working alone or in small teams face particular challenges building accountability structures. External peer networks, compliance forums, and industry associations can provide informal oversight and professional pressure that reinforces compliance commitment.
Continuous Improvement Mindset
Compliance is not static-regulations evolve, business models change, and money laundering techniques adapt. The strongest compliance cultures treat the aml audit as a learning opportunity rather than a threat. Observable behaviours include:
- Welcoming audit findings as improvement opportunities rather than defending current practices
- Implementing not just required remediation but also recommended enhancements
- Conducting root cause analysis to understand why issues occurred
- Sharing lessons learned across the advisor team
- Proactively monitoring regulatory developments and adjusting procedures accordingly
Embedding continuous improvement requires discipline and resources that small practices often struggle to prioritise. Setting quarterly compliance review sessions-even brief ones-creates structured improvement opportunities between formal audits.
Preparing for Regulatory Inspections and Supervisory Engagement
A well-executed aml audit not only strengthens your internal controls but also positions you favourably for regulatory inspections by the FSCA or FIC. Understanding how supervisors evaluate AML compliance helps you prepare effectively.
What Regulators Look for During Inspections
South African financial sector regulators conduct both thematic reviews (examining specific issues across multiple firms) and firm-specific inspections. When evaluating AML compliance, supervisors typically focus on:
- Governance and oversight: Does senior management understand AML risks? Does the compliance officer have appropriate authority and resources?
- Risk assessment quality: Is the business-wide and client-level risk assessment comprehensive, documented, and regularly updated?
- Control implementation: Do policies and procedures translate into actual practice? Is there evidence of consistent application?
- Testing and audit: Has independent testing occurred? Were findings remediated appropriately?
- Suspicious activity reporting: Are advisors identifying and reporting suspicious transactions? Is the quality of STRs adequate?
The OCC’s Bank Supervision Process guidance provides detailed insight into how banking supervisors evaluate AML programmes, offering South African FSPs a template for self-assessment before regulatory visits.
Leveraging Your AML Audit During Inspections
A comprehensive, recent aml audit demonstrates regulatory seriousness and provides a roadmap for inspector discussions. When regulators arrive, you should:
- Proactively share audit reports: Providing your most recent audit report and remediation tracking demonstrates transparency and commitment
- Discuss remediation progress: Be prepared to explain how you've addressed findings, including any delayed or incomplete remediation with clear reasons
- Highlight improvements: Point to control enhancements implemented following audit recommendations
- Acknowledge gaps candidly: If audits identified issues you're still addressing, explain timelines and resource constraints honestly rather than minimising concerns
Inspectors distinguish between firms that conduct audits as compliance theatre versus those using audits for genuine improvement. Demonstrating the latter significantly influences regulatory perception.
Managing Inspection Findings
If regulatory inspections identify AML deficiencies despite your audit efforts, respond strategically:
- Understand precisely what regulators found: Request detailed explanations of concerns, including specific examples and regulatory expectations
- Compare against your audit scope: Did your audit miss the issue due to scope limitations, or did remediation fail? This distinction affects your response
- Develop comprehensive remediation: Address not just the specific finding but underlying root causes and similar scenarios
- Enhance future audit procedures: Update audit programmes to specifically test areas where regulatory concerns emerged
- Consider external validation: For serious findings, engaging external AML specialists to validate your remediation may provide additional assurance
Regulatory enforcement in South Africa has intensified significantly. Fines, licence restrictions, and debarment orders for AML failures have affected brokers and FSPs of all sizes. Treating inspections seriously and implementing robust responses protects both your business and professional standing.
Practical Checklist: Conducting Your AML Audit
This practical checklist provides a structured approach to planning and executing an aml audit for South African FSPs, adaptable to businesses of different scales and complexity.
Pre-Audit Planning (4-6 Weeks Before)
Define audit scope and objectives:
- Determine audit period (typically 12-24 months of activity)
- Identify business areas, products, and advisors within scope
- Set specific testing objectives aligned with FICA requirements and business risks
- Document any scope limitations and justifications
Secure auditor independence:
- If using external auditor, verify their AML expertise and South African regulatory knowledge
- If using internal resources, ensure the auditor has no responsibility for day-to-day compliance
- Obtain management commitment to provide access and address findings
Gather preliminary information:
- Client onboarding volume by period, advisor, and risk category
- Compliance officer reports and management information
- Previous audit reports and remediation status
- RMCP, policies, and procedure documentation
- Training records and materials
- FIC reporting statistics (STRs/UTRs filed)
Documentation and Control Testing (2-4 Weeks)
Customer due diligence testing:
- Select representative client sample (suggest minimum 25-30 files, stratified by risk)
- Review each file against CDD checklist covering identification, verification, beneficial ownership, risk assessment, POPIA compliance
- Document findings with specific file references and deficiency descriptions
- Test whether enhanced due diligence was applied appropriately to high-risk clients
Ongoing monitoring evaluation:
- Review periodic client file reviews for completeness and timeliness
- Test transaction monitoring for sample of client relationships
- Verify that client changes (address, beneficial ownership, activity patterns) triggered appropriate updates
- Assess whether risk ratings are reviewed and updated appropriately
Suspicious activity procedures:
- Interview advisors regarding red flag awareness and escalation procedures
- Review all STRs/UTRs filed during audit period for completeness and timeliness
- Examine internal investigations of escalated concerns (even those not resulting in FIC reports)
- Test whether training adequately covered suspicious activity identification
Record-keeping and governance:
- Verify record retention policies and actual retention practices
- Test data security and POPIA compliance in record management
- Review compliance officer reporting to management/board
- Assess training delivery, attendance, and effectiveness
- Evaluate compliance resource adequacy
Reporting and Remediation (2-3 Weeks)
Draft audit report including:
- Executive summary of key findings and overall assessment
- Detailed findings by compliance area with severity ratings
- Specific examples supporting each finding
- Root cause analysis where patterns emerge
- Recommendations for remediation with suggested timelines
- Positive observations and effective controls identified
Management response:
- Share draft report with compliance officer and management for factual accuracy review
- Conduct closing meeting to discuss findings and recommendations
- Obtain management action plan for each finding, including responsible persons and target dates
- Finalise report incorporating management responses
Implement remediation tracking:
- Create remediation tracker with all findings, actions, owners, and deadlines
- Schedule regular progress reviews (monthly for critical/high findings)
- Escalate delayed remediation appropriately
- Document completed remediation with evidence of implementation
- Plan validation testing in next audit cycle
A robust aml audit forms the cornerstone of sustainable FICA compliance, protecting your FSP from regulatory penalties whilst demonstrating professional commitment to anti-money laundering standards. At Holistic Compliance Management Solutions (Pty) Ltd, we provide independent compliance monitoring and audit services tailored specifically to South African financial advisors and brokers, helping you identify gaps, implement practical remediation, and build confidence in your compliance programme. Our team combines deep regulatory knowledge with practical understanding of broker workflows, delivering audit services that strengthen your practice without disrupting client service. Schedule FICA training and audit consultation with our specialists to ensure your compliance programme meets 2026 regulatory expectations and positions your business for long-term success.
Who this is for: Independent financial brokers, FSP compliance officers, FAIS-regulated advisors, and practices preparing for regulatory inspections.
What's included in our FICA audit and training consultation:
- Comprehensive AML audit tailored to your business model and risk profile
- Detailed findings report with practical, prioritised remediation recommendations
- FICA and POPIA compliance training for your advisor team
- Ongoing compliance monitoring support and regulatory update guidance