PCI Consultant: Navigating Payment Security Compliance in SA
Payment card security has become a critical pillar of risk management for any organisation processing, storing, or transmitting cardholder data. Whether you operate as a merchant, payment service provider, or financial services intermediary in South Africa, the Payment Card Industry Data Security Standard (PCI DSS) sets the benchmark for protecting sensitive payment information. Navigating this complex regulatory landscape often requires specialist expertise, and that is where a pci consultant becomes indispensable. These professionals guide businesses through compliance requirements, remediation strategies, and ongoing security governance, ensuring that payment environments remain resilient against evolving threats whilst meeting the obligations imposed by card brands and acquiring banks.
Understanding the Role of a PCI Consultant
A pci consultant serves as a trusted advisor who translates the technical and procedural requirements of the PCI Data Security Standard into actionable compliance roadmaps. Their responsibilities extend far beyond simple tick-box exercises. Instead, they work alongside internal teams to assess current security postures, identify gaps, design remediation plans, and validate controls through rigorous testing and documentation.
Core Responsibilities and Deliverables
The scope of work for a pci consultant typically encompasses several key areas:
- Gap analysis: Conducting a thorough review of existing systems, processes, and policies against the twelve PCI DSS requirements to identify areas of non-compliance.
- Risk assessment: Evaluating vulnerabilities within the cardholder data environment (CDE) and prioritising remediation efforts based on risk exposure.
- Remediation planning: Developing step-by-step action plans that outline technical controls, policy updates, and process changes needed to achieve compliance.
- Validation and attestation: For organisations requiring formal validation, qualified assessors perform evidence collection, testing, and issuance of Reports on Compliance (RoC) or Attestations of Compliance (AoC).
- Ongoing advisory: Providing continuous guidance on emerging threats, standard updates, and best practices to maintain compliance beyond initial certification.
When you engage a pci consultant, you gain access to deep domain knowledge that extends across network security, application security, access control, cryptography, and incident response. This breadth of expertise is essential because PCI DSS encompasses controls across the entire technology stack and organisational processes.
Qualified Security Assessors vs. Boutique Advisors
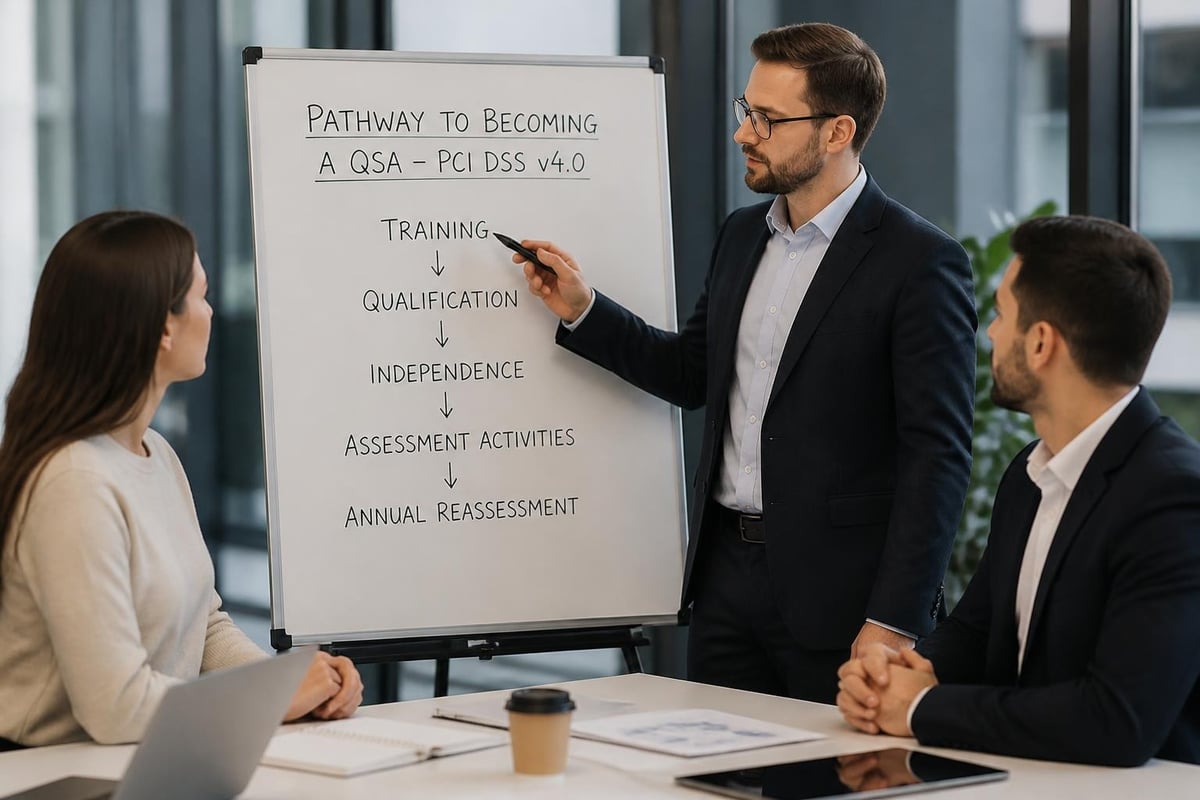
Not all consultants operate under the same credentials or business models. The official PCI DSS standards recognise Qualified Security Assessors (QSAs) as formally trained and certified professionals authorised to conduct validation assessments and issue compliance reports. QSA companies must meet stringent qualification requirements, including annual reassessments, professional indemnity insurance, and adherence to independence standards.
Boutique consultants, on the other hand, may not hold QSA credentials but bring valuable expertise in scoping, remediation, and pre-assessment readiness. A recent comparison of QSA firms versus boutique consultants highlights the trade-offs: large QSA firms offer comprehensive validation services and global reach, whilst boutique advisors often provide more personalised support, flexible pricing, and deep integration with internal teams during remediation phases.
How PCI Compliance Intersects with South African Regulatory Frameworks
For financial services providers and intermediaries operating in South Africa, payment security does not exist in isolation. The regulatory environment weaves together PCI DSS obligations with local statutes governing data protection, financial conduct, and anti-money laundering. Understanding these intersections is critical for building a holistic compliance programme.
POPIA and Cardholder Data Protection
The Protection of Personal Information Act (POPIA) establishes comprehensive data protection obligations for all organisations processing personal information within South Africa. Payment card details, including cardholder names, card numbers, expiry dates, and CVV codes, constitute personal information under POPIA's definition. Consequently, organisations subject to PCI DSS must also ensure their cardholder data handling practices align with POPIA's eight conditions for lawful processing.
A pci consultant with South African market knowledge can help bridge these frameworks by ensuring that:
- Consent mechanisms for payment processing meet POPIA's requirements for voluntary, specific, and informed consent.
- Data subject rights (access, correction, deletion) are supported within payment systems without compromising PCI DSS security controls.
- Cross-border data flows for payment processing comply with both PCI DSS encryption requirements and POPIA's transborder flow restrictions.
- Breach notification procedures satisfy both PCI DSS incident response timelines and POPIA's 72-hour reporting obligation to the Information Regulator.
| Requirement Area | PCI DSS Focus | POPIA Focus | Integration Point |
|---|---|---|---|
| Encryption | Protect cardholder data in transit and at rest | Secure personal information appropriately | Both require strong cryptographic controls |
| Access Control | Restrict access to CDE on need-to-know basis | Process only necessary personal information | Principle of minimality aligns with least privilege |
| Breach Response | Notify card brands and acquirers immediately | Notify Information Regulator within 72 hours | Unified incident management process |
| Retention | Limit retention to business justification | Retain only as long as necessary | Coordinated data retention policies |
FICA, COFI, and Payment Processing Workflows
Independent financial advisors and brokers regulated under the Financial Advisory and Intermediary Services (FAIS) Act frequently process client payments for premiums, investments, and advisory fees. When these payments involve card transactions, the cardholder data environment extends into the broker's operational systems.
The Financial Intelligence Centre Act (FICA) imposes customer due diligence and record-keeping obligations that intersect with payment workflows. A pci consultant familiar with financial services can help ensure that:
- Client verification documents stored for FICA purposes are segregated from payment card data to minimise the scope of the cardholder data environment.
- Payment transaction logs required for audit trails under the Conduct of Financial Institutions (COFI) framework are maintained securely without exposing sensitive authentication data.
- Third-party payment processors used by brokers are themselves PCI DSS compliant, with appropriate service provider agreements and annual attestations.
For brokers implementing FICA RMCP (Risk Management and Compliance Programmes), integrating payment security controls into the broader risk framework ensures a unified approach to operational resilience. The RMCP should explicitly address payment processing risks, including card data exposure, transaction fraud, and processor service failures.
FAIS Compliance and Payment Security Governance
Financial Service Providers (FSPs) licensed under FAIS must demonstrate adequate risk management and operational controls to the Financial Sector Conduct Authority (FSCA). Payment security forms part of this broader governance obligation. A pci consultant can assist FSPs in:
- Scoping the cardholder data environment to determine which systems, networks, and personnel fall within PCI DSS scope.
- Implementing network segmentation to isolate payment systems from general business networks, reducing compliance complexity and costs.
- Establishing policy frameworks that integrate PCI DSS requirements into existing compliance management systems, including key individual (KI) oversight and board reporting.
- Training staff on secure payment handling, social engineering awareness, and incident reporting procedures aligned with FAIS fit-and-proper requirements.
Selecting the Right PCI Consultant for Your Organisation
Choosing a pci consultant requires careful evaluation of credentials, industry experience, and alignment with your organisation's specific needs. The wrong choice can lead to wasted resources, incomplete remediation, and ongoing compliance failures.
Essential Credentials and Qualifications
When evaluating potential consultants, prioritise those with recognised credentials and demonstrable expertise:
- QSA certification: If you require formal validation, ensure the consultant holds current QSA status through the PCI Security Standards Council. The QSA qualification requirements mandate rigorous training, annual reassessment, and adherence to independence standards.
- Industry certifications: Look for complementary credentials such as Certified Information Systems Security Professional (CISSP), Certified Information Security Manager (CISM), or Certified Ethical Hacker (CEH) that demonstrate broader security expertise.
- Sector experience: Consultants with background in financial services understand the regulatory intersections with POPIA, FICA, and FAIS, making them more effective advisors for FSPs and brokers.
- Local market knowledge: South African organisations benefit from consultants familiar with domestic payment ecosystems, regional acquiring banks, and local regulatory expectations.
Key Questions During the Selection Process
A comprehensive guide to choosing a PCI consultant suggests several critical questions to ask during vendor evaluation:
- What is your experience with organisations of similar size, industry, and technology stack?
- Can you provide references from clients who have achieved and maintained compliance through your services?
- How do you approach scoping exercises, and what methodologies do you use to minimise compliance burden?
- What is your incident response capability if a breach occurs during the engagement?
- How do you stay current with PCI DSS updates, emerging threats, and evolving best practices?
- What is your pricing model, and what deliverables are included at each stage?
Understanding Consultant Independence and Conflicts of Interest
The PCI Security Standards Council imposes strict independence requirements on QSAs to ensure objectivity in assessments. Specifically, QSA employees cannot design or implement security controls and then subsequently assess those same controls for compliance. This separation of duties prevents conflicts of interest that could compromise assessment integrity.
When engaging a pci consultant, clarify whether they will provide both remediation services and validation. If so, different team members must perform these functions, with appropriate firewalls between advisory and assessment activities. The PCI SSC’s conflict of interest FAQ provides detailed guidance on these boundaries.
Practical Steps for Working Effectively with a PCI Consultant
Engaging a pci consultant represents a significant investment of time and resources. Maximising the value of this relationship requires active participation from internal stakeholders and a structured approach to the compliance journey.
Pre-Engagement Preparation
Before formal engagement begins, organisations should complete several preparatory steps:
- Document current payment flows: Map all processes involving payment card data, from initial capture through processing, storage, and disposal.
- Inventory relevant systems: Create a comprehensive list of all systems, applications, databases, and network devices that may interact with cardholder data.
- Identify stakeholders: Determine which internal teams (IT, operations, compliance, finance, legal) will participate in the compliance programme and assign clear roles.
- Review existing policies: Gather current security policies, access control procedures, incident response plans, and vendor management frameworks.
This preparation accelerates the consultant's scoping exercise and ensures that initial assessments are based on complete and accurate information.
The Compliance Implementation Workflow
A typical pci consultant engagement follows a structured workflow that balances thoroughness with practical implementation:
| Phase | Duration | Key Activities | Deliverables |
|---|---|---|---|
| Scoping & Discovery | 2-4 weeks | Network diagrams, data flow mapping, system inventory, stakeholder interviews | Scoping document, preliminary gap analysis |
| Detailed Assessment | 4-8 weeks | Control testing, vulnerability scanning, policy review, configuration analysis | Comprehensive gap report with prioritised remediation roadmap |
| Remediation Support | 12-24 weeks | Technical implementation guidance, policy development, training delivery | Updated controls, documented procedures, staff awareness |
| Validation | 4-6 weeks | Evidence collection, penetration testing, final control verification | Report on Compliance (RoC) or Attestation of Compliance (AoC) |
| Ongoing Maintenance | Continuous | Quarterly scanning, annual reassessment, standard update guidance | Quarterly scan reports, annual validation |
The timeline varies significantly based on organisation size, environment complexity, and initial compliance posture. Organisations with mature security programmes may complete initial validation in six months, whilst those with substantial gaps may require eighteen months or more.
Self-Assessment vs. Professional Validation
Smaller merchants and service providers may qualify for self-assessment through completion of a Self-Assessment Questionnaire (SAQ) rather than formal QSA validation. An analysis of SAQ completion versus QSA engagement highlights several considerations:
- Complexity tolerance: SAQs require significant internal expertise to complete accurately; professional guidance reduces the risk of errors or omissions.
- Attestation requirements: Some acquiring banks or card brands mandate QSA validation regardless of merchant tier; verify your specific obligations before choosing self-assessment.
- Risk appetite: Professional validation provides greater assurance to stakeholders (boards, customers, regulators) that controls are genuinely effective.
- Resource availability: Self-assessment demands substantial internal time; consultant engagement may prove more cost-effective when factoring opportunity costs.
Even organisations pursuing self-assessment often benefit from consultant support during initial gap analysis and remediation phases, reserving formal QSA validation for annual attestation requirements.
Advanced Topics in PCI Consultancy
Beyond foundational compliance, experienced pci consultant professionals address sophisticated challenges that arise in complex technology environments and evolving threat landscapes.
Cloud and Hybrid Environment Compliance
The migration of payment systems to cloud platforms introduces unique compliance considerations. A pci consultant must understand shared responsibility models, where cloud providers secure the underlying infrastructure whilst customers remain responsible for application-layer controls, data encryption, and access management.
Key considerations include:
- Tokenisation and encryption: Implementing point-to-point encryption (P2PE) or tokenisation to reduce cloud environment scope by ensuring cardholder data never reaches cloud systems in clear text.
- Container security: Securing containerised payment applications through image scanning, runtime monitoring, and orchestration platform hardening.
- Multi-tenancy risks: Ensuring adequate logical separation when payment workloads share cloud infrastructure with other applications.
- Audit evidence collection: Navigating cloud provider audit reports (SOC 2, ISO 27001) to satisfy PCI DSS evidence requirements whilst maintaining ultimate responsibility for compliance.
The PCI SSC’s guidance on relying on other audit evidence clarifies that whilst QSAs may reference third-party audit reports, they retain ultimate responsibility for validating that controls meet PCI DSS requirements in the specific implementation context.
Remote Assessment Considerations
The shift toward remote work and distributed teams has raised questions about onsite assessment requirements. The PCI SSC’s FAQ on onsite QSA requirements confirms that whilst some assessment activities can be conducted remotely, certain procedures (such as physical security inspection and sensitive authentication data verification) may require physical presence.
A pci consultant should clearly communicate which activities demand onsite visits and which can be completed remotely, allowing organisations to plan accordingly and manage costs effectively.
PCI DSS Version 4.0 Transition
The payment card industry released PCI DSS version 4.0 in 2022, with full enforcement beginning in 2025. Version 4.0 introduces significant changes, including:
- Customised implementation: Organisations may now define alternative controls that meet security objectives through documented risk analysis, providing greater flexibility for innovative technologies.
- Enhanced authentication requirements: Multi-factor authentication extends to all access into the cardholder data environment, not just remote access.
- Expanded logging and monitoring: More comprehensive audit trail requirements, including automated detection of anomalous behaviour.
- Role-based access control: Stricter segregation of duties and least-privilege enforcement across systems and applications.
A knowledgeable pci consultant helps organisations navigate this transition, identifying which new requirements apply immediately and which have extended compliance deadlines, whilst developing roadmaps that align security investments with business priorities.
Building a Sustainable Compliance Programme
Achieving initial PCI DSS compliance represents only the beginning of an ongoing commitment to payment security. A pci consultant's greatest value often lies in helping organisations build sustainable programmes that maintain compliance whilst adapting to business growth, technology evolution, and emerging threats.
Continuous Monitoring and Quarterly Requirements
PCI DSS mandates quarterly vulnerability scanning by Approved Scanning Vendors (ASVs) for all external-facing systems within the cardholder data environment. Additionally, organisations must conduct quarterly internal vulnerability scans and address high-risk findings within defined timeframes.
A sustainable compliance programme integrates these requirements into regular operational rhythms:
- Automated scanning workflows: Schedule scans to run automatically each quarter, with results routed to designated security personnel for review.
- Remediation tracking: Implement ticketing systems that track vulnerabilities from discovery through remediation and verification.
- Exception management: Establish formal processes for documenting risk acceptance when immediate remediation is not feasible.
- Trend analysis: Monitor vulnerability trends over time to identify systemic weaknesses requiring architectural or process improvements.
Staff Training and Awareness
Payment security depends ultimately on people making sound decisions under pressure. Regular training ensures that employees understand their responsibilities and can recognise social engineering attempts, phishing campaigns, and other threats targeting payment systems.
Effective training programmes include:
- Role-specific content: Tailor training to different job functions, with developers receiving secure coding guidance, support staff learning secure authentication procedures, and executives understanding governance obligations.
- Realistic scenarios: Use case studies drawn from actual breach incidents to illustrate consequences and reinforce best practices.
- Regular refreshers: Conduct annual training for all personnel with access to cardholder data, supplemented by quarterly awareness campaigns.
- Assessment and certification: Require personnel to demonstrate competency through testing, with results documented for audit purposes.
Policy Lifecycle Management
PCI DSS requires comprehensive documentation of security policies, procedures, and standards. A pci consultant can help establish a policy framework that satisfies compliance requirements whilst remaining practical and usable.
- Policy hierarchy: Establish clear relationships between high-level policies (board-approved security strategy), standards (specific technical requirements), and procedures (step-by-step implementation guides).
- Annual review cycle: Schedule formal policy reviews at least annually, with triggers for interim updates when significant business or technology changes occur.
- Version control: Maintain policy version histories, approval records, and distribution lists to demonstrate governance maturity during assessments.
- Exception processes: Define how policy exceptions are requested, evaluated, approved, and monitored to prevent informal workarounds that create compliance gaps.
Cost Considerations and ROI Analysis
Engaging a pci consultant represents a significant investment, particularly for smaller organisations or independent brokers. Understanding the cost drivers and potential return on investment helps justify the expenditure to stakeholders.
Typical Consultant Fee Structures
PCI consultant pricing varies based on several factors:
- Organisation size and complexity: Larger environments with multiple locations, diverse technology stacks, and high transaction volumes require more extensive assessment efforts.
- Assessment type: Full QSA validations cost substantially more than gap analyses or remediation support engagements.
- Geographic factors: South African consultants may charge differently than international firms, with exchange rates and travel requirements affecting total costs.
- Engagement model: Some consultants charge fixed project fees, whilst others bill hourly or offer retainer arrangements for ongoing support.
| Service Type | Typical Cost Range (ZAR) | Scope |
|---|---|---|
| Initial Gap Analysis | 45,000 – 120,000 | Scoping, preliminary assessment, prioritised remediation roadmap |
| Remediation Support (6 months) | 180,000 – 450,000 | Technical guidance, policy development, pre-assessment testing |
| QSA Validation (Level 2-3 merchant) | 200,000 – 500,000 | Full assessment, evidence collection, RoC issuance |
| Annual Maintenance Support | 90,000 – 240,000 | Quarterly scanning, policy updates, annual reassessment |
Quantifying the Value Proposition
Beyond avoiding non-compliance penalties, PCI consultant engagements deliver measurable value:
- Breach cost avoidance: The average cost of a payment card breach in South Africa exceeds R12 million when factoring forensic investigations, notification costs, regulatory fines, card brand penalties, and reputational damage. Preventing a single breach justifies years of compliance investment.
- Operational efficiency: Network segmentation and scope reduction strategies recommended by consultants often decrease ongoing compliance costs by 30-50% in subsequent years.
- Customer trust: Demonstrable payment security strengthens client relationships, particularly for FSPs where trust forms the foundation of advisor-client relationships.
- Regulatory alignment: Payment security controls often satisfy multiple regulatory requirements (POPIA, FSCA expectations), creating compliance synergies.
Emerging Trends Shaping PCI Consultancy in 2026
The payment security landscape continues evolving rapidly, with new technologies, threat vectors, and regulatory expectations reshaping how pci consultant professionals approach their work.
Artificial Intelligence in Threat Detection
Machine learning algorithms now power advanced threat detection capabilities within payment environments, identifying anomalous transaction patterns, unusual access behaviours, and potential compromise indicators that traditional rule-based systems miss. Consultants increasingly help organisations:
- Implement behavioural analytics: Deploy user and entity behaviour analytics (UEBA) solutions that baseline normal activity and flag deviations warranting investigation.
- Automate incident response: Configure security orchestration platforms that automatically contain threats, preserve forensic evidence, and initiate notification procedures.
- Enhance fraud detection: Integrate AI-driven fraud scoring into transaction workflows, balancing security with customer experience.
Open Banking and API Security
The gradual adoption of open banking principles in South Africa creates new payment flows involving third-party providers accessing customer account data through APIs. A pci consultant must now address:
- API gateway security, including authentication, authorisation, rate limiting, and input validation.
- Token-based payment initiation that bypasses traditional card networks whilst maintaining equivalent security controls.
- Consent management frameworks ensuring customers understand and control third-party access to payment capabilities.
Quantum-Resistant Cryptography
As quantum computing advances toward practical realisation, current cryptographic algorithms protecting cardholder data face potential vulnerability. Forward-thinking consultants help organisations prepare for this transition by:
- Inventorying cryptographic implementations to understand quantum exposure.
- Planning migrations to post-quantum cryptographic algorithms as standards mature.
- Implementing crypto-agility architectures that allow algorithm updates without wholesale system redesigns.
Navigating PCI DSS compliance demands specialist expertise that bridges technical security, regulatory requirements, and practical business operations. Whether you operate as an independent financial advisor, licensed FSP, or payment service provider in South Africa, the intersection of payment security with POPIA, FICA, and FAIS obligations requires careful coordination and ongoing vigilance. Holistic Compliance Management Solutions (Pty) Ltd brings deep experience helping financial services providers build integrated compliance programmes that address these interconnected requirements whilst supporting sustainable business growth. Our team understands the unique challenges facing South African brokers and advisors, delivering practical guidance that translates complex standards into actionable controls. Visit Holistic Compliance Management Solutions (Pty) Ltd to schedule a compliance consultation and explore how our services can strengthen your risk management framework whilst supporting your practice's ongoing success in an increasingly regulated environment.
Schedule FICA Training
Who this is for: Independent financial brokers, FSP compliance officers, and regulated advisors requiring comprehensive customer due diligence and risk management capabilities.
Our FICA training programme includes:
- Practical RMCP development guidance: Learn to draft Risk Management and Compliance Programmes that integrate payment security, client onboarding, and ongoing monitoring requirements into a unified framework.
- Hands-on compliance implementation workshops: Work through real broker scenarios covering client verification, record-keeping, and suspicious transaction reporting aligned with FICA, POPIA, and payment security obligations.
- Regulatory exam preparation support: Prepare for regulatory examinations with targeted training covering FICA, POPI, FAIS, and emerging COFI requirements affecting broker operations.