ServiceNow GRC for Financial Services Compliance in SA
Financial Services Providers in South Africa operate within an increasingly complex regulatory environment, where FICA, POPIA, COFI, and FAIS compliance demands create mounting pressure on independent brokers and advisory practices. Traditional compliance approaches-spreadsheets, manual tracking, and siloed processes-no longer suffice when regulatory obligations multiply and enforcement intensifies. ServiceNow GRC emerges as a comprehensive platform solution that connects governance, risk management, and compliance activities into a single, integrated system. For South African financial advisors managing client onboarding, risk assessments, and ongoing regulatory obligations, understanding how service now grc capabilities align with local compliance requirements represents a strategic advantage in building sustainable, audit-ready practices.
Understanding ServiceNow GRC Architecture for Financial Services
ServiceNow GRC operates on the Now Platform, delivering integrated risk and compliance management through interconnected modules that replace fragmented compliance tools. The platform architecture centralizes policy management, risk registers, control frameworks, audit workflows, and evidence collection into a unified database, eliminating the duplication and version control issues that plague spreadsheet-based compliance systems.
For South African FSPs, this architecture addresses several critical pain points:
- Centralized authority document repository linking FAIS notices, FSCA communications, FICA guidance notes, and POPIA regulations to specific control requirements
- Real-time compliance dashboards showing FICA verification status, POPIA processing inventory completeness, and COFI conduct assessments across client portfolios
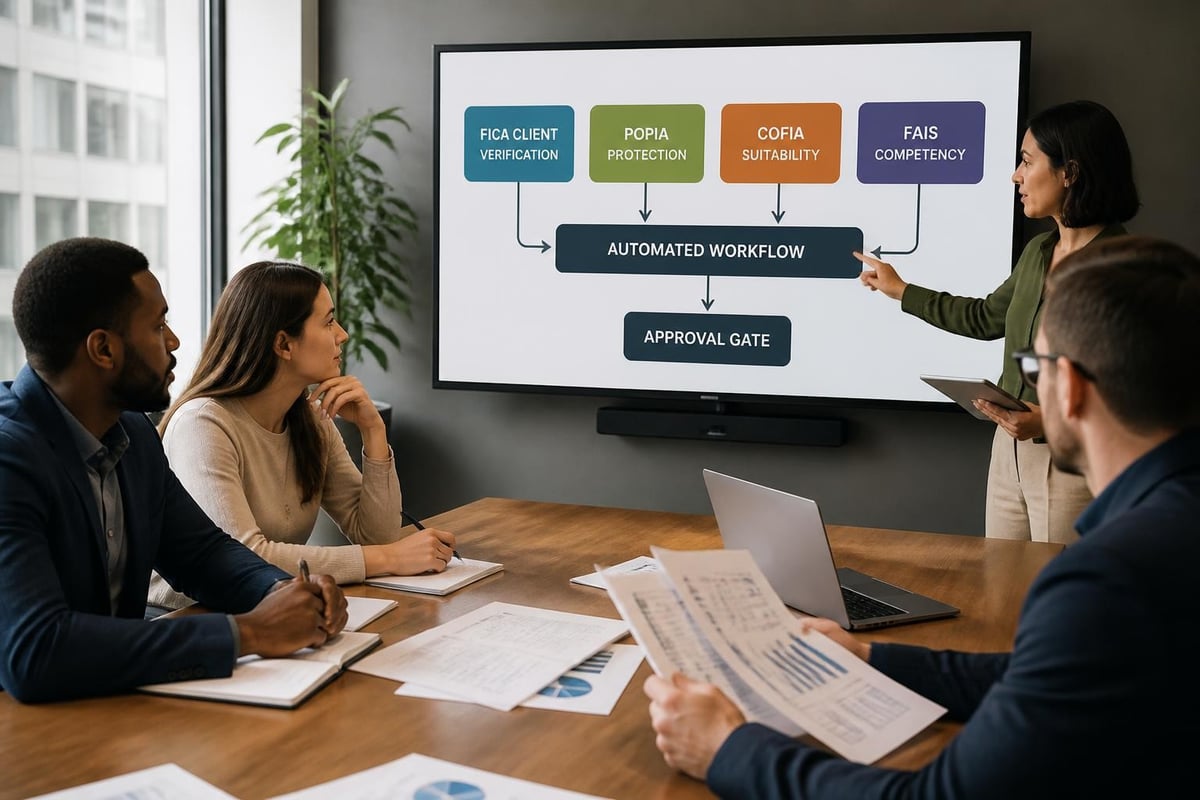
- Automated workflow routing for compliance officer reviews, principal approval chains, and remediation task assignments
- Audit-ready evidence repositories storing client due diligence records, training certificates, complaint registers, and policy attestations with full version history
The platform's database structure allows compliance officers to map regulatory obligations directly to operational controls, creating traceable connections between FSCA requirements and daily broker activities.
Integrated Risk Management Capabilities
Service now grc consolidates risk identification, assessment, treatment, and monitoring into repeatable workflows that align with enterprise risk management frameworks. Financial services practices can configure risk categories specific to their licensing categories, creating distinct risk registers for long-term insurance, short-term insurance, or investment advisory activities.
| Risk Category | ServiceNow GRC Function | Compliance Application |
|---|---|---|
| FICA non-compliance | Risk assessment templates | Client onboarding verification tracking |
| POPIA data breaches | Incident response workflows | Data subject access request management |
| COFI conduct failures | Control effectiveness monitoring | Product suitability assessment reviews |
| FAIS fit and proper lapses | Training compliance tracking | Continuous professional development records |
The platform's risk scoring algorithms calculate inherent and residual risk levels based on control effectiveness ratings, enabling practices to prioritize remediation efforts where regulatory exposure concentrates most significantly.
Policy and Compliance Management for FICA and POPIA
The Policy and Compliance Management module provides structured frameworks for translating regulatory requirements into enforceable internal policies and measurable controls. South African financial advisors face specific challenges in maintaining current policy documentation that reflects FICA amendments, POPIA enforcement guidance, and evolving FSCA expectations.
ServiceNow GRC addresses these challenges through:
Authority document management that links FICA Act 38 of 2001, POPIA Act 4 of 2013, FAIS Act 37 of 2002, and related regulations to internal policy documents. When FSCA publishes updated guidance, compliance officers update the authority document version, triggering automatic reviews of linked policies and controls.
Policy lifecycle workflows managing drafting, review, approval, publication, and attestation cycles. Independent brokers can configure approval chains requiring principal sign-off before policies become effective, creating governance evidence for FSCA inspections.
Control mapping frameworks connecting FICA customer due diligence obligations to specific verification procedures, POPIA processing principles to data handling controls, and COFI fair treatment requirements to sales process checkpoints.
Building FICA-Compliant Customer Onboarding Workflows
Service now grc enables financial services providers to design customer onboarding workflows that embed FICA verification requirements into each process stage. The platform's workflow engine can enforce sequential verification steps, preventing account activation until compliance officers confirm identity verification, residential address confirmation, and risk categorization completion.
For independent financial advisors managing their own client acquisition, this systematic approach offers several advantages:
- Standardized verification checklists ensure every client file contains identical documentation, eliminating the inconsistency that triggers FSCA findings during inspections
- Automated reminder notifications alert advisors when verification documents approach expiry dates, maintaining continuous FICA compliance across the client portfolio
- Centralized evidence storage consolidates identity documents, proof of residence, and source of funds declarations in searchable repositories with access controls
- Audit trail generation captures every verification decision, override justification, and approval timestamp, creating complete compliance histories for each client relationship
The platform's reporting capabilities generate FICA compliance dashboards showing verification completion rates, outstanding documentation requirements, and periodic review due dates across the entire client base.
Implementing POPIA Data Protection Controls
POPIA compliance requires financial services providers to implement comprehensive data protection controls spanning processing inventory management, consent documentation, data subject rights fulfillment, and breach response procedures. Service now grc provides specialized modules addressing each POPIA obligation area through integrated workflows that connect data discovery, control implementation, and compliance monitoring.
Processing Inventory and Lawful Basis Documentation
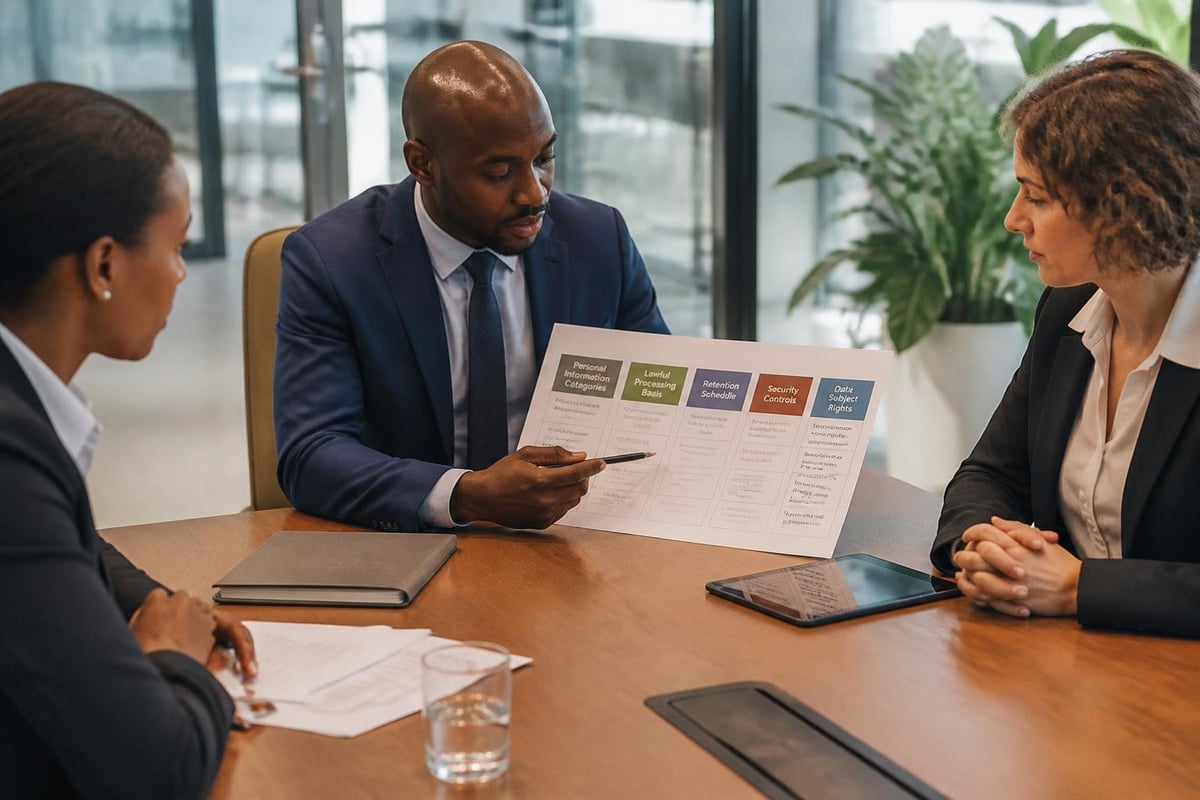
The platform's data protection module enables compliance officers to build complete processing inventories documenting every personal information category collected, processing purpose, lawful basis, retention period, and security control. For financial advisors handling sensitive client information including financial records, health status for risk underwriting, and identity documents for FICA verification, this structured inventory approach satisfies POPIA Section 18 accountability requirements.
ServiceNow GRC supports processing inventory maintenance through:
- Template-driven data discovery guiding compliance officers through systematic identification of processing activities across client onboarding, policy servicing, claims handling, and marketing functions
- Lawful basis assignment linking each processing activity to specific POPIA conditions (consent, contractual necessity, legal obligation, legitimate interest)
- Automated data flow mapping documenting information sharing with underwriters, reinsurers, claims administrators, and marketing service providers
- Retention schedule enforcement triggering deletion workflows when policy-defined retention periods expire
The platform's configuration flexibility allows practices to customize processing categories reflecting their specific product portfolios and operational models, whether focusing on long-term insurance, retirement annuities, or investment management services.
Data Subject Rights Request Management
POPIA grants data subjects specific rights including access requests, correction demands, deletion requests, and objections to processing. Service now grc provides case management workflows that standardize how financial advisors receive, verify, process, and respond to these requests within statutory timeframes.
The platform's request management capabilities include:
| Request Type | Workflow Stage | ServiceNow GRC Function |
|---|---|---|
| Access request | Verification | Identity confirmation against FICA records |
| Access request | Compilation | Automated retrieval from client database, policy systems, correspondence archives |
| Access request | Review | Compliance officer assessment for third-party confidential information |
| Access request | Delivery | Secure transmission with access logging |
| Deletion request | Impact assessment | Identification of legal retention obligations (FICA, tax, claims) |
| Deletion request | Execution | Systematic deletion with evidence capture |
This structured approach ensures advisors meet POPIA Section 23 response obligations whilst maintaining appropriate records for regulatory compliance and litigation defense.
Audit Management and Evidence Collection
Financial services providers face regular audits from FSCA inspectors, compliance officers, and external auditors examining FICA adherence, POPIA implementation, FAIS fit and proper requirements, and COFI conduct standards. Service now grc transforms audit readiness from periodic panic exercises into continuous evidence collection processes embedded within operational workflows.
Building Continuous Compliance Evidence Repositories
The platform's evidence management module automatically captures compliance artifacts throughout normal business processes, creating audit-ready documentation without additional manual effort. When advisors complete FICA verifications, POPIA impact assessments, or COFI suitability analyses, service now grc stores the supporting documents, decision rationales, and approval records in centralized repositories linked to specific control requirements.
This continuous evidence collection approach delivers several audit preparation advantages:
- Instant retrieval capabilities allowing compliance officers to produce requested documentation within minutes rather than days of document hunting
- Complete audit trails showing who performed each compliance activity, when decisions occurred, and what information supported conclusions
- Gap identification highlighting missing evidence before auditors discover deficiencies, enabling proactive remediation
- Trend analysis revealing patterns in compliance exceptions, training needs, or process weaknesses requiring management attention
For independent brokers without dedicated compliance departments, these automated evidence collection capabilities reduce the administrative burden of audit preparation whilst improving documentation quality.
Internal Audit Planning and Execution
Service now grc includes dedicated audit management modules supporting risk-based audit planning, fieldwork execution, finding documentation, and remediation tracking. Compliance officers can design audit programs testing FICA verification consistency, POPIA consent documentation adequacy, or COFI product suitability assessment rigor across representative client samples.
The audit workflow functionality guides auditors through:
- Scope definition specifying which controls, processes, or departments face examination based on risk assessments and regulatory focus areas
- Evidence request issuance automatically notifying process owners about required documentation and interview scheduling
- Testing execution recording sample selections, test procedures performed, and results observed with supporting evidence attachments
- Finding documentation categorizing deficiencies by severity, linking to specific control failures, and drafting management action plans
- Remediation tracking monitoring corrective action completion, verifying implementation effectiveness, and closing findings upon validation
This systematic audit approach helps practices demonstrate proactive compliance management to FSCA inspectors, potentially mitigating enforcement actions when isolated deficiencies emerge.
Integration Capabilities for Financial Services Systems
Service now grc operates most effectively when integrated with core financial services systems including policy administration platforms, customer relationship management databases, and document management repositories. The platform's integration capabilities enable compliance workflows to access client information, policy details, and transaction histories without requiring duplicate data entry or manual information transfers.
API-Based Integration Architecture
The Now Platform provides RESTful APIs and pre-built connectors supporting integration with common financial services applications. South African FSPs using local policy administration systems can develop custom integrations that synchronize client data, policy information, and compliance statuses between operational systems and the service now grc environment.
These integrations deliver practical workflow improvements:
- Automated FICA verification status updates flowing from compliance systems to policy administration platforms, preventing policy issuance until verification completion
- POPIA consent preferences synchronization ensuring marketing systems respect client communication preferences documented during onboarding
- COFI suitability assessment results populating client records with product appropriateness determinations supporting advice justification
- Training compliance synchronization connecting learning management systems to competency tracking modules, maintaining current fit and proper evidence
The platform's integration flexibility accommodates various technical architectures, from simple scheduled data imports to real-time bidirectional synchronization depending on business requirements and IT capabilities.
Risk Assessment and Treatment Workflows for FAIS Compliance
FAIS compliance requires financial services providers to implement comprehensive risk management processes addressing operational risks, compliance risks, and conduct risks that might harm clients or damage market integrity. Service now grc provides structured risk assessment methodologies and treatment tracking workflows that align with FSCA risk management expectations whilst remaining accessible to smaller independent practices.
Operational Risk Assessment for Independent Brokers
Independent financial advisors face specific operational risks including key person dependencies, technology failures, professional indemnity coverage gaps, and business continuity vulnerabilities. The platform's risk assessment templates can be customized to address these broker-specific risk scenarios, guiding compliance officers through systematic identification, analysis, and treatment planning processes.
The risk assessment workflow typically follows this sequence:
Risk identification workshops where principals and advisors brainstorm potential risk scenarios affecting client service delivery, regulatory compliance, or business viability. Service now grc captures each identified risk with detailed descriptions, potential causes, and impact categories.
Inherent risk rating assessing likelihood and consequence before considering existing controls. The platform's risk matrices can be configured to reflect FSP-appropriate scales, perhaps using FSCA likelihood definitions and impact categories relevant to client harm or regulatory breach severity.
Control identification documenting existing measures mitigating each risk. For technology failure risks, relevant controls might include backup systems, disaster recovery procedures, and vendor service level agreements. The platform links these controls to risk records, creating traceable mitigation documentation.
Residual risk calculation determining remaining exposure after considering control effectiveness. Service now grc automatically recalculates residual risk scores when control ratings change, maintaining current risk profiles without manual spreadsheet updates.
Treatment planning for risks exceeding appetite thresholds. The workflow generates treatment tasks assigned to responsible individuals with due dates, budgets, and progress tracking, ensuring risk mitigation plans translate into completed actions rather than forgotten intentions.
Conduct Risk Management Under COFI
The Conduct of Financial Institutions Act introduces explicit conduct risk management obligations requiring financial services providers to identify, assess, and mitigate risks of unfair client treatment throughout product design, marketing, sales, and servicing processes. Service now grc adapts to COFI requirements through configurable conduct risk assessment templates addressing product suitability, disclosure adequacy, claims handling fairness, and complaint resolution effectiveness.
For independent advisors, conduct risk assessments focus on:
- Product recommendation processes evaluating whether needs analysis procedures adequately identify client circumstances, financial objectives, and risk tolerance before product selection
- Disclosure documentation assessing whether clients receive comprehensible information about product features, costs, limitations, and risks in formats supporting informed decisions
- Ongoing suitability reviews examining whether advisors proactively contact clients when circumstances change or product performance deviates from expectations
- Complaint handling procedures determining whether grievance processes operate fairly, independently, and within reasonable timeframes
The platform's workflow automation can route conduct risk assessments through multi-level review processes, requiring both compliance officer evaluation and principal approval before risk acceptance decisions finalize, creating governance evidence valued during FSCA inspections.
Compliance Monitoring and Testing Programs
Effective compliance programs extend beyond policy documentation and control design into active monitoring and testing verifying that controls operate as intended throughout normal business activities. Service now grc supports comprehensive compliance monitoring programs through scheduled testing workflows, exception tracking, and corrective action management that transform compliance from reactive firefighting into proactive risk management.
Designing Risk-Based Monitoring Schedules
The platform's monitoring module enables compliance officers to design annual monitoring plans allocating testing resources toward highest-risk control areas. For South African financial advisors, risk-based monitoring prioritizes FICA verification controls, POPIA data handling procedures, and COFI product suitability assessments based on inherent risk ratings, regulatory focus, and historical deficiency patterns.
Monitoring plan components include:
| Control Area | Testing Frequency | Sample Size | Testing Procedure |
|---|---|---|---|
| FICA verification | Monthly | 10 new clients | Document completeness review against checklist |
| POPIA consent records | Quarterly | 15 marketing activities | Consent presence and specificity verification |
| COFI needs analysis | Monthly | 10 new policies | Needs analysis depth and product alignment review |
| FAIS training compliance | Annually | All representatives | CPD credits and competency exam currency check |
Service now grc generates testing tasks according to defined schedules, assigns them to designated testers, provides standardized testing templates, and tracks completion status, ensuring monitoring programs execute consistently rather than being deferred during busy periods.
Exception Management and Remediation Tracking
When compliance monitoring identifies control deficiencies, service now grc captures exceptions with detailed documentation including specific client files affected, control requirement breached, root cause analysis, and required corrective actions. The platform's remediation workflow assigns corrective tasks to responsible individuals, sets completion deadlines aligned with risk severity, and monitors progress through automated status updates.
For independent brokers, this structured exception management approach offers accountability mechanisms ensuring identified deficiencies receive timely remediation rather than languishing on to-do lists. The platform's escalation capabilities automatically notify principals when remediation deadlines approach without completion, creating oversight visibility that drives action.
Remediation tracking dashboards provide compliance officers with portfolio views showing:
- Open exceptions by risk category highlighting whether deficiencies concentrate in specific compliance areas requiring systemic intervention
- Aging analysis identifying overdue remediation tasks requiring management attention and resource reallocation
- Recurrence patterns revealing whether previously remediated issues reappear, suggesting inadequate root cause analysis or ineffective corrective actions
- Completion trends demonstrating improving compliance cultures when exception volumes decline and remediation cycles accelerate
These analytical capabilities transform compliance monitoring from periodic snapshots into continuous improvement processes driving operational excellence alongside regulatory adherence.
Implementation Considerations for South African FSPs
Deploying service now grc within financial services practices requires careful planning addressing technical infrastructure, process redesign, change management, and ongoing administration. South African FSPs contemplating platform adoption should evaluate implementation approaches ranging from phased module rollouts to comprehensive enterprise deployments based on practice size, complexity, and resource availability.
Phased Implementation Roadmap
Most successful implementations follow phased approaches prioritizing high-impact, lower-complexity modules before expanding into specialized functions. A typical roadmap for independent financial advisors might sequence implementation across three phases:
Phase 1: Policy and Compliance Foundation (Months 1-3)
- Configure authority document repository with FICA, POPIA, FAIS, and COFI regulations
- Migrate existing policies into platform with approval workflow activation
- Implement control library mapping policies to operational procedures
- Deploy attestation workflows for annual policy acknowledgment
Phase 2: Risk and Audit Management (Months 4-6)
- Build risk register with FSP-specific categories and assessment templates
- Configure risk treatment workflows with task assignment and tracking
- Design audit programs for FICA, POPIA, and COFI compliance testing
- Implement finding management and remediation tracking
Phase 3: Advanced Integration and Automation (Months 7-12)
- Develop integrations with policy administration and CRM systems
- Configure automated evidence collection from operational workflows
- Deploy compliance monitoring schedules with exception management
- Implement dashboards and reporting for management oversight
This phased approach allows practices to realize value incrementally whilst building internal expertise and refining configurations based on operational feedback before expanding platform scope.
Training and Change Management Requirements
Service now grc implementation success depends heavily on user adoption, requiring comprehensive training programs and change management initiatives addressing both technical platform skills and process understanding. Financial advisors accustomed to manual compliance tracking need structured onboarding explaining how platform workflows replace previous methods and why consistent platform usage delivers superior compliance outcomes.
Effective training programs typically include:
- Role-based training modules customized for advisors, compliance officers, and principals reflecting their distinct platform interactions and responsibilities
- Hands-on workshops using sanitized client scenarios to practice FICA verification workflows, POPIA request processing, and risk assessment completion in safe training environments
- Quick reference guides providing step-by-step instructions for common tasks like policy attestation, exception documentation, and evidence upload
- Super-user designation identifying enthusiastic early adopters who receive advanced training and provide peer support during initial rollout
Change management activities should emphasize how platform adoption reduces administrative burden, improves audit readiness, and mitigates regulatory risk rather than focusing solely on technical features. When advisors understand platform benefits translating into less stressful FSCA inspections and more efficient client service, adoption resistance typically diminishes.
Vendor Selection and Partnership Considerations
While ServiceNow provides the core platform technology, successful implementations often involve partnerships with consulting firms specializing in GRC deployments, financial services compliance, or ServiceNow configuration. South African FSPs should evaluate potential implementation partners based on relevant industry experience, local regulatory knowledge, and ongoing support capabilities beyond initial deployment.
KPMG’s ServiceNow alliance represents one partnership model combining Big Four consulting expertise with platform technical capabilities, though smaller practices might find specialized boutique consultancies more accessible and cost-effective. The selection criteria should emphasize:
Financial services experience with demonstrated understanding of FICA, POPIA, FAIS, and COFI compliance requirements specific to South African regulatory context. Implementation partners lacking this domain expertise may configure generic GRC workflows requiring extensive customization to address FSP-specific needs.
Reference implementations from comparable practices allowing evaluation of delivered solutions, implementation timelines, budget adherence, and post-deployment support quality. Speaking with reference clients reveals practical insights about partner responsiveness, problem-solving approaches, and knowledge transfer effectiveness.
Ongoing support models clarifying how regulatory updates, configuration changes, and user questions will be handled after initial implementation completes. Service now grc requires continuous administration as regulations evolve, business processes change, and user needs develop, making long-term support partnerships valuable beyond one-time deployment projects.
Training capabilities ensuring implementation partners can deliver comprehensive user training, administrator education, and knowledge transfer enabling internal teams to manage platform operations independently over time. Practices overly dependent on external consultants for routine administration face escalating costs and delayed response times.
According to industry analysis from Forrester, the GRC platform market continues maturing with increasing emphasis on integration capabilities, workflow automation, and regulatory content libraries that reduce implementation complexity. South African FSPs should leverage these platform advances whilst ensuring local regulatory requirements receive adequate attention during configuration.
Measuring Service Now GRC Value and ROI
Platform investments require justification through measurable value delivery and return on investment calculations addressing both quantitative cost savings and qualitative risk reduction benefits. Service now grc generates value across multiple dimensions relevant to financial services compliance management, though measurement approaches vary based on practice priorities and baseline compliance maturity.
Quantitative Value Metrics
Financial advisors can measure platform ROI through several quantifiable metrics:
Compliance administration time reduction comparing hours spent on policy management, risk assessments, audit preparation, and regulatory reporting before and after platform deployment. Many practices report 30-50% efficiency gains in compliance officer productivity through workflow automation and centralized information access.
Audit preparation cost savings measuring reduced external auditor hours, lower consulting fees for FSCA inspection readiness, and diminished overtime expenses during audit seasons. Platform-enabled continuous evidence collection typically reduces audit preparation cycles from weeks to days.
Training administration efficiency calculating time savings from automated CPD tracking, competency requirement monitoring, and training attestation workflows versus manual spreadsheet maintenance. For practices with multiple representatives, these efficiencies compound significantly.
Regulatory penalty avoidance estimating fines, license suspensions, or business restrictions prevented through improved compliance oversight and proactive deficiency remediation. While speculative, practices with documented compliance improvements following platform adoption can reasonably attribute regulatory risk reduction to enhanced capabilities.
Qualitative Value Dimensions
Beyond direct cost savings, service now grc delivers qualitative benefits affecting practice sustainability, client confidence, and competitive positioning:
- Enhanced regulatory credibility demonstrated through sophisticated compliance programs during FSCA inspections, potentially influencing enforcement discretion when minor deficiencies emerge
- Improved client trust resulting from visible compliance professionalism including documented POPIA processing inventories, systematic FICA procedures, and transparent complaint handling
- Reduced compliance stress as advisors transition from reactive firefighting to proactive risk management with clear visibility into compliance statuses and upcoming obligations
- Scalability enablement supporting practice growth without proportional compliance resource increases through automated workflows and standardized processes
These qualitative dimensions prove difficult to monetize directly but significantly influence practice value, acquisition attractiveness, and operational resilience during market disruptions or regulatory intensification.
Integration with South African Regulatory Reporting
Financial services providers face numerous regulatory reporting obligations including FICA suspicious transaction reports, POPIA data breach notifications, FAIS quarterly returns, and COFI conduct indicators. Service now grc can streamline regulatory reporting through data aggregation, automated compilation, and submission tracking that reduces reporting cycles whilst improving accuracy and completeness.
Automated Data Aggregation for Compliance Reporting
The platform's reporting capabilities extract compliance data from operational workflows, eliminating manual compilation exercises prone to errors and omissions. When advisors complete FICA verifications, document POPIA consent preferences, or record complaint resolutions within service now grc workflows, the platform automatically aggregates this information into reporting databases supporting regulatory return preparation.
For FAIS quarterly returns requiring key individual updates, complaint statistics, and training compliance confirmations, the platform generates draft submissions by querying current records rather than requiring compliance officers to manually compile data from multiple sources. This automation approach delivers several advantages:
- Accuracy improvement through systematic data extraction eliminating transcription errors and calculation mistakes common in manual compilation
- Completeness assurance by automatically including all relevant records rather than risking omissions through oversight or incomplete manual searches
- Time efficiency reducing quarterly return preparation from days to hours through automated drafting and review workflows
- Audit trail creation documenting data sources, extraction logic, and review decisions supporting regulatory queries about submitted returns
The platform's configuration flexibility allows practices to customize reporting templates reflecting their specific licensing categories, representative counts, and product portfolios whilst maintaining alignment with FSCA return specifications.
POPIA Breach Notification Workflows
POPIA Section 22 requires responsible parties to notify the Information Regulator and affected data subjects when data breaches occur meeting statutory thresholds. Service now grc provides incident response workflows guiding compliance officers through breach assessment, notification decision-making, regulator reporting, and affected individual communication following prescribed processes and timelines.
The breach response workflow typically includes:
Incident detection and logging capturing initial breach discovery with preliminary impact assessment including information categories affected, individual counts, and potential harm scenarios.
Breach assessment evaluating whether notification thresholds meet through structured criteria examining information sensitivity, breach scope, and harm likelihood. The platform's decision trees guide consistent threshold assessments across different incident types.
Regulator notification generating breach reports meeting Information Regulator specifications including incident timelines, affected individual counts, information categories compromised, breach causes, and remediation actions. The workflow enforces regulatory notification timelines through automatic escalations when deadlines approach.
Individual notification managing communication to affected data subjects through templated letters, email campaigns, or SMS notifications depending on contact information availability and breach severity. The platform tracks notification completion and delivery confirmations creating evidence of POPIA obligation fulfillment.
Remediation tracking monitoring corrective actions addressing breach root causes, control weaknesses, and process deficiencies preventing recurrence. This integration between incident response and control improvement creates continuous security enhancement cycles.
Adapting Service Now GRC to Independent Broker Workflows
Independent financial advisors operate different compliance models than large financial institutions, requiring service now grc configurations reflecting smaller team sizes, limited IT infrastructure, and advisor-led compliance responsibilities. Platform flexibility supports these independent practice requirements through simplified workflows, role consolidation, and user interface customization that maintain comprehensive compliance capabilities whilst accommodating resource constraints.
Simplified Workflow Configurations
Standard ServiceNow GRC implementations often include multi-level approval chains, specialized reviewer roles, and complex workflow branches appropriate for enterprise environments but excessive for independent practices. Smaller FSPs benefit from streamlined configurations that:
- Consolidate approval steps combining compliance officer and principal reviews into single approval stages when the same individual holds both roles
- Reduce workflow branches simplifying conditional routing that adds complexity without value in smaller operations
- Automate low-risk decisions implementing rules-based approvals for routine activities like standard policy updates or recurring risk assessments
- Customize notification frequencies reducing alert volumes to prevent notification fatigue whilst ensuring critical items receive appropriate attention
These simplifications maintain compliance rigor whilst respecting the practical realities of independent practices where principals balance compliance responsibilities with client service, business development, and operational management.
Mobile Access for Field Advisors
Many independent financial advisors conduct significant client interactions outside office environments, requiring mobile access to compliance workflows for remote FICA verification, client consent documentation, and risk assessment completion. Service now grc provides mobile applications supporting field compliance activities through smartphone and tablet interfaces optimized for common workflows.
Mobile capabilities particularly valuable for independent advisors include:
- Client document capture using device cameras to photograph identity documents, proof of residence, and supporting verification materials during client meetings, eliminating subsequent office scanning exercises
- Digital consent collection presenting POPIA processing notices and marketing consent forms on tablets for client review and electronic signature during onboarding discussions
- Offline functionality allowing advisors to complete needs analyses, product suitability assessments, and risk profiling questionnaires without internet connectivity, with automatic synchronization when connection restores
- Task notifications alerting advisors about pending compliance activities, upcoming client review deadlines, and outstanding documentation requirements regardless of physical location
These mobile capabilities extend platform value beyond office-based compliance officers to field advisors conducting day-to-day client interactions where many compliance obligations actually originate.
Service Now GRC and Third-Party Risk Management
Financial services providers increasingly rely on third-party service providers for technology infrastructure, marketing services, claims administration, and specialized advisory support, creating vendor risk management obligations under POPIA, COFI, and prudential requirements. Service now grc includes vendor risk assessment and monitoring modules that standardize how practices evaluate supplier compliance, monitor ongoing performance, and manage vendor-related incidents.
Vendor Onboarding and Due Diligence
The platform's vendor risk module guides compliance officers through systematic supplier evaluation addressing information security controls, regulatory compliance status, financial stability, and service delivery capabilities. For South African FSPs engaging marketing agencies, cloud hosting providers, or claims administrators, these assessments create documented evidence of responsible vendor selection meeting POPIA operator accountability requirements.
Vendor assessment workflows typically examine:
- Information security practices evaluating encryption standards, access controls, backup procedures, and incident response capabilities when vendors process client personal information
- Regulatory compliance status confirming vendor adherence to relevant regulations including POPIA registration, tax compliance, and industry-specific licensing where applicable
- Financial stability assessing vendor viability through financial statement review, credit checks, and business continuity planning evaluation
- Service level commitments documenting expected performance standards, response timeframes, and escalation procedures through formal service level agreements
The platform stores vendor assessment results, supporting documentation, and approval decisions in centralized repositories accessible during FSCA inspections or POPIA compliance audits.
Ongoing Vendor Performance Monitoring
Third-party risk management extends beyond initial onboarding into continuous performance monitoring ensuring vendors maintain compliance standards and service quality throughout engagement lifecycles. Service now grc supports ongoing vendor oversight through automated monitoring schedules, incident tracking, and periodic reassessment workflows that prevent vendor degradation from escaping attention until significant problems emerge.
Monitoring activities automated through the platform include:
Quarterly performance reviews evaluating vendor service delivery against contractual commitments, incident frequency, and compliance obligation fulfillment. The platform generates review tasks, provides standardized evaluation templates, and tracks completion ensuring consistent oversight across all supplier relationships.
Contract renewal workflows triggering reassessments when vendor agreements approach expiration, enabling informed continuation or termination decisions based on performance history and current risk profiles.
Incident aggregation consolidating vendor-related security events, service disruptions, and compliance breaches into vendor risk profiles, providing visibility into supplier reliability trends supporting retention decisions.
For compliance monitoring specialists supporting multiple FSP clients, these vendor oversight capabilities standardize third-party risk management across client portfolios whilst accommodating client-specific risk appetites and vendor relationship particulars.
Cyber Risk Management Through Service Now GRC
Financial services providers face escalating cyber threats targeting client information, transaction systems, and operational infrastructure, requiring comprehensive cyber risk management programs integrating technical controls, incident response procedures, and governance oversight. Service now grc connects cyber risk identification, control implementation, vulnerability management, and incident response into unified workflows that align information security activities with broader compliance obligations.
Cyber Risk Assessment Methodologies
The platform supports structured cyber risk assessments examining threat landscapes, vulnerability exposures, and control adequacy across technology infrastructure, application systems, and data repositories. South African FSPs can configure cyber risk assessment templates addressing sector-specific threats including:
- Phishing attacks targeting advisor credentials to access client information or transaction systems
- Ransomware incidents encrypting policy administration databases or document management repositories
- Payment fraud exploiting compromised client details or transaction authorization procedures
- Data exfiltration through unauthorized access to FICA verification documents or financial records
According to ISACA guidance on managing cyber risk with GRC platforms, integrated approaches connecting risk assessment, control monitoring, and incident response deliver superior outcomes compared to siloed security initiatives operating independently from compliance programs.
The cyber risk assessment workflow guides information security teams through systematic evaluation of:
Threat identification documenting relevant attack vectors based on industry intelligence, historical incidents, and technology environment analysis. The platform's threat library can be customized with financial services-specific scenarios reflecting observed attack patterns targeting South African FSPs.
Vulnerability assessment cataloging technical weaknesses, configuration deficiencies, and process gaps enabling threat exploitation. Integration with vulnerability scanning tools automates weakness identification and prioritization based on exploitability and potential impact.
Control evaluation assessing existing security measures including firewalls, encryption, access controls, monitoring systems, and incident response procedures. The platform links cyber controls to broader compliance requirements, demonstrating how information security investments simultaneously address POPIA obligations, operational risk mitigation, and business continuity objectives.
Risk quantification calculating potential financial impacts from successful cyber attacks considering client information compromise costs, business interruption losses, regulatory penalties, and reputation damage. These quantified risk profiles support investment prioritization and insurance coverage decisions.
Security Incident Response Integration
When cyber incidents occur, rapid response determines whether minor security events remain contained or escalate into significant data breaches requiring regulatory notification and client communication. Service now grc provides incident response workflows connecting event detection, investigation, containment, eradication, recovery, and lessons learned activities into coordinated procedures that minimize damage whilst creating compliance evidence.
The incident response workflow automation includes:
Automated incident creation from security monitoring tools, user reports, or vendor notifications, eliminating manual ticket generation delays that postpone response initiation.
Severity classification through structured criteria assessing information sensitivity, affected individual counts, and potential harm supporting appropriate response escalation and resource allocation.
Investigation task assignment distributing forensic analysis, scope determination, and root cause identification activities to appropriate IT personnel with progress tracking and evidence collection.
Breach notification assessment evaluating whether POPIA Section 22 thresholds meet through standardized decision trees guiding consistent notification determinations across different incident types.
Remediation tracking monitoring vulnerability patching, control strengthening, and process improvements addressing incident root causes preventing recurrence.
This integrated incident response approach ensures cyber security events receive coordinated attention whilst automatically generating compliance documentation supporting regulatory reporting and audit evidence requirements.
Cost Considerations and Licensing Models
Service now grc pricing varies significantly based on deployment scale, module selection, user counts, and customization requirements, making accurate cost estimation dependent on specific implementation parameters. South African FSPs should understand platform licensing models, ongoing administration costs, and total cost of ownership considerations when evaluating budget implications and ROI calculations.
Platform Licensing Structures
ServiceNow typically licenses the platform through subscription models charging per user based on role types and module access requirements. Common licensing tiers include:
Full users with complete platform access including configuration capabilities, workflow design, and administrative functions. Compliance officers typically require full user licenses supporting policy management, risk assessment creation, and reporting configuration.
Standard users accessing designated modules for specific workflow participation like policy attestation, risk response task completion, or audit finding remediation without broader platform privileges. Most advisors and principals fall into this category, participating in compliance workflows without requiring administrative capabilities.
Read-only users viewing reports, dashboards, and compliance documentation without workflow participation or data modification abilities. Senior management monitoring compliance metrics often needs only read-only access.
Platform licensing costs generally scale with user counts and module selections, making phased implementations that gradually expand platform scope more financially accessible than comprehensive deployments activating all modules simultaneously for all users.
Implementation and Ongoing Administration Costs
Beyond licensing fees, service now grc implementations incur consulting costs for configuration, customization, integration development, and training delivery. South African FSPs should budget implementation projects comprehensively addressing:
- Discovery and requirements definition engaging stakeholders to document current compliance processes, pain points, regulatory obligations, and platform objectives
- Configuration and customization adapting platform workflows, forms, and reports to FSP-specific requirements and South African regulatory context
- System integration development connecting service now grc to policy administration, CRM, document management, and other operational systems
- Data migration transferring existing policies, risk registers, audit findings, and compliance evidence from current systems into platform repositories
- User training delivering role-based instruction, creating reference materials, and conducting hands-on workshops
- Testing and validation verifying configured workflows operate correctly before production deployment
Ongoing administration costs include:
Platform subscription fees covering annual licensing for configured user counts and activated modules with typical escalation clauses tied to inflation or user growth.
System administration resources maintaining platform configurations, managing user access, applying updates, and providing first-level user support. Smaller practices may engage external administrators on retainer arrangements whilst larger FSPs often hire dedicated ServiceNow administrators.
Regulatory update maintenance modifying workflows, policies, and controls when regulations change, FSCA issues new guidance, or business processes evolve. These updates require ongoing platform expertise ensuring compliance relevance over time.
Understanding total cost of ownership including both initial implementation and ongoing administration expenses enables realistic budget planning and accurate ROI projections supporting informed platform adoption decisions.
ServiceNow GRC represents a transformative approach to compliance management for South African financial services providers, replacing fragmented manual processes with integrated workflows that connect policy management, risk assessment, audit execution, and regulatory reporting. Independent brokers and advisors navigating FICA, POPIA, FAIS, and COFI obligations gain significant advantages through platform capabilities that standardize compliance activities, automate evidence collection, and provide continuous visibility into regulatory adherence across their practices. Holistic Compliance Management Solutions (Pty) Ltd helps financial services providers implement comprehensive compliance frameworks tailored to South African regulatory requirements, whether you're establishing your first formal compliance program or enhancing existing risk management capabilities.
Schedule FICA training with Holistic Compliance Management Solutions to implement systematic customer due diligence procedures aligned with FICA obligations. Our training covers:
- FICA verification requirements and documentation standards for different client risk categories
- RMCP development and implementation for independent broker practices
- Practical workflows integrating FICA compliance into daily client onboarding processes
Who this is for: Independent brokers establishing formal compliance functions, compliance officers strengthening FICA procedures, and FSP applicants preparing for licensing approval.