PCI DSS Consultant: Your Complete South Africa Guide 2026
The Payment Card Industry Data Security Standard (PCI DSS) has become a cornerstone of payment security across the globe, yet many South African financial service providers and independent brokers underestimate its relevance to their daily operations. When your practice processes credit or debit card transactions-whether for policy premiums, advisory fees, or client payments-you enter the scope of PCI DSS compliance. A pci dss consultant brings specialised expertise to navigate this complex framework, helping your business avoid costly data breaches, regulatory penalties, and reputational damage whilst maintaining the trust your clients place in your financial services practice.
Understanding the PCI DSS Consultant Role in Financial Services
A pci dss consultant serves as your dedicated expert for implementing, maintaining, and validating payment card security controls. Unlike general IT consultants, these specialists possess deep knowledge of the twelve PCI DSS requirements, the nuances of scoping cardholder data environments, and the practical application of security measures within South African business contexts.
What Distinguishes a PCI DSS Consultant from General Compliance Advisors
The distinction matters significantly for financial service providers operating under South Africa's regulatory umbrella. Whilst your existing compliance framework addresses FAIS, FICA, POPIA, and COFI requirements, payment card security demands additional technical controls and validation procedures. A qualified pci dss consultant brings:
- Technical security expertise spanning network architecture, encryption standards, and vulnerability management
- Assessment methodology aligned with the PCI Security Standards Council requirements
- Scoping proficiency to minimise your cardholder data environment and reduce compliance burden
- Remediation planning that integrates with your existing risk management frameworks
- Validation services through self-assessment questionnaires (SAQs) or full audits
The Qualified Security Assessor (QSA) program establishes the gold standard for PCI DSS professionals, ensuring consultants maintain current knowledge through annual recertification and adherence to strict quality standards.
How PCI DSS Overlaps with South African Financial Compliance
South African financial service providers face a unique compliance landscape where payment security intersects with data protection and financial services regulations. Your pci dss consultant must understand how the standard complements POPIA's data protection principles, FICA's client verification requirements, and FAIS's fit-and-proper criteria for FSPs.
Consider this compliance intersection:
| Regulatory Framework | Primary Focus | PCI DSS Connection |
|---|---|---|
| POPIA (Protection of Personal Information Act) | Personal data protection across all categories | Cardholder data qualifies as special personal information requiring enhanced security |
| FICA (Financial Intelligence Centre Act) | Client identification and record-keeping | Payment records intersect with customer due diligence documentation |
| FAIS (Financial Advisory and Intermediary Services Act) | Professional conduct and client protection | Secure payment handling demonstrates professional competence |
| COFI (Conduct of Financial Institutions) | Fair treatment of customers | Payment security protects clients from financial harm through data breaches |
This intersection means your compliance monitoring programme must address payment security alongside traditional financial services obligations, creating efficiency when consultants understand both domains.
Determining When Your Practice Requires a PCI DSS Consultant
Not every financial service provider needs the same level of PCI DSS support. The scope, complexity, and validation requirements depend on how your practice handles payment card data. Understanding these distinctions helps you engage the right consultant at the appropriate stage.
Transaction Volume and Merchant Level Classification
The card brands (Visa, Mastercard, American Express) classify merchants into four levels based on annual transaction volumes. Your classification determines validation requirements:
Level 1 Merchants (over 6 million transactions annually) require an annual Report on Compliance (ROC) completed by a QSA and quarterly network scans by an Approved Scanning Vendor (ASV). Most independent financial advisory practices won't reach this threshold, but larger FSPs with extensive client bases might.
Level 2 Merchants (1-6 million transactions) typically complete an annual Self-Assessment Questionnaire and quarterly network scans. Mid-sized brokerages processing substantial premium payments often fall into this category.
Level 3 and 4 Merchants (under 1 million transactions) generally complete SAQs and may require quarterly scans depending on their acquiring bank's requirements. Most independent brokers and smaller advisory practices occupy these levels.
Payment Processing Methods and SAQ Types
Your payment processing approach determines which Self-Assessment Questionnaire applies. The SAQ Instructions and Guidelines detail nine different SAQ types, but financial service providers typically encounter these scenarios:
- SAQ A – E-commerce merchants who fully outsource payment processing through redirect or iframe integration (no cardholder data touches your systems)
- SAQ A-EP – E-commerce merchants with website payment forms where data passes through but isn't stored
- SAQ B – Standalone terminals or dial-up machines with no electronic storage
- SAQ C – Payment application systems connected to the internet
- SAQ D – All other merchant environments not fitting the above criteria
A pci dss consultant evaluates your current payment infrastructure and recommends the optimal processing method to minimise scope and compliance burden. Many South African brokers discover they can shift from complex SAQ D scenarios to simpler SAQ A configurations by redesigning payment workflows.
Red Flags That Signal Consultant Engagement
Certain situations demand immediate pci dss consultant involvement rather than self-guided compliance attempts:
- Data breach or suspected compromise – Consultants coordinate forensic investigation and remediation
- Failed compliance validation – When your SAQ reveals extensive gaps requiring technical remediation
- Major system changes – Network upgrades, new payment applications, or office relocations affecting cardholder data
- Acquiring bank compliance notices – Formal warnings about non-compliance or required validation deadlines
- Expansion into new payment channels – Adding online payments, mobile processing, or recurring billing
- Merger or acquisition activity – Integrating payment systems from acquired practices
The NIST framework alignment provides useful context for understanding how PCI DSS controls map to broader cybersecurity objectives, helping you assess where payment security fits within your overall risk management approach.
Core Services Financial Service Providers Receive from PCI DSS Consultants
Engaging a pci dss consultant provides access to a comprehensive suite of services designed to establish, maintain, and prove payment security compliance. These services adapt to your practice's size, complexity, and current compliance maturity.
Gap Analysis and Current State Assessment
Every consultant engagement should begin with a thorough evaluation of your existing payment security posture. This initial assessment:
- Documents your cardholder data flow from initial capture through storage, transmission, and destruction
- Identifies all systems, people, and processes within scope of PCI DSS requirements
- Compares current controls against the twelve PCI DSS requirement domains
- Quantifies compliance gaps with prioritisation based on risk severity
- Estimates remediation effort including time, resources, and costs
The gap analysis provides your compliance roadmap, establishing clear priorities and realistic timelines for achieving validation readiness. For South African FSPs managing multiple regulatory obligations, this assessment should integrate with your existing FICA RMCP (Risk Management and Compliance Programme) to avoid duplicated effort.
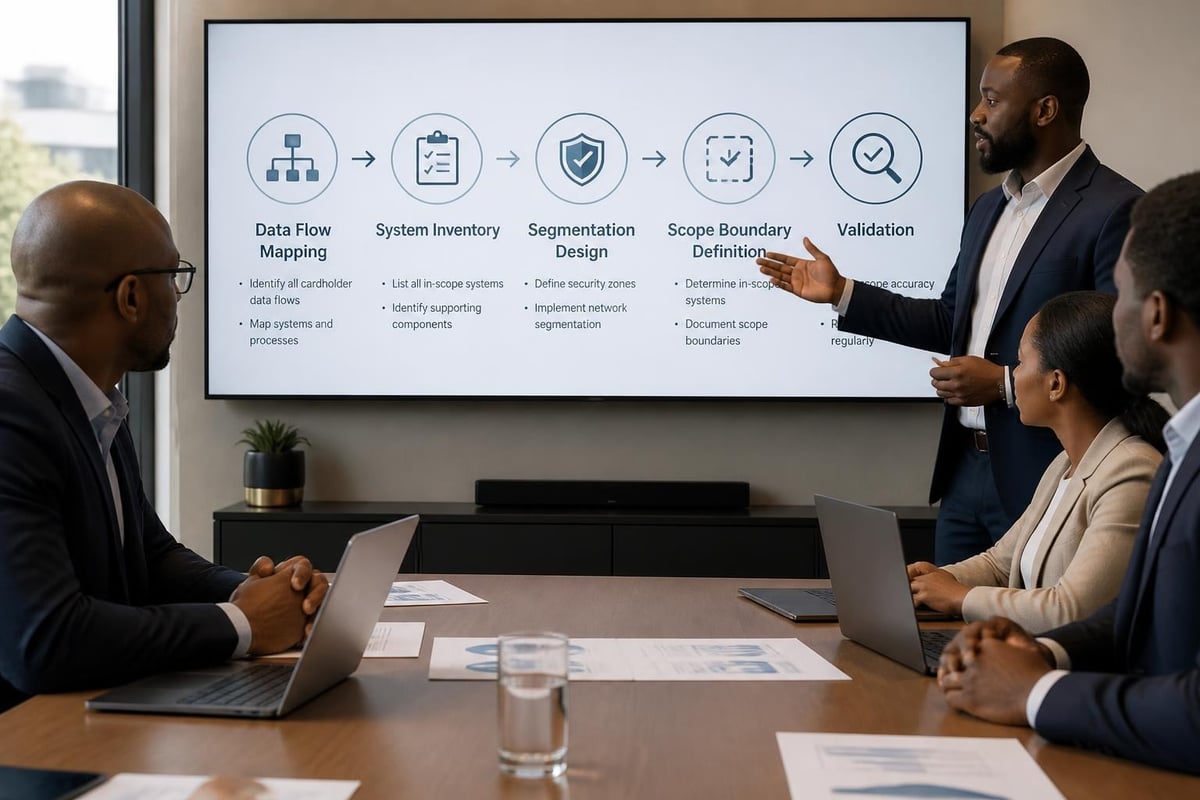
Scoping and Network Segmentation Guidance
Perhaps the most valuable service a pci dss consultant delivers is proper scoping-defining exactly which systems, networks, and processes must comply with PCI DSS requirements. Effective scoping dramatically reduces compliance costs and complexity.
Segmentation strategies isolate cardholder data environments from general business networks through:
- Physical network separation with distinct switches and routers
- Virtual LAN (VLAN) configuration with restricted inter-VLAN routing
- Firewall rules limiting traffic flows between zones
- Air-gapped systems processing payments independently
Consider this scoping scenario common among independent brokers:
| System/Function | Initially In Scope | After Consultant Scoping | Scope Reduction Method |
|---|---|---|---|
| Client management CRM | Yes (stored card data) | No | Redirect payment processing; remove card storage |
| Practice management software | Yes (payment history) | No | Store only masked card numbers and transaction IDs |
| Email servers | Yes (payment confirmations) | No | Eliminate card data from email templates |
| Staff workstations | Yes (manual card entry) | Partial (one dedicated station) | Designate single hardened workstation for payments |
| File servers | Yes (document storage) | No | Implement strict policy against storing card images/forms |
The OWASP payment integration guidance offers practical techniques for developers and consultants to minimise application scope through proper integration patterns.
Policy Development and Documentation Support
PCI DSS requires extensive written policies, procedures, and documentation across all twelve requirement domains. Your pci dss consultant develops or updates:
- Information security policy establishing governance and accountability
- Acceptable use policies for staff accessing payment systems
- Access control procedures defining user provisioning and termination
- Change management processes for system modifications
- Incident response plans addressing suspected or confirmed breaches
- Vendor management frameworks for third-party service providers
- Security awareness training materials tailored to financial services contexts
These documents must align with your existing compliance framework. For example, your PCI DSS incident response plan should integrate with POPIA breach notification procedures and FAIS complaint handling processes, creating a unified approach rather than siloed documentation.
Technical Control Implementation and Validation
Beyond documentation, achieving PCI DSS compliance demands specific technical security controls. A pci dss consultant either implements these controls directly or provides specifications for your IT team:
- Firewall and router configuration restricting unnecessary inbound and outbound traffic
- Strong cryptography for cardholder data transmission across public networks
- Anti-malware solutions with automatic updates and regular scanning
- Secure system development and change control for payment applications
- Access control mechanisms including unique user IDs and two-factor authentication
- Physical security measures protecting payment terminals and server infrastructure
- Monitoring and logging systems recording all access to cardholder data
- Vulnerability scanning and penetration testing identifying security weaknesses
The SANS white paper on managing human risk emphasises that technical controls fail without corresponding attention to staff awareness, training, and security culture-particularly relevant for small broker practices where administrative staff often handle payment processing.
SAQ Completion and ROC Preparation
When validation deadlines approach, your pci dss consultant guides you through the appropriate attestation process. For most South African financial service providers, this means completing a Self-Assessment Questionnaire specific to your processing method.
The consultant:
- Selects the correct SAQ type based on your payment infrastructure
- Gathers evidence demonstrating compliance with each applicable requirement
- Documents compensating controls where standard implementations prove impractical
- Identifies any non-compliant items requiring remediation before attestation
- Completes the attestation for submission to your acquiring bank
Larger FSPs requiring a Report on Compliance engage QSA-certified consultants to perform the formal audit, test controls, and issue the validation report.
Selecting the Right PCI DSS Consultant for South African Financial Services
The consultant you choose significantly impacts your compliance journey's success, cost-effectiveness, and ongoing sustainability. South African FSPs should evaluate candidates against specific criteria reflecting local regulatory context and financial services expertise.
Essential Qualifications and Certifications
Whilst PCI DSS consulting doesn't require specific South African licensing (unlike financial services itself), certain credentials indicate professional competence:
Industry Certifications to Prioritise:
- Qualified Security Assessor (QSA) – The premier PCI DSS credential for consultants performing formal assessments
- Internal Security Assessor (ISA) – Appropriate for consultants supporting self-assessment processes
- Certified Information Systems Security Professional (CISSP) – Demonstrates broad security expertise
- Certified Information Security Manager (CISM) – Indicates management and governance capabilities
- Payment Card Industry Professional (PCIP) – Shows PCI-specific knowledge foundation
Beyond certifications, verify the consultant's practical experience with financial services clients, particularly in South Africa. Understanding POPIA, FICA, and FAIS requirements enables integrated compliance approaches that save time and resources.
South Africa-Specific Considerations
Geography matters in compliance consulting. A pci dss consultant familiar with South African business contexts brings distinct advantages:
- Understanding of local payment ecosystems including prevalent acquiring banks, payment gateways, and processing platforms
- Knowledge of POPIA alignment ensuring cardholder data protection meets both PCI DSS and data protection standards
- Familiarity with FSP operations including policy administration, premium collection, and claims processing workflows
- Awareness of infrastructure constraints in areas with connectivity challenges or load-shedding impacts
- Local time zone availability for urgent support during business hours
Consultants based internationally may offer lower rates but often lack context for South Africa's unique operating environment and regulatory landscape.
Evaluating Consultant Service Models
PCI DSS consultants typically offer three engagement models, each suited to different practice sizes and compliance maturity levels:
| Service Model | Best For | Typical Deliverables | Engagement Duration |
|---|---|---|---|
| Project-Based | Initial compliance implementation or major remediation | Gap analysis, policy templates, technical specifications, SAQ completion | 3-6 months |
| Retainer/Ongoing | Continuous compliance management and annual validation | Quarterly reviews, policy updates, staff training, annual SAQ/ROC | 12+ months (renewable) |
| Virtual CISO/Fractional | Practices needing strategic security leadership | Monthly strategy sessions, vendor management, incident response, board reporting | 12+ months (part-time role) |
Independent brokers and smaller advisory practices typically start with project-based engagements to achieve initial compliance, then transition to lighter retainer arrangements for annual validation support. Larger FSPs often find ongoing or fractional models more cost-effective than building internal PCI expertise.
Questions to Ask During Consultant Selection
Interview potential consultants using these qualifying questions:
- How many South African financial service providers have you helped achieve PCI DSS compliance? (Look for specific FSP/broker examples)
- What SAQ types have you completed for practices similar to ours? (Ensures relevant experience)
- How do you integrate PCI DSS with POPIA, FICA, and FAIS compliance? (Tests understanding of local regulatory context)
- What scope reduction strategies have proven most effective for broker practices? (Evaluates practical optimization skills)
- Can you provide references from current or former South African FSP clients? (Enables verification of claimed expertise)
- What tools and technologies do you recommend for our practice size? (Assesses solution appropriateness)
- How do you handle ongoing support between annual validations? (Clarifies service continuity)
- What happens if we experience a suspected data breach during your engagement? (Tests incident response capabilities)
The ISACA audit resources provide professional standards that reputable consultants should reference in their assessment methodologies.
Implementing PCI DSS Compliance: A Step-by-Step Broker Workflow
Achieving and maintaining PCI DSS compliance follows a structured process that your consultant guides you through. This workflow adapts to South African broker practices whilst meeting the standard's technical requirements.
Phase 1: Discovery and Documentation (Weeks 1-3)
Your pci dss consultant begins by thoroughly understanding your payment operations:
Week 1 Activities:
- Conduct stakeholder interviews with principals, administrators, and IT support
- Document all payment acceptance channels (in-person, telephone, online, mobile)
- Inventory systems that store, process, or transmit cardholder data
- Review existing IT infrastructure diagrams and update for accuracy
- Collect current security policies related to data handling and access control
Week 2 Activities:
- Map complete cardholder data flows from capture through disposal
- Identify all personnel with access to payment systems or data
- Document third-party service providers involved in payment processing
- Review contracts with payment processors, gateways, and technology vendors
- Conduct initial walkthrough of physical security measures
Week 3 Activities:
- Define preliminary scope boundaries for the cardholder data environment
- Assess current alignment with each PCI DSS requirement domain
- Identify quick wins for immediate risk reduction
- Prioritise compliance gaps based on severity and remediation complexity
- Present initial findings and recommend scope reduction opportunities
This discovery phase establishes your compliance baseline and often reveals that many brokers unnecessarily expanded their PCI scope through poor payment handling practices.
Phase 2: Scope Reduction and Architecture Redesign (Weeks 4-8)
The most impactful compliance work happens during scoping optimisation. Your consultant redesigns payment workflows to minimise systems touching cardholder data:
Common Scope Reduction Strategies for Brokers:
- Redirect payment processing – Client clicks "Pay Now" on invoice and gets redirected to payment gateway's secure page
- Tokenisation implementation – Replace stored card numbers with meaningless tokens for recurring billing
- Point-to-point encryption (P2PE) – Encrypt card data at the moment of capture, before it reaches your systems
- Dedicated payment terminals – Use standalone EMV terminals disconnected from your business network
- Outsourced telephone payments – Direct clients to payment service provider's IVR system for phone payments
These strategies can reduce your scope from dozens of systems (SAQ D with hundreds of requirements) to a handful (SAQ A with just 22 requirements). The compliance burden difference is enormous.
Phase 3: Control Implementation and Remediation (Weeks 9-16)
With optimised scope defined, implementation addresses remaining compliance gaps:
Technical Controls Implementation:
- Configure firewalls to restrict traffic to/from cardholder data environment
- Implement multi-factor authentication for administrative access
- Deploy anti-malware software with centralised management
- Enable comprehensive logging for payment system access
- Schedule quarterly vulnerability scans through approved scanning vendor
- Establish encrypted connections (TLS 1.2+) for any cardholder data transmission
Administrative Controls Implementation:
- Develop or update information security policy suite
- Create role-based access control matrix defining who can access what
- Implement formal user provisioning and termination procedures
- Establish change management process for payment system modifications
- Design security awareness training programme for all staff
- Document incident response procedures aligned with POPIA breach notification
Physical Controls Implementation:
- Restrict physical access to rooms containing payment terminals or servers
- Implement visitor logs and escort procedures
- Deploy video surveillance (where appropriate) for sensitive areas
- Secure backup media in locked, access-controlled storage
- Establish secure destruction procedures for paper records containing card data
The FTC’s Start with Security guidance provides practical baseline recommendations that complement PCI DSS technical requirements.
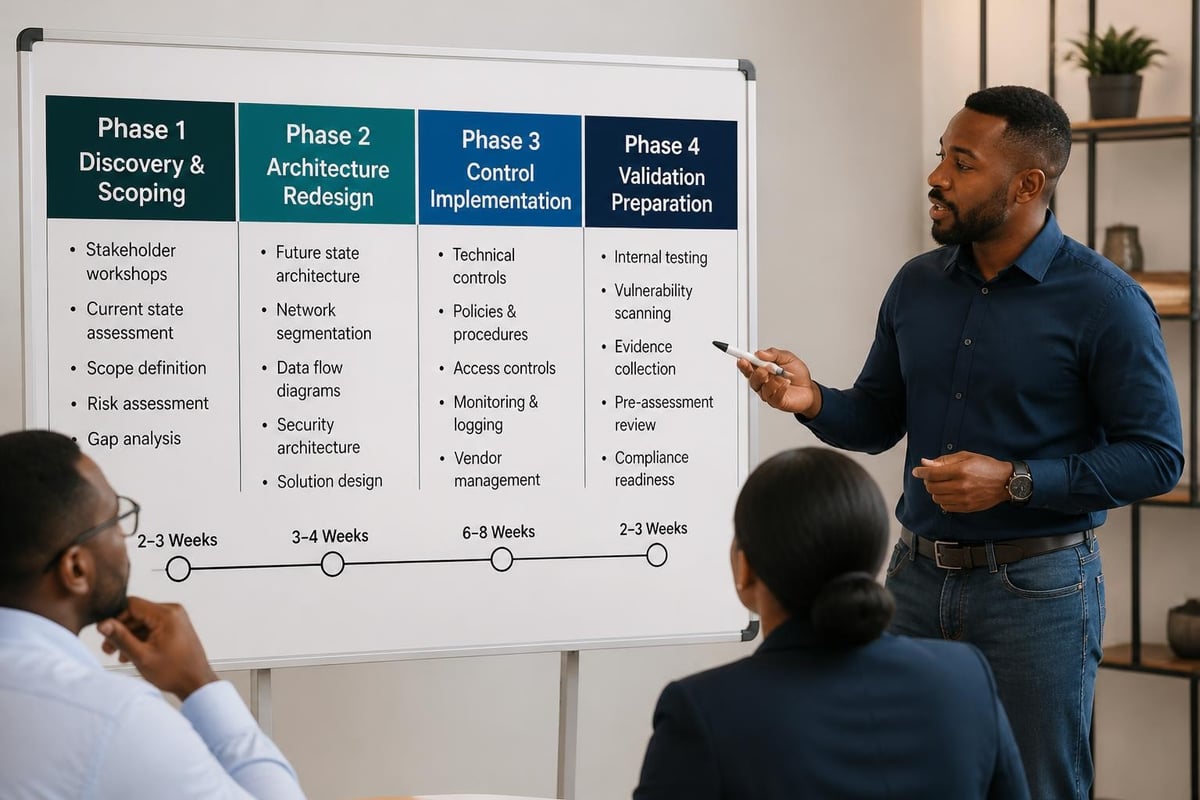
Phase 4: Validation and Attestation (Weeks 17-20)
Final validation proves compliance readiness before submitting attestation to your acquiring bank:
Pre-Validation Activities:
- Review all evidence collected demonstrating compliance with applicable requirements
- Conduct internal control testing to verify effectiveness
- Address any identified gaps or weaknesses discovered during testing
- Complete required penetration testing (for SAQs that require it)
- Obtain quarterly vulnerability scan reports showing passing results
SAQ Completion Process:
- Select and complete appropriate Self-Assessment Questionnaire type
- Document compensating controls for any requirements where standard approaches prove impractical
- Gather executive attestation confirming accuracy and completeness
- Submit completed SAQ and Attestation of Compliance to acquiring bank
- Maintain all supporting evidence in organised compliance repository
Ongoing Compliance Maintenance:
- Schedule quarterly vulnerability scans throughout the year
- Conduct annual SAQ renewal with evidence updates
- Perform security awareness training for new staff within 30 days of hire
- Review and update policies annually or when business changes occur
- Monitor PCI Security Standards Council for updates to requirements
Your pci dss consultant typically remains engaged for the first annual validation cycle, then transitions to lighter advisory support for subsequent years.
Managing PCI DSS Compliance Costs for South African Brokers
Compliance costs concern every independent broker and advisory practice. Understanding the investment required helps you budget appropriately and evaluate return through reduced breach risk and client confidence.
Typical Consultant Fee Structures
PCI DSS consultant pricing varies based on practice size, complexity, and current compliance maturity. South African market rates (2026) typically fall into these ranges:
Initial Implementation Projects:
- Small practice (1-5 staff, simple payment processing): R45,000 – R85,000
- Medium practice (6-20 staff, multiple payment channels): R85,000 – R165,000
- Large practice (21+ staff, complex environment): R165,000 – R350,000+
Ongoing Annual Support:
- Quarterly reviews and annual SAQ completion: R15,000 – R35,000 per year
- Retainer arrangements with monthly support: R8,500 – R18,000 per month
- Virtual CISO fractional services: R25,000 – R55,000 per month
These fees cover consultant time but exclude technology investments (security software, payment terminals, encryption solutions) and any required infrastructure upgrades.
Hidden Costs to Anticipate
Beyond consultant fees, budget for these compliance-related expenses:
- Quarterly vulnerability scanning – R2,500 – R6,500 per quarter through approved scanning vendors
- Annual penetration testing – R18,000 – R65,000 (required for some SAQ types and all ROCs)
- Security technology – R15,000 – R85,000 for firewalls, anti-malware, logging systems, encryption tools
- Payment gateway fees – Scope-reducing gateways may charge slightly higher transaction fees
- Staff training time – Hours invested in security awareness programmes
- Policy documentation – Time spent reviewing, customising, and implementing required policies
For many practices, shifting to scope-reducing payment methods delivers net cost savings despite slightly higher transaction fees, as the reduced compliance burden more than compensates.
Cost-Benefit Analysis: Compliance Investment vs Breach Impact
Evaluating PCI DSS investment requires comparing compliance costs against potential breach consequences:
Direct Breach Costs (South African Context):
- Forensic investigation – R125,000 – R450,000 for qualified investigators
- Card brand fines – R50,000 – R500,000+ depending on breach size and merchant level
- Card reissuance fees – R175 – R425 per compromised card
- POPIA penalties – Up to R10 million or imprisonment for serious data protection violations
- Legal expenses – R85,000 – R350,000+ for breach response and potential litigation
- Credit monitoring services – R350 – R750 per affected client for 12-24 months
Indirect Breach Consequences:
- Loss of payment card acceptance privileges (business-ending for many brokers)
- Reputational damage affecting client acquisition and retention
- Increased insurance premiums or loss of coverage
- Regulatory scrutiny affecting FSP license status
- Mandatory compliance programmes imposed by card brands
- Loss of competitive advantage as clients migrate to secure competitors
The NCSC ransomware guidance provides valuable context on breach response decision-making that consultants should incorporate into incident planning.
Maximising Compliance ROI
Strategic approaches increase value from your PCI DSS investment:
- Integrate with existing compliance programmes – Align PCI work with POPIA, FICA, and FAIS requirements to reduce duplicated effort
- Leverage consultant expertise broadly – Use PCI engagement to strengthen overall cybersecurity posture, not just payment security
- Invest in scope reduction – Upfront architecture changes deliver ongoing compliance savings
- Build internal capability – Train staff to maintain compliance between consultant engagements
- Choose scalable solutions – Select technologies that support practice growth without requiring replacement
The compliance monitoring services offered by specialised providers can integrate PCI DSS oversight with broader regulatory obligations, creating efficiency for South African FSPs.
Common PCI DSS Challenges for South African Financial Service Providers
South African brokers and advisors encounter unique compliance obstacles stemming from infrastructure constraints, resource limitations, and the complexity of integrating multiple regulatory frameworks. Your pci dss consultant must address these practical realities.
Load-Shedding and Infrastructure Reliability
Scheduled power outages create specific PCI DSS compliance challenges:
Security Control Impacts:
- Firewalls and network security devices losing configuration during power events
- Logging systems experiencing gaps during outages and recovery periods
- Physical access controls (electronic locks, video surveillance) failing during power loss
- Backup systems and redundancy measures being tested repeatedly
Consultant Solutions:
- Implement uninterruptible power supplies (UPS) for critical payment infrastructure
- Configure automatic restore and verification of security settings post-outage
- Establish compensating controls for gaps in video surveillance or electronic access logs
- Document load-shedding impacts in risk assessment and include in SAQ evidence
- Design incident response procedures specifically addressing power-related security events
Your pci dss consultant should evaluate infrastructure resilience as part of the initial assessment and recommend practical, cost-effective solutions appropriate for South African operating conditions.
Remote Work and Distributed Practice Models
The shift toward hybrid work arrangements introduced new payment security considerations:
Scope Expansion Risks:
- Home networks of staff processing payments becoming in-scope
- Personal devices used for payment-related activities
- Unsecured Wi-Fi connections transmitting cardholder data
- Lack of physical security for payment terminals in home offices
- Difficulty monitoring and logging remote payment activities
Effective Scoping Strategies:
- Implement browser-based payment processing requiring no local software
- Deploy virtual desktop infrastructure (VDI) for payment system access
- Establish strict policy prohibiting payment processing from home
- Centralise all payment activities in secure office environment
- Use mobile point-of-sale devices with built-in encryption for field work
Remote work doesn't prevent PCI compliance, but requires thoughtful architectural decisions that your consultant guides.
Resource Constraints in Small and Medium Practices
Independent brokers and smaller advisory practices lack dedicated IT staff, creating compliance implementation challenges:
Common Resource Gaps:
- No in-house technical expertise for security configuration
- Limited budget for enterprise-grade security technologies
- Insufficient time for comprehensive policy development and maintenance
- Lack of security awareness training infrastructure
- Minimal incident response capabilities
Consultant Approaches:
- Recommend managed security services providing enterprise capabilities at SME price points
- Design simplified policies using templates customised to practice specifics
- Deliver turnkey training programmes requiring minimal internal administration
- Establish relationships with incident response retainers for breach support
- Prioritise scope reduction to minimise ongoing compliance burden
The most effective pci dss consultant recognises resource constraints and designs pragmatic solutions rather than gold-plated enterprise approaches inappropriate for small practices.
Integrating Multiple Compliance Frameworks
South African financial service providers juggle numerous regulatory obligations simultaneously. Your consultant must understand how PCI DSS intersects with:
POPIA (Protection of Personal Information Act):
- Cardholder data qualifies as personal information requiring protection
- PCI DSS technical controls satisfy many POPIA security safeguard requirements
- Breach notification procedures must address both PCI and POPIA obligations
- Data subject access requests may extend to payment transaction records
- Cross-border data flow restrictions affect payment processor selection
FICA (Financial Intelligence Centre Act):
- Payment records contribute to client due diligence documentation
- Record retention requirements apply to both FICA and PCI contexts
- Secure storage protects payment data supporting FICA obligations
- Access controls serve both payment security and FICA confidentiality needs
FAIS (Financial Advisory and Intermediary Services Act):
- Secure payment handling demonstrates competence and professionalism
- Client protection obligations extend to payment security
- Complaints handling must address payment security incidents
- Fit-and-proper requirements include data protection capabilities
Holistic compliance approaches recognise these overlaps and design integrated programmes rather than siloed frameworks. For South African FSPs managing FICA RMCP requirements, PCI DSS controls should integrate seamlessly with existing risk management and compliance programmes rather than creating separate, parallel documentation.
Securing payment card data through proper PCI DSS compliance protects your clients, preserves your reputation, and demonstrates the professional competence South African financial regulators expect. Whether you're an independent broker processing occasional card payments or a larger FSP with substantial transaction volumes, engaging a qualified pci dss consultant ensures you implement appropriate controls efficiently whilst integrating payment security with your broader compliance obligations under POPIA, FICA, FAIS, and COFI.
Who this is for: Independent insurance brokers, regulated financial advisors, FSP compliance officers, and practice principals managing payment card acceptance.
Schedule a compliance consultation with Holistic Compliance Management Solutions (Pty) Ltd to evaluate your current payment security posture and develop an integrated approach addressing PCI DSS alongside your existing regulatory obligations. Our consultation includes:
- Assessment of your current payment processing methods and PCI scope
- Gap analysis comparing your controls against PCI DSS requirements
- Recommendations for scope reduction and architecture optimisation
- Integration strategy aligning payment security with POPIA, FICA, and FAIS compliance
- Practical implementation roadmap tailored to independent broker workflows