Financial Services Regulatory Compliance Guide 2026
Financial services regulatory compliance has become increasingly complex for independent brokers and Financial Service Providers (FSPs) operating in South Africa. With multiple pieces of legislation governing data protection, anti-money laundering, conduct standards, and licensing requirements, staying compliant demands structured systems, ongoing training, and proactive risk management. For broker practices and advisory firms, understanding the interplay between POPIA, FICA, FAIS, and COFI is not merely about avoiding penalties-it's about building client trust, operational resilience, and sustainable business growth in 2026's evolving regulatory landscape.
Understanding South Africa's Financial Services Regulatory Framework
The South African financial services sector operates under a multi-layered regulatory framework designed to protect consumers, prevent financial crime, and maintain market integrity. Financial services regulatory compliance requires FSPs and independent brokers to navigate four primary pieces of legislation, each with distinct obligations and enforcement mechanisms.
The Financial Advisory and Intermediary Services Act (FAIS) governs the licensing and conduct of financial advisors and intermediaries, establishing minimum competency requirements and practice standards. The Financial Intelligence Centre Act (FICA) imposes anti-money laundering and counter-terrorism financing obligations, requiring robust client identification and transaction monitoring. The Protection of Personal Information Act (POPIA) regulates how FSPs collect, process, store, and share client data, whilst the Conduct of Financial Institutions Bill (COFI) introduces comprehensive conduct standards that will reshape client engagement and product design.
Regulatory Bodies and Enforcement
Three primary regulators oversee financial services regulatory compliance in South Africa:
- Financial Sector Conduct Authority (FSCA) supervises market conduct, enforces FAIS and COFI requirements, and issues licences to FSPs
- Prudential Authority (PA) focuses on the safety and soundness of financial institutions
- Information Regulator enforces POPIA compliance and investigates data protection complaints
- Financial Intelligence Centre (FIC) monitors FICA compliance and receives suspicious transaction reports
Penalties for non-compliance have escalated significantly. POPIA violations can result in fines up to R10 million or imprisonment of up to 10 years for directors. FICA breaches attract administrative sanctions up to R10 million per contravention. FAIS non-compliance can lead to licence suspension, debarment, and criminal prosecution. The international standards for prudential supervision inform South Africa's regulatory approach, ensuring alignment with global best practices.
FAIS Compliance Requirements for Independent Brokers
Financial Advisory and Intermediary Services compliance forms the foundation of lawful practice for independent brokers. The FAIS Act requires all individuals and entities providing financial services to hold an FSP licence or operate as authorised representatives under a licensed FSP.
FSP Licensing Categories and Prerequisites
South Africa's licensing framework distinguishes between several FSP categories, each with specific capital, competency, and governance requirements:
| Licence Category | Capital Requirement | Key Representatives | Common Use Case |
|---|---|---|---|
| Category I | R100,000 | Key Individual, Compliance Officer | Full-service brokerage |
| Category IIA | R50,000 | Key Individual | Short-term insurance intermediary |
| Category IIB | R30,000 | Key Individual | Long-term insurance intermediary |
| Category III | None | Key Individual | Representative office |
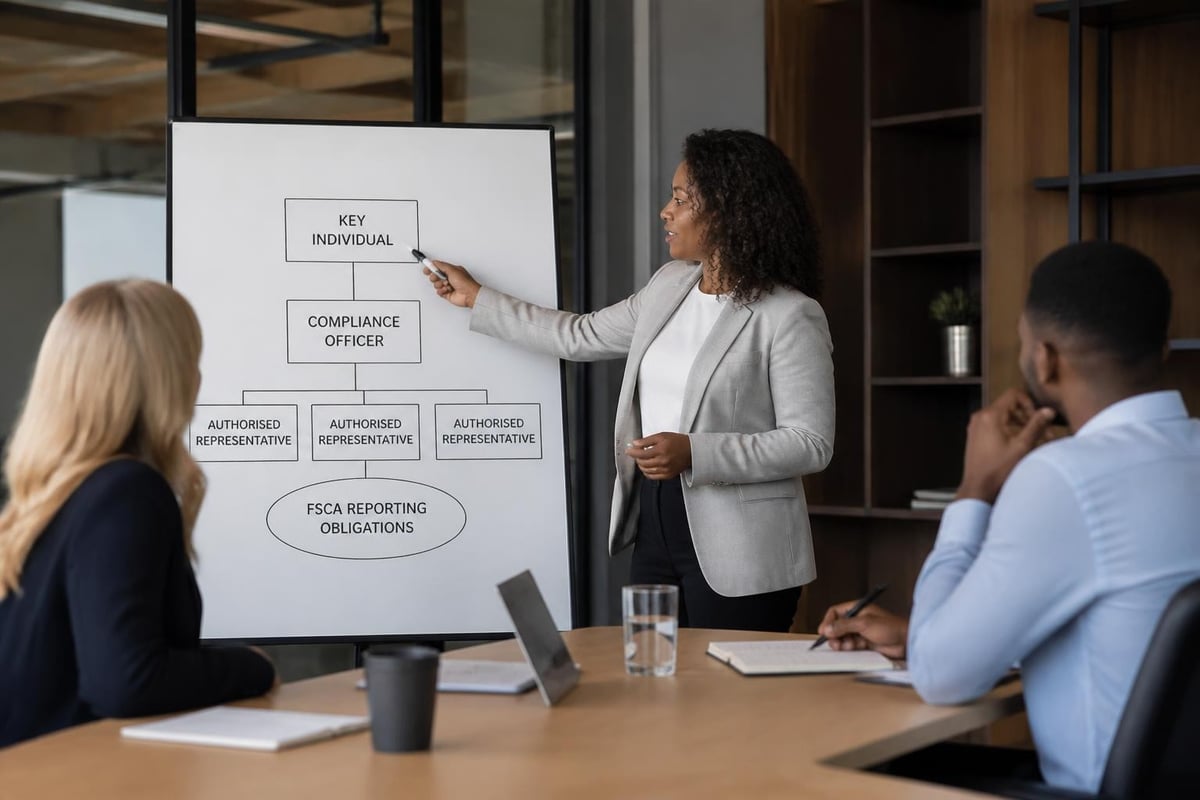
Each FSP must appoint a Key Individual who meets fit-and-proper requirements and holds the appropriate regulatory examinations. The Compliance Officer (required for Category I licences) ensures the FSP maintains ongoing financial services regulatory compliance and submits required returns to the FSCA.
Regulatory Examination Requirements
The FSCA mandates that all representatives complete regulatory examinations aligned to the financial products they advise on. The RE 1 examination covers regulatory frameworks and ethics. Product-specific examinations (RE 5 for long-term insurance, RE 5 short-term for general insurance, RE 7 for securities) test technical knowledge.
Independent brokers expanding their product range must complete additional examinations within 12 months of registration. Many practices struggle with exam preparation and pass rates. Structured RE EXAM Training programmes significantly improve first-time pass rates by focusing on practical application of regulatory principles rather than rote memorisation.
Fit and Proper Requirements
Financial services regulatory compliance demands that all representatives, Key Individuals, and Compliance Officers meet ongoing fit-and-proper standards:
- Honesty and integrity – no findings of dishonesty, fraud, or theft
- Competence – current regulatory examinations and 30 CPD hours annually
- Operational ability – systems, controls, and resources to deliver services
- Financial soundness – no insolvency, sequestration, or debt counselling
The FSCA conducts regular fit-and-proper assessments and can withdraw authorisation when standards are breached. Brokers must notify the regulator within 30 days of any changes affecting fit-and-proper status, including criminal charges, civil judgments, or complaints upheld by the Ombud.
FICA Compliance and Risk Management Control Programmes
The Financial Intelligence Centre Act imposes stringent client identification, verification, and transaction monitoring obligations on all FSPs. Financial services regulatory compliance under FICA aims to prevent money laundering, terrorist financing, and other financial crimes.
Customer Due Diligence Obligations
FICA establishes three tiers of customer due diligence, each triggered by risk factors and transaction characteristics:
Standard Due Diligence applies to all client relationships and requires:
- Full name, date of birth, and identification number
- Residential or business address (verified)
- Source of funds and nature of business relationship
- Copy of identity document or company registration
Enhanced Due Diligence is mandatory for high-risk clients, including politically exposed persons (PEPs), cash-intensive businesses, and clients from high-risk jurisdictions. Enhanced measures include senior management approval, ongoing monitoring, and source-of-wealth verification.
Simplified Due Diligence may apply to low-risk scenarios such as small premium policies or clients from low-risk regulated entities, subject to documented risk assessment.
Risk Management and Compliance Programme (RMCP)
Every FSP must develop, document, and implement a Risk Management and Compliance Programme that addresses the institution's specific money laundering and terrorism financing risks. The RMCP serves as the operational blueprint for FICA compliance.
A compliant RMCP includes:
- Risk assessment methodology covering products, delivery channels, clients, and geographic risk
- Client acceptance policy defining due diligence requirements for each risk category
- Ongoing monitoring procedures for detecting suspicious transactions and patterns
- Record-keeping standards ensuring five-year retention of identification and transaction records
- Training programme for all staff handling client onboarding or transactions
- Independent testing through annual compliance audits or reviews
Many independent brokers underestimate the complexity of RMCP development. The World Bank’s good practice note on AML/CFT risk management provides frameworks applicable to financial intermediaries, emphasising risk-based approaches tailored to institutional size and complexity.
Suspicious Transaction Reporting
Financial services regulatory compliance requires FSPs to identify and report suspicious and unusual transactions to the Financial Intelligence Centre. A transaction is suspicious when it raises concerns about money laundering, terrorist financing, or proceeds of crime, regardless of the amount.
Common indicators in insurance broking include:
- Clients requesting early policy termination and cash refunds
- Premium payments from third parties with no clear relationship to the policyholder
- Overpayments followed by refund requests
- Investment products selected with no regard to investment performance or client objectives
- Inconsistent client information or reluctance to provide standard documentation
Reports must be filed within 15 days of forming the suspicion. Tipping off the client about a report constitutes a criminal offence punishable by fines or imprisonment.
POPIA Compliance for Financial Service Providers
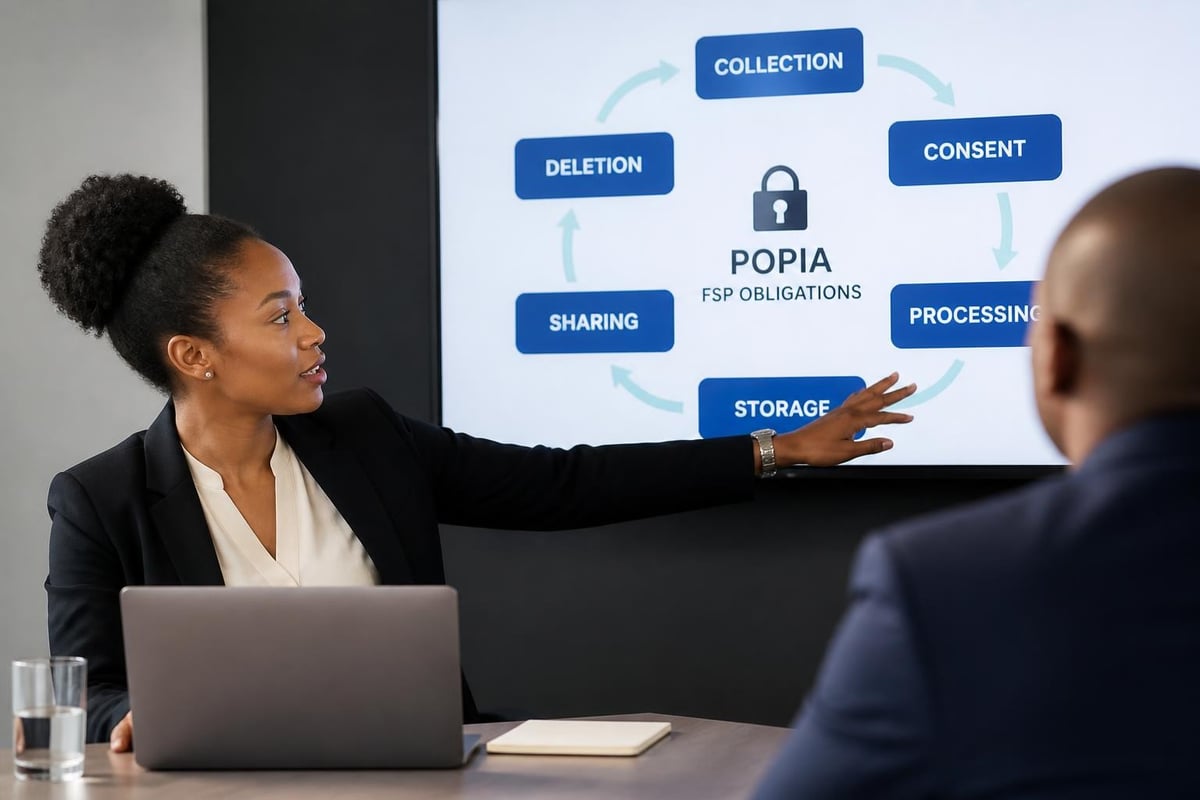
The Protection of Personal Information Act transformed how FSPs handle client data. Financial services regulatory compliance now demands comprehensive data governance, transparent processing notices, and robust security measures.
Eight Lawful Processing Conditions
POPIA establishes eight conditions for lawful processing of personal information:
| Condition | Core Requirement | Broker Application |
|---|---|---|
| Accountability | Appoint Information Officer, document compliance | Information Officer registration, POPIA manual |
| Processing limitation | Lawful, reasonable, necessary for purpose | Process only data needed for advice/administration |
| Purpose specification | Clear purpose at collection, documented | Privacy notices explaining use of client data |
| Further processing limitation | Compatible with original purpose | No marketing without consent |
| Information quality | Accurate, complete, up-to-date | Regular data cleansing and verification |
| Openness | Transparent about collection and use | Privacy policy on website and in agreements |
| Security safeguards | Protect against loss, damage, unauthorised access | Encryption, access controls, breach response plan |
| Data subject participation | Access, correction, deletion rights | Process for client data requests within 30 days |
Consent Requirements and Marketing
POPIA distinguishes between explicit consent (required for direct marketing and processing special personal information) and implied consent (acceptable for purposes necessary to service relationship).
For independent brokers, critical consent scenarios include:
- Marketing communications – explicit opt-in required; opt-out mechanism in every message
- Sharing data with product providers – disclosed in privacy notice; necessary for service delivery
- Third-party services – data processor agreements required with software vendors, call centres
- Special personal information – explicit consent needed for health data in life insurance applications
Pre-ticked boxes do not constitute valid consent. Consent must be specific, informed, and freely given. Brokers bundling consent with service agreements risk POPIA violations.
Data Security and Breach Response
FSPs must implement appropriate technical and organisational measures to protect personal information, considering the nature of the data and harm from security compromise. Minimum security safeguards include:
- Access controls limiting data access to authorised personnel only
- Encryption for data in transit and sensitive data at rest
- Password policies enforcing complexity and regular changes
- Physical security for paper records and server infrastructure
- Backup and recovery ensuring business continuity
- Vendor management through data processor agreements and security audits
When a data breach occurs-whether through cyber-attack, employee error, or physical theft-FSPs must notify the Information Regulator and affected data subjects as soon as reasonably possible. Notification triggers when breach may cause harm (financial loss, identity theft, reputational damage).
COFI and Conduct Standards Implementation
The Conduct of Financial Institutions Bill represents the most significant shift in South Africa's financial services regulatory compliance framework in two decades. COFI replaces portions of FAIS and establishes comprehensive conduct standards for all financial institutions and intermediaries.
Product Design and Value Assessment
COFI introduces mandatory product value assessments requiring FSPs to evaluate whether products meet the needs of target customers and provide fair value. Financial intermediaries must consider:
- Product features, benefits, and limitations relative to customer needs
- Pricing and cost structures compared to alternatives
- Complexity and customer understanding
- Distribution methods and advice requirements
Products failing value assessments must be withdrawn or redesigned. Brokers recommending poor-value products may face regulatory action even when technically disclosing all fees and terms.
Treating Customers Fairly (TCF) Outcomes
COFI embeds the six TCF outcomes as enforceable standards:
- Outcome 1: Fair culture across the institution
- Outcome 2: Products designed to meet customer needs
- Outcome 3: Clear communication and appropriate advice
- Outcome 4: Suitable product recommendations
- Outcome 5: Product performance meets expectations
- Outcome 6: No unreasonable barriers to switching, claims, or complaints
Financial services regulatory compliance under COFI requires documented evidence that customer outcomes are achieved, not merely that processes are followed. This shifts regulatory focus from box-ticking to substantive customer treatment.
Remuneration and Conflicts of Interest
COFI imposes detailed requirements on remuneration structures to mitigate conflicts of interest. Key provisions include:
- Disclosure of all remuneration received from product providers
- Remuneration structures that do not incentivise unsuitable advice
- Prohibition of remuneration contingent on excluding product alternatives
- Enhanced disclosure for cross-selling and bundled products
Independent brokers must review commission structures, override agreements, and incentive arrangements to ensure COFI compliance before implementation dates.
Building a Practical Compliance Management System
Effective financial services regulatory compliance requires more than policy documents-it demands embedded workflows, regular monitoring, and continuous improvement. Independent brokers need practical systems that integrate compliance into daily operations without overwhelming small teams.
Compliance Calendar and Task Management
A structured compliance calendar ensures critical obligations are never missed. Essential recurring tasks include:
Monthly
- Review new client onboarding for FICA compliance
- Monitor transaction reports for suspicious patterns
- Update representative authorisations for new joiners or departures
Quarterly
- Submit regulatory returns to FSCA (if applicable)
- Review complaints register and identify trends
- Conduct POPIA data quality audits
Annually
- Renew FSP licence and pay regulatory fees
- Complete compliance officer report to Board/principal
- Deliver FICA and POPIA training to all staff
- Conduct internal compliance audit
- Review and update RMCP based on risk assessment
Digital compliance management platforms can automate reminders, document workflow approvals, and generate evidence for regulatory inspections.
Document Management and Record Retention
Financial services regulatory compliance creates extensive documentation obligations. Minimum retention periods include:
| Document Type | Retention Period | Regulatory Source |
|---|---|---|
| Client files and advice records | 5 years from termination | FAIS |
| FICA identification documents | 5 years from termination | FICA |
| Transaction records | 5 years from transaction | FICA |
| Marketing materials | 5 years from last use | FAIS |
| Complaints files | 5 years from resolution | FAIS |
| Personal information (no ongoing relationship) | Reasonable period for purpose | POPIA |
Cloud storage solutions offer cost-effective retention with appropriate security controls, provided data processor agreements address POPIA requirements. Physical records must be stored securely with controlled access and destruction protocols.
Staff Training and Competency Management
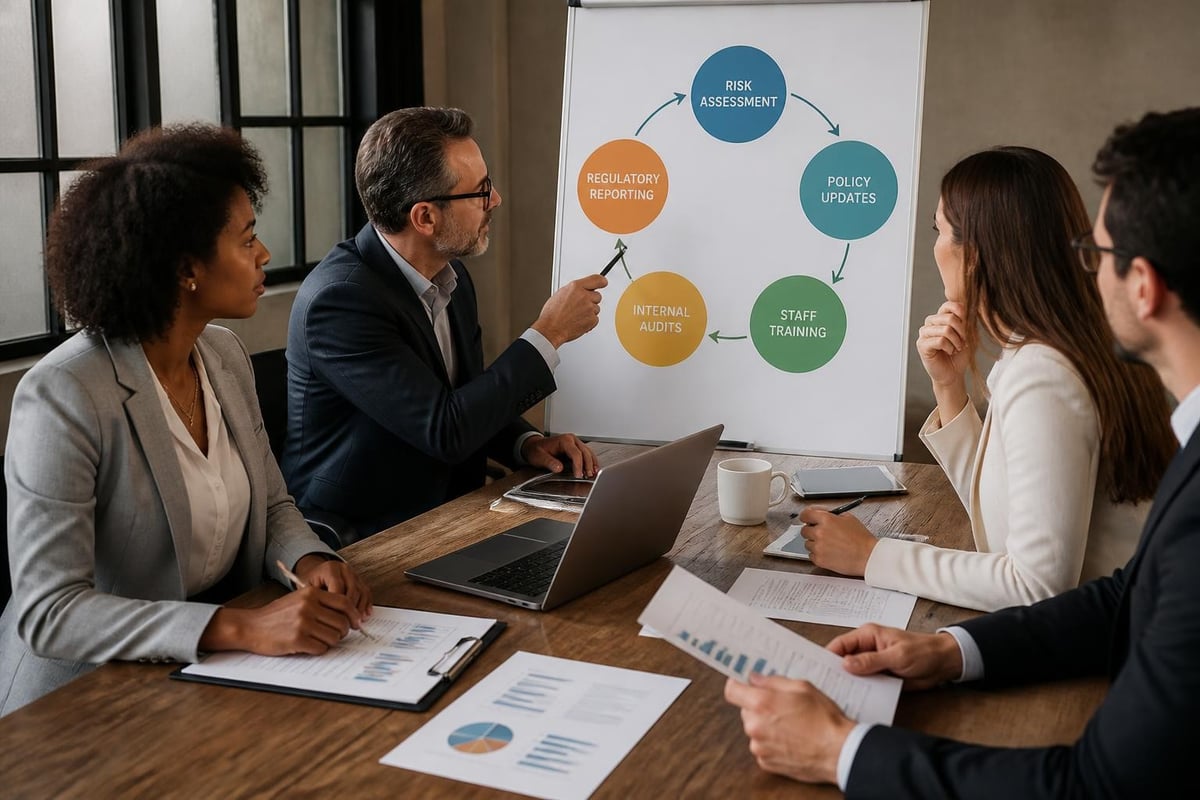
Compliance failures often stem from staff knowledge gaps rather than intentional misconduct. Comprehensive training programmes address:
- Induction training covering FAIS, FICA, POPIA, and COFI obligations for new representatives
- Product training on features, risks, and target markets for each product range
- Scenario-based training using case studies to identify conflicts, FICA red flags, and POPIA breaches
- Regulatory update sessions when legislation or conduct standards change
- Annual refresher training maintaining awareness and reinforcing standards
Training must be documented with attendance registers, assessment results, and competency sign-offs. The FSCA increasingly reviews training records during inspections to assess compliance culture.
Compliance Monitoring and Internal Audits
Proactive monitoring identifies compliance gaps before they escalate into regulatory breaches or client complaints. Financial services regulatory compliance programmes should include both ongoing monitoring and periodic internal audits.
File Review Programmes
Regular file reviews assess whether advice processes deliver compliant customer outcomes. Effective review programmes sample files across:
- Different representatives to identify individual training needs
- Product types to detect systemic advice gaps
- Client risk profiles (high-net-worth, vulnerable customers, complex needs)
- New business and policy servicing to cover the full client lifecycle
Review criteria should assess:
- FICA compliance – identification verified, source of funds documented, risk rating appropriate
- Needs analysis – comprehensive fact-finding covering objectives, circumstances, risk tolerance
- Product suitability – recommendation aligns with needs, alternatives considered, switching justified
- Disclosure quality – fees, conflicts, product risks clearly explained in plain language
- Record quality – file documents the advice process, customer understanding, and decisions
Results feed into training plans, process improvements, and representative performance management. Persistent file quality issues may indicate inadequate supervision or representative competence concerns requiring FSCA notification.
Internal Audit Scope and Methodology
Annual internal audits provide independent assessment of compliance programme effectiveness. Whilst small brokerages may lack dedicated internal audit functions, engaging external compliance specialists ensures objectivity and technical expertise.
Audit scope should cover:
- Licensing status and representative authorisations
- RMCP implementation and suspicious transaction identification
- POPIA compliance including consent management, security controls, and breach readiness
- Complaints handling and Ombud determinations
- Treating Customers Fairly outcomes evidence
- Financial soundness and operational ability
Audit findings should be formally reported to the FSP's governing body or principal, with management responses addressing identified deficiencies within defined timeframes. The U.S. guidance on financial institution compliance illustrates comprehensive audit methodologies adaptable to South African intermediary contexts.
Managing Regulatory Change and Updates
South Africa's financial services regulatory compliance environment evolves continuously through new legislation, regulatory notices, guidance notes, and case law. Staying current requires structured monitoring and rapid implementation.
Information Sources and Monitoring
Reliable compliance monitoring depends on tracking multiple information channels:
- FSCA website and regulatory notices – official pronouncements on licensing, conduct standards, enforcement
- Information Regulator guidance – POPIA interpretations and enforcement priorities
- FIC guidance notes – sector-specific FICA requirements and typologies
- Industry associations – regulatory updates and compliance best practices shared through bodies like the FPI or ASISA
- Legal updates – court decisions interpreting regulatory obligations
Compliance officers should consolidate updates into regular briefings for management and representatives, highlighting changes affecting practice operations or client engagement.
Impact Assessment and Implementation
When regulatory changes are announced, structured impact assessment prevents rushed, incomplete implementation:
- Identify affected areas – Which products, processes, or client segments are impacted?
- Gap analysis – What changes to policies, procedures, systems, or training are required?
- Implementation plan – Who is responsible, what resources are needed, what is the timeline?
- Communication strategy – How will clients, staff, and service providers be informed?
- Monitoring and review – How will compliance with new requirements be verified?
The CFPB’s compliance resources demonstrate how consumer protection regulators communicate expectations and support implementation, offering models for South African FSPs navigating COFI implementation.
Technology and Compliance Automation
Digital transformation offers significant opportunities to streamline financial services regulatory compliance whilst reducing human error and operational costs. Independent brokers should evaluate technology solutions across several domains.
Client Onboarding and FICA Verification
Digital onboarding platforms integrate FICA verification, risk assessment, and documentation into seamless customer experiences. Capabilities include:
- Electronic identity verification using Home Affairs databases and biometric matching
- Automated risk scoring based on client profile, product selection, and transaction patterns
- Digital signature capture creating enforceable records without paper processing
- Workflow automation routing high-risk applications for enhanced due diligence
These systems reduce onboarding time from days to minutes whilst creating comprehensive audit trails demonstrating FICA compliance.
POPIA Compliance Tools
Data protection compliance demands robust systems for consent management, data subject requests, and security monitoring:
- Consent management platforms capturing, storing, and tracking opt-ins for marketing and data processing
- Data mapping tools identifying where personal information is stored across systems and service providers
- Automated deletion workflows expunging data when retention periods expire or subjects withdraw consent
- Breach detection systems alerting to unusual access patterns, data exports, or security anomalies
Integration with existing CRM and policy administration systems ensures POPIA controls apply to all personal information processing.
Compliance Reporting and Dashboard Tools
Management oversight requires consolidated visibility across multiple compliance dimensions. Dashboard solutions provide:
| Metric Category | Key Indicators | Management Use |
|---|---|---|
| Licensing | Representative authorisations, exam expiry dates, CPD completion | Proactive renewal, training planning |
| FICA | CDD completion rates, pending verifications, STR submissions | Quality assurance, FIC audit readiness |
| POPIA | Consent rates, outstanding data requests, security incidents | Privacy risk management |
| Complaints | Complaint volumes, resolution times, Ombud escalations | Service quality, process improvement |
| Advice quality | File review scores, unsuitable advice flags | Training needs, representative performance |
Real-time dashboards enable early intervention when metrics deteriorate, preventing minor issues from becoming regulatory breaches.
Common Compliance Pitfalls and Risk Mitigation
Despite best intentions, independent brokers frequently encounter recurring compliance challenges. Understanding common pitfalls enables proactive risk mitigation.
Inadequate Needs Analysis Documentation
Representatives often conduct thorough verbal fact-finding but fail to document comprehensive needs analysis. When complaints arise years later, missing documentation makes defending advice suitability nearly impossible.
Mitigation strategies:
- Standardised needs analysis templates covering all material client circumstances
- Mandatory fields in CRM systems preventing file completion without key data points
- File review programmes focusing on documentation quality, not just technical compliance
- Regular training on documentation standards and litigation risk
Delayed Regulatory Notifications
FAIS requires FSPs to notify the FSCA within 30 days of events affecting licensing status, fit-and-proper requirements, or material compliance breaches. Common missed notifications include:
- Representative resignations or terminations
- Criminal charges against representatives or key individuals
- Complaints upheld by the Ombud for Financial Services Providers
- Material changes to business structure or ownership
- Compliance officer resignations
Late notifications trigger separate regulatory contraventions beyond the underlying issue. Diarised notification reviews and clear escalation protocols ensure timely reporting.
Third-Party Service Provider Oversight
Outsourcing compliance functions or administrative services does not transfer regulatory accountability. FSPs remain fully responsible for all regulatory obligations, regardless of operational arrangements.
Many brokers fail to:
- Conduct due diligence on service provider compliance capabilities and track records
- Document service agreements addressing regulatory responsibilities, audit rights, and performance standards
- Monitor service provider performance through regular reviews and audit reports
- Maintain direct relationships with clients despite administrative outsourcing
The OCC’s guidance on third-party risk management provides frameworks applicable to financial intermediaries ensuring vendor relationships support rather than undermine compliance.
Inconsistent Complaint Handling
Financial services regulatory compliance demands systematic complaint management, yet many brokerages treat complaints as isolated incidents rather than potential indicators of systemic issues.
Robust complaint processes require:
- Clear escalation criteria defining what constitutes a complaint versus general service query
- Centralised complaint register capturing all complaints regardless of initial contact point
- Root cause analysis identifying whether complaints reflect individual errors or process failures
- Timely resolution with 30-day acknowledgement and 6-week resolution targets
- Trend analysis quarterly reviews identifying patterns requiring process changes or training
- Ombud notification when complaints cannot be resolved or involve material compliance issues
Navigating financial services regulatory compliance in South Africa requires comprehensive systems, ongoing vigilance, and deep technical knowledge across POPIA, FICA, FAIS, and COFI. Independent brokers and FSPs who embed compliance into operational workflows-rather than treating it as administrative overhead-build more resilient practices and stronger client relationships.
Who this is for: Independent financial brokers, regulated FSP compliance officers, and advisory practices seeking structured FICA risk management.
Holistic Compliance Management Solutions (Pty) Ltd provides independent compliance support tailored to the realities of broker operations. Schedule FICA training to ensure your practice meets all risk management obligations:
- Comprehensive FICA and RMCP drafting assistance aligned to your business model and risk profile
- Practical training sessions equipping your team to identify suspicious transactions and complete proper customer due diligence
- Ongoing compliance monitoring identifying gaps before they become regulatory issues