Compliance as a Service: Modern Solutions for 2026
Organizations across every industry face an unprecedented regulatory burden in 2026. Managing compliance requirements internally demands significant resources, specialized expertise, and constant vigilance as regulations evolve. Compliance as a service has emerged as a strategic solution, enabling businesses to access professional compliance management without maintaining extensive internal teams. This service delivery model transforms compliance from a resource-intensive burden into a manageable, scalable business function that adapts to changing regulatory landscapes while protecting organizations from costly violations and reputational damage.
Understanding the Compliance as a Service Model
Compliance as a service represents a fundamental shift in how organizations approach regulatory requirements. Rather than building internal compliance departments, businesses partner with specialized providers who deliver comprehensive compliance management through subscription-based or contracted arrangements. This model provides access to compliance expertise, technology platforms, monitoring systems, and reporting frameworks without the capital investment required for internal programs.
The service encompasses multiple critical functions that work together seamlessly. Organizations receive regulatory monitoring, policy development, employee training, audit preparation, and ongoing advisory support. These components integrate to create a continuous compliance posture rather than sporadic compliance activities.
Key Components of Service Delivery
Modern compliance as a service offerings include several essential elements that distinguish them from traditional consulting:
- Continuous regulatory monitoring that tracks changes across relevant frameworks
- Automated compliance controls integrated with existing business systems
- Real-time reporting dashboards providing visibility into compliance status
- Expert advisory services offering interpretation and implementation guidance
- Training and awareness programs ensuring organizational understanding
- Incident response protocols addressing compliance breaches quickly
Financial service providers particularly benefit from these comprehensive approaches, as they navigate complex requirements under frameworks like FICA and POPI. The compliance services offered by specialized providers deliver targeted support that addresses sector-specific challenges while maintaining cost efficiency.
The Business Case for Outsourced Compliance
Organizations evaluating compliance as a service must consider both quantitative and qualitative benefits. The financial advantages extend beyond simple cost reduction to encompass risk mitigation, operational efficiency, and strategic flexibility. Continuous compliance management provides ongoing protection rather than point-in-time assessments that quickly become outdated.
Internal compliance programs require substantial investments across multiple categories. Personnel costs include salaries for compliance officers, auditors, and support staff. Technology expenses encompass compliance management platforms, monitoring tools, and reporting systems. Training costs multiply as organizations must maintain current expertise across evolving regulatory frameworks.
Cost Comparison Analysis
| Cost Category | Internal Program | Compliance as a Service | Annual Savings |
|---|---|---|---|
| Personnel | $250,000-$500,000 | $60,000-$120,000 | 60-76% |
| Technology | $50,000-$150,000 | Included in service | 100% |
| Training | $25,000-$75,000 | Included in service | 100% |
| Audit Preparation | $40,000-$100,000 | $10,000-$25,000 | 75% |
| Total Annual | $365,000-$825,000 | $70,000-$145,000 | 70-82% |
These figures demonstrate substantial financial advantages, particularly for small to medium-sized organizations. Larger enterprises may realize different savings ratios but still benefit from reduced overhead and increased flexibility. The service model converts fixed costs into variable expenses that scale with organizational needs.
Regulatory Frameworks and Coverage Areas
Compliance as a service providers must demonstrate expertise across the regulatory frameworks relevant to their clients. In 2026, the complexity and interconnection of these frameworks demand specialized knowledge that most organizations cannot maintain internally. Providers develop deep expertise in specific sectors while maintaining awareness of cross-industry requirements.
Financial services organizations face particularly dense regulatory environments. Requirements span consumer protection, data privacy, anti-money laundering, know-your-customer protocols, and market conduct standards. Automated compliance engines now quantify regulatory compliance as dynamic trust metrics, providing nuanced assessments beyond traditional binary pass-fail evaluations.
Common Regulatory Frameworks
- Financial Services Regulations: FICA, POPI, market conduct rules, and FSP licensing requirements
- Data Protection Standards: GDPR, CCPA, sector-specific privacy regulations, and data sovereignty rules
- Industry-Specific Requirements: Healthcare HIPAA, payment card PCI-DSS, manufacturing safety standards
- Information Security Frameworks: ISO 27001, SOC 2, NIST Cybersecurity Framework
- Occupational Health and Safety: Workplace safety regulations, training requirements, incident reporting
The FICA RMCP compliance practice demonstrates how specialized services address specific regulatory requirements for insurance brokers and other financial intermediaries. This targeted approach ensures comprehensive coverage while maintaining efficiency through focused expertise.
Technology Infrastructure and Automation
Modern compliance as a service relies heavily on sophisticated technology platforms that automate routine tasks, monitor controls continuously, and provide real-time visibility. Fully managed compliance services leverage automation to maintain continuous compliance rather than periodic assessment cycles.
The technology stack typically includes several integrated components working together. Regulatory intelligence systems track changes across relevant frameworks and jurisdictions. Control monitoring platforms continuously assess organizational compliance with established policies and procedures. Risk assessment engines evaluate emerging threats and prioritize mitigation efforts.
Essential Technology Capabilities
Effective compliance as a service platforms deliver specific capabilities that distinguish professional offerings:
- Automated evidence collection gathering documentation without manual intervention
- Control testing automation validating compliance controls on scheduled intervals
- Policy lifecycle management tracking policy versions, approvals, and acknowledgments
- Integrated workflow systems routing tasks to appropriate personnel automatically
- Exception tracking mechanisms identifying and escalating compliance gaps
- Reporting customization options generating stakeholder-specific compliance views
Policy-driven enforcement layers for AI systems demonstrate how automated controls can regulate outputs at runtime without altering underlying models. This approach ensures compliance in autonomous systems while maintaining operational efficiency.
Continuous Monitoring and Risk Management
The shift from periodic audits to continuous monitoring represents one of the most significant advantages of compliance as a service. Traditional compliance programs conduct annual or quarterly assessments that create substantial gaps in visibility. Continuous monitoring provides real-time awareness of compliance status and enables immediate response to emerging issues.
Risk management integrates seamlessly with compliance monitoring through modern service platforms. Organizations receive ongoing risk assessments that evaluate both inherent and residual risk across their operational landscape. These assessments inform prioritization decisions and resource allocation to address the most significant compliance challenges first.
| Monitoring Approach | Assessment Frequency | Detection Speed | Resource Intensity | Compliance Gaps |
|---|---|---|---|---|
| Annual Audits | Once yearly | 6-12 months | High (periodic spike) | Significant |
| Quarterly Reviews | Four times yearly | 2-3 months | High (periodic spikes) | Moderate |
| Continuous Monitoring | Real-time | Immediate | Low (distributed) | Minimal |
Automated analysis of SLA compliance in cloud services demonstrates how formal models integrate with static analysis tools and runtime monitors. Similar approaches apply to regulatory compliance, creating verifiable compliance claims that withstand scrutiny.
Implementation and Onboarding Process
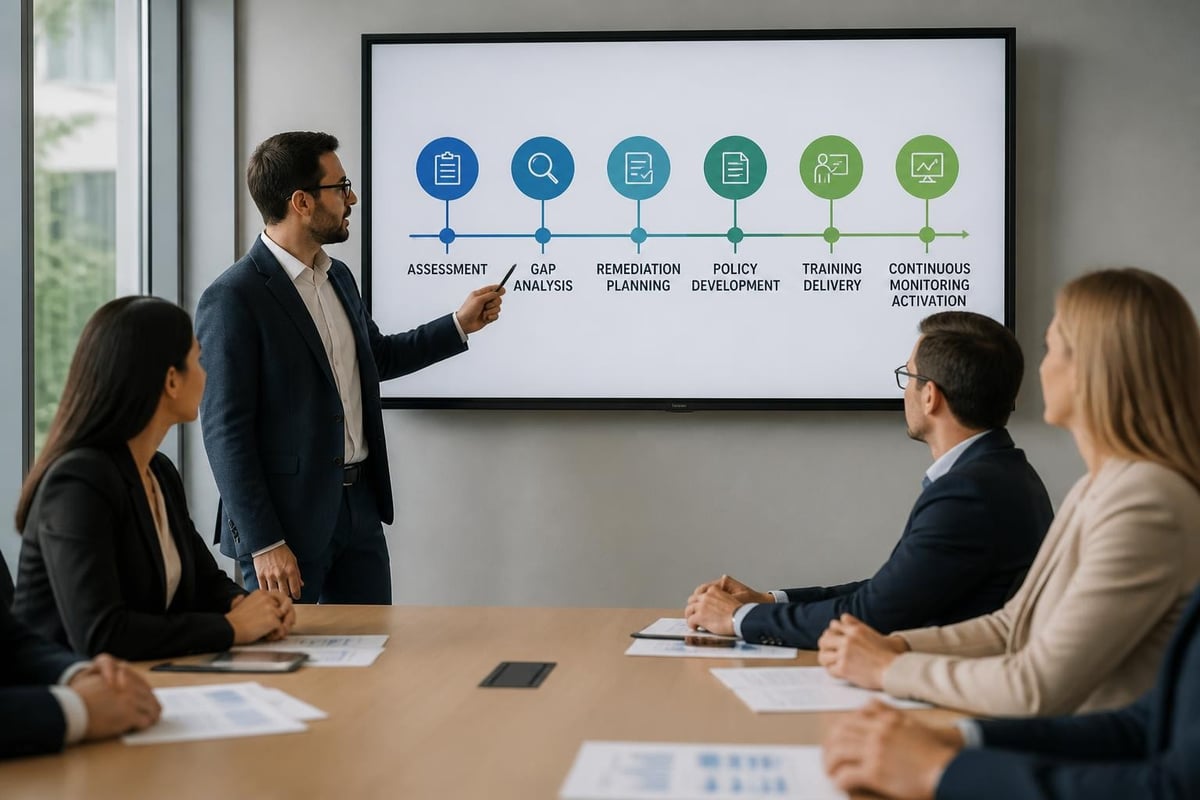
Organizations adopting compliance as a service follow structured implementation processes that minimize disruption while establishing effective compliance frameworks. The onboarding phase typically spans 60 to 90 days, depending on organizational complexity and existing compliance maturity.
Initial assessment activities establish baseline understanding of current compliance posture. Service providers evaluate existing policies, procedures, controls, and documentation. This assessment identifies gaps against relevant regulatory requirements and establishes priorities for remediation efforts.
Typical Implementation Timeline
- Weeks 1-2: Initial assessment and scope definition, stakeholder interviews, documentation review
- Weeks 3-4: Gap analysis completion, remediation planning, technology platform configuration
- Weeks 5-6: Policy development or refinement, control framework establishment, workflow design
- Weeks 7-8: Training program delivery, system testing, pilot monitoring period
- Weeks 9-12: Full deployment, continuous monitoring activation, reporting establishment
Organizations should expect active involvement during implementation. Subject matter experts must participate in interviews and validation activities. Leadership teams review and approve policies, risk tolerances, and escalation procedures. Operational staff receive training on new processes and systems.
Selecting the Right Service Provider
The compliance as a service market has expanded significantly in recent years, creating numerous provider options with varying capabilities and specializations. Organizations must evaluate potential partners carefully to ensure alignment with their specific needs, industry requirements, and organizational culture.
Provider selection criteria should address both technical capabilities and service delivery characteristics. Technical evaluation focuses on platform functionality, automation capabilities, regulatory expertise, and integration options. Service delivery assessment examines responsiveness, communication practices, reporting quality, and relationship management approaches.
Critical Evaluation Criteria
Organizations should assess potential providers across multiple dimensions:
- Industry expertise demonstrating deep knowledge of relevant regulatory frameworks
- Technology maturity offering robust platforms with proven automation capabilities
- Service level commitments providing clear performance guarantees and response times
- Scalability options supporting organizational growth and changing requirements
- Reference customers showing successful engagements with similar organizations
- Pricing transparency delivering clear cost structures without hidden fees
Comprehensive compliance service offerings emphasize continuous compliance over one-time audits, reflecting the evolution from periodic assessment to ongoing posture management. This approach aligns with regulatory expectations in 2026 and beyond.
Integration with Existing Systems
Successful compliance as a service implementations require seamless integration with organizational systems and processes. Isolated compliance programs create inefficiencies and increase the likelihood of gaps between compliance documentation and operational reality. Modern service providers prioritize integration capabilities that embed compliance into business operations.
Technical integration encompasses connections to core business systems, data repositories, communication platforms, and security tools. These integrations enable automated evidence collection, reduce manual data entry, and ensure compliance activities reflect actual operational conditions rather than theoretical documentation.
Integration Architecture Components
| System Category | Integration Purpose | Data Exchange | Update Frequency |
|---|---|---|---|
| HR Systems | Employee onboarding, training tracking, role changes | Bidirectional | Daily |
| Financial Systems | Transaction monitoring, approval workflows | Inbound | Real-time |
| IT Infrastructure | Access controls, security configurations | Inbound | Continuous |
| Document Management | Policy distribution, acknowledgment tracking | Bidirectional | Event-based |
| Communication Tools | Incident notifications, approval requests | Outbound | Real-time |
Verifiable SLA violation claims generated through trusted hardware monitors and zero-knowledge proofs demonstrate advanced integration approaches that enhance trustworthiness. Similar techniques apply to compliance verification, creating auditable trails that satisfy regulatory scrutiny.
Measuring Success and ROI
Organizations investing in compliance as a service must establish clear success metrics that demonstrate value and justify ongoing investment. Measurement frameworks should address both compliance outcomes and operational efficiency improvements. Scalable compliance platforms emphasize metrics that demonstrate both profitability and effectiveness.
Quantitative metrics provide objective assessment of compliance program performance. These include compliance control effectiveness rates, audit finding frequencies, incident response times, and regulatory violation occurrences. Financial metrics track cost per compliant entity, investment avoidance through proactive management, and penalty prevention savings.
Key Performance Indicators
Organizations should monitor compliance as a service effectiveness through comprehensive KPI frameworks:
- Control effectiveness rate: Percentage of compliance controls operating as designed
- Gap closure velocity: Average time to remediate identified compliance gaps
- Audit readiness score: Preparedness assessment based on documentation completeness
- Training completion rate: Percentage of required personnel completing compliance training
- Incident detection speed: Time from control failure to identification and escalation
- Regulatory change adaptation: Time from regulatory update to policy implementation
Qualitative benefits often exceed quantitative savings but prove harder to measure. Reduced compliance-related stress for leadership teams, improved organizational reputation, enhanced customer confidence, and easier access to capital all contribute substantial value. Organizations should document these benefits through stakeholder surveys and business opportunity tracking.
Future Trends in Service Delivery
The compliance as a service market continues evolving rapidly as technology advances and regulatory expectations increase. Organizations evaluating long-term compliance strategies must consider emerging trends that will shape service delivery in coming years. Providers investing in these capabilities position themselves as forward-thinking partners rather than transactional vendors.
Artificial intelligence and machine learning increasingly automate compliance activities that previously required human judgment. Natural language processing analyzes regulatory updates and identifies impacts on organizational policies. Predictive analytics forecast compliance risks based on operational patterns and environmental factors. Automated response systems remediate certain compliance gaps without human intervention.
Emerging Capabilities and Approaches
- Predictive compliance analytics: Forecasting potential violations before they occur based on operational patterns
- Blockchain-based audit trails: Creating immutable compliance records that satisfy regulatory scrutiny
- Integrated GRC platforms: Combining governance, risk, and compliance into unified management frameworks
- Real-time regulatory intelligence: Delivering immediate notification of relevant regulatory changes
- Collaborative compliance networks: Sharing anonymized compliance insights across industry participants
Comprehensive compliance components including continuous monitoring, risk assessments, and policy management represent current best practices. Future services will extend these foundations with predictive capabilities, autonomous responses, and industry collaboration features that transform compliance from defensive protection to competitive advantage.
Building Internal Capability Alongside Outsourcing
Organizations adopting compliance as a service should not entirely abandon internal compliance capability. Effective models combine external service expertise with internal ownership and oversight. This hybrid approach ensures organizational knowledge development while leveraging specialized provider capabilities.
Internal teams maintain strategic compliance direction, risk tolerance decisions, and organizational policy ownership. External providers deliver operational execution, specialized expertise, technology platforms, and continuous monitoring. This division of responsibilities creates sustainable compliance programs that adapt to organizational growth and changing requirements.
The knowledge transfer component of compliance as a service relationships proves particularly valuable. Organizations should select providers committed to building client capability rather than creating dependency. Regular training, documentation sharing, and collaborative problem-solving develop internal expertise that complements external support.
Modern compliance challenges demand sophisticated, continuous management that most organizations struggle to deliver through internal resources alone. Compliance as a service provides access to specialized expertise, advanced technology platforms, and proven processes that transform compliance from burden to competitive advantage. For organizations seeking to establish sustainable compliance programs without excessive internal investment, partnering with experienced providers delivers measurable value across risk reduction, operational efficiency, and strategic flexibility. Holistic Compliance Management Solutions offers professional compliance management, occupational safety training, and risk management services specifically tailored for Financial Service Providers and modern organizations navigating complex regulatory environments. Contact HCMS today to discover how specialized compliance expertise can support your organization's sustainable growth within evolving regulatory frameworks.