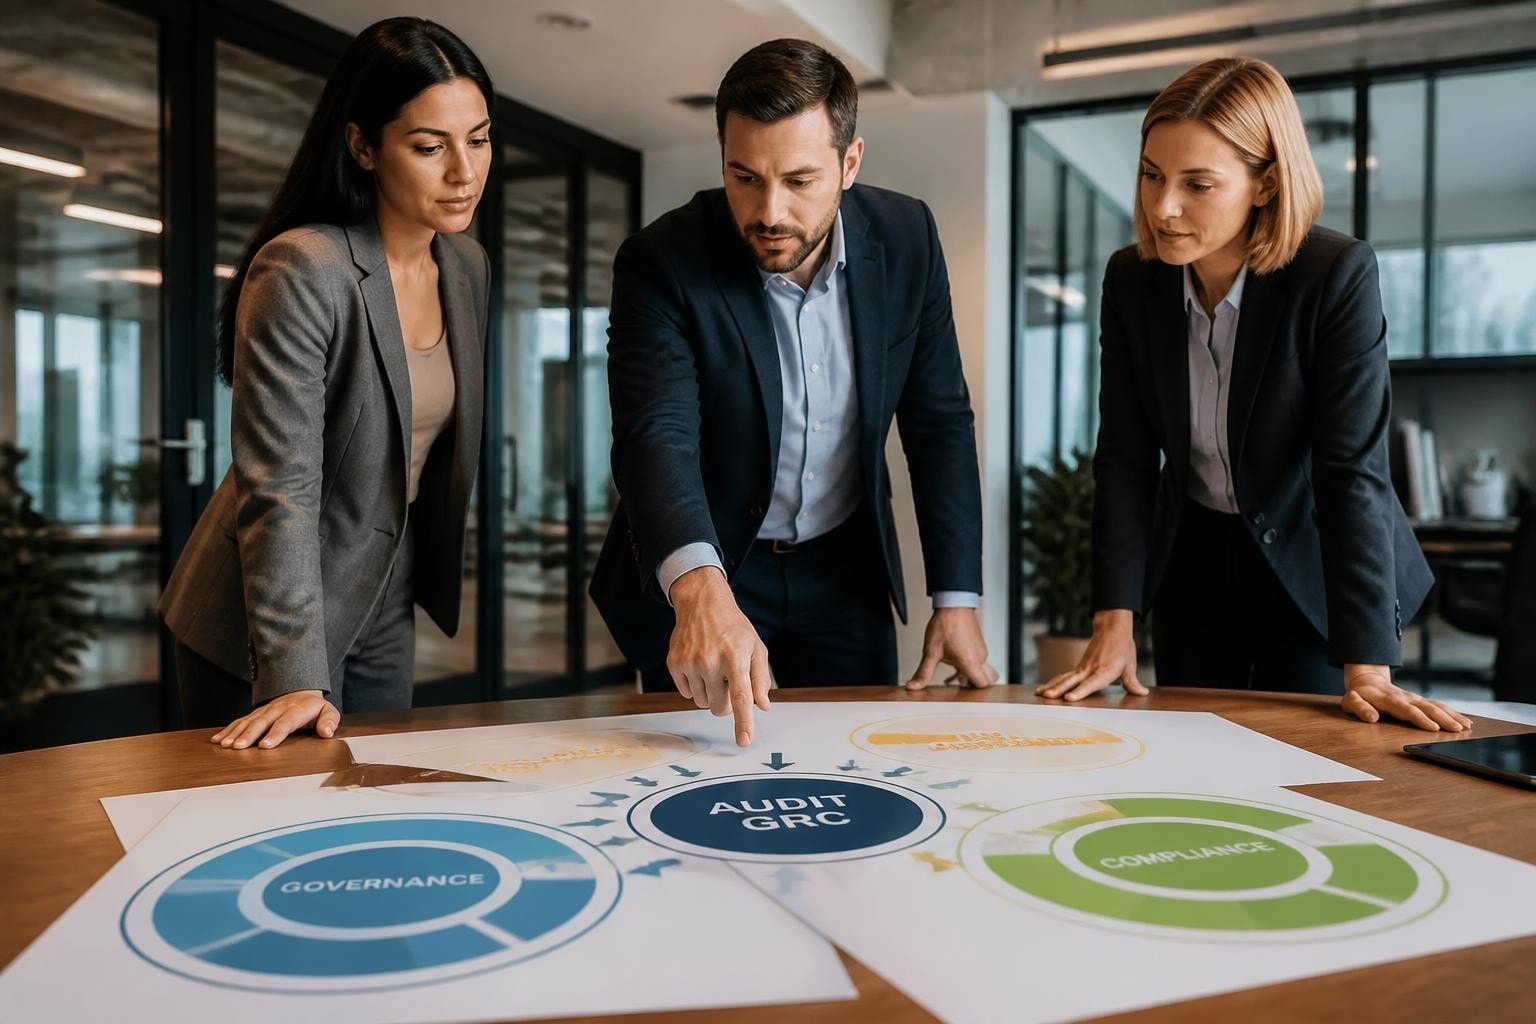
Audit GRC: Essential Framework for Modern Compliance
Organizations today face unprecedented regulatory complexity, operational risks, and governance challenges that demand integrated approaches to oversight and control. The traditional siloed approach to managing these critical functions has proven inadequate, leading forward-thinking enterprises to embrace a comprehensive methodology that unifies governance, risk management, and compliance activities. This strategic convergence, known as audit GRC, represents a fundamental shift in how organizations assess and strengthen their internal controls, regulatory posture, and strategic alignment. For businesses operating in highly regulated sectors, particularly financial services providers, understanding and implementing effective audit GRC practices has become essential to maintaining operational integrity and competitive advantage.
Understanding the Audit GRC Framework
Audit GRC combines three foundational pillars into a cohesive assessment methodology that evaluates organizational effectiveness across multiple dimensions. This integrated approach recognizes that governance structures, risk management processes, and compliance obligations are inherently interconnected and should be examined holistically rather than in isolation.
The governance component examines how organizations establish strategic direction, allocate resources, and maintain accountability throughout their operations. Effective governance ensures that executive leadership, board members, and operational teams work within clearly defined roles and responsibilities that support organizational objectives. Through audit GRC assessments, organizations can identify gaps in decision-making authority, strategic alignment, and stakeholder communication.
Risk management evaluation focuses on how organizations identify, analyze, prioritize, and mitigate threats to their objectives. This encompasses operational risks, financial exposures, reputational concerns, and strategic vulnerabilities. Understanding audit GRC as a strategic approach enables organizations to develop comprehensive risk frameworks that anticipate emerging threats while optimizing resource allocation.
Compliance Assessment Components
The compliance dimension examines adherence to regulatory requirements, industry standards, contractual obligations, and internal policies. For financial services providers, this includes monitoring obligations under financial regulations, data protection laws, and sector-specific requirements. Organizations must demonstrate not only current compliance but also their capacity to adapt to evolving regulatory landscapes.
Compliance assessment within audit GRC extends beyond simple checkbox verification. It evaluates the maturity of compliance programs, the effectiveness of control mechanisms, and the organization's cultural commitment to ethical operations. This comprehensive view helps organizations identify systemic weaknesses that might not appear in traditional compliance reviews.
Strategic Benefits of Integrated Audit GRC
Organizations implementing robust audit GRC practices realize measurable advantages across operational, financial, and strategic dimensions. The integration eliminates redundant activities, reduces assessment fatigue, and provides executive leadership with consolidated insights into organizational health.
Key advantages include:
- Enhanced visibility into interconnected risks and control effectiveness
- Reduced compliance costs through streamlined assessment processes
- Improved resource allocation based on integrated risk priorities
- Strengthened stakeholder confidence through comprehensive oversight
- Faster identification of emerging threats and regulatory changes
- Better alignment between strategic objectives and operational activities
The financial impact of effective audit GRC can be substantial. Organizations avoid costly regulatory penalties, reduce insurance premiums through demonstrated risk management, and optimize operational efficiency by eliminating duplicative controls. More importantly, they build resilience that protects long-term value creation.
Operational Efficiency Through Integration
Traditional approaches often require separate teams conducting governance reviews, risk assessments, and compliance audits. This fragmentation creates coordination challenges, inconsistent findings, and competing priorities for operational teams. Audit GRC consolidates these activities into unified assessment cycles that provide holistic insights while minimizing disruption.
Integration also improves data quality and consistency. When governance, risk, and compliance teams share common frameworks, terminology, and assessment criteria, organizations develop more reliable metrics for measuring performance and tracking improvements over time. This consistency proves particularly valuable when demonstrating compliance to regulators or providing assurance to stakeholders.
Implementing Effective Audit GRC Processes
Successful audit GRC implementation requires methodical planning, appropriate technology infrastructure, and organizational commitment to integrated oversight. Organizations should begin by mapping existing governance, risk, and compliance activities to identify redundancies, gaps, and opportunities for consolidation.
The implementation process typically follows these sequential steps:
- Assess current state maturity across governance, risk, and compliance functions
- Define integrated objectives that align with strategic priorities and regulatory obligations
- Develop unified assessment frameworks incorporating relevant standards and regulations
- Establish cross-functional teams representing governance, risk, compliance, and operational areas
- Select appropriate technology platforms that support integrated data collection and analysis
- Create standardized procedures for conducting assessments, documenting findings, and tracking remediation
- Train personnel on integrated methodologies and collaborative approaches
- Execute pilot assessments to validate frameworks and refine processes
- Scale implementation across organizational units and geographic locations
- Continuously monitor and improve based on performance metrics and stakeholder feedback
Technology plays a crucial role in enabling effective audit GRC. Modern platforms provide centralized repositories for policies, controls, risks, and assessment evidence. They automate workflow management, facilitate collaboration among distributed teams, and generate real-time dashboards that provide executive visibility into organizational performance.
Best Practices for GRC Audit Excellence
Organizations achieving superior results from their audit GRC programs consistently apply proven practices that enhance effectiveness, efficiency, and stakeholder value. Following essential best practices for GRC auditing helps organizations avoid common pitfalls while accelerating maturity development.
Establish Clear Objectives and Scope
Every audit GRC initiative should begin with explicitly defined objectives that connect to organizational strategy and stakeholder expectations. Ambiguous objectives lead to scope creep, misallocated resources, and findings that fail to drive meaningful improvements. Clear objectives also facilitate stakeholder communication and support prioritization decisions throughout the assessment process.
Scope definition should balance comprehensiveness with practical constraints. Organizations must consider available resources, operational disruption tolerance, and the relative importance of different business units or processes. Risk-based scoping ensures that audit GRC activities focus attention on areas with the greatest potential impact.
Maintain Independence and Objectivity
Effective audit GRC requires appropriate separation between assessment teams and operational management. This independence ensures that findings accurately reflect organizational reality rather than politically influenced perspectives. Organizations should establish clear reporting lines that provide audit teams with direct access to governance bodies and protection from operational pressure.
Objectivity also requires diverse perspectives and balanced evaluation criteria. Assessment teams should include members with varied backgrounds, expertise areas, and organizational tenures. This diversity reduces blind spots and challenges assumptions that might otherwise compromise audit quality.
Leverage Risk-Based Prioritization
Not all governance structures, risk exposures, and compliance obligations warrant equal attention. Understanding GRC audits and their benefits emphasizes the importance of risk-based approaches that allocate assessment resources proportionally to potential impact and likelihood of issues.
Risk-based prioritization considers multiple factors:
| Prioritization Factor | Assessment Criteria | Data Sources |
|---|---|---|
| Regulatory impact | Potential fines, sanctions, operational restrictions | Regulatory guidance, enforcement actions, legal analysis |
| Financial exposure | Revenue at risk, cost of control failures, remediation expenses | Financial statements, loss history, insurance claims |
| Operational criticality | Process dependencies, customer impact, recovery time objectives | Business impact analysis, service level agreements |
| Historical performance | Previous audit findings, control test results, incident frequency | Audit reports, compliance tracking systems, risk registers |
| Change velocity | Regulatory updates, technology implementations, organizational restructuring | Change management logs, regulatory monitoring, project plans |
This systematic approach ensures that audit GRC activities deliver maximum value by addressing the most significant organizational exposures first.
Critical Components of Comprehensive GRC Audits
Thorough audit GRC assessments examine multiple dimensions of organizational performance, controls, and capabilities. Each component provides unique insights that contribute to the overall assessment of organizational health and resilience.
Governance Structure Evaluation
Governance assessment examines how organizations establish strategic direction, allocate authority, and maintain accountability. This includes reviewing board composition and effectiveness, executive leadership structures, committee charters, delegation frameworks, and stakeholder communication mechanisms. Internal audit frameworks provide structured approaches for evaluating governance maturity and identifying improvement opportunities.
Effective governance evaluation also considers cultural factors that influence decision-making quality. Organizations with strong governance demonstrate ethical leadership, transparent communication, constructive challenge mechanisms, and alignment between stated values and actual behaviors. These cultural elements often prove more important than formal structures in determining organizational outcomes.
Risk Assessment and Management
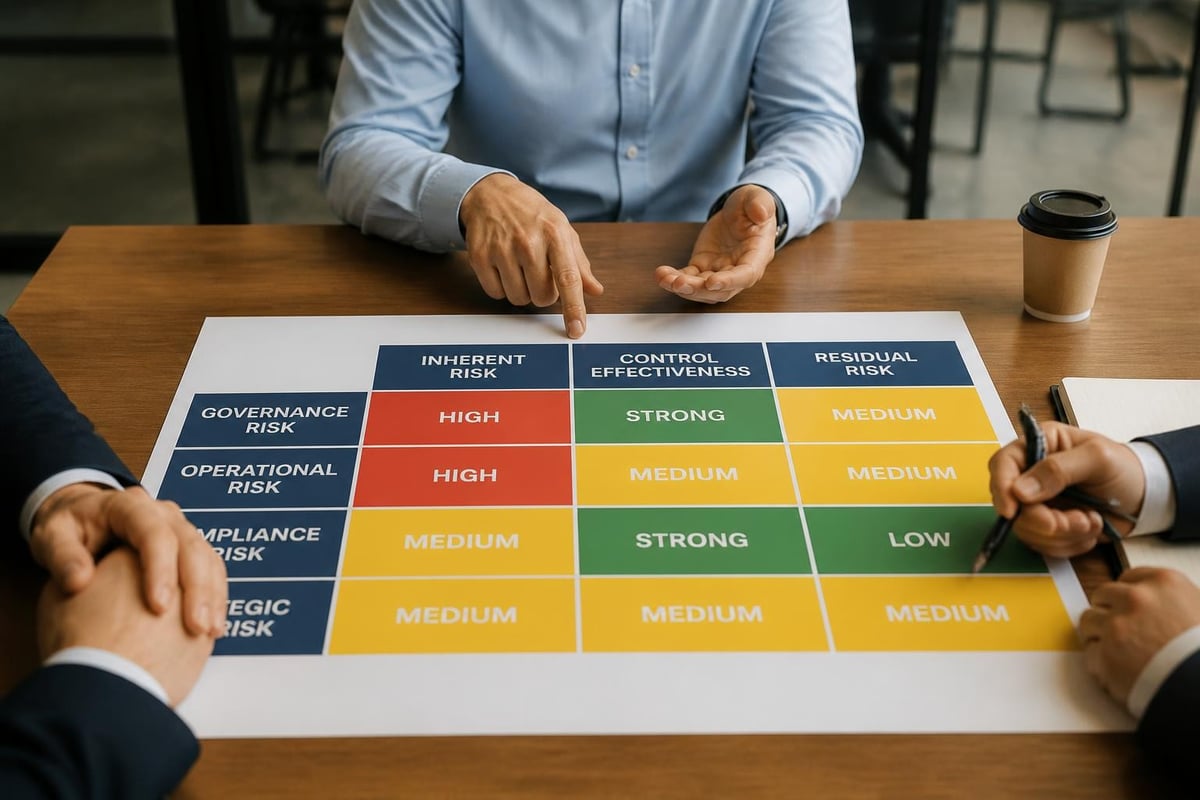
Risk evaluation within audit GRC examines how organizations identify emerging threats, assess their potential impact, prioritize mitigation efforts, and monitor risk exposure over time. This includes reviewing risk assessment methodologies, risk appetite statements, mitigation strategies, and monitoring mechanisms.
Organizations should evaluate both inherent risks (before controls) and residual risks (after controls) to understand control effectiveness. This dual perspective helps identify areas where control investments deliver insufficient risk reduction or where excessive controls create operational inefficiency without commensurate risk benefit.
Compliance Monitoring and Verification
Compliance assessment verifies adherence to applicable regulations, industry standards, contractual obligations, and internal policies. For financial services providers in South Africa, this encompasses requirements under financial sector regulations, data protection laws, anti-money laundering obligations, and sector-specific requirements. Organizations offering FICA RMCP compliance services understand the complexity of maintaining comprehensive compliance programs across multiple regulatory domains.
Effective compliance assessment extends beyond point-in-time verification to evaluate the sustainability of compliance programs. This includes reviewing compliance monitoring processes, training programs, policy update procedures, and escalation mechanisms for potential violations.
Documentation and Reporting Standards
Audit GRC effectiveness depends significantly on the quality of documentation and reporting throughout the assessment process. Comprehensive documentation provides evidence supporting findings, facilitates stakeholder communication, and enables continuous improvement through historical analysis.
Essential documentation elements include:
- Detailed audit plans outlining scope, objectives, methodologies, and timelines
- Comprehensive working papers documenting evidence collection and analysis
- Clear findings statements articulating issues, root causes, and potential impacts
- Actionable recommendations with specific implementation guidance
- Management response documentation capturing agreement and remediation commitments
- Follow-up tracking systems monitoring recommendation implementation progress
Reporting should be tailored to audience needs and decision-making requirements. Executive summaries provide governance bodies with high-level insights and strategic implications. Detailed findings reports give operational management the specifics needed for remediation planning. Trend reports help organizations track performance improvements and identify emerging patterns requiring attention.
Technology Enablement and Automation
Modern audit GRC programs increasingly rely on technology platforms that integrate data collection, analysis, workflow management, and reporting capabilities. These systems transform audit GRC from periodic manual assessments to continuous monitoring programs that provide real-time insights into organizational performance.
Advanced platforms incorporate artificial intelligence and machine learning capabilities that identify anomalies, predict emerging risks, and suggest optimization opportunities. Natural language processing analyzes unstructured data sources including emails, contracts, and policy documents to identify compliance gaps and governance issues that might escape traditional detection methods.
| Technology Capability | Audit GRC Application | Business Value |
|---|---|---|
| Centralized data repository | Single source of truth for policies, controls, risks, assessments | Improved consistency, reduced duplication, enhanced accessibility |
| Automated workflow management | Standardized assessment processes, task assignments, deadline tracking | Increased efficiency, better accountability, consistent execution |
| Real-time dashboards | Executive visibility into key performance indicators and trends | Faster decision-making, proactive issue identification, stakeholder confidence |
| Continuous monitoring | Automated control testing, exception identification, trend analysis | Earlier issue detection, reduced manual effort, comprehensive coverage |
| Integrated reporting | Consolidated insights across governance, risk, compliance dimensions | Holistic understanding, strategic alignment, informed resource allocation |
Integration with existing enterprise systems amplifies technology value. Connections to financial systems, human resources platforms, procurement tools, and operational databases enable automated evidence collection and continuous control monitoring without creating additional operational burden.
Continuous Improvement and Maturity Development
Organizations should view audit GRC as an evolutionary journey rather than a static state to achieve. Conducting effective GRC audits requires ongoing refinement of methodologies, frameworks, and capabilities based on performance results and changing organizational contexts.
Maturity models provide structured frameworks for assessing current capabilities and planning advancement. These models typically define progressive stages from initial, reactive approaches through optimized, predictive programs that anticipate issues before they materialize. Organizations can benchmark their current position, identify capability gaps, and prioritize improvement initiatives that deliver maximum value.
Continuous improvement also requires regular stakeholder feedback. Organizations should solicit input from audit participants, operational management, executive leadership, and external stakeholders to understand perception gaps and improvement opportunities. This feedback informs refinements to assessment scope, methodologies, reporting formats, and communication approaches.
Adapting to Regulatory Evolution
The regulatory landscape continuously evolves as governments respond to emerging risks, technological changes, and societal expectations. Effective audit GRC programs incorporate mechanisms for tracking regulatory developments, assessing their organizational impact, and adapting compliance programs accordingly.
Organizations should establish regulatory monitoring processes that systematically track proposed legislation, regulatory guidance updates, enforcement actions, and industry interpretations. This intelligence enables proactive adaptation rather than reactive scrambling when requirements become effective. For organizations in specialized sectors like financial services, staying current with regulatory changes represents both a compliance obligation and competitive advantage.
Stakeholder Communication and Engagement
Audit GRC success depends on effective communication with diverse stakeholders including governance bodies, executive leadership, operational management, external auditors, regulators, and business partners. Each audience requires tailored messaging that addresses their specific interests and decision-making needs.
Governance bodies need strategic insights into organizational risk posture, control effectiveness trends, and significant emerging issues. These communications should connect audit findings to strategic objectives and stakeholder expectations rather than overwhelming boards with operational details.
Executive leadership requires balanced information that highlights both achievements and challenges. Communications should provide sufficient context for informed decision-making while respecting time constraints through concise summaries and prioritized recommendations.
Operational management needs detailed, actionable information that supports remediation planning and implementation. These communications should clearly articulate expected outcomes, resource requirements, and implementation timelines while acknowledging operational constraints and competing priorities.
Measuring Audit GRC Effectiveness
Organizations must establish metrics that demonstrate audit GRC value and drive continuous improvement. GRC audit frameworks and best practices emphasize the importance of measuring both process efficiency and outcome effectiveness.
Process efficiency metrics include:
- Assessment cycle time from planning through reporting
- Resource hours invested per assessment area
- Stakeholder satisfaction with audit processes and communication
- Finding implementation rate within target timeframes
- Technology utilization and automation percentage
Outcome effectiveness metrics include:
- Regulatory examination results and citation frequency
- Control deficiency trends over time
- Risk incident frequency and severity
- Compliance violation rates across regulatory domains
- Strategic objective achievement related to governance and risk management
These metrics should be tracked consistently over time to identify trends, benchmark performance, and demonstrate continuous improvement. Organizations should also compare their performance against industry peers and best practice standards to identify relative strengths and development opportunities.
Implementing effective audit GRC practices strengthens organizational resilience, enhances regulatory compliance, and supports sustainable growth in increasingly complex business environments. For financial services providers and other regulated organizations in South Africa, professional guidance can accelerate maturity development while ensuring compliance with evolving requirements. Holistic Compliance Management Solutions provides specialized expertise in developing comprehensive compliance programs, risk management frameworks, and governance structures tailored to your operational context. Contact HCMS today to discover how integrated audit GRC approaches can transform your compliance posture and operational effectiveness.