AML Services for South African FSPs: Complete Guide
Financial Service Providers operating in South Africa face increasingly complex anti-money laundering obligations that demand sophisticated compliance infrastructure and ongoing vigilance. As regulatory scrutiny intensifies and global standards evolve, independent brokers and financial advisors must implement robust AML services that address both local requirements under the Financial Intelligence Centre Act (FICA) and international best practices. The convergence of FICA, the Protection of Personal Information Act (POPIA), the Conduct of Financial Institutions Act (COFI), and the Financial Advisory and Intermediary Services Act (FAIS) creates a comprehensive compliance landscape where effective AML services serve as the foundation for sustainable practice management and risk mitigation.
Understanding AML Service Requirements for South African FSPs
Anti-money laundering services encompass the policies, procedures, systems, and controls that Financial Service Providers implement to detect, prevent, and report suspicious activities that may indicate money laundering or terrorist financing. For independent brokers and financial advisors registered under FAIS, these obligations extend beyond simple tick-box exercises to form the cornerstone of professional practice.
The Financial Intelligence Centre Act (Act 38 of 2001) designates FSPs as accountable institutions, creating specific obligations that shape the scope of required AML services. These responsibilities include customer identification and verification, understanding the nature of business relationships, conducting ongoing monitoring, and submitting reports to the Financial Intelligence Centre when suspicious transactions occur.
Core Components of Effective AML Services
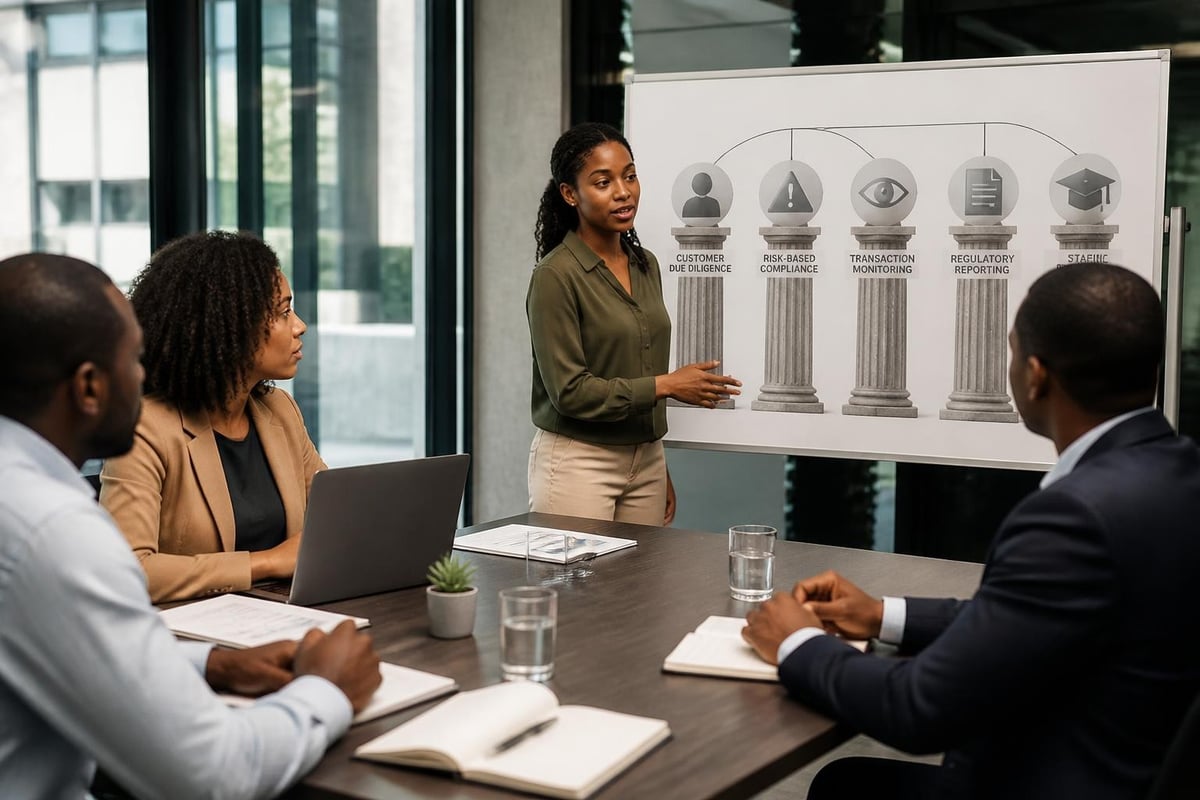
Comprehensive aml services for financial advisors must address five fundamental pillars:
- Customer Due Diligence (CDD) processes that verify client identity, beneficial ownership, and source of funds
- Risk-based approaches that allocate compliance resources according to assessed money laundering risks
- Transaction monitoring systems that identify unusual patterns or suspicious activities
- Reporting mechanisms that facilitate timely submission of Suspicious Transaction Reports (STRs) and Cash Threshold Reports (CTRs)
- Training programmes that ensure all staff understand their AML obligations and can recognise red flags
The complexity of these components varies according to practice size, client base, and product offerings. A boutique advisory practice handling high-net-worth individuals faces different risks compared to a general insurance broker serving retail clients, and effective AML services must reflect these distinctions.
FICA Compliance and Risk Management Control Programme Requirements
The Risk Management and Compliance Programme (RMCP) stands as the documented expression of an FSP's commitment to anti-money laundering compliance. This programme outlines how the practice identifies, assesses, monitors, mitigates, and reports money laundering and terrorist financing risks throughout its operations.
Effective aml services integrate RMCP requirements with daily workflows rather than treating compliance as a separate administrative burden. The RMCP must address specific elements mandated by the Financial Intelligence Centre, including governance structures, risk assessment methodologies, internal controls, and independent review mechanisms.
Developing Your FICA RMCP: Practical Steps
Independent brokers often struggle with RMCP development due to resource constraints and competing priorities. A systematic approach breaks this complex requirement into manageable phases:
- Conduct a comprehensive risk assessment examining client types, products, delivery channels, and geographic exposure
- Document existing controls that currently mitigate identified money laundering risks
- Identify control gaps where risks exceed current mitigation measures
- Design remediation strategies including new policies, procedures, or systems
- Create implementation timelines with realistic milestones and resource allocation
- Establish monitoring protocols for ongoing effectiveness testing
For practices requiring expert guidance, specialised Fica RMCP services provide affordable solutions that ensure compliance whilst allowing brokers to focus on client service and business development.
The relationship between FICA and POPIA adds complexity to AML service delivery. Personal information collected during customer due diligence processes must comply with POPIA's eight conditions for lawful processing. This means obtaining explicit consent, implementing appropriate security measures, and respecting data subject rights whilst simultaneously fulfilling FICA's identification and verification obligations.
| FICA Requirement | POPIA Consideration | Practical Solution |
|---|---|---|
| Collect ID documents | Minimise data collection | Collect only required fields |
| Verify physical address | Purpose specification | Use third-party verification |
| Retain records 5 years | Storage limitation | Implement secure disposal schedules |
| Share data with FIC | Lawful disclosure | Include regulatory disclosure in privacy notices |
Customer Due Diligence Processes for Financial Advisors
Customer identification and verification form the first line of defence in any effective AML programme. South African regulations distinguish between simplified, standard, and enhanced due diligence, with the appropriate level determined by assessed risk.
Standard CDD for individual clients requires collecting and verifying full names, date of birth, identity number, residential address, and contact details. Advisors must obtain original documents or certified copies, with verification conducted through reliable independent sources such as the Department of Home Affairs database or reputable third-party verification services.
Enhanced Due Diligence Triggers
Certain client characteristics or transaction types mandate enhanced scrutiny and more comprehensive aml services:
- Politically Exposed Persons (PEPs) including domestic and foreign public officials, their family members, and close associates
- High-risk jurisdictions identified by the Financial Action Task Force or South African authorities
- Complex ownership structures involving trusts, foundations, or offshore entities
- Cash-intensive businesses where clients operate in sectors known for money laundering vulnerabilities
- Unusual transaction patterns that lack apparent economic or lawful purpose
Enhanced due diligence extends beyond basic identification to understanding source of wealth, anticipated transaction patterns, and the purpose of the business relationship. This deeper investigation requires documented evidence and ongoing monitoring to ensure the relationship continues to match the expected profile.
International guidance from the Bank for International Settlements provides valuable perspectives on sound AML practices, though advisors must ensure local implementation aligns with South African regulatory expectations.
Beneficial Ownership Identification in Practice
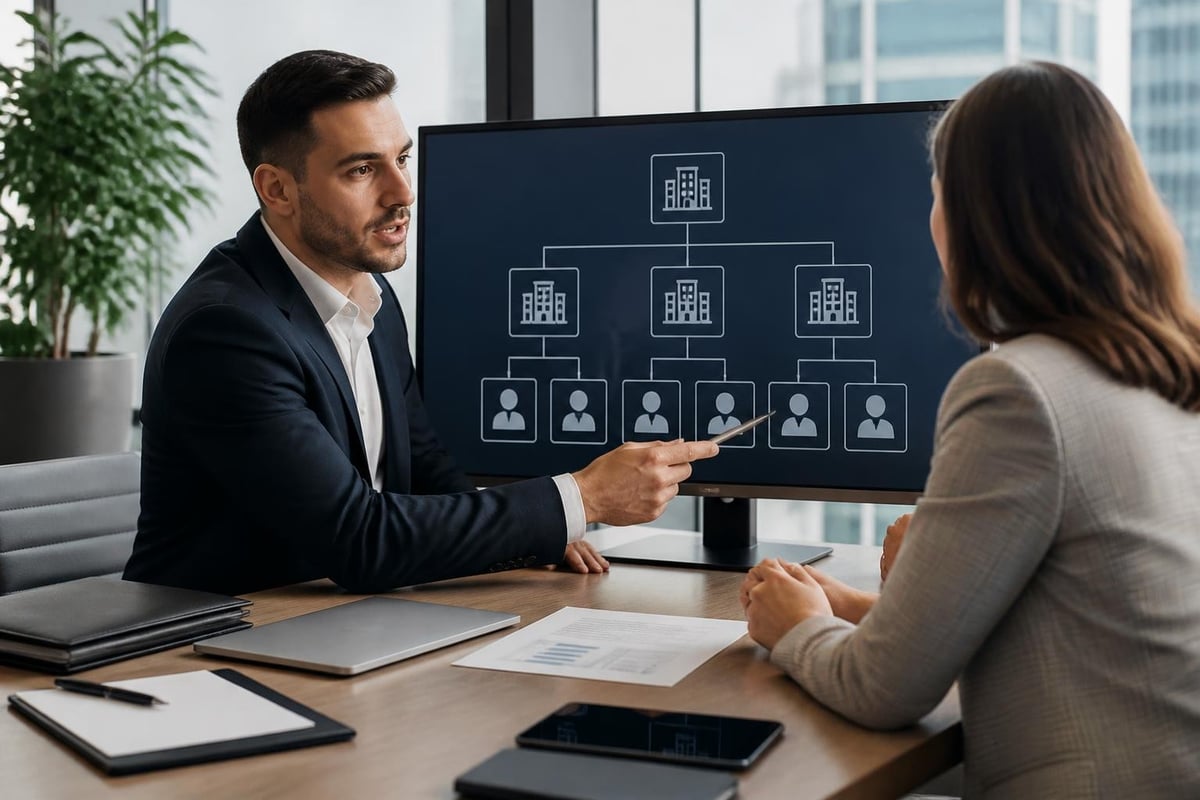
One of the most challenging aspects of customer due diligence involves identifying beneficial owners of legal entities and trusts. FICA amendments have strengthened these requirements, mandating that FSPs determine the natural persons who ultimately own or control corporate clients.
For private companies, beneficial ownership typically means any natural person who holds more than 25% of shares or voting rights, either directly or indirectly. However, effective aml services go beyond mechanical percentage calculations to identify those who exercise control through other means, including veto rights, management authority, or family relationships.
The FinCEN guidance on obtaining and retaining beneficial ownership information offers useful frameworks that complement South African requirements, particularly for advisors serving clients with international connections.
Trust Beneficial Ownership Verification
Trusts present particular complexity given their flexible nature and multiple stakeholders. Comprehensive beneficial ownership verification for trust clients requires identifying:
- The founder or settlor who established the trust
- All trustees with legal control over trust assets
- Beneficiaries entitled to trust distributions
- The protector if one has been appointed
- Any other natural person exercising effective control
Documentation must include certified copies of the trust deed, letters of authority, and identity documents for all identified beneficial owners. Where discretionary trusts name classes of beneficiaries rather than specific individuals, advisors must document the approach used to determine material beneficiaries.
Transaction Monitoring and Suspicious Activity Detection
Ongoing monitoring represents a continuous AML service obligation that extends throughout the client relationship. This requirement goes beyond periodic file reviews to encompass active surveillance of transactions, activities, and information changes that might indicate money laundering risks.
Effective monitoring programmes balance automation with human judgement. While large institutions deploy sophisticated software platforms, independent advisors typically rely on manual processes supported by well-designed checklists and alert triggers.
Red Flags for Independent Brokers
Financial advisors should train staff to recognise common money laundering indicators relevant to their product mix and client base:
- Clients reluctant to provide standard identification documentation or offering suspicious alternatives
- Transaction amounts structured just below reporting thresholds
- Frequent policy cancellations within free-look periods followed by refund requests
- Payments from third parties unrelated to the client without reasonable explanation
- Sudden changes in transaction patterns inconsistent with known client circumstances
- Requests to use products in ways inconsistent with their intended purpose
- Unusual interest in compliance procedures or reporting thresholds
- Client background inconsistent with presented financial position
Detection of red flags triggers enhanced scrutiny rather than automatic reporting. Advisors must investigate further, document their findings, and make informed decisions about whether circumstances warrant filing a Suspicious Transaction Report.
Regulatory Reporting Obligations Under FICA
Two primary reporting obligations flow from effective aml services: Cash Threshold Reports for qualifying cash transactions and Suspicious Transaction Reports when money laundering indicators emerge.
Cash Threshold Reports must be filed within the prescribed period whenever a single cash transaction exceeds R24,999.99 or multiple cash transactions by or on behalf of the same person exceed R24,999.99 within a single calendar day. These reports capture factual transaction data without requiring suspicion of criminal activity.
Suspicious Transaction Reports demand different considerations. These reports arise when an FSP knows, suspects, or has reasonable grounds to suspect that property or a transaction relates to money laundering or terrorist financing activities. The subjective element of suspicion creates challenges for advisors who must exercise professional judgement whilst managing legal obligations.
STR Filing Decision Framework
A structured approach helps advisors navigate STR filing decisions:
- Gather all relevant facts about the transaction, client, and circumstances
- Assess against known typologies using FIC guidance documents and industry alerts
- Evaluate alternative explanations that might account for unusual features
- Document the analysis including factors supporting and contradicting suspicion
- Make a reasoned decision balancing false positives against potential failures to report
- Submit promptly if suspicious within the prescribed timeframe from knowledge or suspicion
The UNODC goAML services platform facilitates electronic reporting in many jurisdictions and offers insights into case management systems that can inform South African reporting workflows.
Protection from civil liability exists for good-faith STR submissions, but this protection requires genuine suspicion rather than defensive over-reporting. Quality exceeds quantity in suspicious transaction reporting, with well-researched reports providing more value than numerous speculative submissions.
POPIA Compliance in AML Data Processing
The intersection of anti-money laundering obligations and privacy rights creates tension that requires careful navigation. POPIA grants data subjects various rights including access, correction, and deletion, whilst FICA mandates five-year record retention and sharing with regulatory authorities.
Effective aml services implement privacy-protective measures within the constraints of regulatory obligations. This means designing information flows that collect only necessary data, implement appropriate security controls, and respect data subject rights whilst ensuring compliance with FICA requirements.
| POPIA Principle | AML Implementation | Compliance Strategy |
|---|---|---|
| Accountability | Designated information officer | Assign AML and POPIA oversight to qualified person |
| Processing limitation | Collect minimal necessary data | Map data fields to specific FICA requirements |
| Purpose specification | Clear privacy notices | Explain AML purposes in client communications |
| Security safeguards | Protect sensitive documents | Implement secure storage and access controls |
| Data subject participation | Access and correction rights | Establish request handling procedures |
| Openness | Transparent processing | Publish privacy policies explaining FICA compliance |
AML Training Programmes for FSP Staff
Comprehensive staff training represents an essential component of sustainable aml services. The Financial Intelligence Centre expects accountable institutions to ensure employees understand their obligations, can recognise suspicious activities, and know how to escalate concerns appropriately.
Training requirements vary according to role and exposure. Client-facing advisors require different content compared to administrative staff, whilst compliance officers need deeper technical knowledge of regulatory requirements and reporting procedures.
Effective Training Content Structure
Annual AML training programmes should address core content areas with practical application:
- Regulatory framework overview covering FICA, POPIA, and relevant regulations
- Money laundering typologies specific to financial services and insurance sectors
- Customer due diligence requirements with role-specific procedures
- Beneficial ownership identification including complex structures
- Transaction monitoring obligations and red flag recognition
- Reporting procedures for suspicious activities and cash transactions
- Record-keeping requirements and retention schedules
- Data protection obligations under POPIA
Interactive elements enhance retention and application. Case studies drawn from Financial Intelligence Centre enforcement actions or industry examples help staff connect abstract principles to practical situations they might encounter.
Technology Solutions for AML Compliance
Independent brokers increasingly leverage technology to deliver efficient aml services without the cost structures of enterprise solutions. Cloud-based platforms now offer modular functionality suitable for smaller practices, including customer screening, document management, and transaction monitoring.
Identity verification services connect to government databases and third-party information sources, automating much of the verification process whilst generating audit trails. These services typically charge per verification, making them economically viable for practices with modest client onboarding volumes.
Sanctions screening represents another area where technology delivers disproportionate value. Global sanctions lists change frequently, and manual checking proves time-consuming and error-prone. Automated screening services flag potential matches for investigation, ensuring practices don't inadvertently engage with sanctioned individuals or entities.
Building Your Compliance Technology Stack
A practical technology approach for independent advisors includes:
- Client relationship management (CRM) systems with built-in compliance fields and alerts
- Document management platforms providing secure storage with version control and retention automation
- Identity verification services offering certified document checks and biometric validation
- Sanctions and PEP screening through subscription databases or API services
- Training management systems tracking completion, competency assessment, and refresh cycles
Integration matters as much as individual components. Disconnected systems create inefficiency and increase error risk, whilst integrated platforms streamline workflows and ensure consistent data across compliance functions.
Risk Assessment Methodologies for Financial Advisors
The risk-based approach underpins modern AML frameworks, allowing practices to allocate resources according to assessed threats rather than applying uniform measures regardless of risk. Financial advisors must conduct both business-wide risk assessments examining overall exposure and individual client risk assessments determining appropriate due diligence levels.
Business-wide assessments consider inherent risks arising from client types, products, delivery channels, and geographic factors. A practice serving predominantly domestic retail clients through face-to-face channels presents different risks compared to one managing high-net-worth portfolios with international assets and offshore structures.
The World Bank Legal Persons and Arrangements ML Risk Assessment Tool provides structured methodologies applicable to sectoral assessments, helping advisors identify and quantify exposures across their operations.
Client Risk Rating Framework
Individual client assessments typically employ scoring models that weight various risk factors:
Low-risk indicators:
- Domestic individual with verified employment income
- Long-standing relationship with consistent transaction patterns
- Products appropriate to demonstrated needs and financial position
- Transparent source of funds and wealth
High-risk indicators:
- Politically exposed person status or close association
- Complex corporate or trust structures with opaque ownership
- Cash-intensive business activities or high-risk industry sectors
- Geographic connections to high-risk jurisdictions
- Transactions inconsistent with stated purposes or client profile
Risk ratings drive due diligence intensity and monitoring frequency. Low-risk clients may receive periodic reviews, whilst high-risk relationships demand enhanced due diligence at onboarding and more frequent ongoing monitoring.
COFI and TCF Integration with AML Services
The Conduct of Financial Institutions Act introduces conduct standards that complement existing AML obligations. Treating Customers Fairly (TCF) principles interact with anti-money laundering requirements, particularly around information disclosure and product suitability.
Effective aml services support conduct outcomes by ensuring advisors understand client circumstances sufficiently to recommend appropriate products. Customer due diligence processes that probe income sources, financial objectives, and risk tolerance serve both AML risk assessment and TCF suitability analysis.
Vulnerable clients present particular challenges where AML vigilance must balance against fair treatment. Elderly clients, those with cognitive impairments, or individuals from disadvantaged backgrounds may struggle with documentation requirements or exhibit patterns that superficially resemble red flags. Advisors must distinguish genuine vulnerability from suspicious evasion whilst ensuring equitable access to financial services.
Independent Review and Quality Assurance
The RMCP must include mechanisms for independent testing of AML systems and controls. For sole practitioners and small practices, true independence proves challenging but remains achievable through creative approaches.
External compliance consultants provide periodic reviews assessing policy effectiveness, procedure adherence, and control adequacy. These reviews examine sample files, test transaction monitoring processes, and evaluate staff competency through interviews or assessments.
Peer review arrangements among non-competing advisors offer cost-effective alternatives. Two practices exchange compliance files and procedures for reciprocal assessment, providing fresh perspectives whilst sharing expertise and spreading costs.
Quality Assurance Metrics
Effective aml services incorporate measurable indicators of programme health:
| Metric | Target | Review Frequency |
|---|---|---|
| CDD documentation completeness | 100% | Monthly file sampling |
| Beneficial ownership verification | 100% for legal entities | Quarterly review |
| PEP screening coverage | 100% of clients | System-generated reports |
| Training completion rates | 100% within 90 days | Quarterly tracking |
| Average STR investigation time | Within 5 business days | Per incident review |
| Records within retention policy | 95%+ compliance | Annual audit |
Metrics should drive improvement rather than merely documenting deficiencies. Trends matter more than point-in-time measurements, with sustained improvements indicating effective programme management.
Regulatory Developments and Future Outlook
South Africa's AML framework continues evolving in response to international standards and emerging threats. The Financial Action Task Force mutual evaluation process drives legislative and regulatory changes that affect required aml services.
Recent amendments to FICA strengthen beneficial ownership requirements, expand the definition of domestic prominent influential persons, and enhance enforcement mechanisms available to supervisory bodies. Advisors must monitor these developments and adapt compliance programmes accordingly.
The European Commission’s anti-money laundering and countering the financing of terrorism framework offers insights into global trends that often influence South African policy development, including beneficial ownership registers, cryptocurrency regulation, and enhanced due diligence standards.
Preparing for Enhanced Supervision
The Financial Sector Conduct Authority increasingly emphasises proactive compliance monitoring rather than reactive enforcement. This shift requires advisors to demonstrate ongoing commitment to AML obligations through documented programmes, regular training, and continuous improvement.
Supervisory expectations extend beyond policy documentation to evidence of practical implementation. Site visits examine actual workflows, staff competency, and management oversight rather than simply reviewing written procedures. Effective aml services must therefore bridge the gap between documented aspirations and daily practice.
Building a Sustainable Compliance Culture
Long-term AML effectiveness requires embedding compliance into organisational culture rather than treating it as an administrative burden. Leadership commitment, clear accountability, and consistent messaging shape how staff approach their obligations.
Regular communication reinforces expectations and provides updates on emerging risks or regulatory changes. Team meetings should include compliance agenda items, discussing recent cases, regulatory updates, or emerging typologies relevant to the practice.
Recognition and accountability mechanisms encourage desired behaviours. Acknowledging staff who identify suspicious activities or maintain exemplary file documentation reinforces standards, whilst addressing deficiencies promptly prevents normalisation of substandard practices.
Practical Compliance Monitoring Workflows
Daily integration of AML activities into standard workflows prevents compliance from becoming an afterthought addressed during panic-driven annual reviews. Structured processes ensure consistent application across all client interactions.
New client onboarding checklist:
- Obtain and verify identity documents using approved sources
- Complete beneficial ownership identification for legal entities and trusts
- Conduct PEP and sanctions screening before account activation
- Assess and document money laundering risk rating
- Obtain client acknowledgement of privacy notices and disclosures
- Upload documentation to secure storage with appropriate retention classification
Ongoing monitoring protocols:
- Monthly review of high-risk client transactions and activities
- Quarterly screening updates against sanctions and PEP lists
- Annual file reviews confirming information currency and risk rating appropriateness
- Immediate investigation of red flag triggers or unusual patterns
- Periodic quality assurance sampling across client portfolios
Automation helps maintain consistency whilst reducing manual effort. Calendar reminders trigger scheduled reviews, whilst workflow tools ensure completion of required steps before progressing to subsequent stages.
Cost-Effective Compliance for Independent Practices
Budget constraints challenge independent brokers seeking to implement comprehensive aml services without enterprise resources. Strategic prioritisation and creative solutions enable effective compliance within realistic financial parameters.
Shared services arrangements with peer practices distribute costs across multiple businesses. Pooled subscriptions to screening databases, joint procurement of training programmes, or collaborative development of template policies reduce per-practice expenses.
Outsourced compliance support provides access to expertise without full-time employment costs. Specialist consultants offer hourly or retainer-based services covering risk assessments, RMCP development, staff training, or periodic quality reviews.
Technology investments should prioritise high-impact, low-cost solutions before considering premium platforms. Free or low-cost document management systems, basic CRM functionality, and manual screening against publicly available sanctions lists provide foundational capabilities pending practice growth that justifies more sophisticated tools.
Effective anti-money laundering services form the foundation of sustainable financial advisory practices in South Africa's evolving regulatory landscape. By implementing comprehensive customer due diligence, risk-based monitoring, and robust reporting processes whilst balancing POPIA privacy obligations, independent brokers demonstrate professional commitment and protect both clients and their businesses from financial crime risks.
Who this is for: Independent insurance brokers, financial advisors, compliance officers, and FSPs seeking to strengthen their AML frameworks and FICA compliance programmes.
Holistic Compliance Management Solutions (Pty) Ltd provides specialist support to Financial Service Providers navigating the complexities of AML compliance, FICA requirements, and RMCP development. Schedule FICA training to ensure your practice meets regulatory obligations through expert-led programmes covering:
- Comprehensive FICA and POPIA compliance requirements for FSPs
- Practical beneficial ownership identification and verification procedures
- RMCP development workshops with customised documentation templates
- Transaction monitoring protocols and suspicious activity reporting guidance
- Ongoing compliance monitoring support tailored to independent broker workflows