PCI Compliance Consultant: A South African Guide
Navigating the complex landscape of payment card industry security in South Africa requires specialised expertise that extends beyond basic data protection. For independent financial advisors, brokers, and Financial Service Providers (FSPs) who process card payments, understanding how PCI DSS requirements intersect with local regulations such as POPIA, FICA, and FAIS creates unique compliance challenges. A qualified pci compliance consultant bridges this gap, helping financial services businesses protect sensitive payment data whilst maintaining adherence to South African regulatory frameworks. This comprehensive guide explores how compliance specialists support FSPs in building robust payment security programmes that satisfy both international card brand requirements and domestic financial services legislation.
Understanding PCI Compliance in the South African Financial Services Context
The Payment Card Industry Data Security Standard (PCI DSS) applies to any organisation that accepts, processes, stores, or transmits credit card information. For South African financial services providers, this creates a dual compliance obligation: satisfying international payment security standards whilst simultaneously meeting requirements under the Protection of Personal Information Act (POPIA), the Financial Intelligence Centre Act (FICA), and the Conduct of Financial Institutions Act (COFI).
A pci compliance consultant operating in the South African market must understand this regulatory intersection. Unlike general IT security advisors, specialists in this field recognise that independent brokers and FSPs face unique challenges when processing client payments through card terminals, online portals, or recurring payment systems.
Key Regulatory Overlaps for South African FSPs
The relationship between PCI DSS and South African financial services regulation creates several critical compliance points:
- POPIA Section 19: Requires security safeguards for personal information, which includes payment card data
- FICA Record-Keeping: Demands secure retention of client transaction records, including payment histories
- FAIS Fit and Proper Requirements: Expect FSPs to maintain robust operational systems, including secure payment processing
- COFI Treating Customers Fairly: Requires protection of client financial information throughout the service relationship
When these frameworks overlap, compliance becomes more complex. For example, POPIA requires data minimisation, suggesting businesses should retain minimal client data, whilst FICA mandates detailed transaction record retention for five years. A skilled consultant helps FSPs navigate these apparent contradictions whilst maintaining payment card security.
| Regulatory Framework | Primary Focus | Intersection with PCI DSS |
|---|---|---|
| PCI DSS | Payment card data protection | Core standard for card security |
| POPIA | Personal information processing | Governs how cardholder data is collected and used |
| FICA | Anti-money laundering and record-keeping | Affects retention of payment transaction records |
| FAIS | FSP conduct and client protection | Requires operational security for client transactions |
| COFI | Consumer protection in financial services | Demands secure handling of client payment information |
The Role of a PCI Compliance Consultant for Independent Brokers
Independent insurance brokers and financial advisors often operate lean practices with limited IT infrastructure. Yet when these businesses accept premium payments via credit or debit card, full PCI compliance becomes mandatory. This creates a significant burden for small practices that lack dedicated compliance resources.
A pci compliance consultant provides the specialised knowledge needed to implement appropriate security controls without overwhelming the broker's operational capacity. The consultant's role extends across several critical functions that align directly with the operational realities of independent financial services practices.
Initial Scoping and Risk Assessment
The first step in any PCI engagement involves determining which systems, networks, and processes fall within scope. For a typical independent broker practice, this might include:
- Point-of-sale terminals used to collect premium payments
- Virtual terminal access through payment gateway websites
- Recurring payment systems for ongoing policy premiums
- Client databases that store payment card details (strongly discouraged)
- Network infrastructure connecting payment systems to the Internet
The scoping and segmentation guidance for modern networks published by the PCI Security Standards Council provides essential frameworks for this process. However, applying these technical standards to a small broker practice requires practical interpretation.
A qualified consultant conducts a thorough assessment of the broker's payment processing workflows, identifying where cardholder data enters, moves through, and exits the organisation. This assessment must also consider how payment processes interact with other regulated activities such as FICA client verification, POPIA consent management, and FAIS record-keeping.
Determining the Appropriate Validation Level
Not all businesses face identical PCI compliance requirements. The card brands (Visa, Mastercard, American Express) set different validation levels based on transaction volume. Understanding these distinctions prevents both under-compliance and wasteful over-investment in unnecessary controls.
For most independent South African brokers and advisors, compliance falls into these categories:
Level 4 Merchants (fewer than 20,000 e-commerce transactions or 1 million total transactions annually):
- Complete annual Self-Assessment Questionnaire (SAQ)
- Conduct quarterly network vulnerability scans
- Maintain evidence of compliance
- No external audit required
Level 3 Merchants (20,000 to 1 million e-commerce transactions annually):
- Annual SAQ with Attestation of Compliance
- Quarterly vulnerability scans by Approved Scanning Vendor (ASV)
- May require network segmentation documentation
A pci compliance consultant helps brokers accurately classify their merchant level and select the appropriate SAQ type. The Visa guidance on accepting payments online clarifies these validation options, though interpreting them within South African regulatory context requires specialised knowledge.
Implementation of Security Controls
Once scoping and validation requirements are clear, the consultant assists with implementing the twelve PCI DSS requirements. For independent financial services practices, certain requirements demand particular attention:
- Requirement 1: Install and maintain network security configurations including firewalls
- Requirement 2: Eliminate vendor-supplied defaults for system passwords and security parameters
- Requirement 3: Protect stored cardholder data (ideally, don't store it at all)
- Requirement 4: Encrypt transmission of cardholder data across public networks
- Requirement 7: Restrict access to cardholder data by business need-to-know
- Requirement 8: Identify and authenticate access to system components
- Requirement 9: Restrict physical access to cardholder data
- Requirement 10: Track and monitor all access to network resources and cardholder data
- Requirement 11: Regularly test security systems and processes
- Requirement 12: Maintain a policy that addresses information security for employees and contractors
For compliance monitoring practices serving the financial services industry, these requirements often align naturally with existing POPIA and FICA obligations. The principle of data minimisation under POPIA complements PCI Requirement 3's mandate to limit cardholder data storage. Similarly, FICA's access control requirements for client records parallel PCI Requirements 7 and 8.
Practical Implementation Steps for South African FSPs
Implementing PCI compliance within an independent broker practice requires a structured, phased approach that respects operational constraints whilst building robust security. A pci compliance consultant typically guides FSPs through the following implementation pathway.
Phase One: Immediate Risk Mitigation (Weeks 1-2)
1. Eliminate Unnecessary Cardholder Data Storage
The simplest path to compliance is reducing scope. Most independent brokers have no legitimate business need to store full credit card numbers, CVV codes, or magnetic stripe data.
Review current practices:
- Do staff write down card numbers on paper forms? (Immediately cease this practice)
- Are card details stored in spreadsheets or practice management systems? (Securely delete)
- Do email records contain payment card information? (Implement retention policies)
2. Secure Existing Payment Systems
If using third-party payment processors or terminals:
- Confirm the processor is PCI DSS compliant (request Attestation of Compliance)
- Ensure terminals are not jailbroken or modified
- Place terminals in secure physical locations
- Change all default passwords immediately
3. Implement Basic Access Controls
- Limit payment system access to essential staff only
- Create unique login credentials for each user
- Disable shared accounts or generic logins
- Document who has access to what systems
Phase Two: Policy and Process Development (Weeks 3-6)
A fundamental PCI DSS requirement often overlooked by small practices is comprehensive security policy documentation. For South African FSPs already maintaining FICA Risk Management and Compliance Programmes (RMCPs), integrating payment security policies creates natural synergy.
The consultant assists in developing:
Information Security Policy: Governing all aspects of data protection, encompassing both PCI and POPIA requirements
Acceptable Use Policy: Defining how staff may use payment systems, client databases, and network resources
Incident Response Plan: Outlining steps to take if a data breach or security incident occurs (required by both PCI DSS and POPIA Section 22)
Access Control Procedures: Documenting how payment system access is granted, reviewed, and revoked
These policies should integrate seamlessly with existing FAIS compliance frameworks. For FSPs already working with compliance monitoring services, PCI policy development can be incorporated into broader governance reviews.
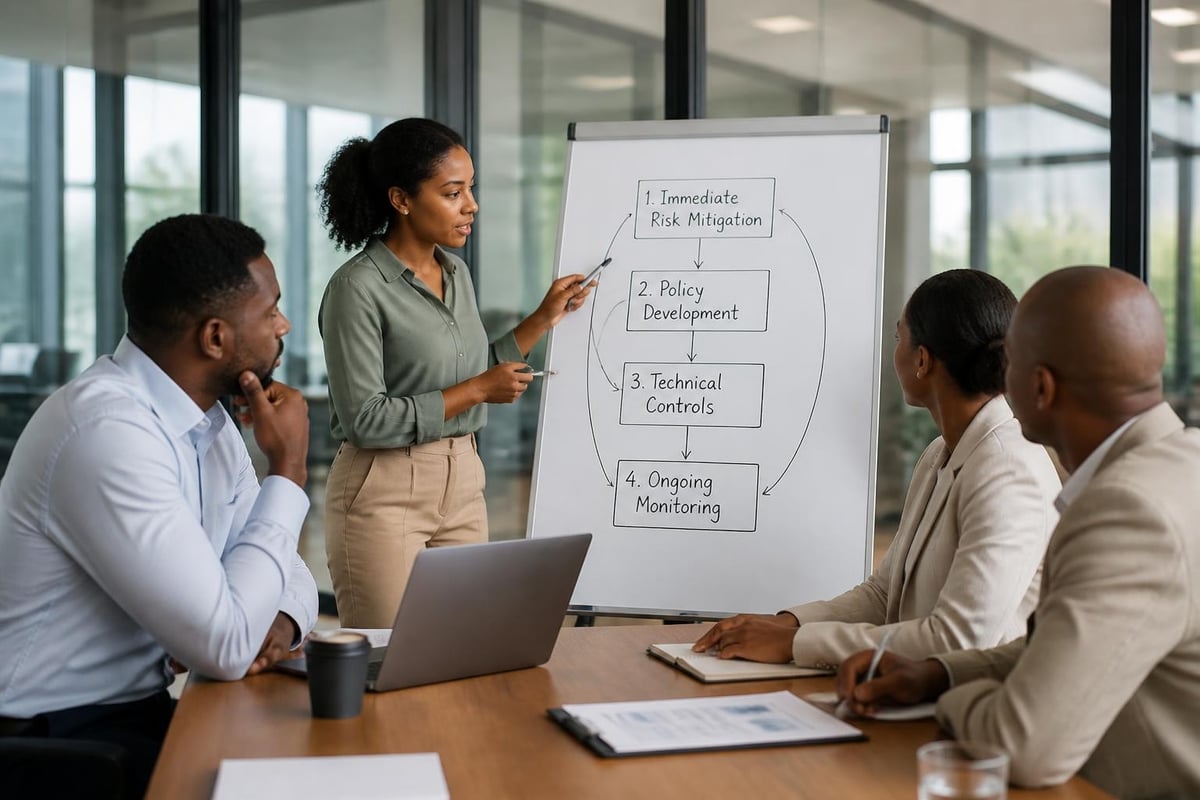
Phase Three: Technical Control Implementation (Weeks 7-12)
With policies established, attention turns to technical security measures. The FTC’s business security guidance provides foundational principles that pci compliance consultants adapt to financial services contexts.
Network Segmentation
For practices with on-premise payment infrastructure, network segmentation isolates payment systems from general business networks. This dramatically reduces compliance scope.
Implementation steps:
- Deploy a dedicated firewall or router for payment systems
- Configure separate network VLANs for payment and administrative systems
- Implement strict firewall rules allowing only necessary traffic
- Document network diagrams showing segmentation boundaries
- Conduct regular firewall rule reviews (quarterly minimum)
Vulnerability Management
PCI DSS mandates quarterly vulnerability scans and regular patching. For cloud-hosted payment systems, understanding shared responsibility models becomes critical. The AWS PCI DSS v4.0 compliance guide illustrates how cloud providers and customers divide security obligations.
Encryption and Data Protection
All cardholder data transmission must be encrypted:
- Payment terminals should use point-to-point encryption (P2PE)
- Web-based payment forms must use TLS 1.2 or higher
- Wireless networks transmitting payment data require WPA2/WPA3 encryption
- Email should never be used to transmit card numbers
Phase Four: Testing and Validation (Weeks 13-16)
Before submitting compliance attestation, thorough testing verifies that controls function as intended. A pci compliance consultant coordinates several validation activities:
Internal Vulnerability Scanning: Using approved scanning tools to identify network weaknesses
External Vulnerability Scanning: Conducted by an Approved Scanning Vendor (ASV) to test Internet-facing systems
Penetration Testing: For higher merchant levels or complex environments, simulated attacks verify control effectiveness
Security Awareness Testing: Ensuring staff understand their roles in maintaining payment security
Policy Compliance Review: Confirming that documented procedures are followed in daily operations
Addressing Human Risk in Payment Security
Technical controls form only part of an effective PCI compliance programme. Research consistently shows that human error causes the majority of data breaches. The SANS Institute whitepaper on managing human risk provides practical frameworks for addressing people-related vulnerabilities.
For independent South African brokers, human risk manifests in several common scenarios:
Staff Training and Awareness
Every employee who handles payment transactions must understand basic security principles:
- Never write down card numbers or security codes
- Don't photograph or screenshot payment information
- Always verify caller identity before discussing payment details
- Report suspicious activities immediately
- Follow established procedures for payment processing
Training should occur during onboarding and annually thereafter. For FSPs already conducting FICA and POPIA training through specialised providers, payment security awareness can be integrated into existing training programmes, creating efficiency.
Social Engineering Prevention
Fraudsters increasingly target small financial services practices through sophisticated social engineering attacks. Staff must be trained to recognise:
Phishing emails claiming to be from payment processors, requesting login credentials or system changes
Pretexting calls where attackers pose as bank officials, IT support, or compliance auditors to extract sensitive information
Physical breaches where individuals pose as maintenance staff to gain physical access to payment terminals or network equipment
Regular scenario-based training helps staff develop healthy scepticism when unusual requests are received.
Third-Party Vendor Management
Most independent brokers rely on multiple third-party vendors: payment processors, practice management software providers, IT support companies, and cloud service platforms. Each vendor relationship introduces potential security risks.
A pci compliance consultant assists FSPs in:
- Inventorying all vendors with access to payment systems or cardholder data
- Requesting PCI compliance attestations from service providers
- Reviewing vendor contracts for security requirements
- Establishing service level agreements that include security expectations
- Conducting periodic vendor security reviews
Under POPIA, FSPs bear responsibility for how operators (vendors) process personal information on their behalf. This creates a direct regulatory link between PCI vendor management and POPIA Section 21 obligations.
Ongoing Compliance Monitoring and Maintenance
Achieving initial PCI compliance represents a significant milestone, but compliance is not a one-time project. A pci compliance consultant helps establish sustainable processes for maintaining ongoing adherence to payment security standards.
Annual Validation Requirements
Each year, merchants must revalidate compliance:
- Complete the appropriate SAQ
- Submit quarterly ASV scan results
- Update network diagrams and system inventories
- Review and update security policies
- Conduct staff security awareness training
- Sign Attestation of Compliance
- Submit documentation to acquiring bank
Missing annual validation deadlines can result in non-compliance fees from payment processors, typically ranging from R1,500 to R15,000 monthly until compliance is restored.
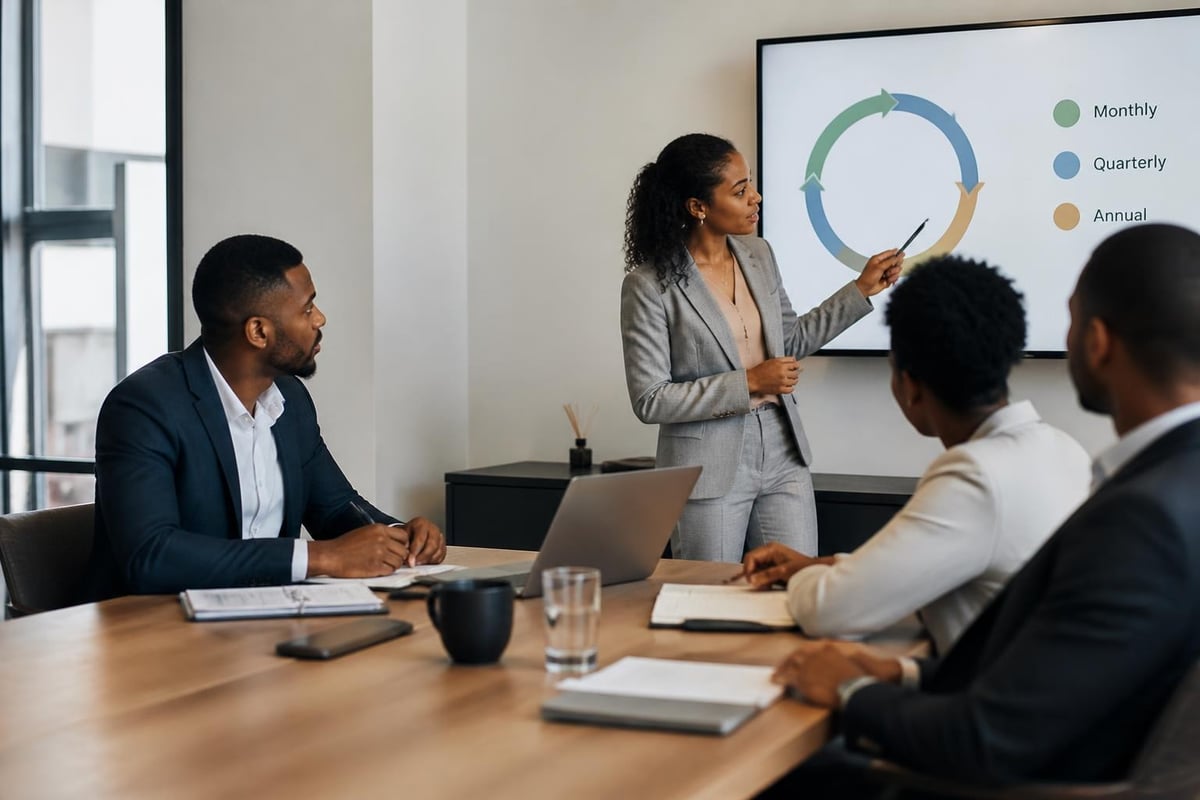
Continuous Monitoring Activities
Between annual validations, several ongoing activities maintain security posture:
Monthly Tasks:
- Review access logs for payment systems
- Verify anti-virus definitions are current
- Monitor for unauthorized system changes
- Review physical security of payment terminals
Quarterly Tasks:
- Conduct vulnerability scans (if applicable)
- Review and update firewall rules
- Test backup restoration procedures
- Audit user access rights
Annual Tasks:
- Comprehensive security policy review
- Staff security awareness training refresh
- Penetration testing (for higher merchant levels)
- Business continuity plan testing
For practices already implementing holistic compliance management solutions covering FICA, POPIA, and FAIS requirements, PCI monitoring activities integrate naturally into existing compliance calendars.
PCI DSS Version 4.0: New Requirements for 2026
The PCI Security Standards Council released version 4.0 of the Data Security Standard in March 2022, with a transition period extending through March 2025. From April 2025 onward, all previous version 3.2.1 requirements became obsolete, and any remaining "future-dated" requirements became mandatory.
A knowledgeable pci compliance consultant ensures FSPs understand and prepare for these enhanced requirements:
Multi-Factor Authentication Expansion
Version 3.2.1: Required MFA for remote network access to cardholder data environment
Version 4.0: Requires MFA for all access to cardholder data environment, whether remote or local, with limited exceptions
This significantly affects independent broker practices where staff previously accessed payment systems using only username and password combinations.
Enhanced Password Requirements
New minimum standards:
- Passwords must be at least 12 characters (increased from 7)
- Passwords must be changed at least every 90 days if not using MFA
- Password history requirements prevent reuse of recent passwords
Customised Implementation for Targeted Risk Analysis
Version 4.0 introduces the "Customised Approach," allowing organisations to implement alternative controls if they achieve equivalent security outcomes. This flexibility particularly benefits small FSPs with unique operational models.
However, pursuing customised implementations requires:
- Comprehensive risk assessment documentation
- Demonstration that alternative controls meet security objectives
- Annual validation of control effectiveness
- Qualified assessor approval (for audited environments)
Role-Based Access Controls
Enhanced requirements for role-based access emphasize:
- Documented access policies defining roles and permissions
- Regular access reviews (at least every six months)
- Immediate revocation when employment ends or roles change
- Audit logs tracking all administrative actions
For South African FSPs already implementing FICA-compliant access controls for client records, extending these frameworks to payment systems creates operational efficiency.
Selecting a Qualified PCI Compliance Consultant
Not all compliance advisors possess equivalent expertise in payment security. When engaging a pci compliance consultant, South African FSPs should evaluate several critical qualifications.
Professional Certifications and Training
The PCI Security Standards Council offers formal qualifications:
Qualified Security Assessor (QSA): Authorized to conduct PCI DSS compliance assessments for merchants and service providers. The QSA certification programme requires extensive training, background verification, and ongoing recertification.
Internal Security Assessor (ISA): Qualified to conduct internal PCI assessments within their own organization
PCI Professional (PCIP): Demonstrates comprehensive understanding of PCI DSS requirements
Whilst QSA certification is mandatory only for external audits of higher-level merchants, it signals deep technical expertise valuable even for Level 4 merchant consulting.
South African Regulatory Knowledge
Beyond payment security expertise, consultants serving FSPs must understand local regulatory contexts:
- POPIA compliance: How data protection principles apply to cardholder information
- FICA requirements: Integration of payment transaction records with FICA record-keeping
- FAIS frameworks: Operational risk management expectations for FSPs
- COFI principles: Consumer protection obligations affecting payment processing
A consultant with dual expertise in PCI standards and South African financial services regulation delivers significantly more value than a pure IT security specialist.
Industry-Specific Experience
Payment processing varies dramatically across industries. A consultant experienced with retail merchants may lack understanding of the unique challenges facing independent financial advisors:
- Recurring premium payment processing
- Integration with insurance administration systems
- FICA client verification during payment setup
- POPIA consent management for stored payment methods
- Alignment with existing FSP compliance monitoring programmes
Request case studies or references from similar practices when evaluating potential consultants.
Building Business Cases for PCI Investment
Independent brokers and advisors often question whether PCI compliance investment delivers commensurate value, particularly when transaction volumes are modest. A skilled pci compliance consultant helps articulate both risk mitigation and business opportunity arguments.
Risk Quantification
Data breaches carry severe financial consequences:
Direct Costs:
- POPIA administrative penalties up to R10 million
- Card brand fines ranging from R100,000 to R5 million
- Forensic investigation costs (R150,000 to R500,000 for small breaches)
- Legal fees for client notification and potential litigation
- Credit monitoring services for affected clients
Indirect Costs:
- Reputational damage affecting client retention and new business
- Increased payment processing costs or loss of card acceptance
- Regulatory scrutiny potentially affecting FSP license
- Professional indemnity insurance premium increases
For a typical independent broker processing R2 million in annual premium payments, a single breach could cost 5-10 times annual profit.
Competitive Advantage
Demonstrable security compliance creates market differentiation:
Client Trust: Professional clients increasingly evaluate advisors on data protection practices
Institutional Partnerships: Underwriters and product providers prefer brokers with robust compliance programmes
Referral Confidence: Centres of influence (accountants, attorneys) refer more confidently to compliant practices
Regulatory Standing: Strong compliance history supports future license applications or expansions
Operational Efficiency
Well-implemented PCI programmes often streamline operations:
- Automated payment processing reduces administrative burden
- Clear policies minimize staff confusion and errors
- Integrated compliance frameworks eliminate duplicated effort across POPIA, FICA, and PCI requirements
- Documented procedures facilitate staff training and business continuity
Integration with Broader FSP Compliance Programmes
The most effective PCI implementations integrate seamlessly with existing compliance frameworks rather than creating parallel, isolated processes. For South African FSPs already managing FICA RMCPs, POPIA processing records, and FAIS operational policies, strategic integration reduces both effort and cost.
FICA RMCP Integration
The FICA Risk Management and Compliance Programme (RMCP) required of all accountable institutions provides an ideal framework for incorporating payment security controls:
Section 42 (General Risk Management): Include payment system security within overall risk assessment
Section 43 (Internal Rules): Incorporate PCI policies into broader compliance policies
Section 45 (Compliance Function): Assign payment security monitoring to compliance officer
Section 46 (Independent Review): Include PCI controls in periodic compliance audits
For practices requiring assistance with RMCP development or updates, specialists offering FICA RMCP drafting services can incorporate payment security requirements from inception.
POPIA Alignment
The Protection of Personal Information Act creates natural synergies with PCI DSS:
| POPIA Requirement | PCI DSS Alignment | Integrated Control Example |
|---|---|---|
| Security safeguards (Section 19) | Requirements 1-4, 8-9 | Network firewalls protecting both personal information and payment data |
| Data minimisation (Section 10) | Requirement 3 | Policies eliminating storage of both unnecessary personal information and payment card details |
| Access restrictions (Section 19) | Requirements 7-8 | Role-based access controlling both client records and payment systems |
| Breach notification (Section 22) | Requirement 12 | Unified incident response plan covering all data categories |
| Operator accountability (Section 21) | Requirement 12.8 | Vendor management programme covering all third-party processors |
FAIS Operational Risk Management
The Financial Advisory and Intermediary Services Act expects FSPs to maintain robust operational systems. Payment security directly supports several FAIS obligations:
Treating Customers Fairly Principle 5: Clients' transaction processing must be secure and efficient
Fit and Proper Requirements: Operational competence includes secure payment handling
Record-Keeping Requirements: Payment transaction records must be securely retained
Complaints Management: Security incidents affecting clients must be properly addressed
By framing PCI compliance as integral to FAIS obligations rather than an additional burden, consultants help FSPs recognize payment security as core business practice.
Common PCI Compliance Challenges for South African Brokers
Despite clear requirements, independent FSPs frequently encounter recurring obstacles when implementing PCI compliance. Understanding these challenges helps practices proactively address them.
Budget Constraints
Small practices operate on tight margins, making compliance investment difficult to justify. Practical solutions include:
Scope Reduction: Eliminate card data storage entirely, using tokenization or third-party payment pages
Outsourcing: Leverage compliant payment processors to shift technical burden
Cloud Solutions: Use PCI-compliant cloud services rather than building on-premise infrastructure
Phased Implementation: Prioritize high-risk items first, addressing lower-priority requirements over time
Technical Knowledge Gaps
Many independent advisors lack IT expertise necessary for technical controls. Mitigation strategies:
Managed Service Providers: Engage IT firms specializing in financial services compliance
Simplified Solutions: Choose payment processors offering integrated, compliant solutions requiring minimal technical configuration
External Support: Retain a pci compliance consultant for technical guidance whilst handling policy and process elements internally
Staff Training: Develop basic security awareness even without deep technical knowledge
Resource Limitations
Solo practitioners and small teams struggle to maintain ongoing compliance monitoring. Practical approaches:
Compliance Calendars: Create annual schedules tracking all required activities
Automated Tools: Implement security monitoring tools that alert to issues
Shared Resources: For multi-advisor practices, designate one person for security coordination
External Monitoring: Engage compliance monitoring services offering integrated PCI, POPIA, and FICA oversight
Keeping Current with Evolving Standards
Payment security standards evolve continuously. The PCI Watch document library tracker helps consultants monitor changes, but independent brokers need simplified guidance on how updates affect their practices.
Establishing a relationship with a knowledgeable consultant ensures timely notification of relevant changes without requiring constant personal monitoring of technical standards.
Industry-Specific Considerations for Financial Services
Whilst PCI DSS applies across all industries, financial services organizations face unique contextual factors that influence compliance approaches.
Regulatory Examination Overlap
South African FSPs undergo regular regulatory examinations by the Financial Sector Conduct Authority (FSCA). Examiners increasingly scrutinize data protection practices, including payment security, during comprehensive examinations.
Maintaining documented PCI compliance provides valuable evidence of robust operational risk management during regulatory interactions. Conversely, identified security weaknesses can trigger increased supervisory attention and potential enforcement actions.
Professional Indemnity Insurance
Many professional indemnity insurers now require evidence of data protection compliance as a condition of coverage. Policies may exclude data breach claims when PCI or POPIA violations contributed to the incident.
Before renewing professional indemnity coverage, brokers should:
- Review policy exclusions related to data breaches
- Document PCI compliance status
- Understand whether validation reports affect premium calculations
- Consider cyber insurance as complementary coverage
Client Contractual Requirements
Institutional clients and product providers increasingly demand security attestations from distribution partners. FSPs seeking appointments with premium insurers or investment platforms may face due diligence questionnaires covering payment security practices.
Documented PCI compliance streamlines these credentialing processes and expands market access.
Payment Method Trends
The shift toward digital premium collection accelerates PCI relevance for financial advisors. Trends affecting compliance include:
Recurring Debit Orders: Require secure storage of tokenized payment credentials
Online Payment Portals: Demand web application security and encryption
Mobile Payment Apps: Introduce additional device security requirements
Cryptocurrency Integration: Creates new questions about scope and applicability (currently outside PCI DSS but subject to FICA/POPIA)
A forward-thinking pci compliance consultant helps FSPs anticipate how emerging payment technologies will affect compliance obligations.
Creating Sustainable Compliance Cultures
The most successful PCI implementations transcend checkbox compliance, creating genuine security awareness throughout the organisation. This cultural transformation requires leadership commitment and consistent reinforcement.
Top-Down Commitment
Principal officers and practice owners must visibly prioritize security:
- Allocate appropriate budget for security investments
- Participate in security training personally
- Discuss security in staff meetings regularly
- Recognize employees who identify and report risks
- Model secure behaviors in daily operations
When staff observe leadership treating security as core business practice rather than regulatory nuisance, cultural change accelerates.
Clear Accountability
Assign specific security responsibilities:
Compliance Officer/Security Coordinator: Overall programme oversight and policy maintenance
IT Manager/External Provider: Technical control implementation and monitoring
All Staff: Following security procedures in daily work
Third-Party Vendors: Meeting contractual security obligations
Document these assignments clearly, including in position descriptions and performance expectations.
Regular Communication
Security awareness degrades without reinforcement. Effective communication strategies include:
- Monthly security tips in team communications
- Quarterly security discussion in staff meetings
- Annual comprehensive training sessions
- Immediate notifications when new threats emerge
- Recognition of security-conscious behaviors
Incident Learning
When security incidents or near-misses occur, treat them as learning opportunities:
- Investigate root causes without blame
- Identify control failures or gaps
- Implement corrective measures
- Share lessons learned across the team
- Update procedures to prevent recurrence
This approach builds resilience whilst demonstrating commitment to continuous improvement.
Successfully navigating PCI compliance whilst managing the complex web of South African financial services regulations demands specialized expertise that most independent brokers and FSPs cannot develop internally. Understanding how payment card security intersects with POPIA data protection, FICA record-keeping, FAIS operational standards, and COFI client protection creates the foundation for comprehensive risk management.
For Financial Service Providers seeking expert guidance on building integrated compliance programmes that address payment security alongside broader regulatory obligations, Holistic Compliance Management Solutions (Pty) Ltd offers specialized support tailored to independent brokers and financial advisors. Whether you're implementing initial PCI controls, updating compliance frameworks for version 4.0, or integrating payment security with existing FICA RMCP and POPIA programmes, professional compliance support ensures sustainable adherence whilst maintaining operational efficiency. Request a compliance consultation to receive a comprehensive assessment covering:
- Current PCI compliance status and gap analysis aligned with POPIA and FICA obligations
- Practical implementation roadmap tailored to your practice size and payment processing methods
- Integration strategies connecting payment security with existing FSP compliance monitoring programmes
- Ongoing support for annual validation, policy updates, and regulatory change management
This consultation is designed for: Independent insurance brokers processing premium payments via card, financial advisors offering online payment options, FSPs seeking to strengthen operational risk management, and compliance officers managing multi-framework compliance programmes. Schedule your assessment today to transform compliance from burden to competitive advantage.